免责声明:本站提供安全工具、程序(方法)可能带有攻击性,仅供安全研究与教学之用,风险自负!
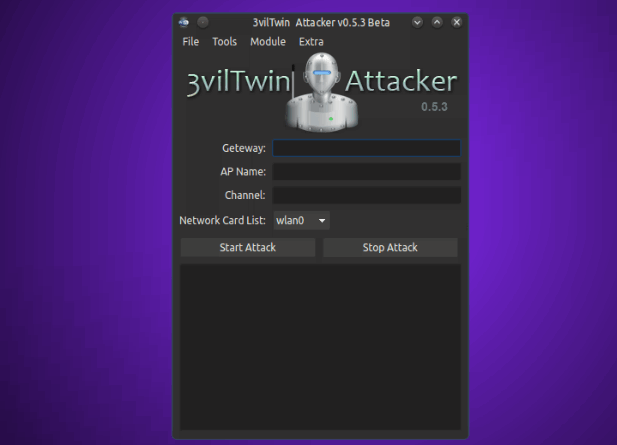
3vilTwinAttacker可以帮助渗透测试人员建立一个虚假的钓鱼wifi,表面上这是一个提供上网服务的正常AP(网络接入点),而实际上它却在不知不觉嗅探获取网络流量。
软件依赖
推荐使用Kali linux
Ettercap
Sslstrip
Airbase-ng(包含于aircrack-ng)
DHCP
Nmap
DHCP安装(Debian)
Ubuntu
$ sudo apt-get install isc-dhcp-server
Kali Linux
$ echo "deb http://ftp.de.debian.org/debian wheezy main " >> /etc/apt/sources.list
$ apt-get update && apt-get install isc-dhcp-server
DHCP安装(RedHat)
Fedora
$ sudo yum install dhcp
工具选项
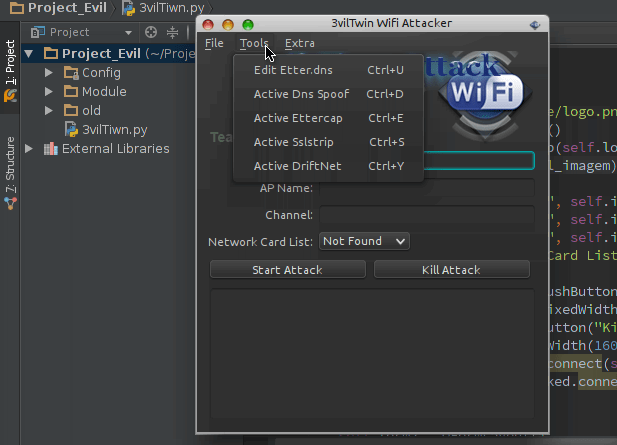
Etter.dns: Edit etter.dns to loading module dns spoof.
Dns Spoof: Start dns spoof attack in interface ath0 fake AP.
Ettercap: Start ettercap attack in host connected AP fake Capturing login credentials.
Sslstrip: The sslstrip listen the traffic on port 10000.
Driftnet: The driftnet sniffs and decodes any JPEG TCP sessions, then displays in an window.
Deauth Attack: kill all devices connected in AP (wireless network) or the attacker can Also put the Mac-address in the Client field, Then only one client disconnects the access point.
Probe Request: Probe request capture the clients trying to connect to AP,Probe requests can be sent by anyone with a legitimate Media Access Control (MAC) address, as association to the network is not required at this stage.
Mac Changer: you can now easily spoof the MAC address. With a few clicks, users will be able to change their MAC addresses.
Device FingerPrint: list devices connected the network mini fingerprint, is information collected about a local computing device.
视频演示
原版(需要梯子,本博客提供,请搜索):http://www.youtube.com/watch?v=Jrb43KVPIJw
国内通道:http://v.youku.com/v_show/id_XOTE4NDM1NDcy/v.swf.html
下载地址:github